
How to Safeguard Against Sophisticated Impersonation and Passkey Phishing Attacks [2025]
Last week, a high-profile breach revealed a complex phishing campaign targeting Microsoft Cloud accounts. This attack, characterized by its use of impersonation tactics and passkey phishing, has raised alarms across the industry. Let's dive deep into the mechanics of this attack, explore how it happened, and discover how you can protect yourself and your organization.
TL; DR
- Impersonation Tactics: Attackers pose as trusted IT personnel to trick users, as detailed in Microsoft's security blog.
- Passkey Phishing: A new method bypassing traditional password defenses, highlighted by Rescana.
- Targeted Assets: Files exfiltrated from Share Point, One Drive, and Exchange, as reported by Microsoft.
- Defense Strategies: Implement multi-factor authentication and educate your team, according to HKCERT.
- Future of Phishing: As technology evolves, so do the tactics of cybercriminals, as noted in Anthropic's threat intelligence report.
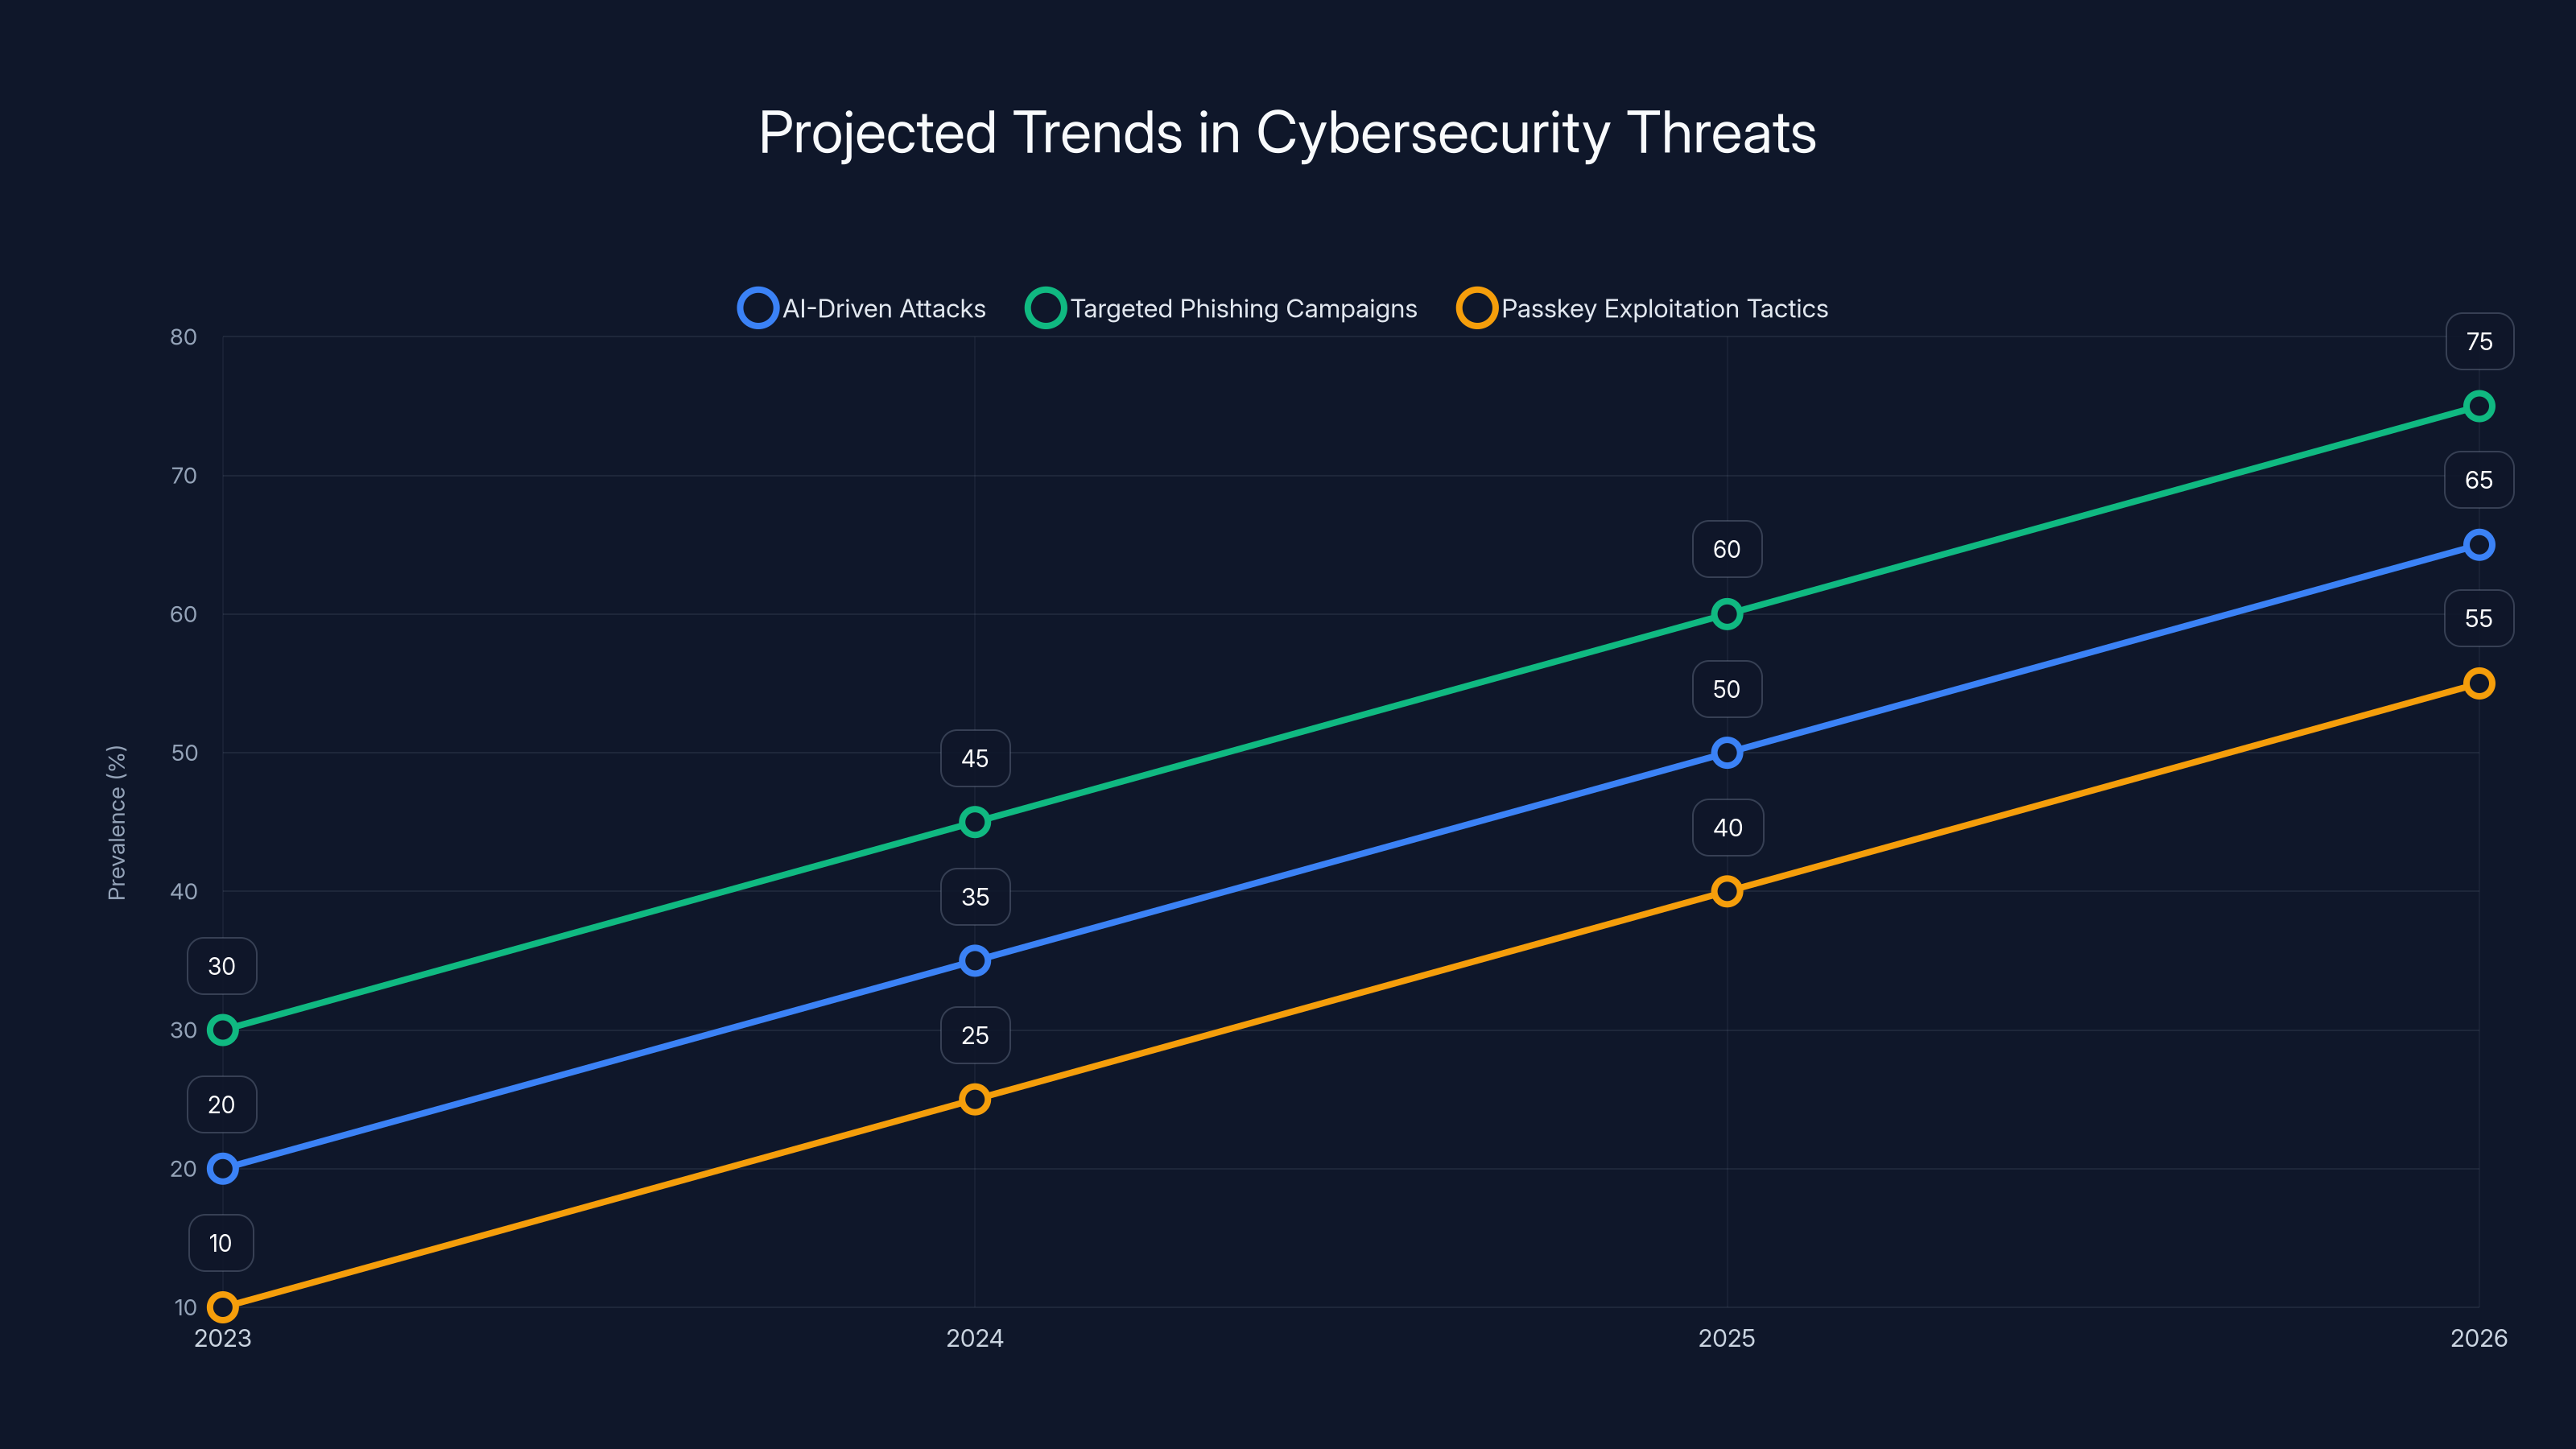
The line chart illustrates the projected increase in AI-driven attacks, targeted phishing campaigns, and passkey exploitation tactics from 2023 to 2026. Estimated data based on current trends.
Understanding the Attack
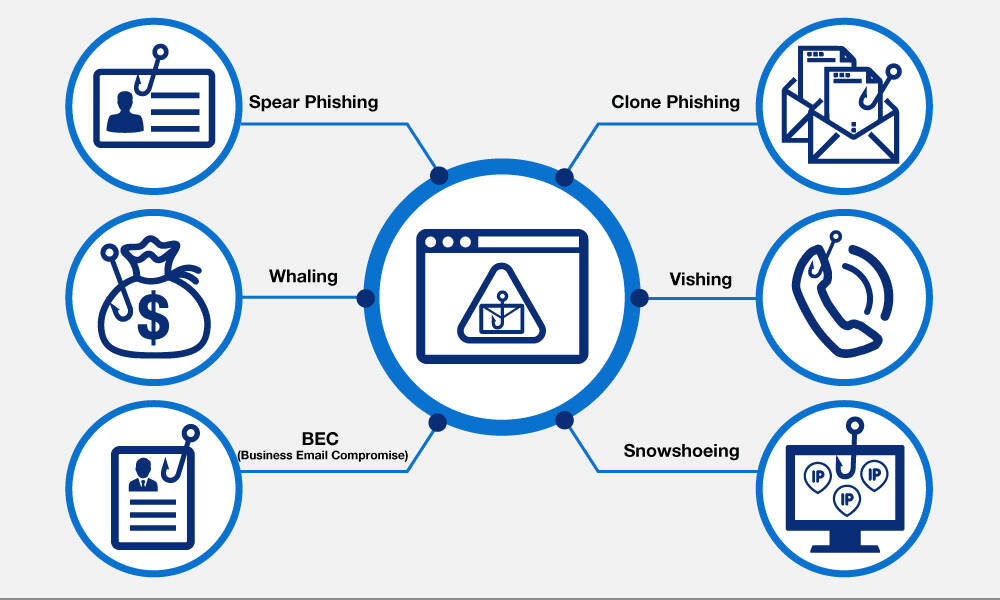
To fully grasp the sophistication of this phishing campaign, it's crucial to understand its components: impersonation and passkey phishing.
Impersonation Tactics
Impersonation in the digital realm involves attackers masquerading as legitimate IT personnel. They often use social engineering to deceive users into believing the communication is from a trusted source. This can include emails, phone calls, or even fake websites designed to mimic the organization's IT helpdesk, as explained by Microsoft's blog on AI-assisted impersonation.
Example: Imagine receiving a call from someone claiming to be from your company's IT department. They inform you of an urgent security update that requires your attention. Trusting their authority, you might follow their instructions without question.
Passkey Phishing
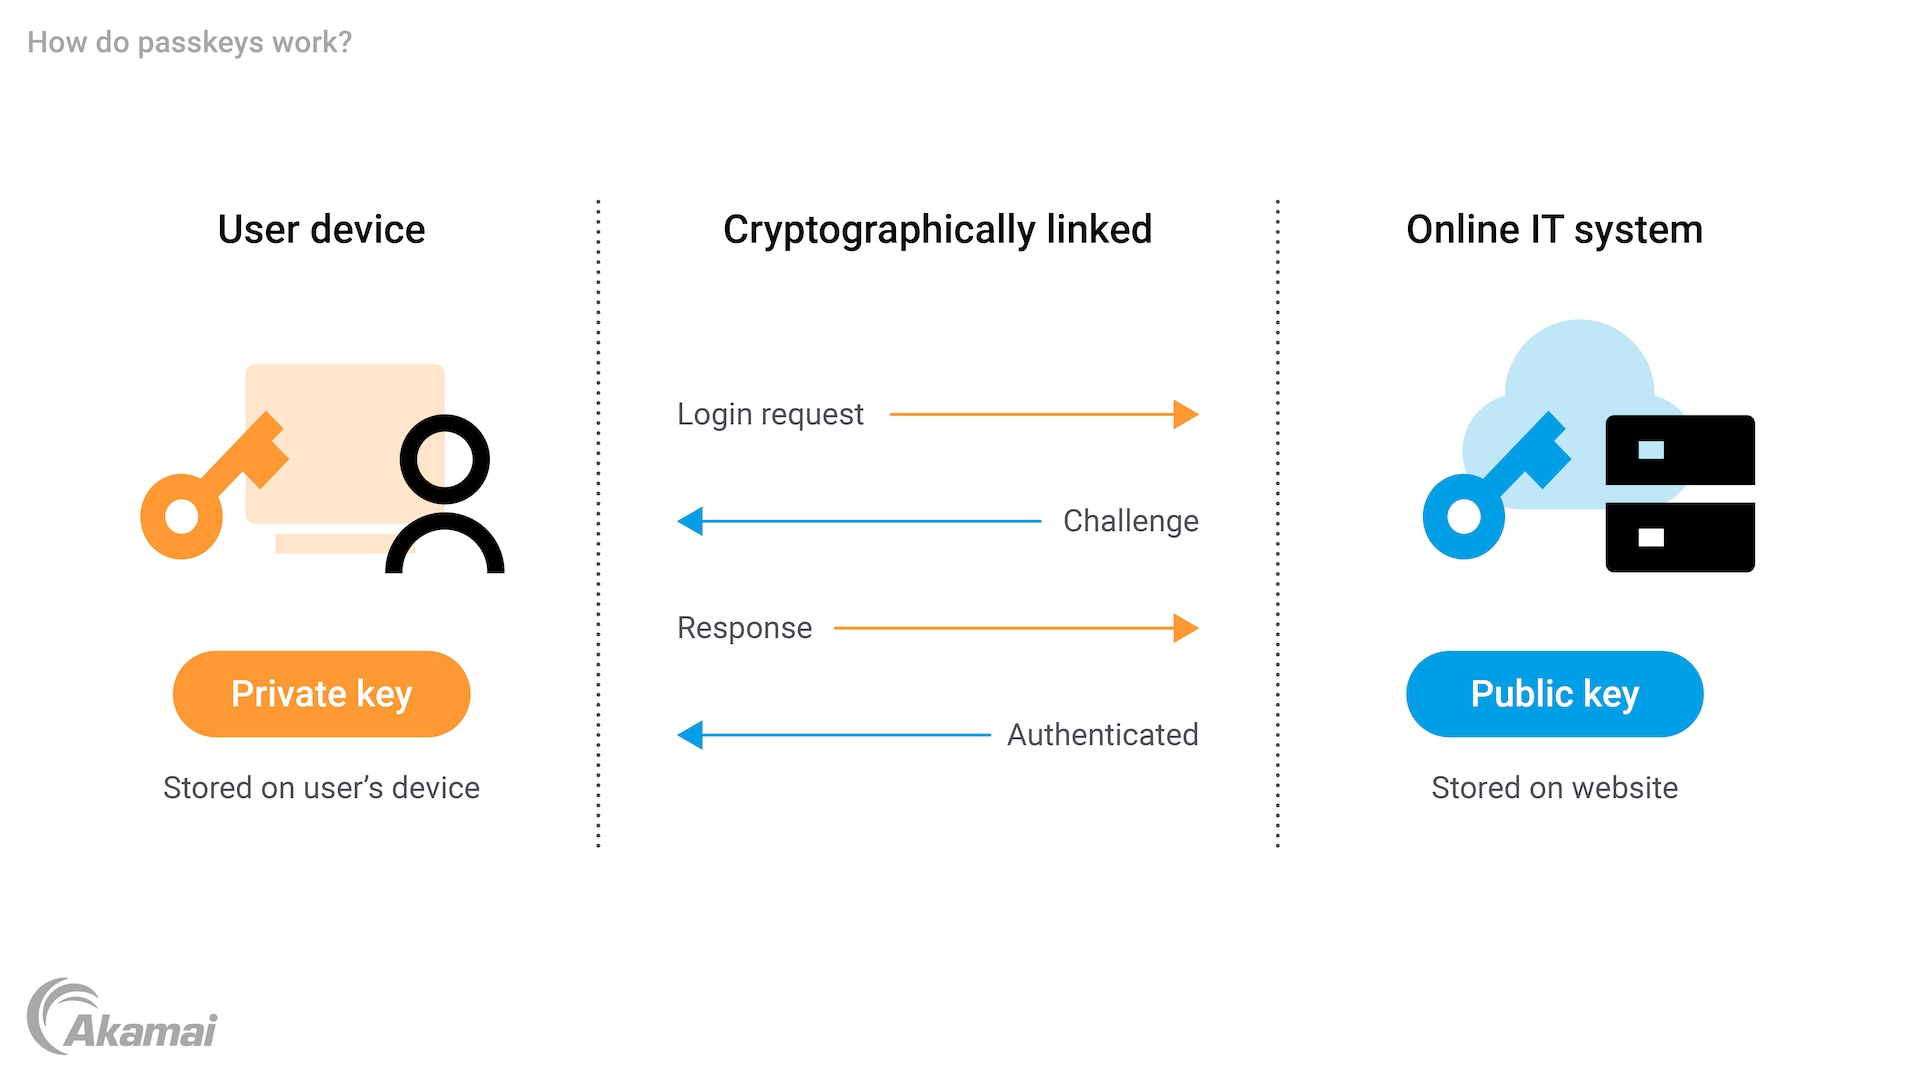
Passkey phishing is a relatively new tactic that targets the modern authentication methods designed to replace passwords. Unlike traditional phishing, which aims to steal passwords, passkey phishing tricks users into revealing their authentication tokens or passkeys. This method is discussed in detail by The Hacker News.
Example: An attacker sends an email with a link to a fake login page, requesting you to 'update your passkey.' Once you enter your passkey, the attacker captures it and uses it to access your account.

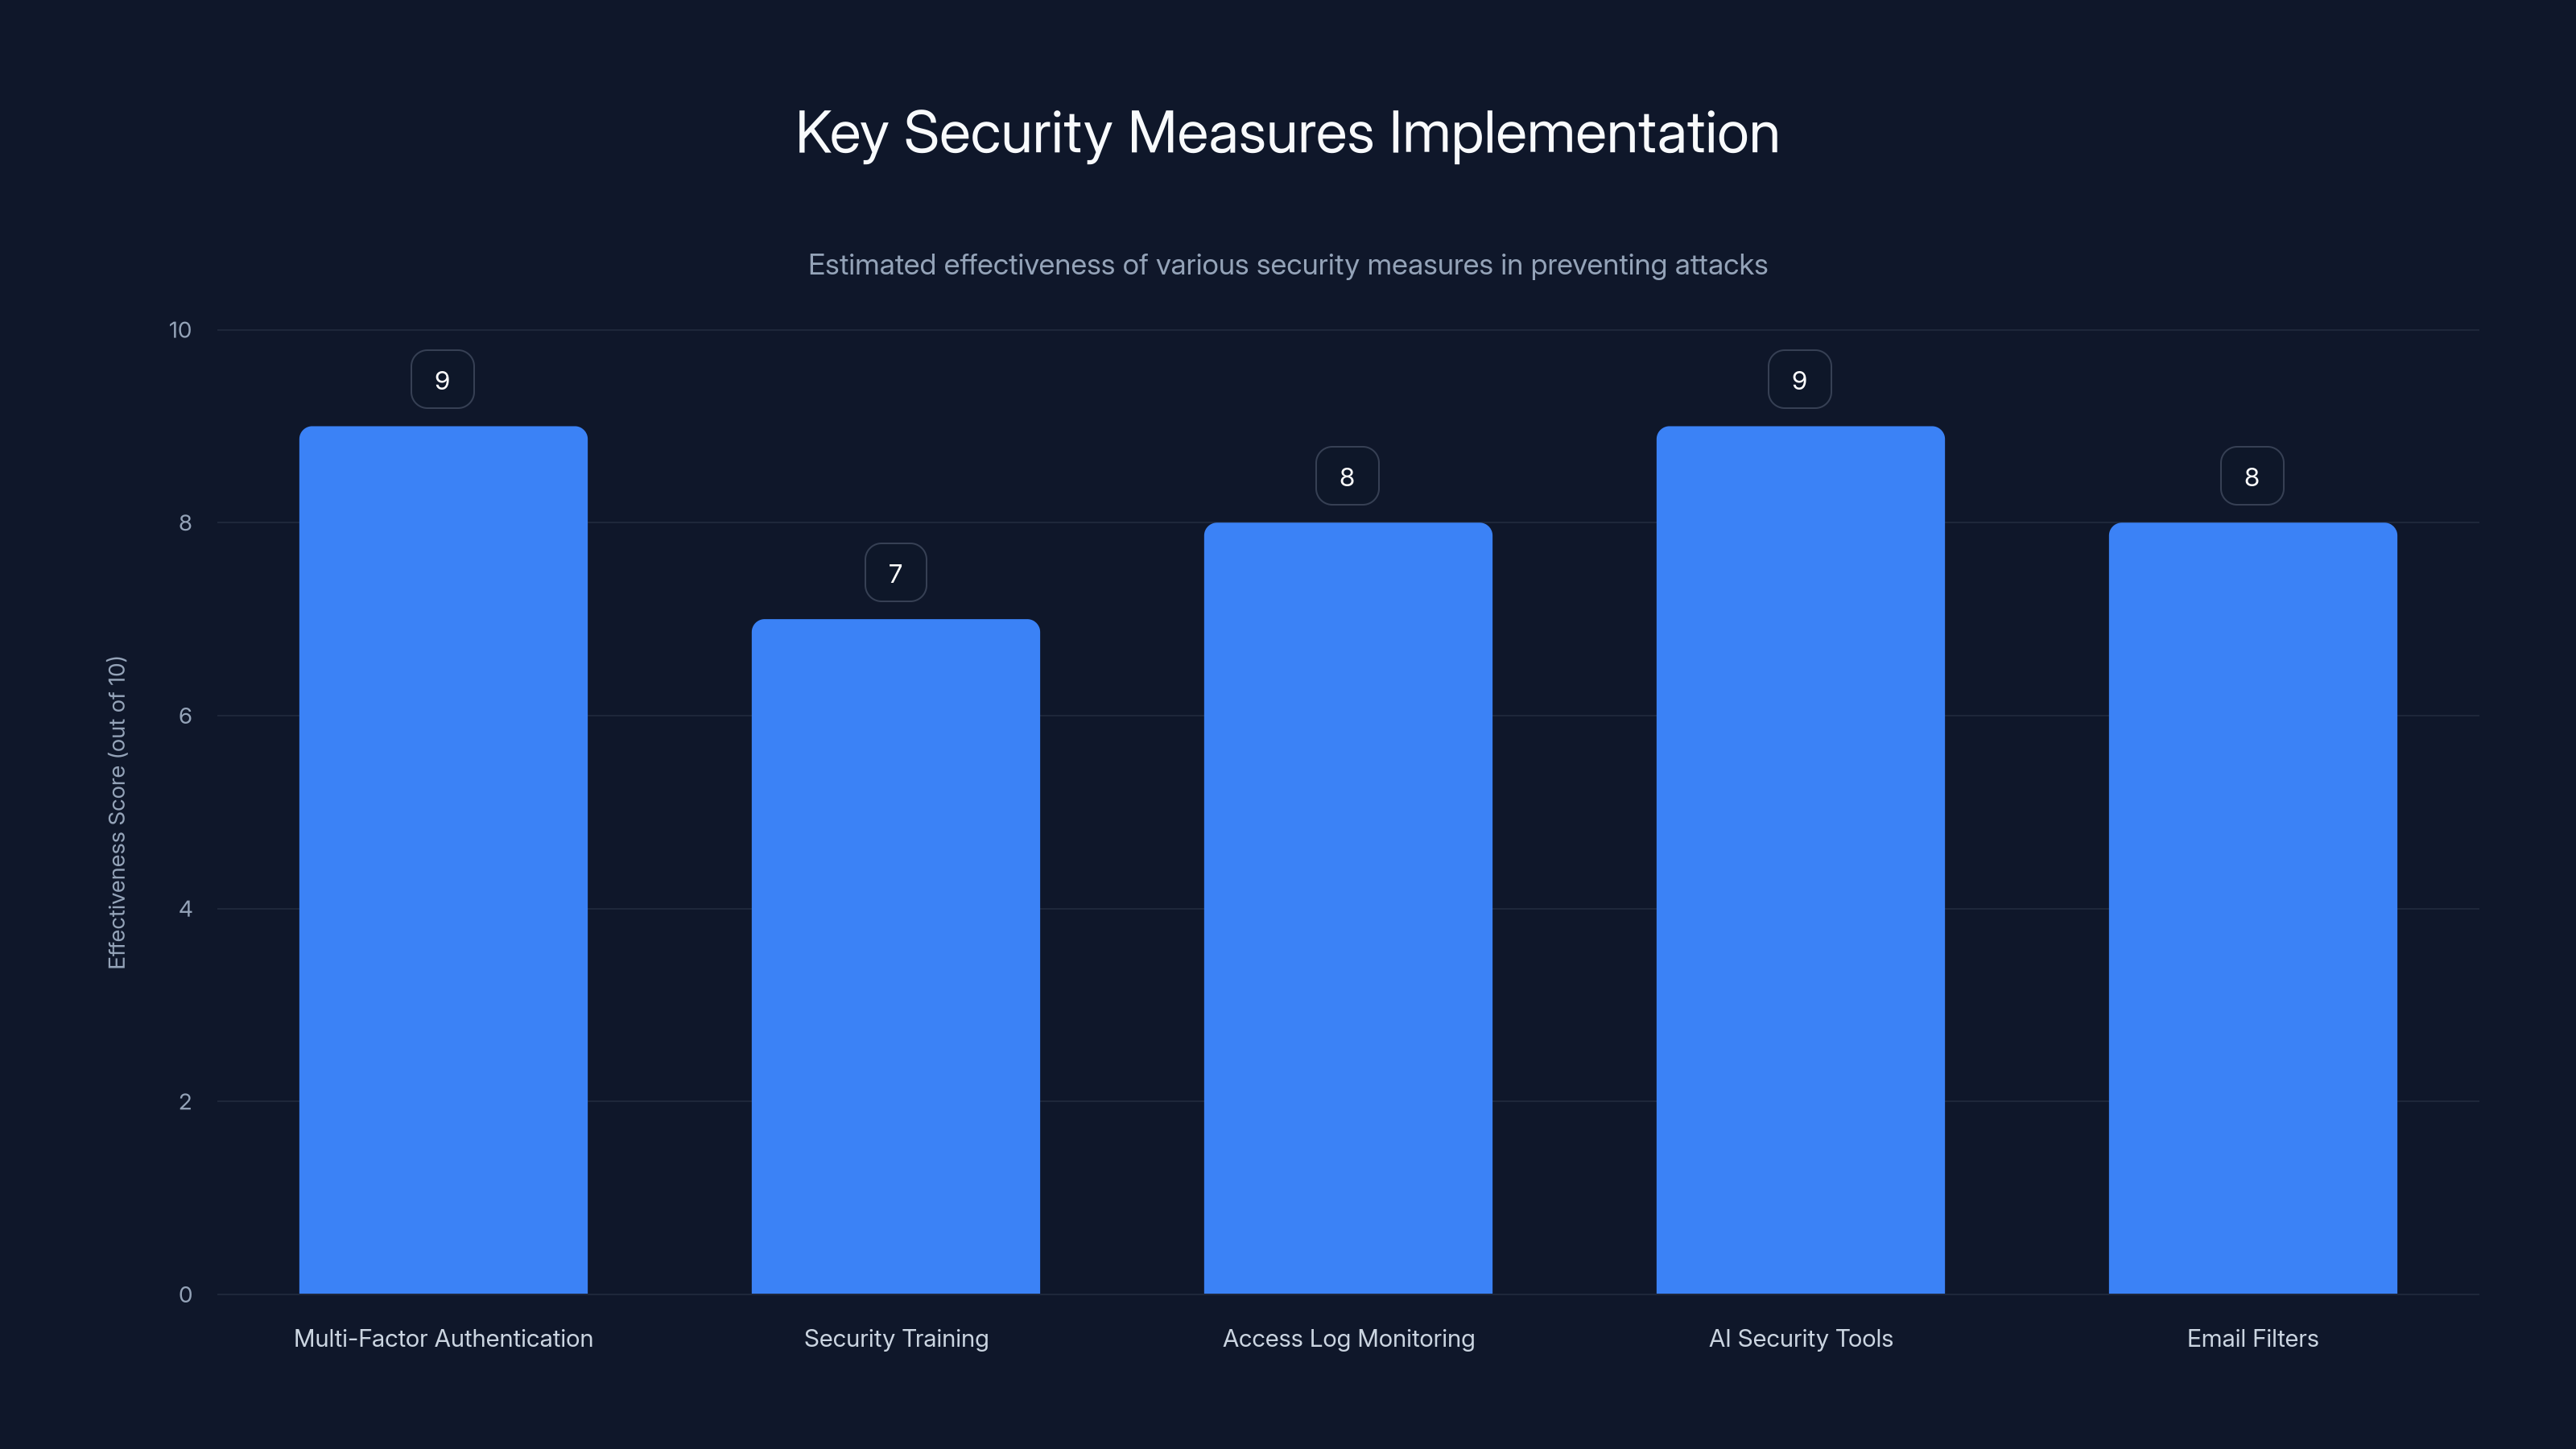
Multi-Factor Authentication and AI Security Tools are estimated to be the most effective measures, each scoring 9 out of 10 in preventing attacks. Estimated data.
Anatomy of the Campaign
The attack on Microsoft Cloud accounts was meticulously planned and executed. Here's how it unfolded:
- Initial Contact: Attackers initiated contact via emails and phone calls, posing as IT support, as described in Help Net Security.
- Fake Websites: They directed users to counterfeit websites resembling Microsoft's login pages, as noted by Microsoft.
- Passkey Harvesting: Users unknowingly submitted their passkeys, believing they were complying with security protocols, as reported by gHacks.
- Data Exfiltration: With access to accounts, attackers exfiltrated sensitive files from Share Point, One Drive, and Exchange, as detailed in Microsoft's security blog.
Practical Implementation Guide
To defend against these types of attacks, organizations must adopt a multi-faceted approach:
1. Enhance Authentication Methods
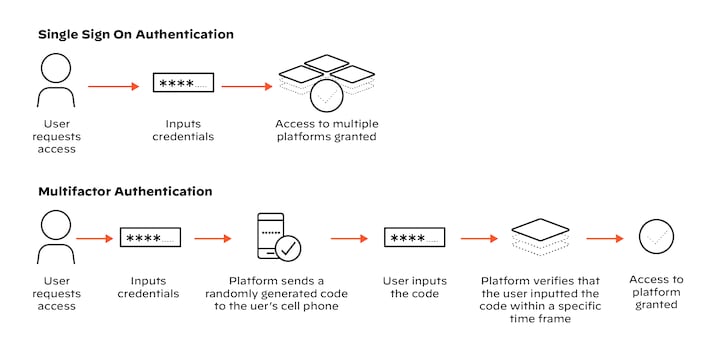
- Multi-Factor Authentication (MFA): Implement MFA across all accounts. This adds an extra layer of security by requiring additional verification steps, such as a text message code or biometric scan, as recommended by SoSafe.
plaintext// Example of setting up MFA 1. Go to your account security settings. 2. Select 'Enable Multi-Factor Authentication.' 3. Choose your preferred authentication method: SMS, authenticator app, or biometric. 4. Follow the prompts to complete the setup.
- Passkey Awareness: Educate employees about the importance of passkeys and how to recognize phishing attempts, as emphasized by Anthropic's threat intelligence report.
2. Conduct Regular Security Training
Regular training sessions can help employees recognize phishing attempts and report them promptly. Include real-world scenarios and simulations to enhance learning, as suggested by VA News.
3. Monitor and Audit Access Logs
Regularly review access logs to detect unusual activity. Look for patterns such as logins from unfamiliar locations or attempts outside of normal business hours, as advised by NJ Spotlight News.
4. Utilize AI-Powered Security Tools
Leverage AI tools to identify and mitigate threats in real-time. These tools can analyze patterns and detect anomalies that might indicate a phishing attack, as highlighted by Microsoft's insights on AI security.
5. Implement Strict Email Filters
Configure email filters to block suspicious emails. Use machine learning to continuously adapt and refine the filtering criteria, as recommended by The Hacker News.
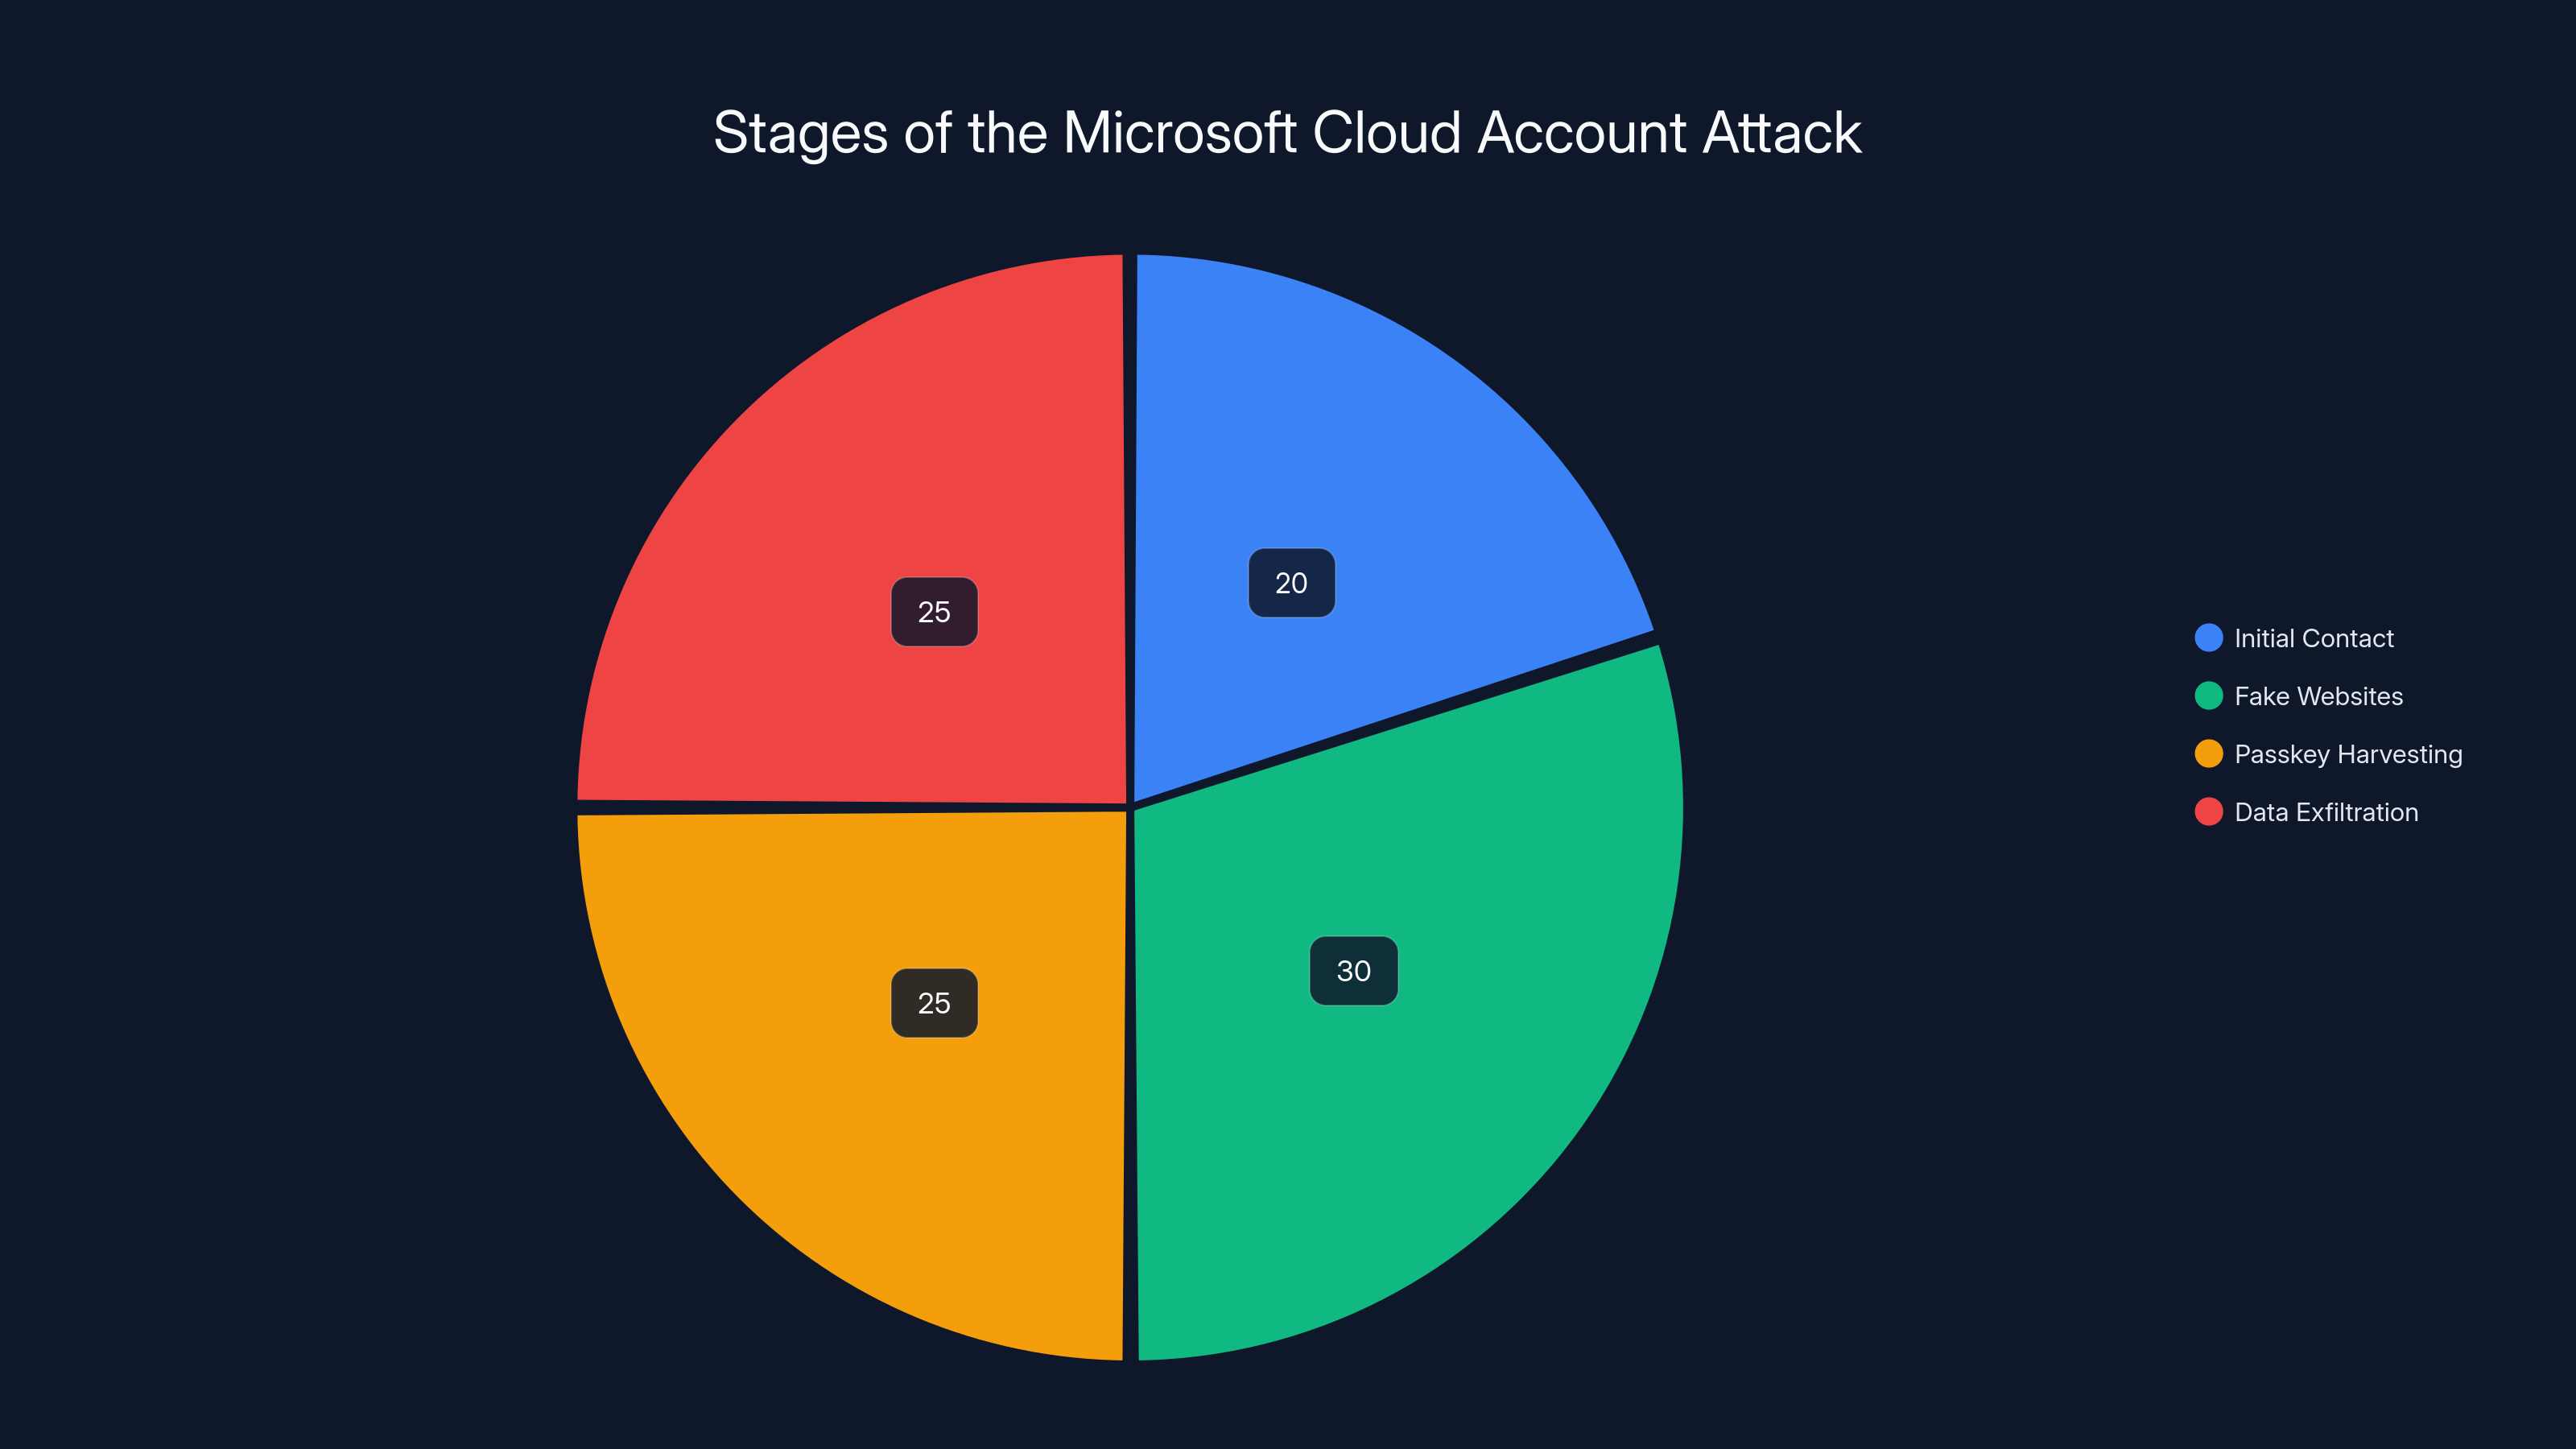
The attack was distributed across four main stages, with fake websites and data exfiltration being equally prioritized. Estimated data.
Common Pitfalls and Solutions
Pitfall 1: Overreliance on Technology
While technology is essential, it should not be the sole defense. Human vigilance is equally important, as noted by Anthropic.
Solution: Combine technological solutions with regular training and awareness programs.
Pitfall 2: Inadequate Incident Response Plans
Many organizations lack a structured plan for responding to phishing incidents, as highlighted by Microsoft.
Solution: Develop and regularly update an incident response plan. Conduct drills to ensure everyone knows their role in case of an attack.
Future Trends and Recommendations
As cybercriminals become more sophisticated, organizations must stay ahead of emerging threats.
Trend 1: Increased Use of AI by Attackers
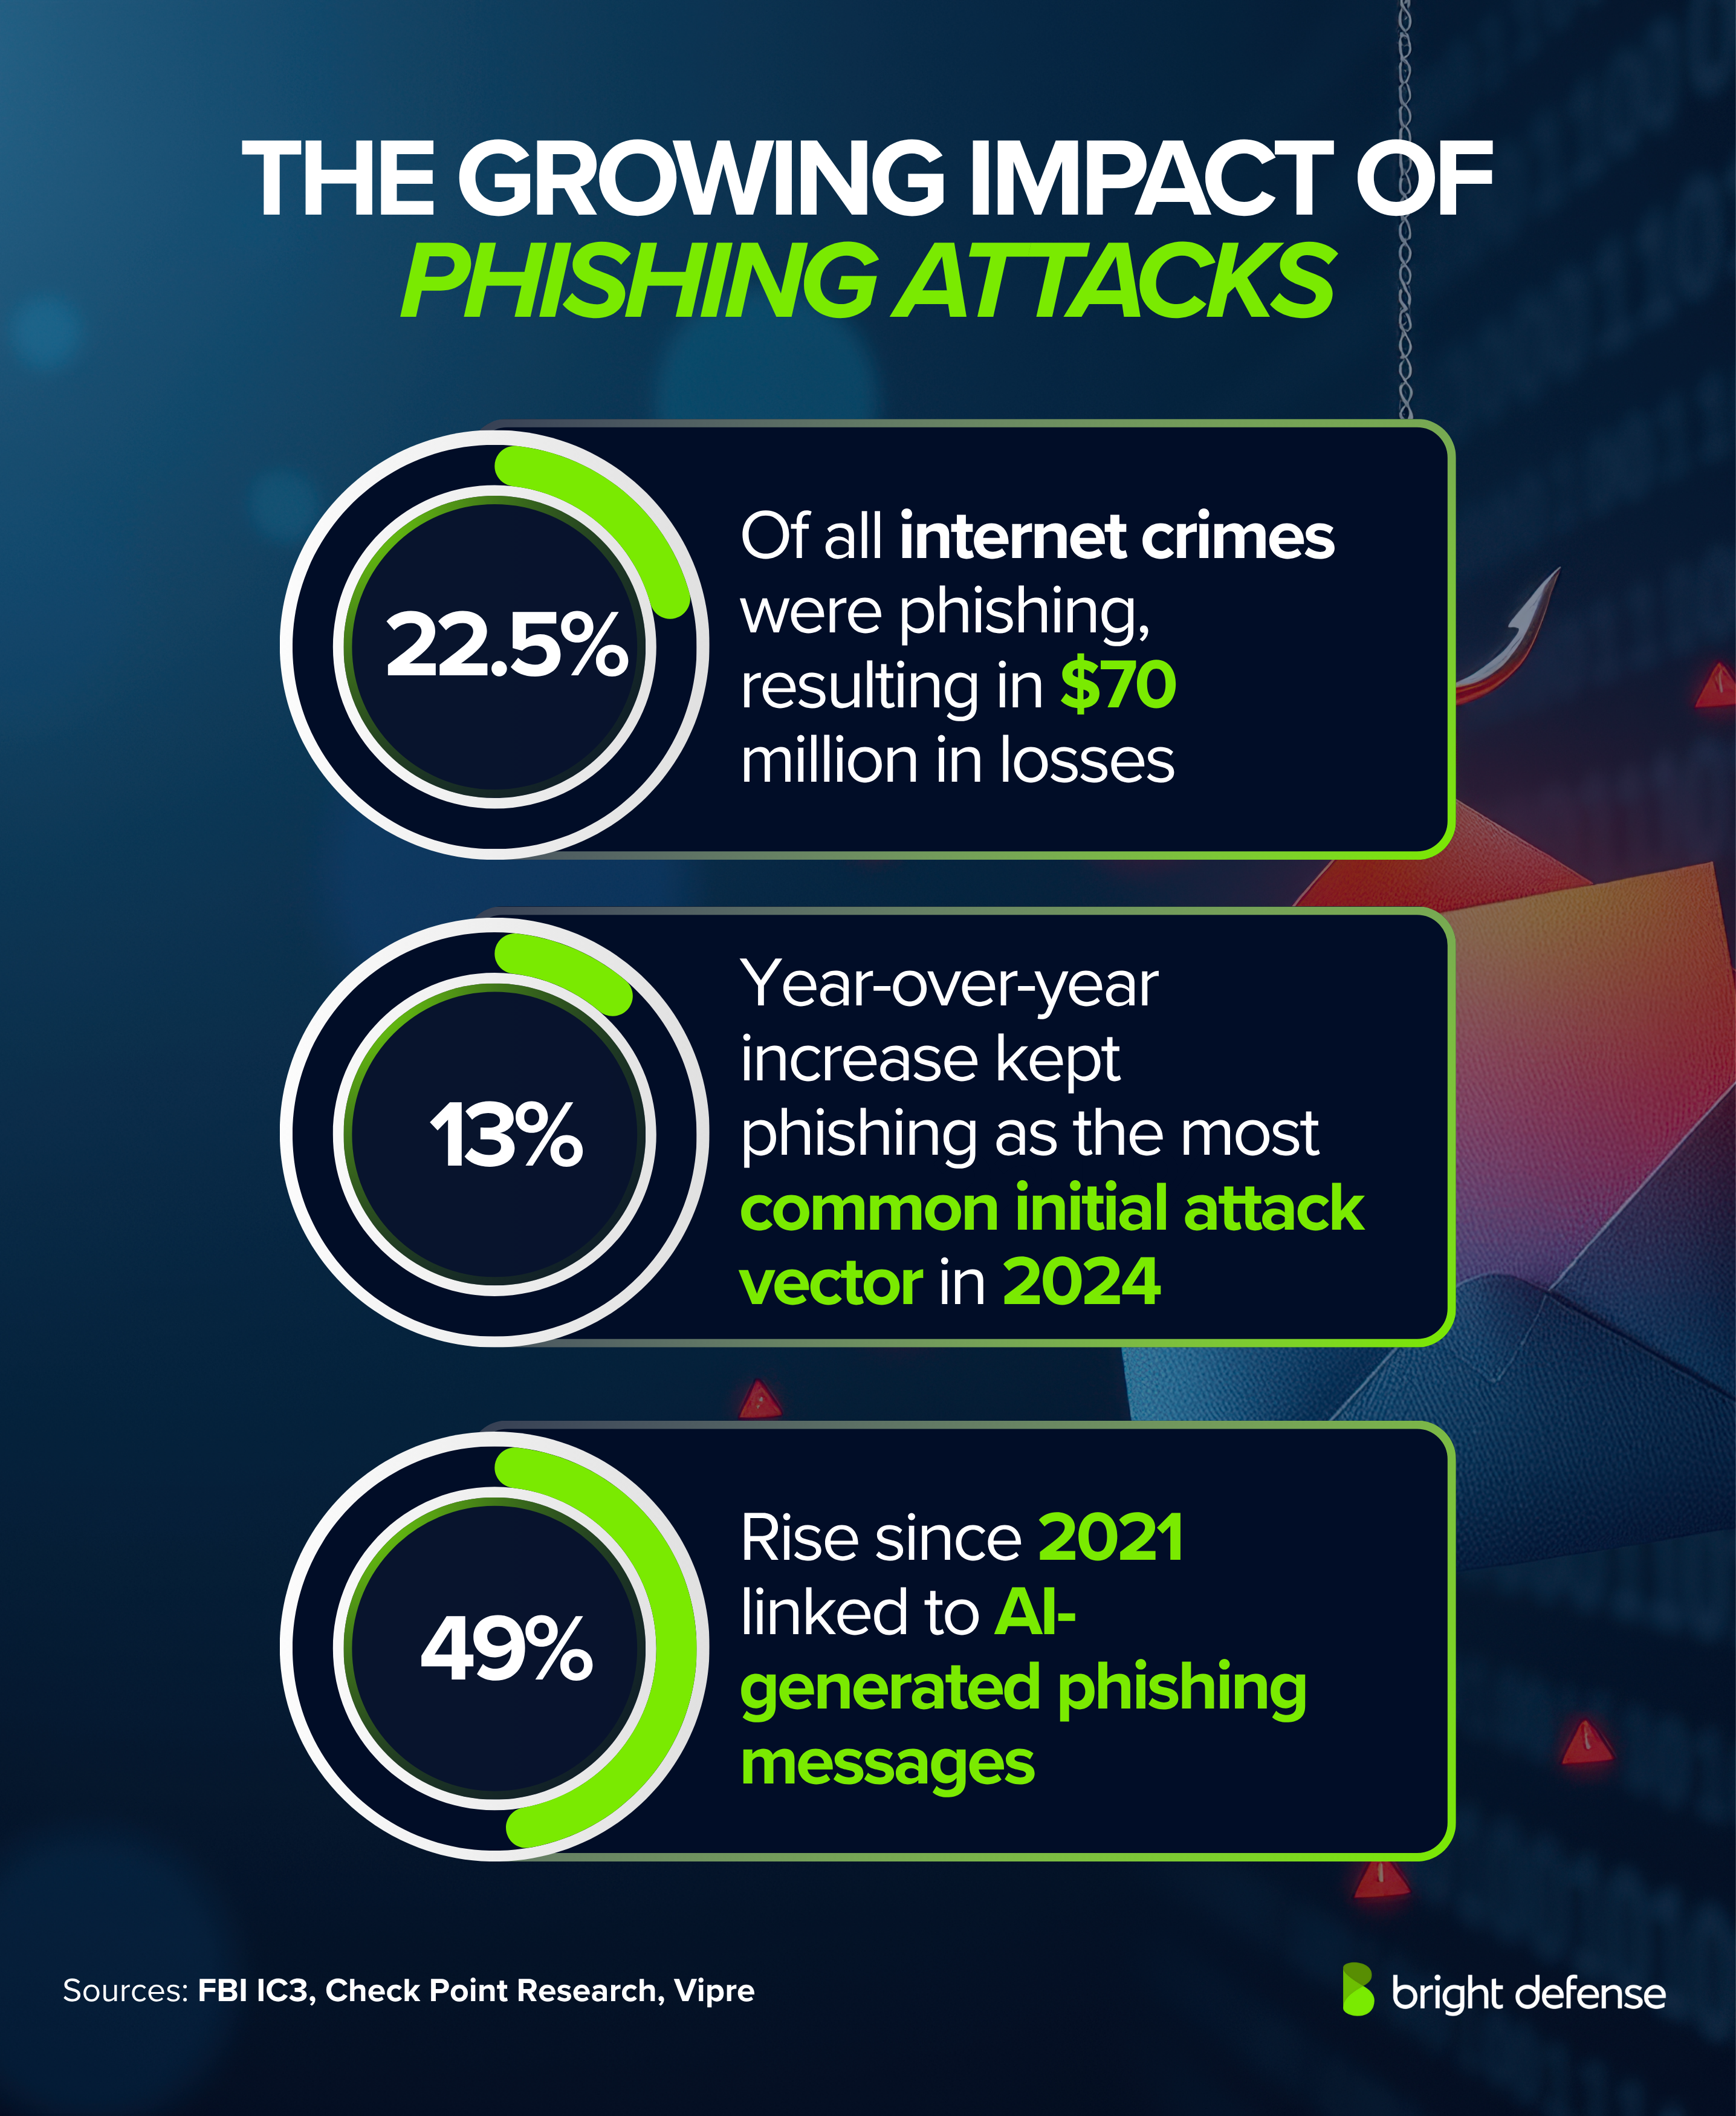
Attackers are increasingly using AI to craft more convincing phishing scams and automate attacks, as discussed by HKCERT.
Recommendation: Invest in AI-driven security solutions to counter these threats.
Trend 2: Targeted Phishing Campaigns
Phishing attacks are becoming more personalized and targeted, as noted by Rescana.
Recommendation: Implement user behavior analytics (UBA) to detect anomalies and predict potential threats.
Trend 3: Evolution of Passkey Technologies
As passkeys become more prevalent, so will the tactics to exploit them, as highlighted by gHacks.
Recommendation: Continuously update security protocols to accommodate advancements in passkey technology.
Conclusion
The recent phishing campaign targeting Microsoft Cloud accounts underscores the need for robust security measures. By understanding the tactics used by attackers and implementing comprehensive defense strategies, organizations can significantly reduce their risk of falling victim to such sophisticated attacks. As technology evolves, so must our defenses, ensuring we stay one step ahead in the ongoing battle against cybercrime.
FAQ
What is impersonation in phishing attacks?
Impersonation involves attackers posing as legitimate sources, such as IT personnel, to deceive users into revealing sensitive information, as explained by Microsoft.
How does passkey phishing work?
Passkey phishing tricks users into revealing their authentication tokens or passkeys, allowing attackers to bypass traditional password defenses, as detailed by The Hacker News.
What are the benefits of multi-factor authentication?
Multi-factor authentication adds an extra layer of security by requiring additional verification steps, significantly reducing the likelihood of unauthorized access, as noted by SoSafe.
How can organizations improve employee awareness of phishing threats?
Regular security training, phishing simulations, and clear communication about potential threats can enhance employee awareness and readiness, as recommended by VA News.
What role does AI play in modern phishing attacks?
AI is used by attackers to automate and craft more convincing phishing scams, making them harder to detect with traditional methods, as highlighted by HKCERT.
Key Takeaways
- Understand impersonation tactics to better defend against phishing.
- Passkey phishing targets modern authentication methods.
- Implement MFA to add an extra layer of security.
- Regular security training is crucial to employee awareness.
- AI tools can help mitigate real-time threats.
Related Articles
- Why CIOs are Paying Closer Attention to Physical Security [2025]
- Maximizing Online Security: The Benefits of Keeping Your VPN On 24/7 [2025]
- From Hacks to Bioweapons, Claude Misuse Is Now Everywhere | WIRED
- Anthropic's Cybersecurity Challenges and the Future of AI Security [2025]
- US Treasury Demands Better Cyber Scam Reporting: $13 Billion Lost [2025]
- Thinking Like a Hacker to Boost Cyber Resilience [2025]


