
Introduction
In recent years, artificial intelligence has become deeply integrated into various aspects of our lives. From smart assistants to autonomous vehicles, AI-powered systems are transforming industries. However, with great power comes great responsibility, and AI technologies are not immune to vulnerabilities. One such concern is the potential for exploits that allow attackers to control AI agents, posing significant risks to both individuals and organizations.
TL; DR
- AI Vulnerabilities: AI systems are susceptible to exploits that can compromise their functioning.
- Security Strategies: Implement robust security measures to protect AI agents from unauthorized access.
- Monitoring and Response: Continuous monitoring and rapid response are key to managing AI security incidents.
- Future Trends: As AI evolves, so will the tactics used by attackers, necessitating ongoing vigilance.
- Collaboration: Industry-wide collaboration is essential to develop effective security standards for AI technologies.
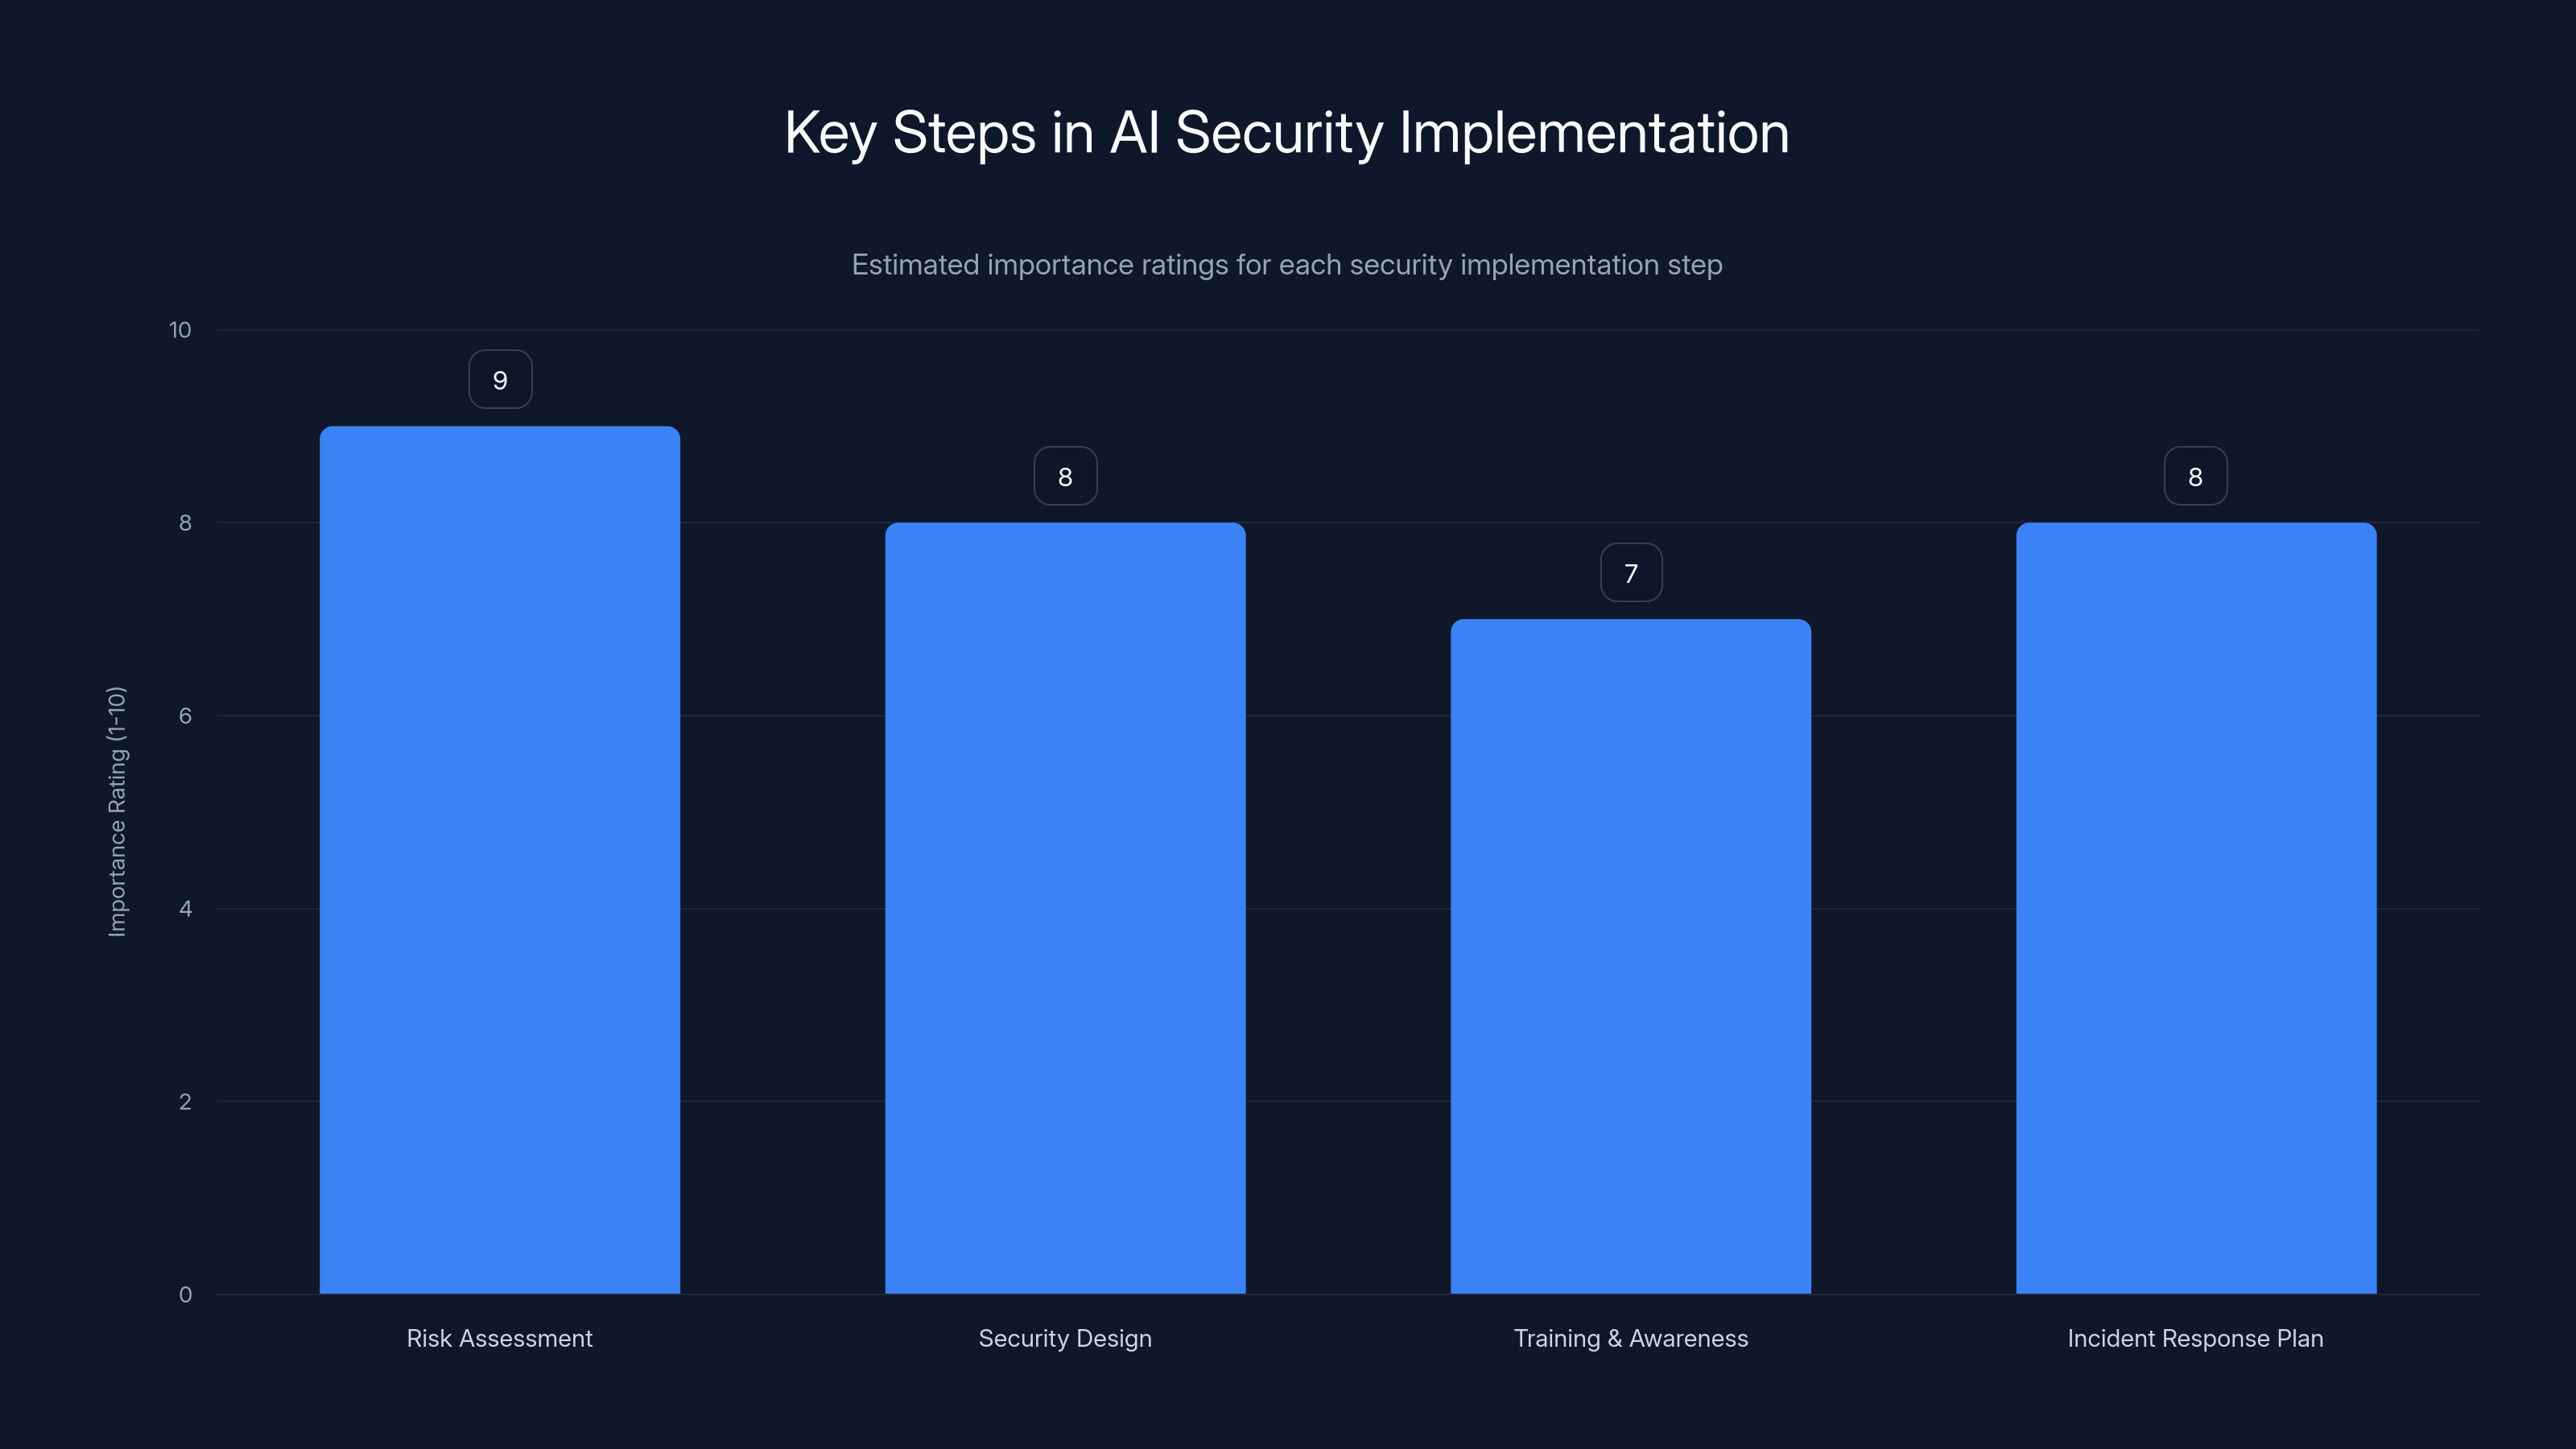
Risk Assessment is rated as the most critical step in AI security implementation, followed closely by Security Design and Incident Response Planning. Estimated data based on typical security priorities.
Understanding AI Exploits
AI exploits occur when attackers identify and leverage vulnerabilities within AI systems, allowing them to manipulate or control the AI's actions. These exploits can range from simple data manipulation to complex attacks that compromise the AI's decision-making processes.
How Exploits Occur
Exploits typically target weaknesses in the AI's architecture, data processing, or communication channels. Common methods include:
- Data Poisoning: Introducing malicious data into the training dataset to alter the AI's behavior.
- Adversarial Attacks: Crafting inputs that deceive the AI into making incorrect decisions.
- Model Extraction: Stealing the AI's model to replicate its functionality and identify vulnerabilities.
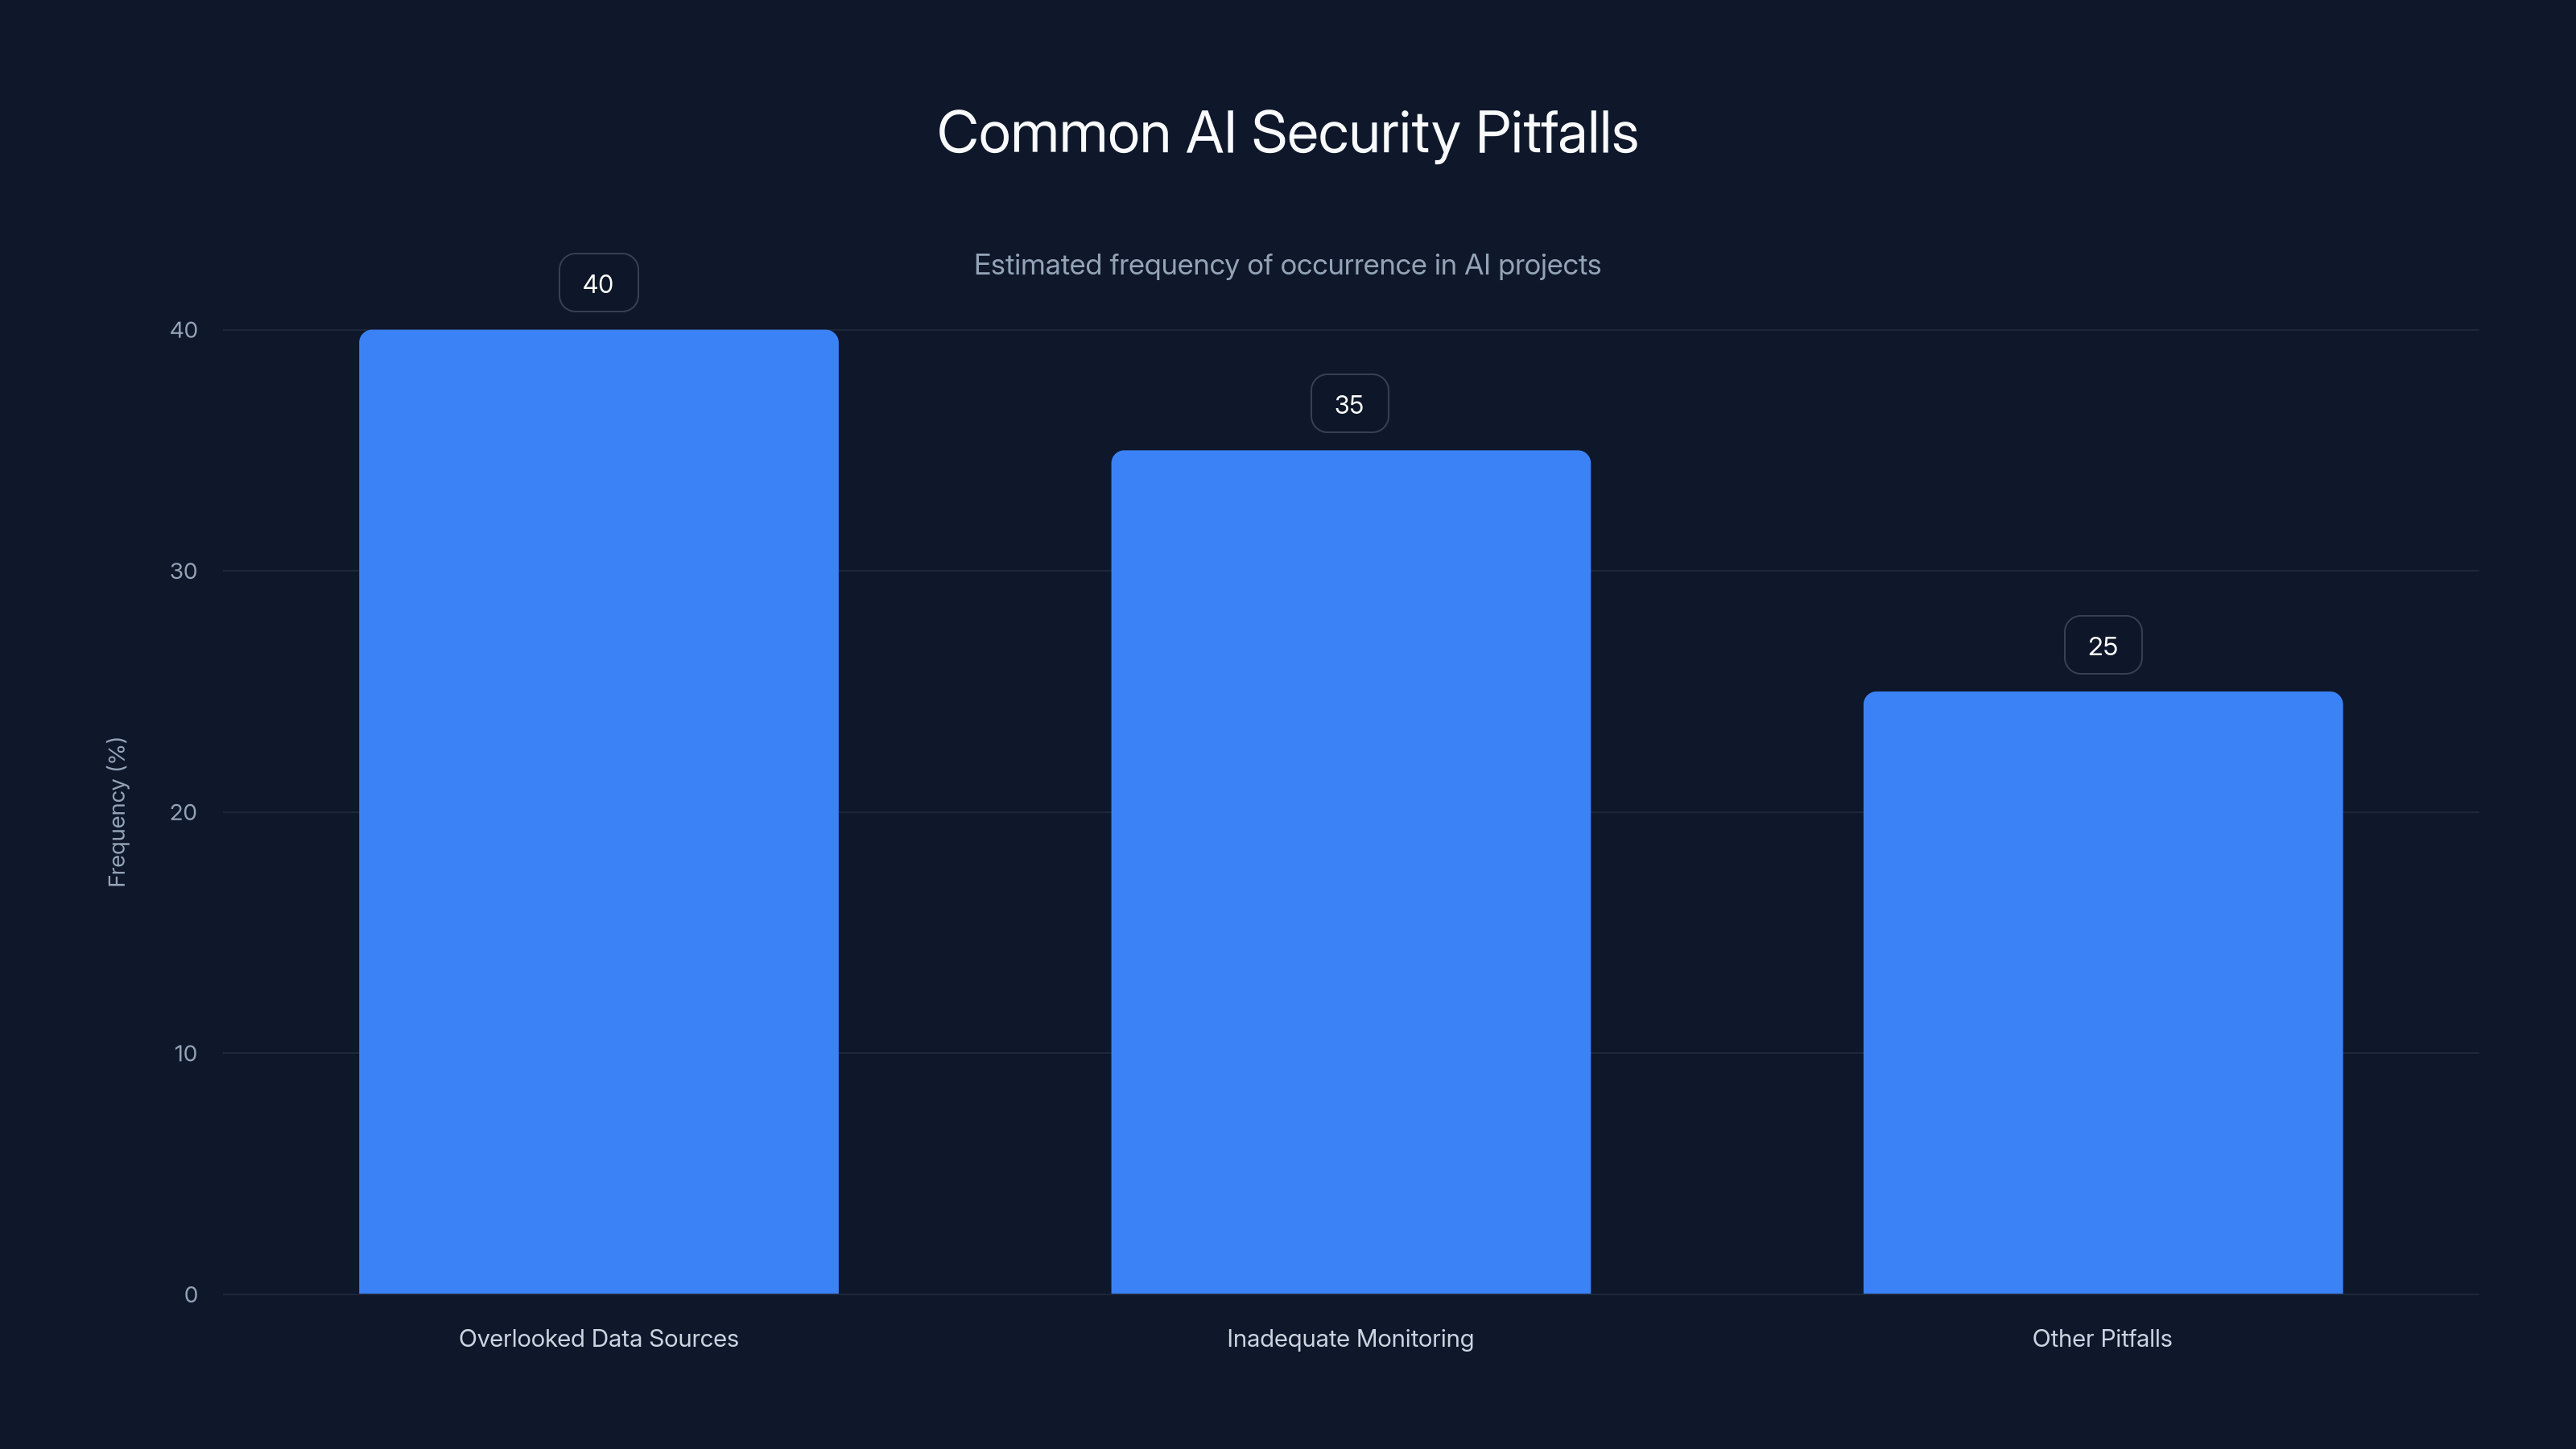
Overlooked data sources and inadequate monitoring are common pitfalls in AI security, with estimated frequencies of 40% and 35% respectively. Estimated data.
Real-World Examples
Consider a scenario where an AI-powered traffic management system is compromised. An attacker could manipulate traffic signals to create congestion or allow unauthorized vehicles through restricted zones. Similarly, in a healthcare setting, altering the AI's diagnosis algorithms could lead to incorrect treatment recommendations.
Best Practices for AI Security
To mitigate the risk of AI exploits, organizations should implement comprehensive security strategies. Here are some best practices:
Regular Security Audits
Conduct periodic audits to identify and address potential vulnerabilities in AI systems. This includes reviewing code, data integrity, and access controls, as highlighted in Qualys' continuous audit readiness approach.
Data Validation
Implement rigorous data validation processes to ensure that only clean, verified data is used for training and decision-making.
Access Controls
Restrict access to AI systems and their underlying data to authorized personnel only. Utilize multi-factor authentication and role-based access controls, as recommended by Duo's adaptive authentication solutions.
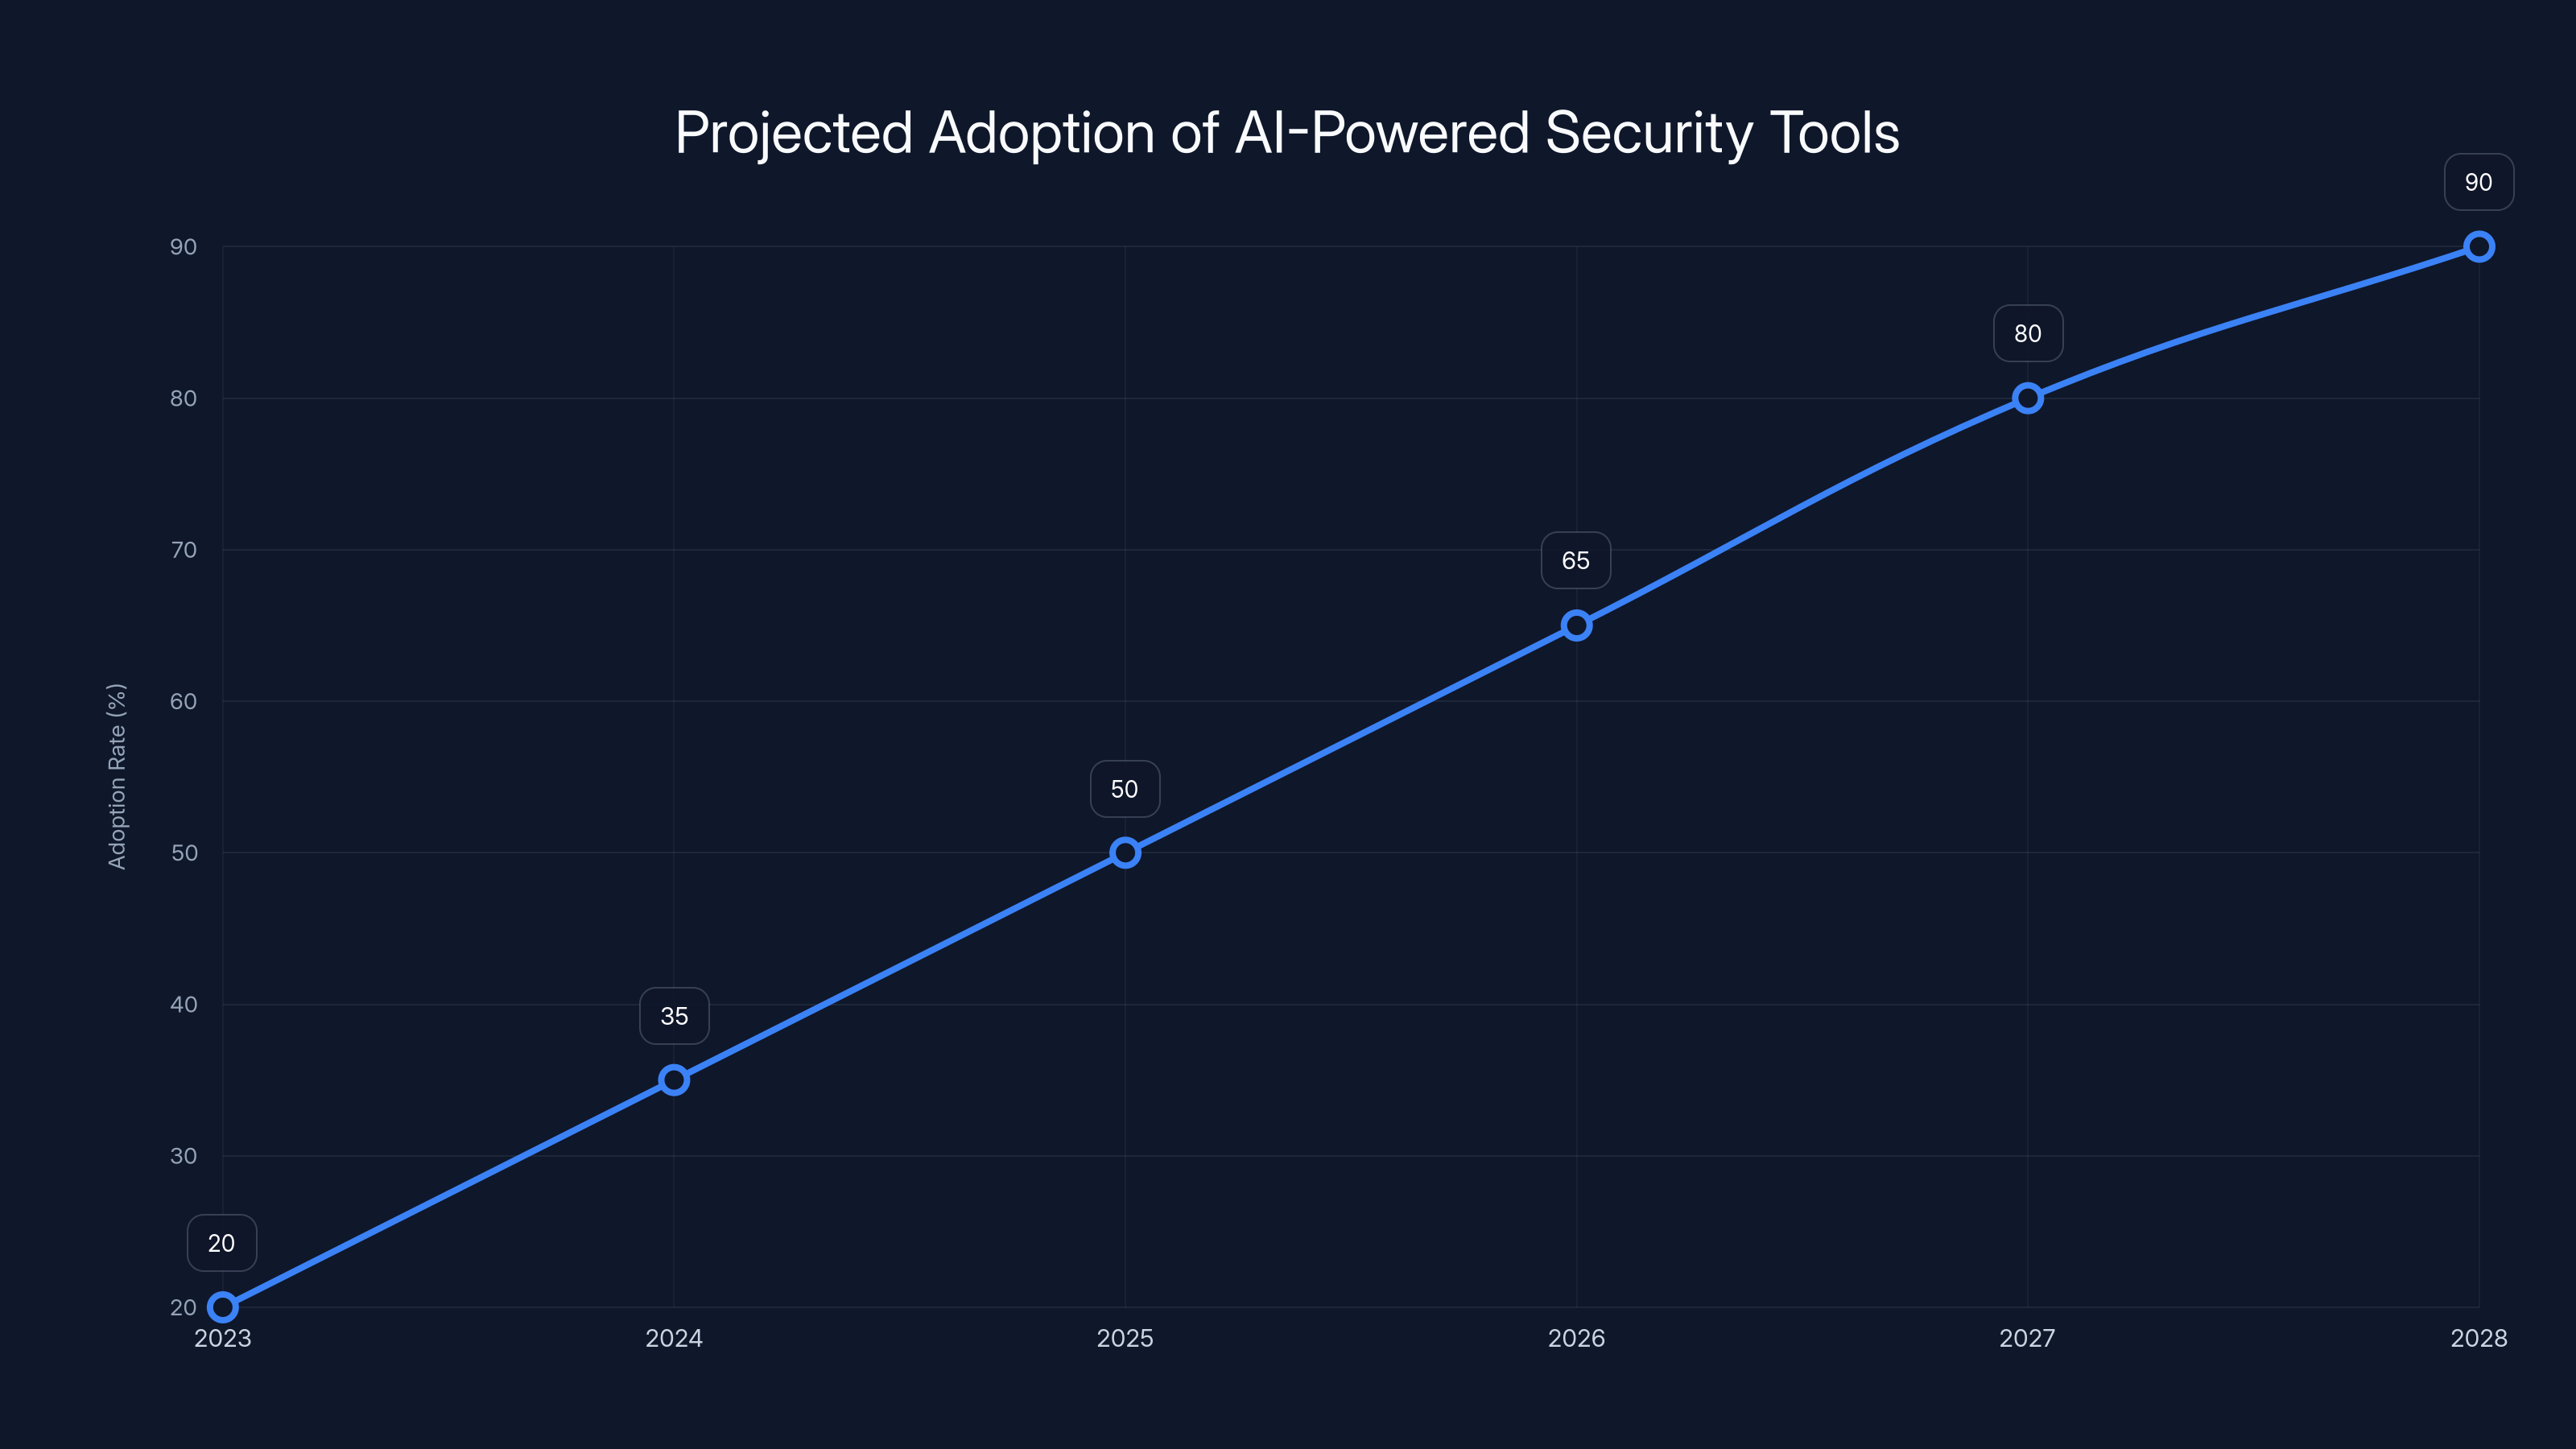
The adoption of AI-powered security tools is expected to grow significantly, reaching 90% by 2028. (Estimated data)
Practical Implementation Guides
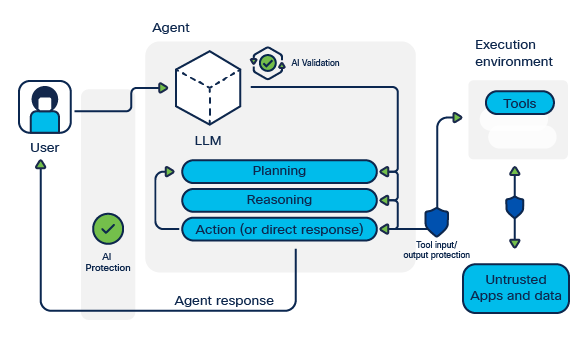
Step-by-Step Security Implementation
- Risk Assessment: Identify potential threats and vulnerabilities specific to your AI systems.
- Security Design: Incorporate security features into the AI's architecture from the outset.
- Training and Awareness: Educate staff on AI security best practices and potential threats.
- Incident Response Plan: Develop and test a comprehensive response plan for AI-related security incidents.
Example Code for Secure AI Deployment
pythonimport torch
from torchvision import models
# Load pre-trained model with strict security measures
def load_secure_model():
model = models.resnet50(pretrained=True)
model.eval()
# Implement model freezing to prevent unauthorized modifications
for param in model.parameters():
param.requires_grad = False
return model
model = load_secure_model()
Common Pitfalls and Solutions
Overlooked Data Sources
Organizations often focus on securing the AI model but neglect data sources. Ensure all data inputs are verified and secured against tampering.
Inadequate Monitoring
Lack of continuous monitoring can lead to delayed detection of exploits. Implement real-time monitoring tools to track AI performance and identify anomalies, as discussed in IT Brew's insights on AI security risks.

Future Trends and Recommendations
As AI technologies continue to advance, so too will the methods used by attackers. Here are some trends and recommendations to consider:
AI-Powered Security Tools
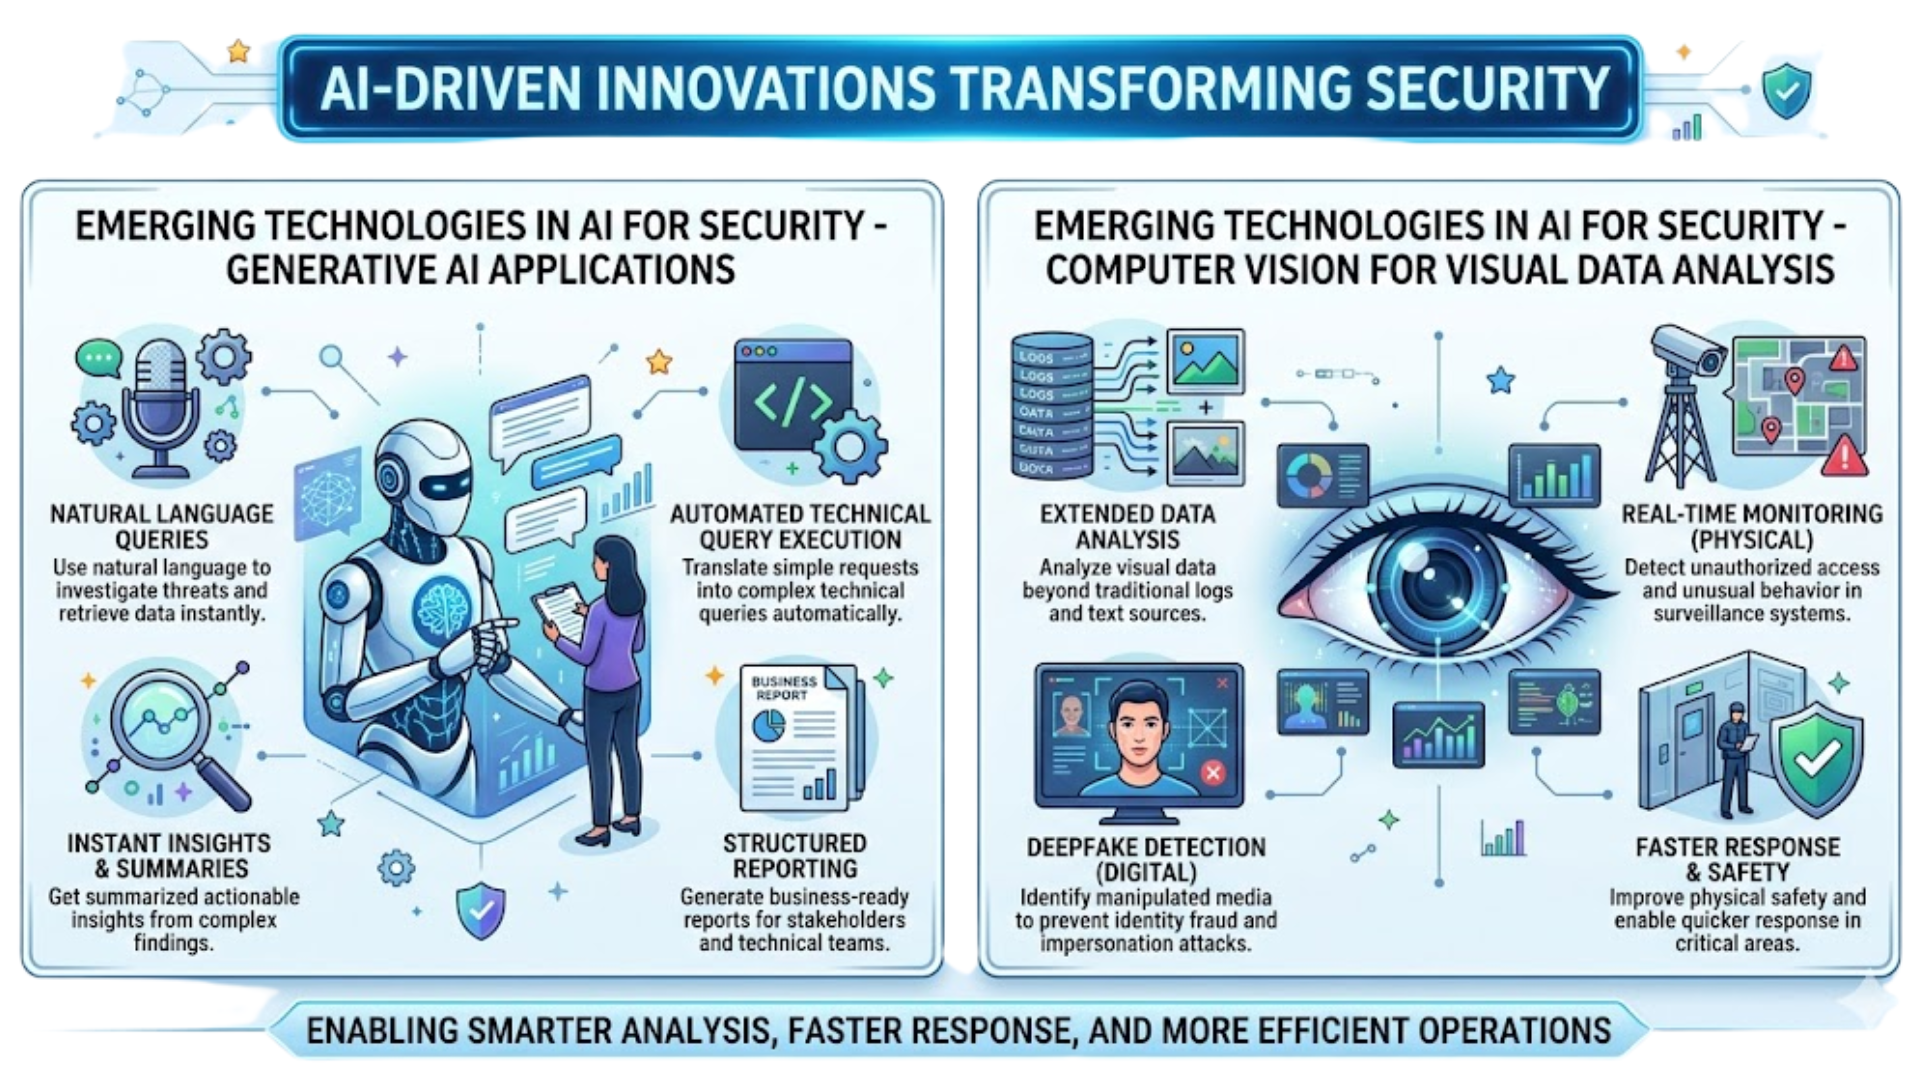
Leverage AI technologies to develop security tools that can autonomously detect and respond to threats in real-time, as highlighted in OpenAI's standards for AI.
Industry Collaboration
Organizations should collaborate to share threat intelligence and develop standardized security frameworks for AI systems, as emphasized by Governor Newsom's executive order on AI oversight.
Conclusion
The potential for AI exploits highlights the importance of proactive security measures. By understanding vulnerabilities and implementing robust security strategies, organizations can safeguard their AI systems and maintain trust in these transformative technologies.
FAQ
What are AI exploits?
AI exploits are vulnerabilities in AI systems that attackers can manipulate to control or alter the AI's behavior.
How can organizations protect against AI exploits?
Organizations can protect against AI exploits by implementing security audits, data validation, access controls, and continuous monitoring.
What are the consequences of AI exploits?
Consequences can range from operational disruptions to compromised data integrity and unauthorized access to sensitive information.
Are there any tools to help detect AI exploits?
Yes, there are AI-powered security tools that can autonomously detect and respond to potential threats in real-time.
How important is industry collaboration in AI security?
Industry collaboration is crucial for sharing threat intelligence and developing standardized security frameworks for AI systems.
What role does data play in AI security?
Data is a critical component of AI security, as malicious data can be used to manipulate AI behavior. Rigorous data validation is essential.
What future trends should organizations be aware of in AI security?
Organizations should be aware of the evolving tactics used by attackers and the potential for AI-powered security tools to enhance protection.
Key Takeaways
- AI systems are vulnerable to exploits that can compromise their functioning and security.
- Implementing robust security measures is essential to protect AI agents from unauthorized access.
- Continuous monitoring and rapid response are key to managing AI security incidents.
- As AI evolves, so will the tactics used by attackers, necessitating ongoing vigilance.
- Industry-wide collaboration is essential to develop effective security standards for AI technologies.
- AI-powered security tools can autonomously detect and respond to threats in real-time.
- Organizations should incorporate security features into AI's architecture from the outset.
- Educating staff on AI security best practices and potential threats is crucial.
Related Articles
- The Impact of Infrastructure Failures on Air Travel: Lessons from a Cable Cut [2025]
- Patti Harrison Had Dreams of a Tech Utopia. Silicon Valley Smashed Them | WIRED
- How to Use AI With Your Privacy Intact | WIRED
- Apple's Bold Leap into Live Music: The New Era of Immersive Experiences [2025]
- Why It's Important To Unplug Your PC During A Power Outage [2025]
- X Now Tells Users When Local Laws Affect Post Visibility [2025]


