
Skullcandy Earbuds Bluetooth Security Flaw: What You Need to Know [2025]
Last month, a surprising discovery about Skullcandy's popular line of earbuds sent shockwaves through the tech community. These affordable devices, known for their sound quality and design, were found to have a troubling Bluetooth flaw that could allow unintended connections. This article dives deep into the technical details of this flaw, its implications, and what you can do to safeguard your devices.
TL; DR
- Skullcandy's vulnerability: A Bluetooth flaw that could let unauthorized devices connect, as detailed by Cybersecurity News.
- Firmware limitations: Unlike Apple, Skullcandy cannot remotely fix this issue, as noted in HotHardware's report.
- Security best practices: Steps to mitigate risks and protect your devices.
- Industry insights: How Bluetooth vulnerabilities affect other tech.
- Future trends: What to expect in Bluetooth security advancements.

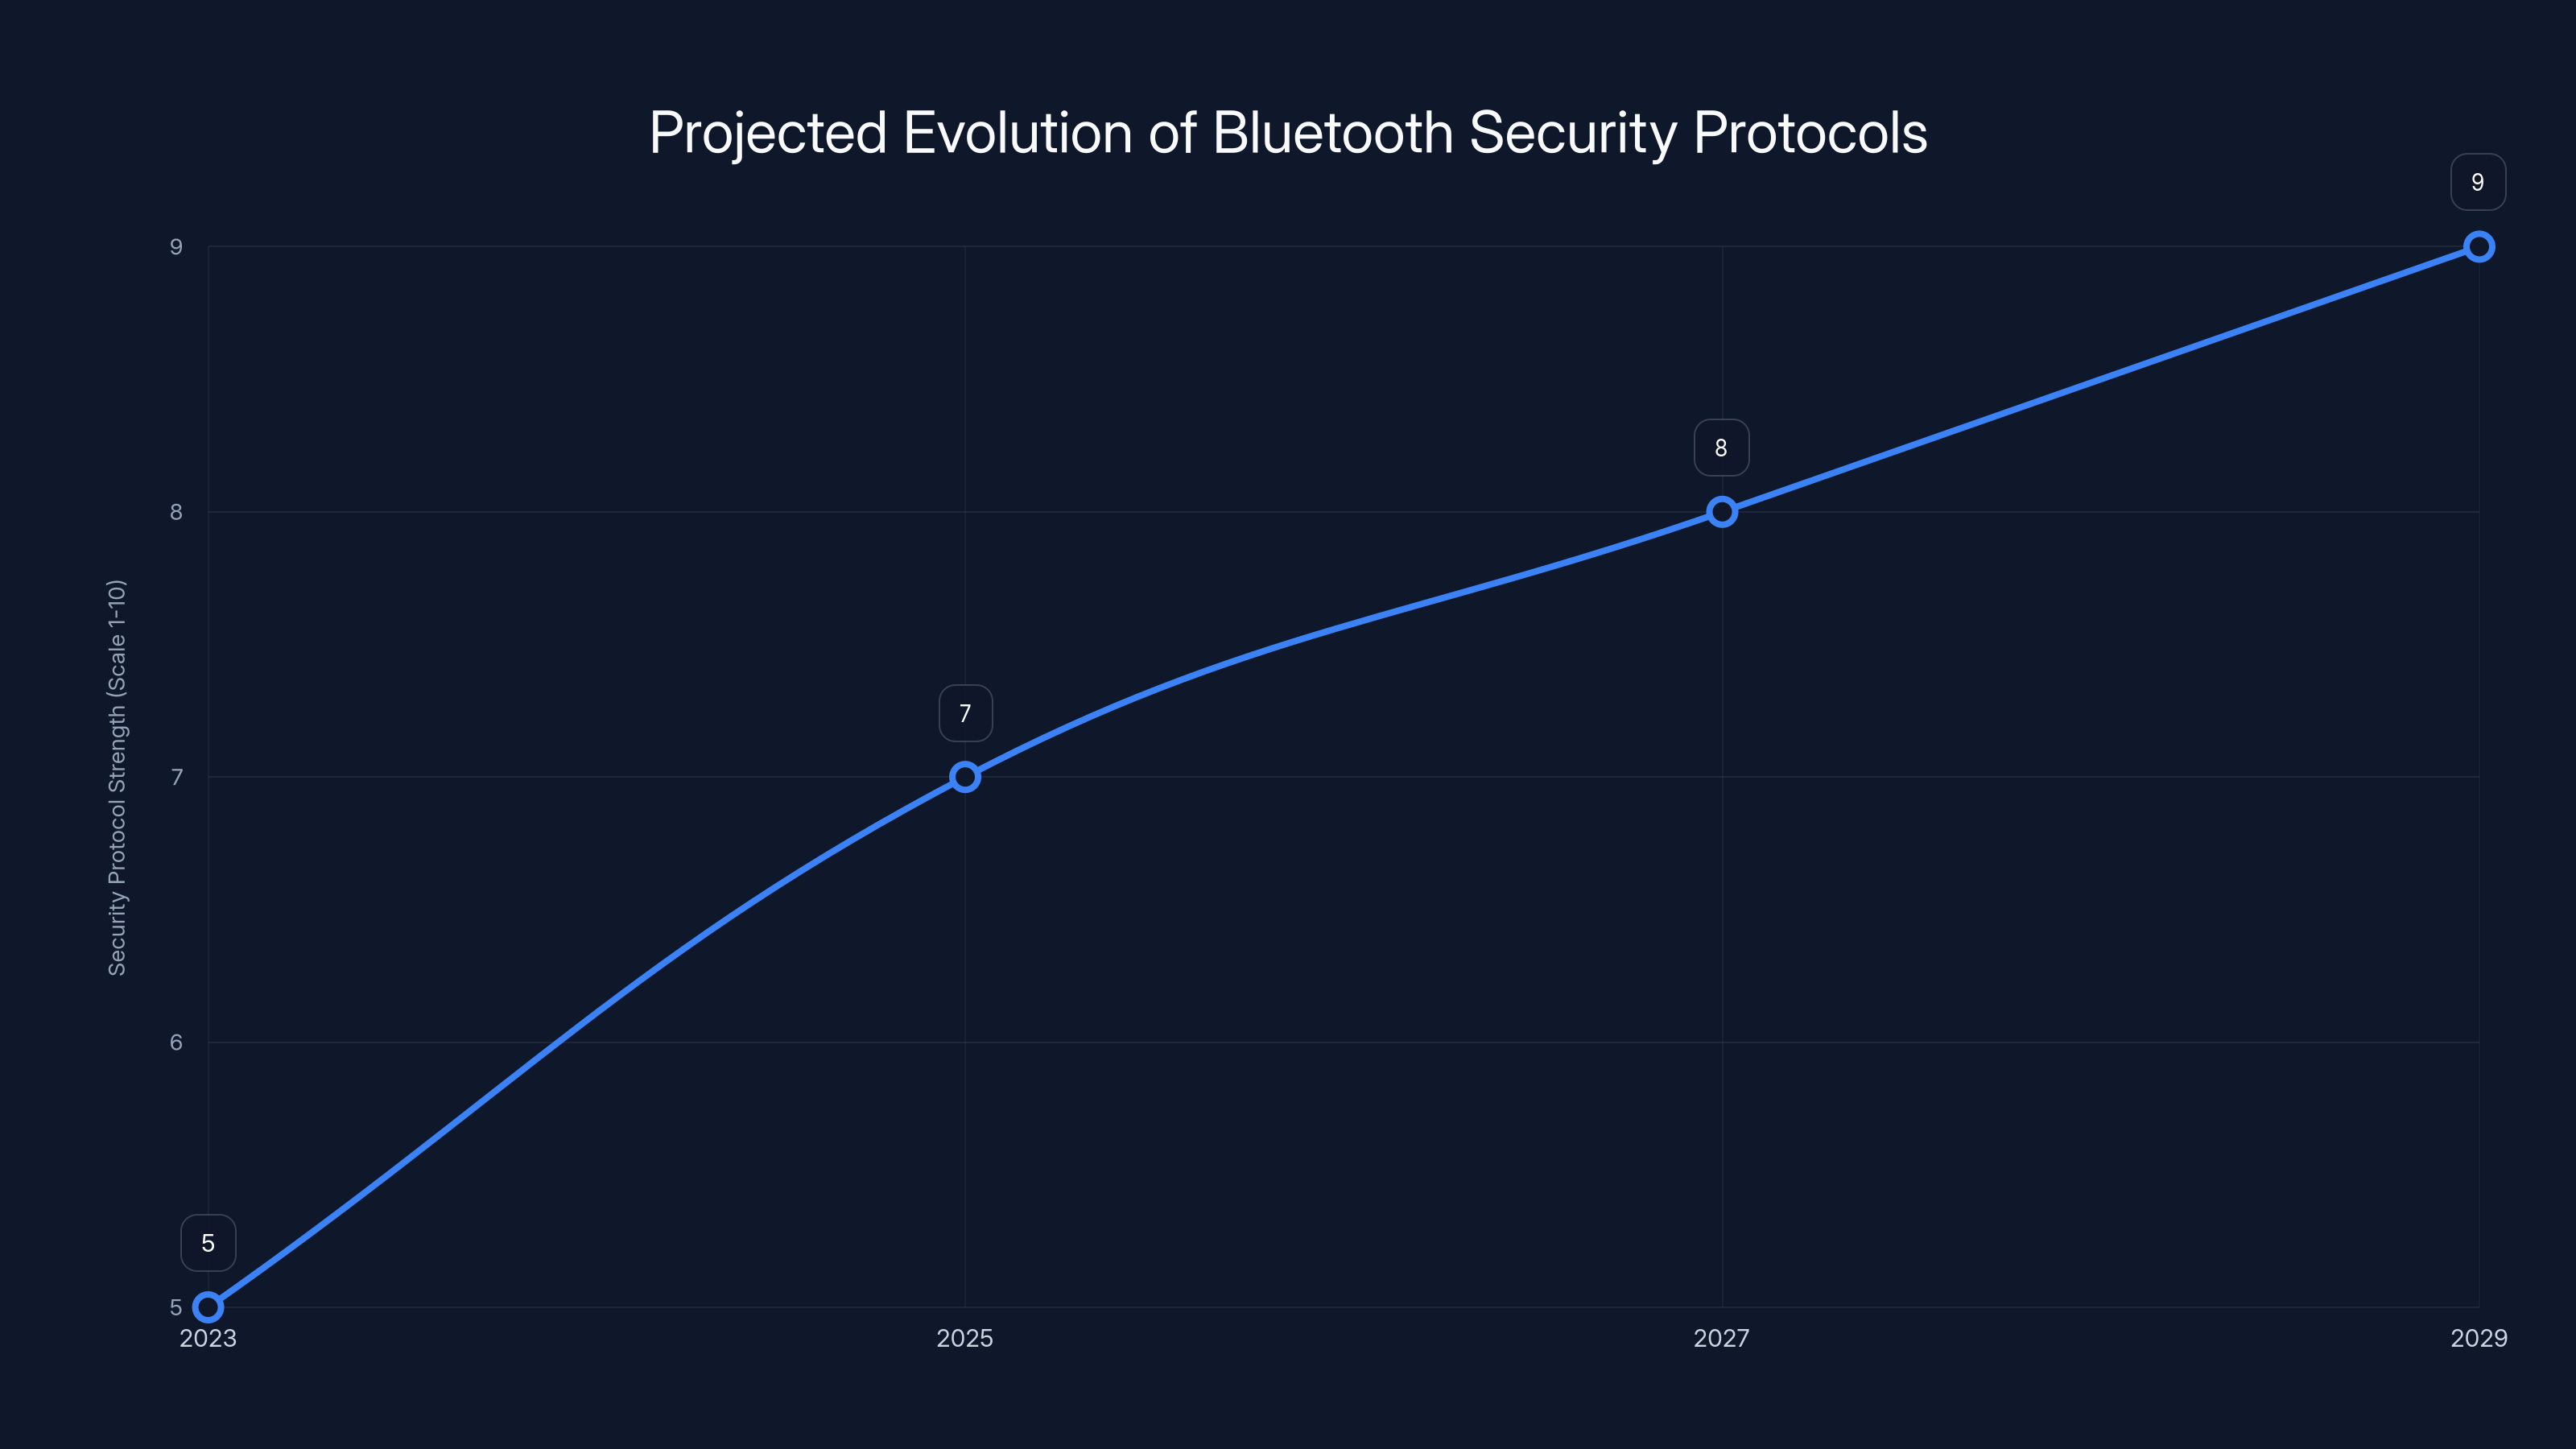
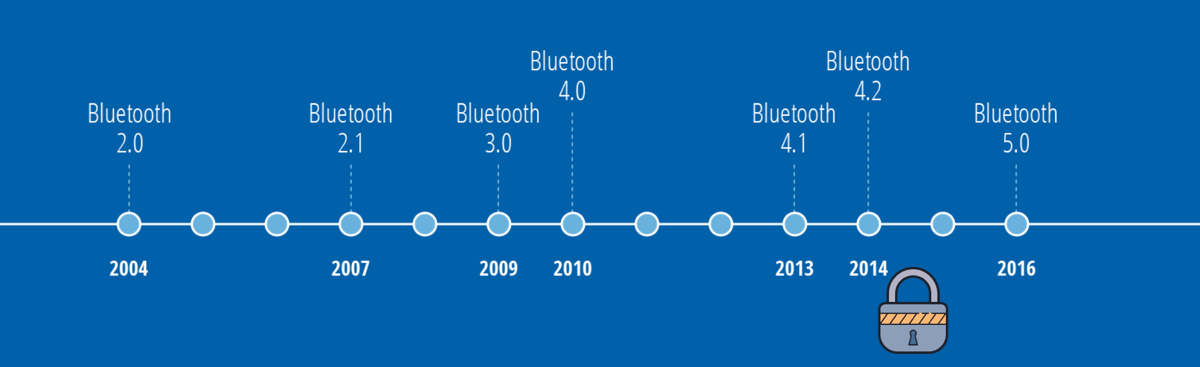
The strength of Bluetooth security protocols is expected to improve significantly by 2029, with enhancements in encryption and AI-driven security measures. (Estimated data)
Understanding the Bluetooth Flaw
The flaw discovered in Skullcandy's Dime 3 earbuds relates to the device's Bluetooth implementation. In essence, these earbuds are susceptible to accepting pairing requests from any nearby devices without proper authentication checks. This vulnerability arises from outdated firmware that lacks the necessary security protocols, as highlighted by SC World.
Technical Breakdown
Bluetooth technology operates on the 2.4 GHz ISM band, which is shared by many other wireless devices. This commonality increases the risk of interference and unauthorized access if proper security measures aren't in place. Skullcandy's issue stems from a lack of Secure Simple Pairing (SSP) implementation, which helps ensure that connections are initiated only by authorized devices, according to Make Tech Easier.
Without SSP, the earbuds might accept connections from any device within range, potentially allowing malicious actors to intercept audio streams or inject unwanted audio.
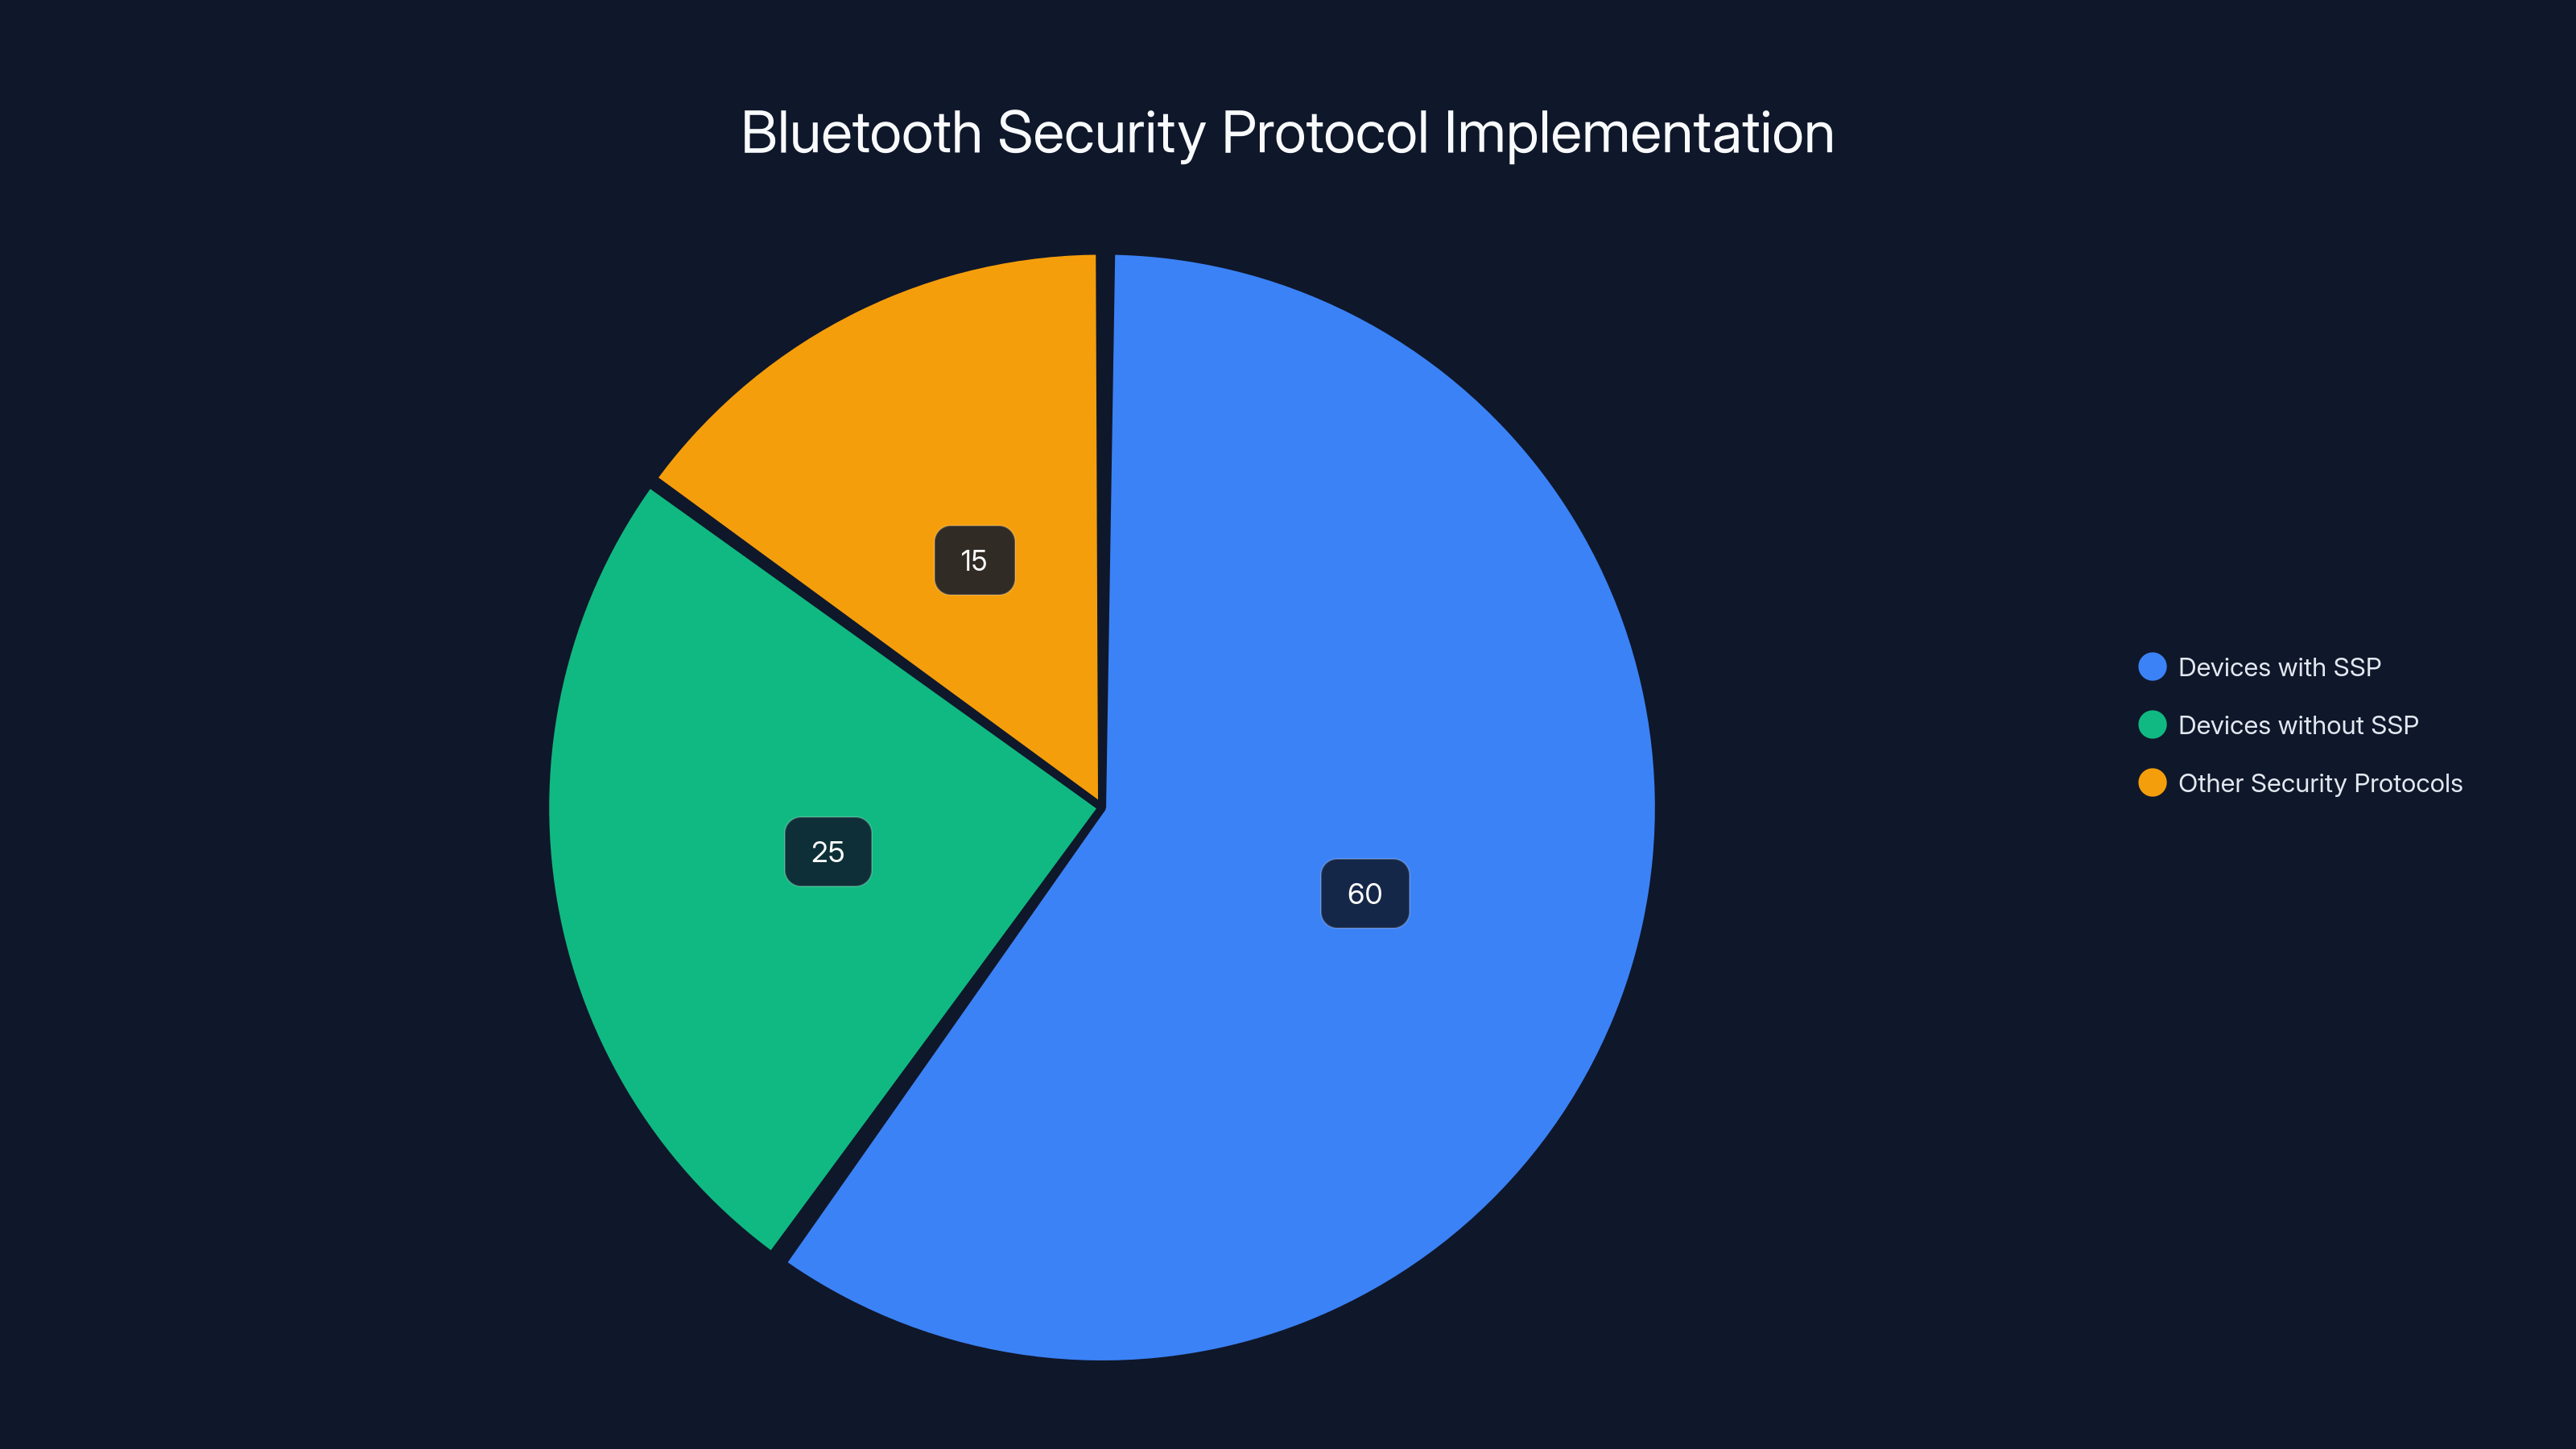
Estimated data shows that 25% of devices lack SSP, increasing vulnerability to unauthorized access.
Real-World Implications
Imagine you're on a crowded train, listening to your favorite playlist, when suddenly, someone nearby connects their device to your Skullcandy earbuds. This scenario, while unlikely, is possible due to the Bluetooth flaw. Beyond mere inconvenience, this vulnerability poses risks such as:
- Data interception: Malicious actors could intercept audio transmissions, compromising privacy, as noted by HotHardware.
- Device manipulation: Unauthorized users might inject audio, disrupting your listening experience.
- Battery drain: Unwanted connections can quickly deplete your earbuds' battery, leaving you without music.
Common Pitfalls and Solutions
Pitfalls
- Outdated Firmware: Many consumers overlook firmware updates, which can leave devices vulnerable, as discussed in Forbes.
- Default Settings: Using default Bluetooth settings often lacks adequate security.
- Public Spaces: Increased risk of unauthorized access in crowded areas.
Solutions
- Manual Firmware Updates: Regularly check for updates on the Skullcandy website and manually install them.
- Bluetooth Visibility: Set your device to 'non-discoverable' mode when not pairing.
- Awareness: Stay informed about security updates and threats to your devices.
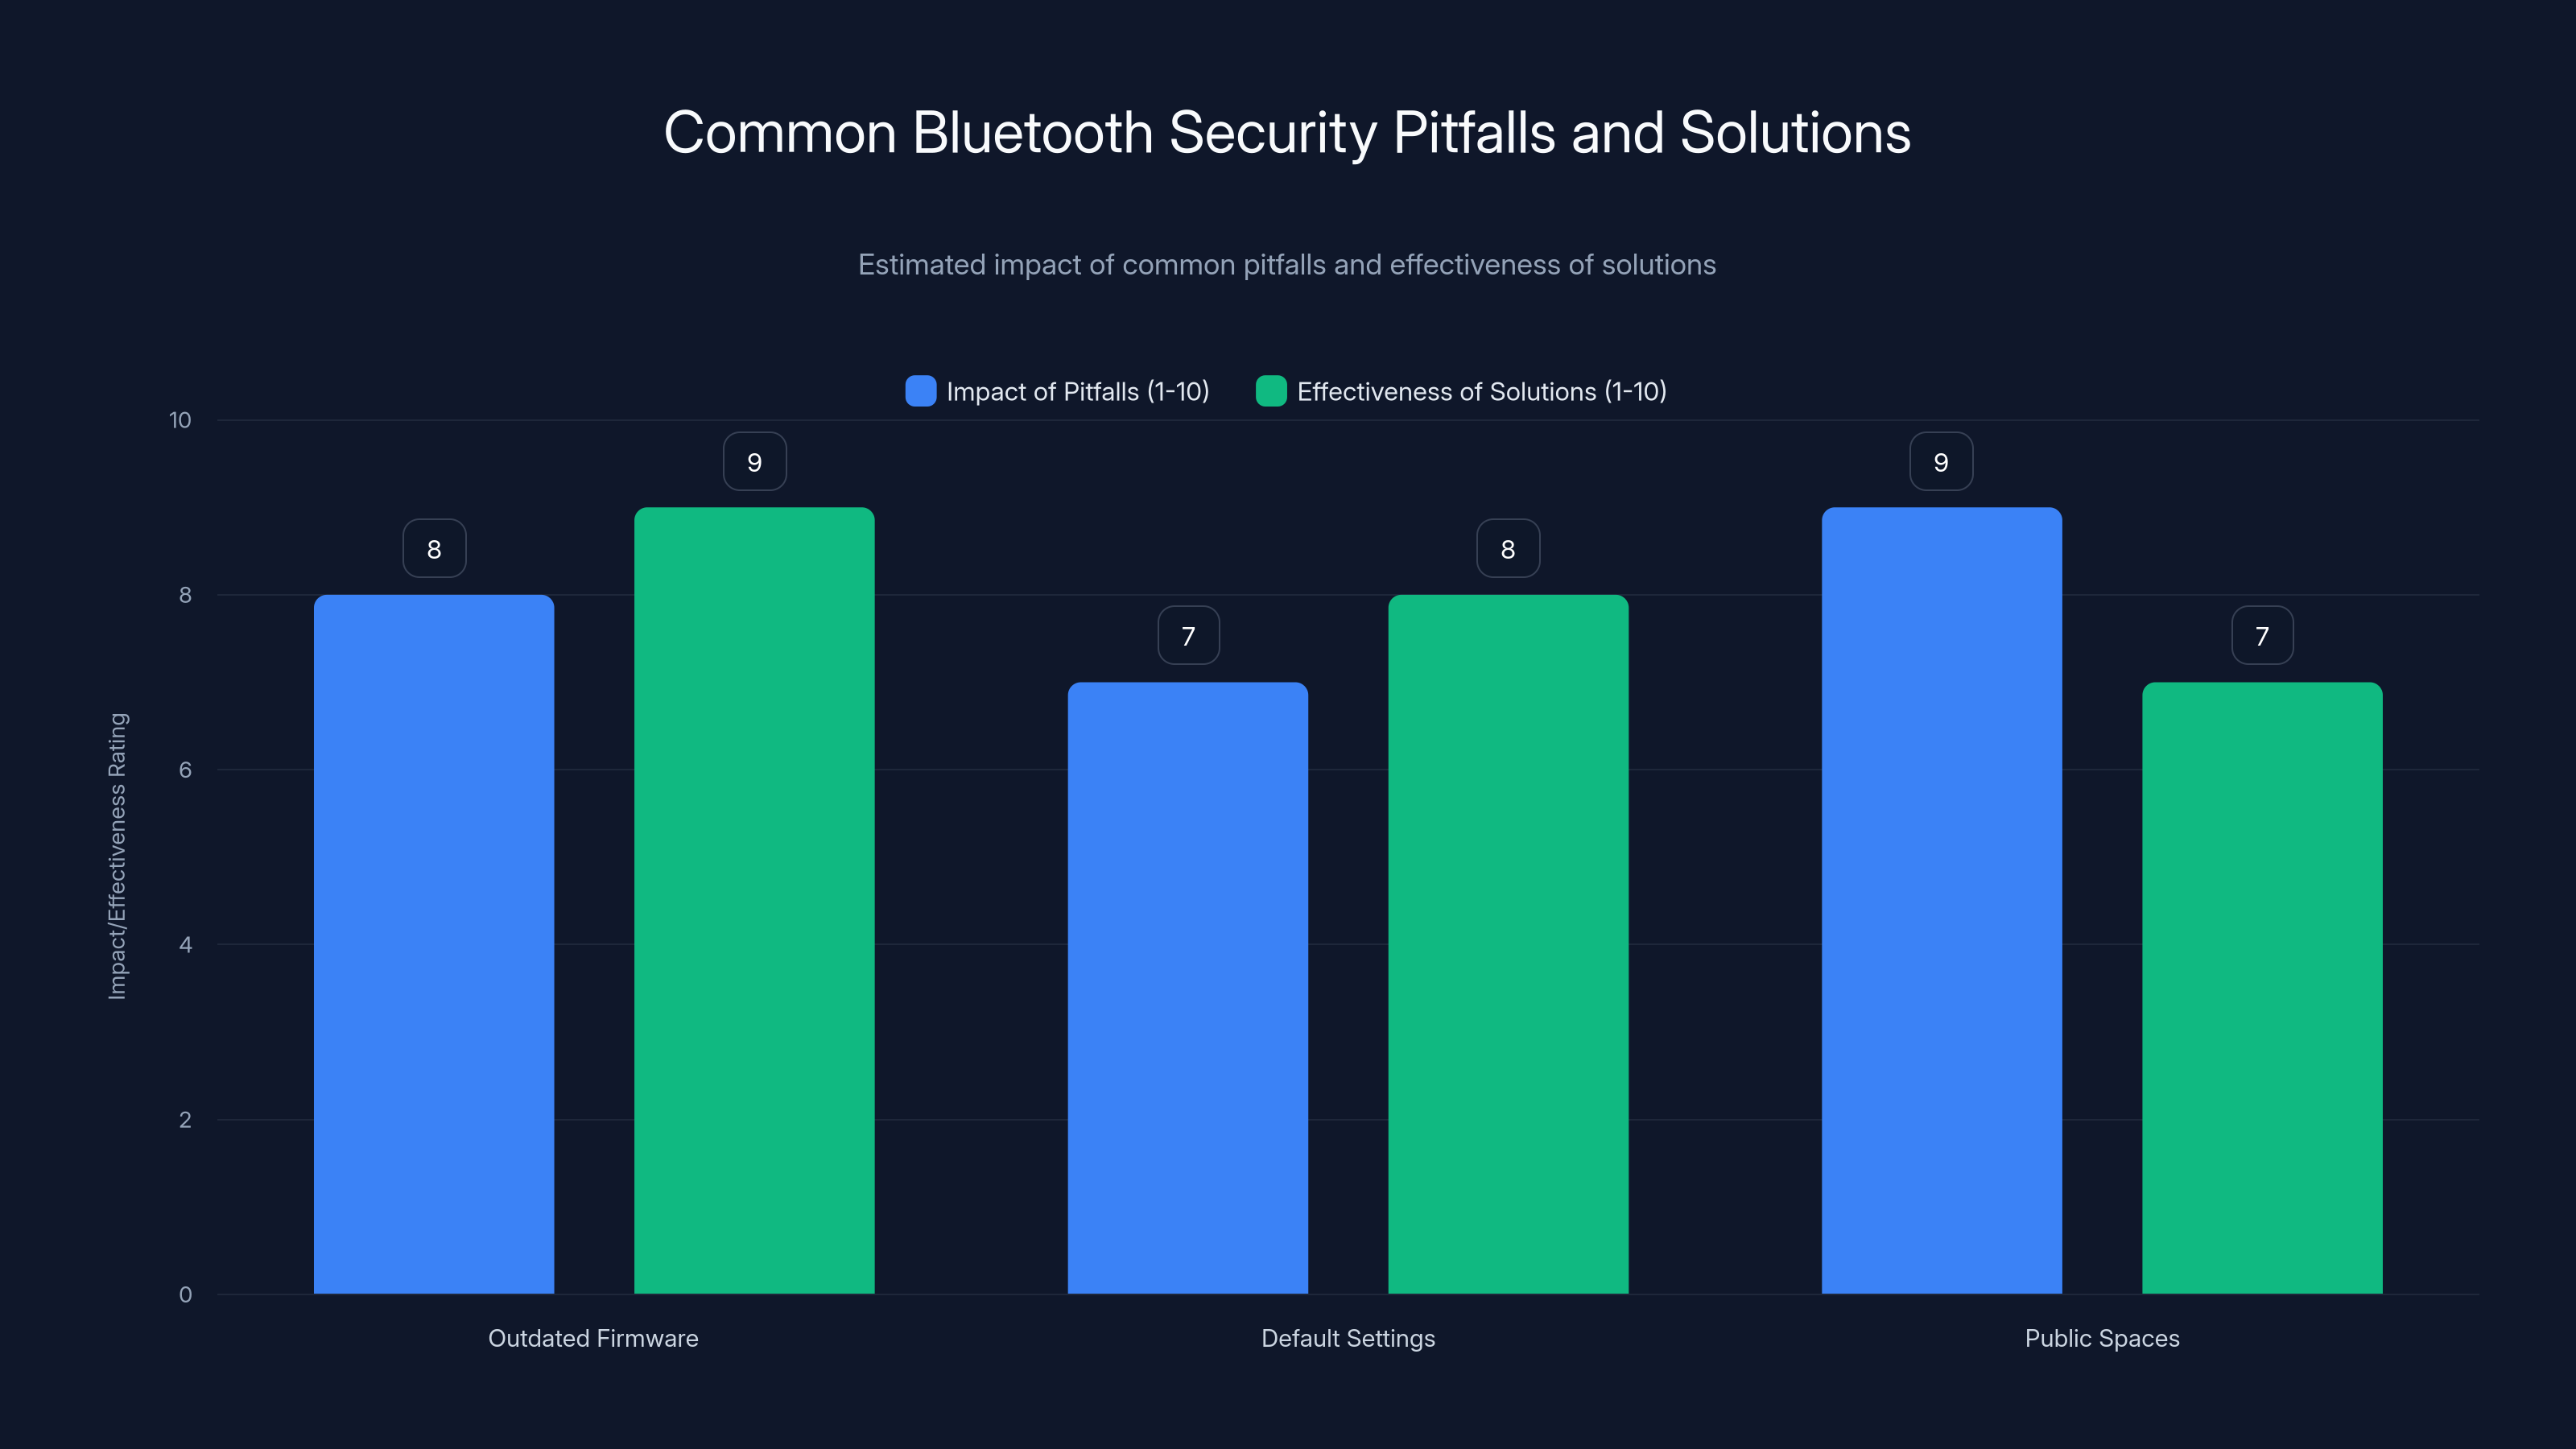
Outdated firmware and public spaces pose the highest security risks, but manual updates and awareness can effectively mitigate these issues. (Estimated data)
The Broader Context of Bluetooth Security
Bluetooth technology is ubiquitous, found in everything from smartphones to smart home devices. However, its widespread use also makes it a target for security vulnerabilities. Here's how the Skullcandy flaw fits into the larger picture:
Industry-Wide Challenges
- Complex Ecosystem: The diversity of Bluetooth-enabled devices makes standardizing security across the board challenging.
- Backward Compatibility: Maintaining compatibility with older devices often compromises security, as explained by Engadget.
- User Awareness: Many users are unaware of how to implement basic security measures.
Solutions and Best Practices
- Enhanced Security Protocols: Implementing SSP and encryption can mitigate many risks.
- User Education: Providing clear instructions on securing Bluetooth devices is crucial.
- Regular Audits: Manufacturers should conduct regular security audits to identify and patch vulnerabilities.
Future Trends in Bluetooth Security
Enhanced Security Protocols
The Bluetooth Special Interest Group (SIG) is continuously working on improving security standards. Future iterations of Bluetooth technology are expected to include more robust encryption and authentication methods.
AI-Driven Security
Artificial Intelligence (AI) is poised to play a significant role in Bluetooth security. AI can help detect unusual pairing attempts and alert users in real time.
Integrated Security Features
As technology advances, we can expect more devices to feature built-in security tools that automatically manage Bluetooth connections and alert users to potential threats.
Practical Implementation Guides
Setting Up Secure Bluetooth Connections
- Initial Pairing: Always perform the initial pairing in a secure environment.
- Use a PIN: Set up a PIN or passkey when pairing devices.
- Forget Unused Devices: Regularly check and remove devices you no longer use from your Bluetooth settings.
Monitoring and Managing Connections
- Third-Party Apps: Use apps that can monitor Bluetooth activity and alert you to suspicious connections.
- Security Audits: Conduct regular security audits on your devices to ensure they are not vulnerable to attacks.
Recommendations for Skullcandy
Skullcandy can take several steps to address this issue and improve customer confidence:
- Firmware Updates: Develop a method for remotely updating firmware, similar to how Apple manages its devices.
- User Education: Provide clear guides on securing Bluetooth connections and recognizing threats.
- Partnerships: Collaborate with cybersecurity firms to enhance device security.
Conclusion
The Bluetooth flaw in Skullcandy earbuds highlights the larger issue of security in wireless technologies. While it poses a significant risk, understanding the vulnerabilities and taking proactive steps can mitigate these dangers. As the industry continues to evolve, manufacturers and consumers alike must prioritize security to protect their devices and personal information.
FAQ
What is the Bluetooth flaw in Skullcandy earbuds?
The flaw allows unauthorized devices to connect to Skullcandy earbuds due to a lack of proper authentication in the Bluetooth implementation, as reported by Cybersecurity News.
How can I protect my Skullcandy earbuds from unauthorized connections?
Keep your device's firmware up-to-date, use secure pairing methods, and disable Bluetooth when not in use.
What are the risks of this Bluetooth flaw?
Unauthorized connections can lead to data interception, device manipulation, and increased battery drain.
How does Bluetooth security work?
Bluetooth security involves encryption and authentication protocols to ensure connections are secure and only authorized devices can pair.
What future trends can improve Bluetooth security?
Enhanced protocols, AI-driven security, and integrated security features are expected to bolster Bluetooth security in the coming years.
Why can't Skullcandy fix this flaw remotely?
Skullcandy currently lacks the infrastructure to push firmware updates remotely, unlike companies like Apple, as noted by HotHardware.
Key Takeaways
- Skullcandy earbuds have a Bluetooth flaw allowing unauthorized access.
- Firmware updates are essential to secure Bluetooth devices.
- Users should practice safe Bluetooth habits to mitigate risks.
- Future Bluetooth security will involve AI and enhanced protocols.
- Manufacturers need remote update capabilities for quick fixes.
Related Articles
- Exploring Apple Home's New Security Camera Features: Costs, Benefits, and Future Trends [2025]
- Valve Steam Frame Review: A Promising VR Headset Arriving in a Saturated Market [2025]
- iOS 27 Unveiled: Transforming Siri with AI Advancements [2025]
- USB-C vs 3.5mm: Which Offers Superior Audio Quality? [2025]
- Sexually Explicit Deepfake Sites Target 100-Plus Politicians in Europe | WIRED
- Maximize Your Savings: Samsung's Big Cashback Offer on Galaxy Devices [2025]


