
Understanding Salt Typhoon: China's Cyber Espionage and the Sparro Wocky Backdoor [2025]
In the intricate world of cyber espionage, few names evoke as much intrigue and concern as Salt Typhoon. Known for its sophisticated methods and strategic targets, Salt Typhoon has recently shifted its focus to Latin America, deploying the newly developed Sparro Wocky backdoor. This move has not only raised alarms among cybersecurity professionals but has also sparked discussions about the implications of such cyber activities on global politics and national security.
TL; DR
- Salt Typhoon Focus: Recently shifted its cyber espionage focus to Latin American countries like Argentina and Peru.
- Sparro Wocky Backdoor: A newly developed tool with over 30 commands for extensive data extraction and system manipulation.
- Cyber Espionage Impact: Raises geopolitical tensions and concerns over national security in targeted regions.
- Security Measures: Emphasizes the need for robust cybersecurity frameworks and international cooperation.
- Future Trends: Increased sophistication in cyber tools and the need for advanced threat intelligence.
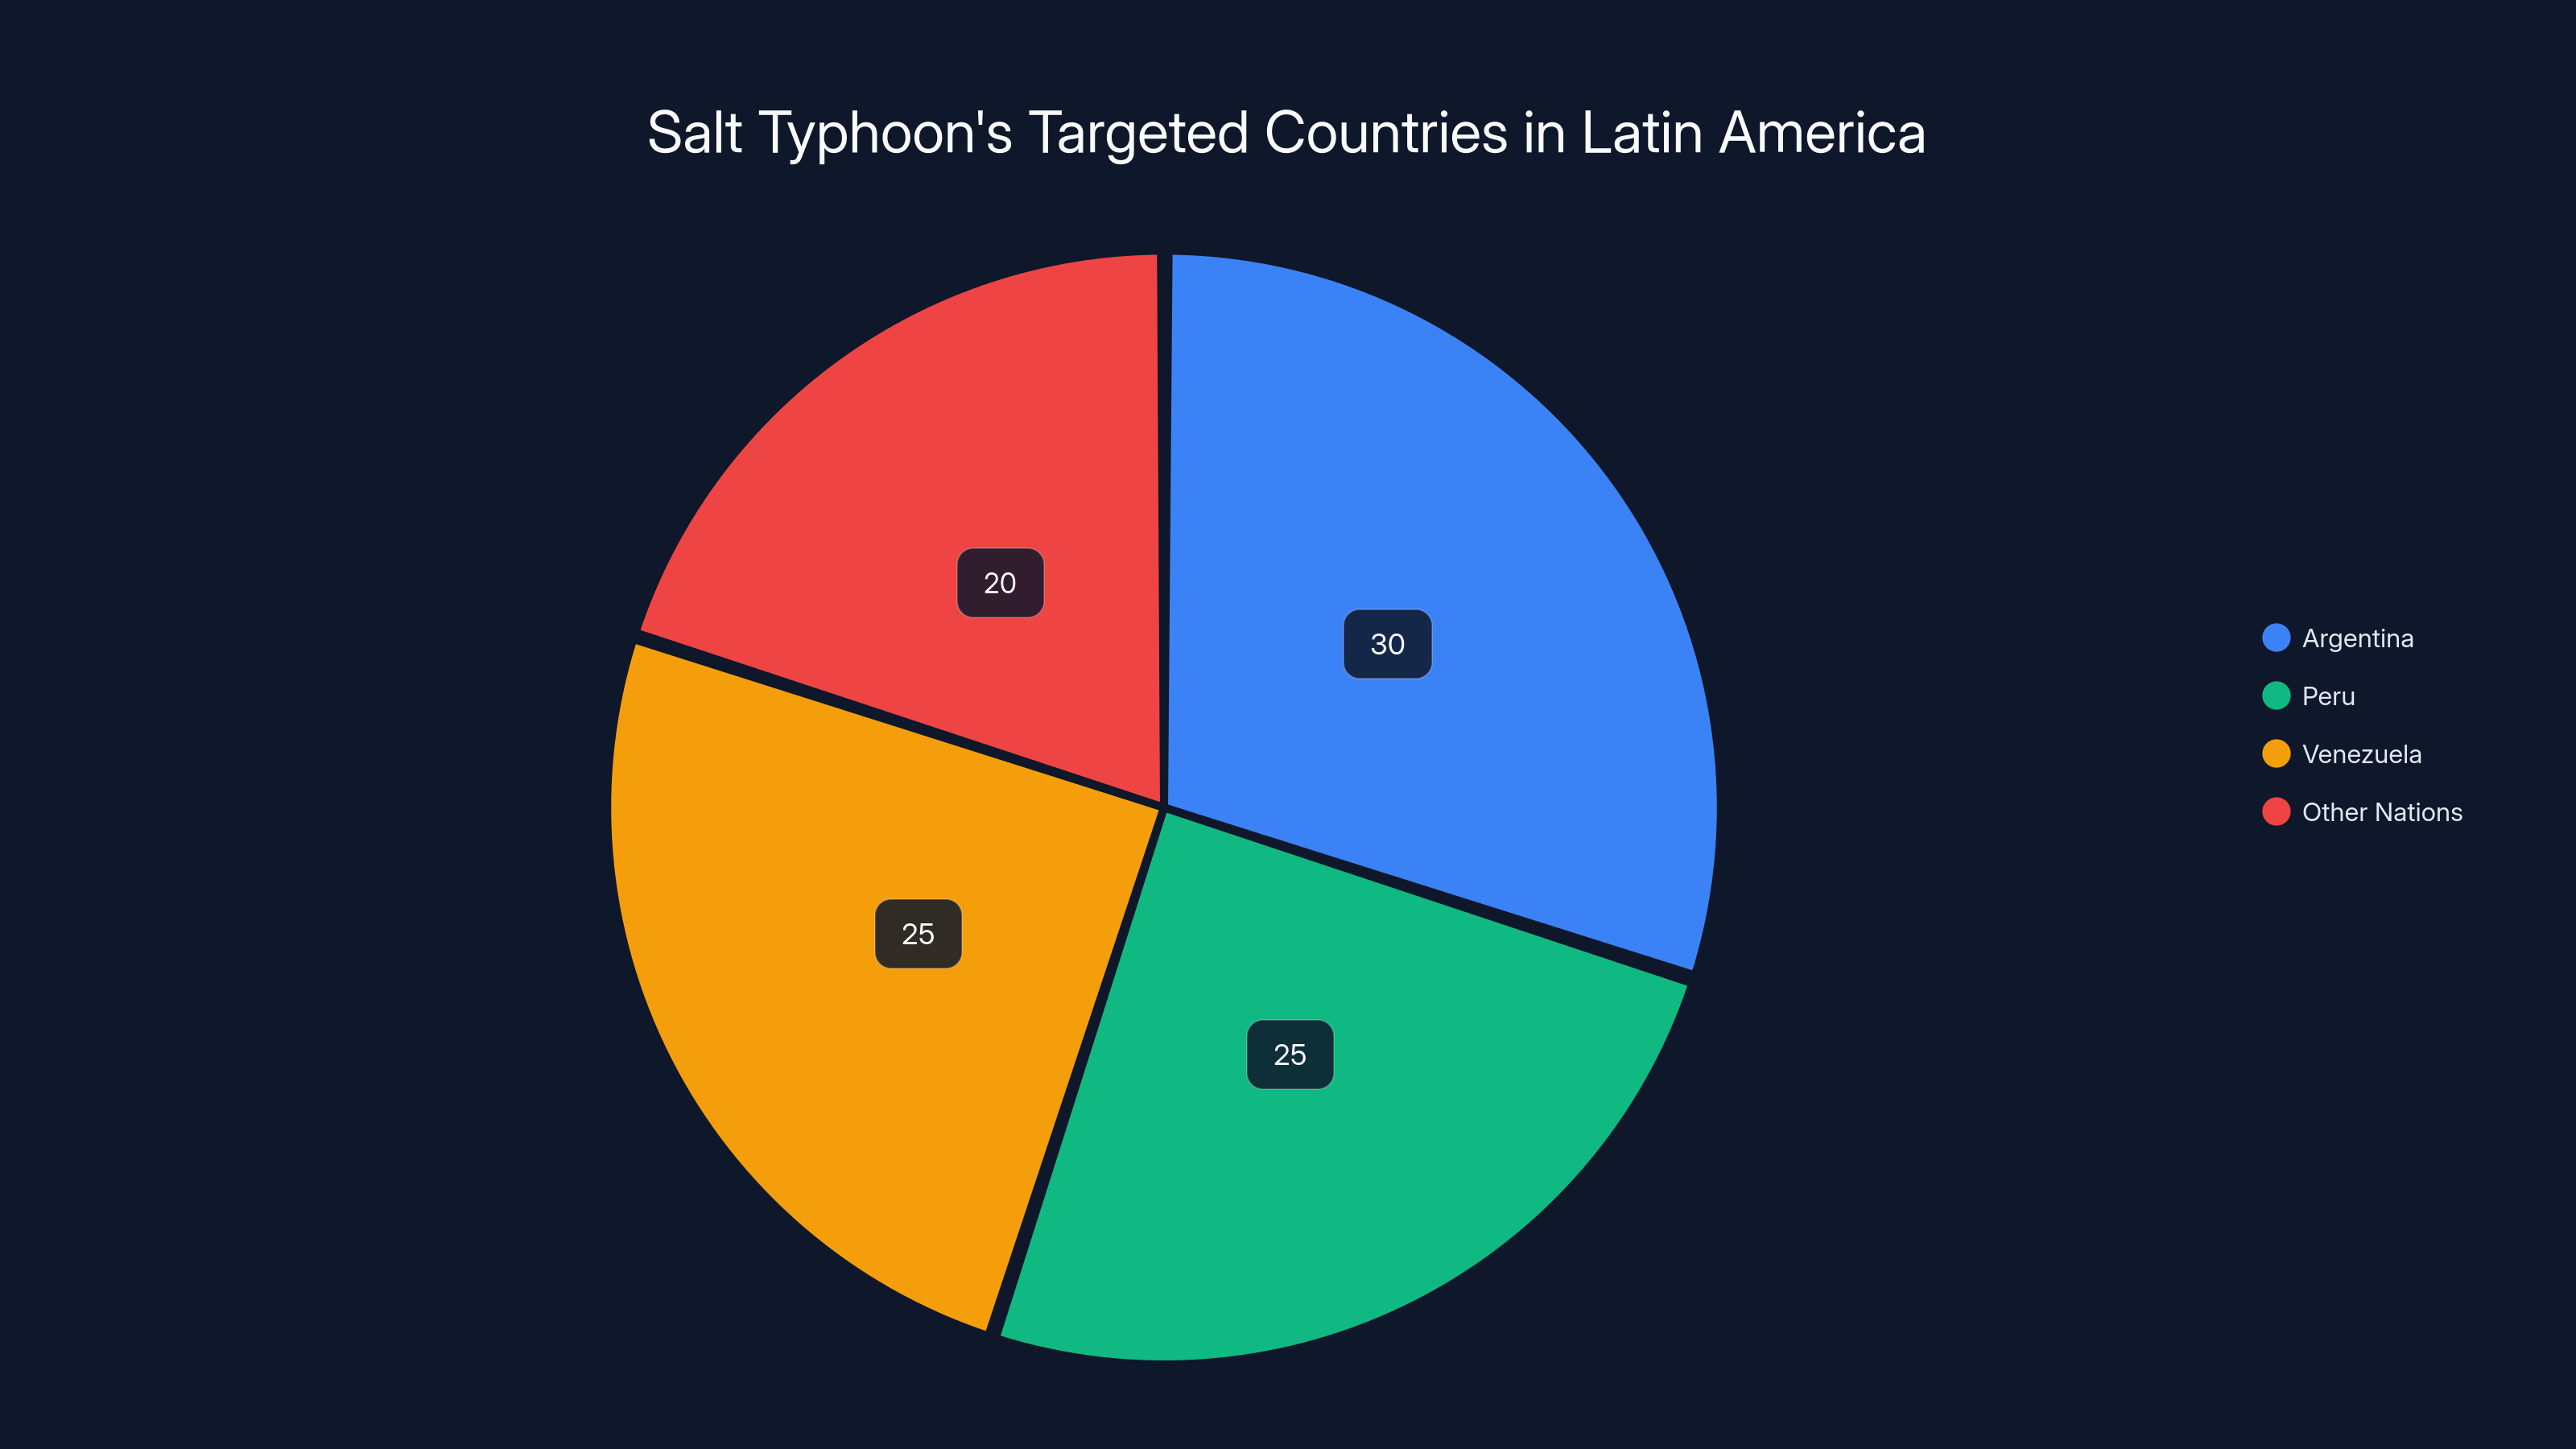
Estimated data shows Argentina, Peru, and Venezuela are primary targets for Salt Typhoon due to their strategic geopolitical and economic roles.
The Rise of Salt Typhoon
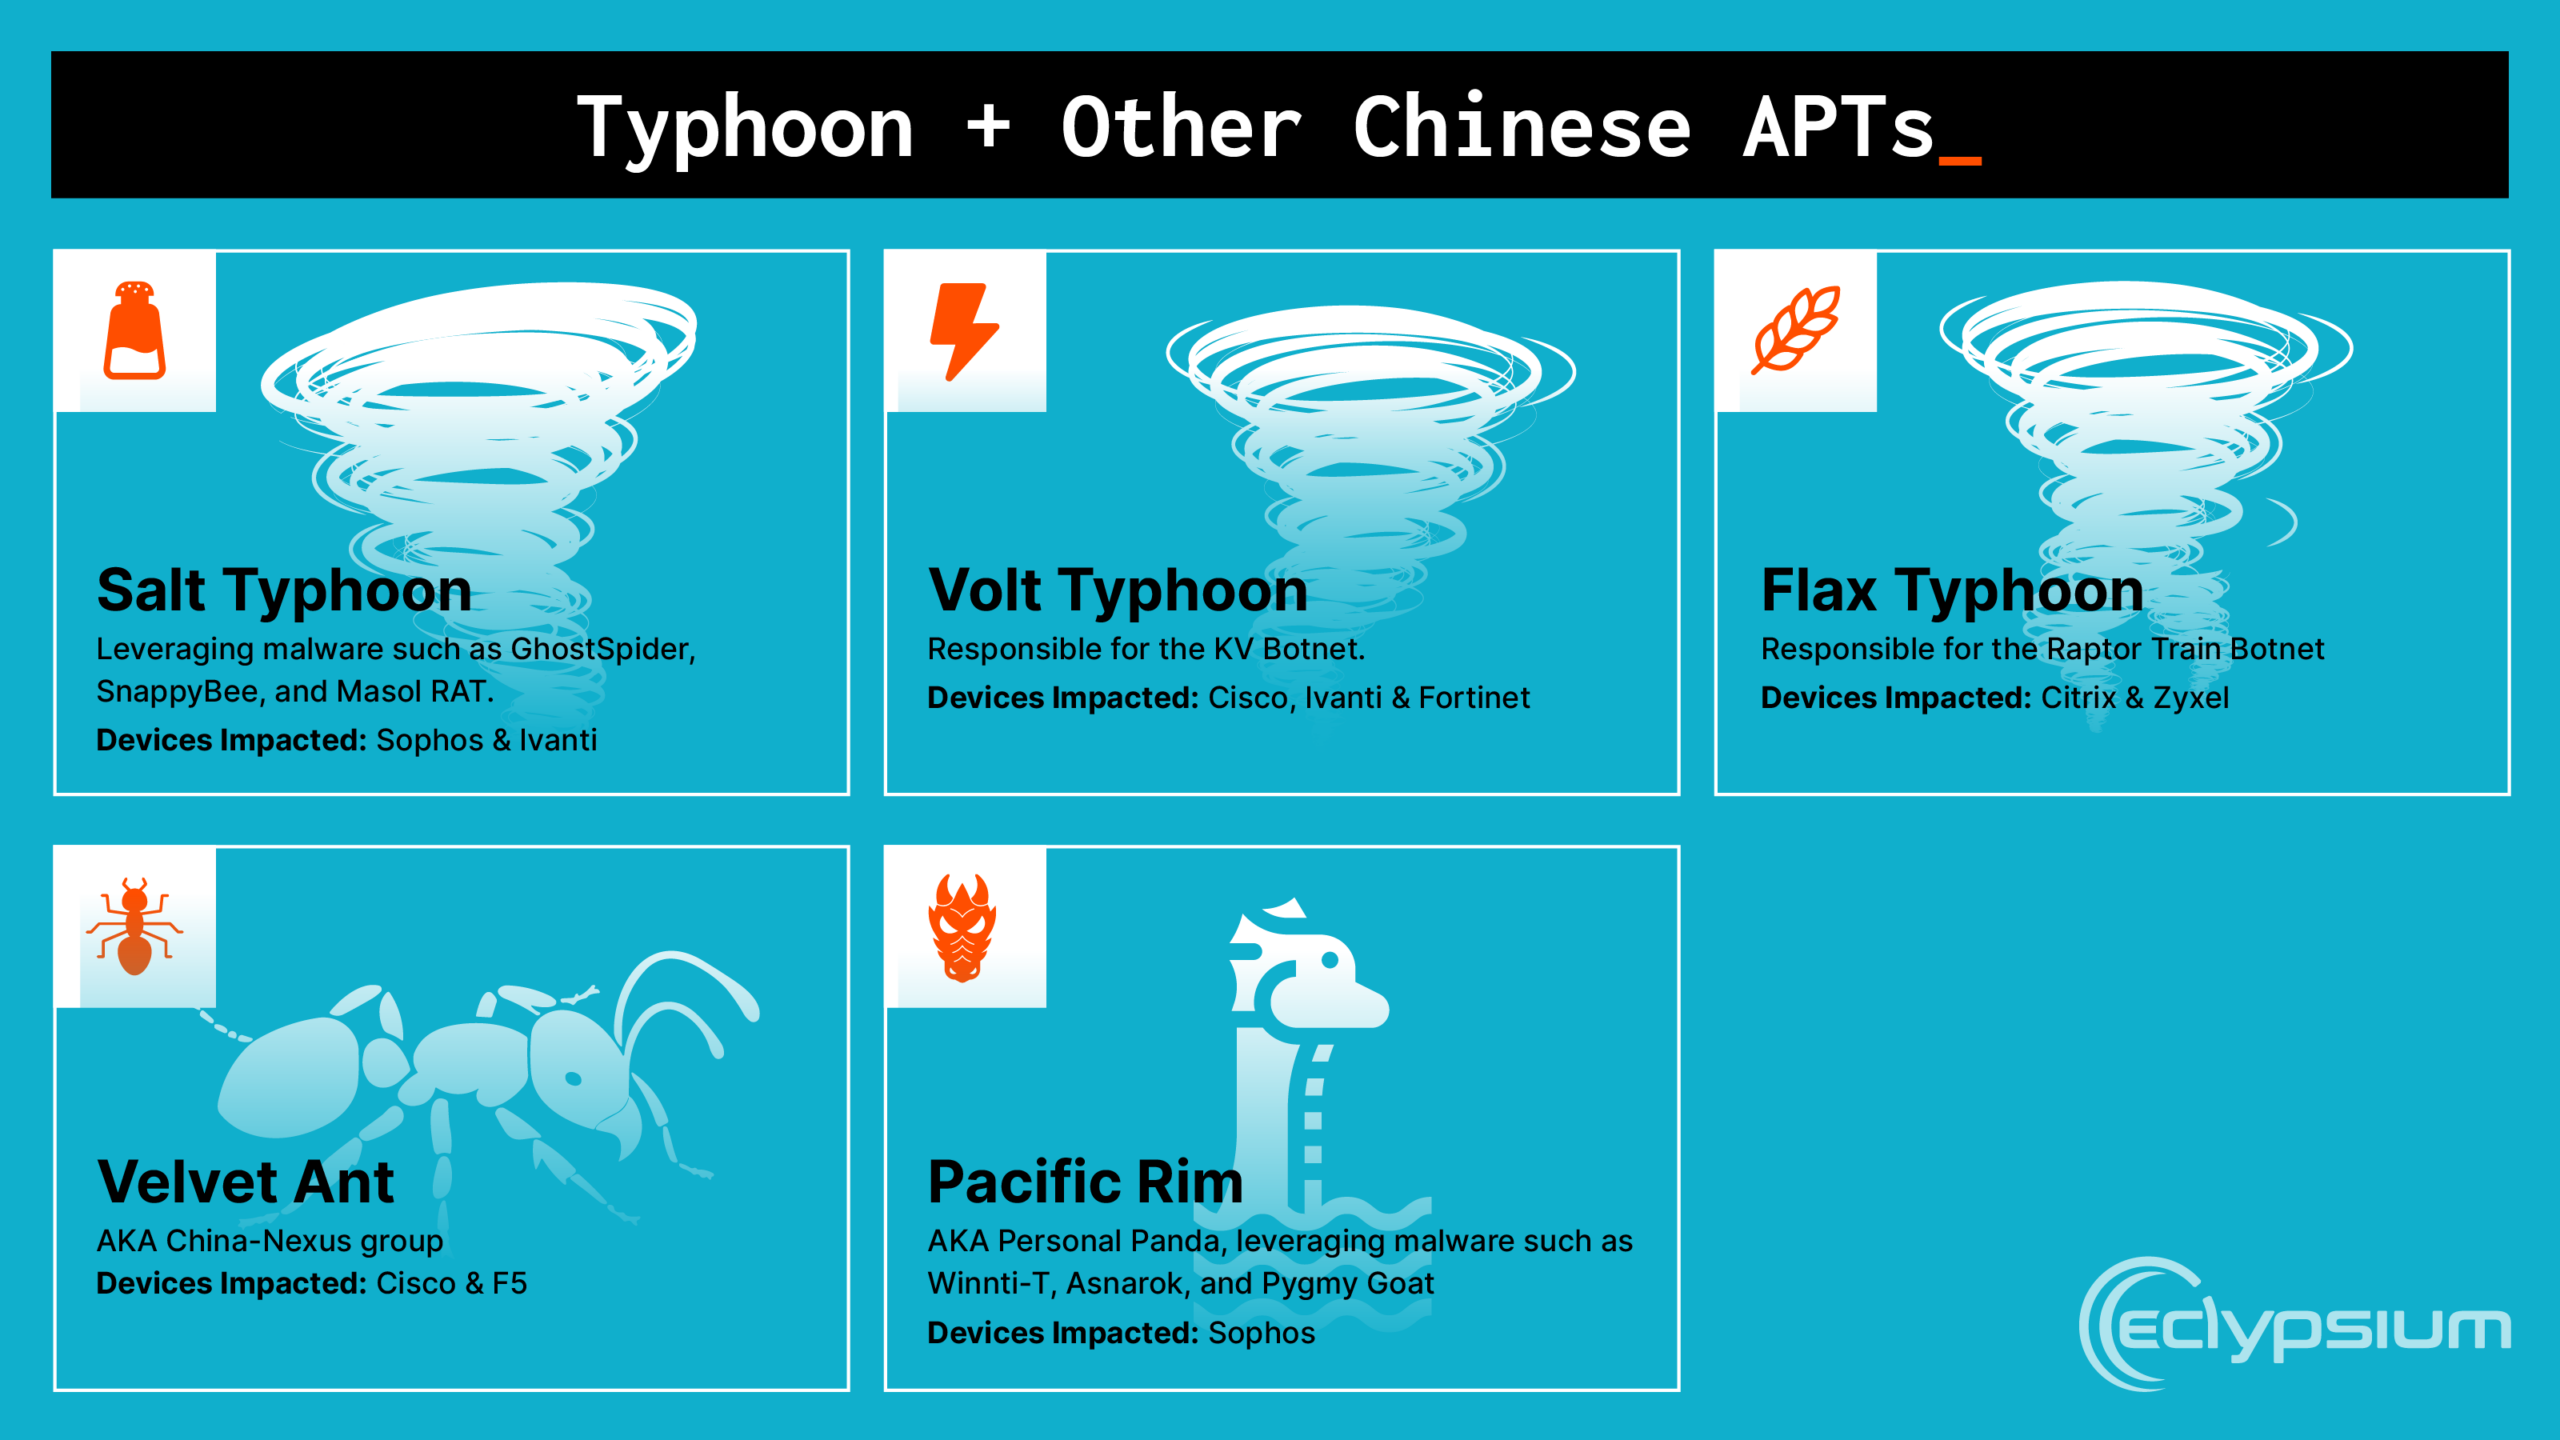
Salt Typhoon, allegedly backed by the Chinese state, has been involved in numerous cyber-espionage campaigns over the years. Their targets have ranged from governmental organizations to critical infrastructure sectors. The group's operations are characterized by their precision, stealth, and adaptability, making them a formidable adversary.
What is Salt Typhoon?
Salt Typhoon is believed to be a state-sponsored cyber-espionage group working out of China. The group has been active for several years, known for targeting government entities, research institutions, and private sector organizations globally. Their operations are typically aimed at gathering intelligence and sensitive data.
Key Characteristics of Salt Typhoon:
- Sophisticated Toolsets: Utilizes advanced malware, zero-day vulnerabilities, and custom backdoors.
- Persistent Threat: Known for long-term infiltration and data exfiltration operations.
- Global Reach: Targets entities across various continents, with recent focus on Latin America.
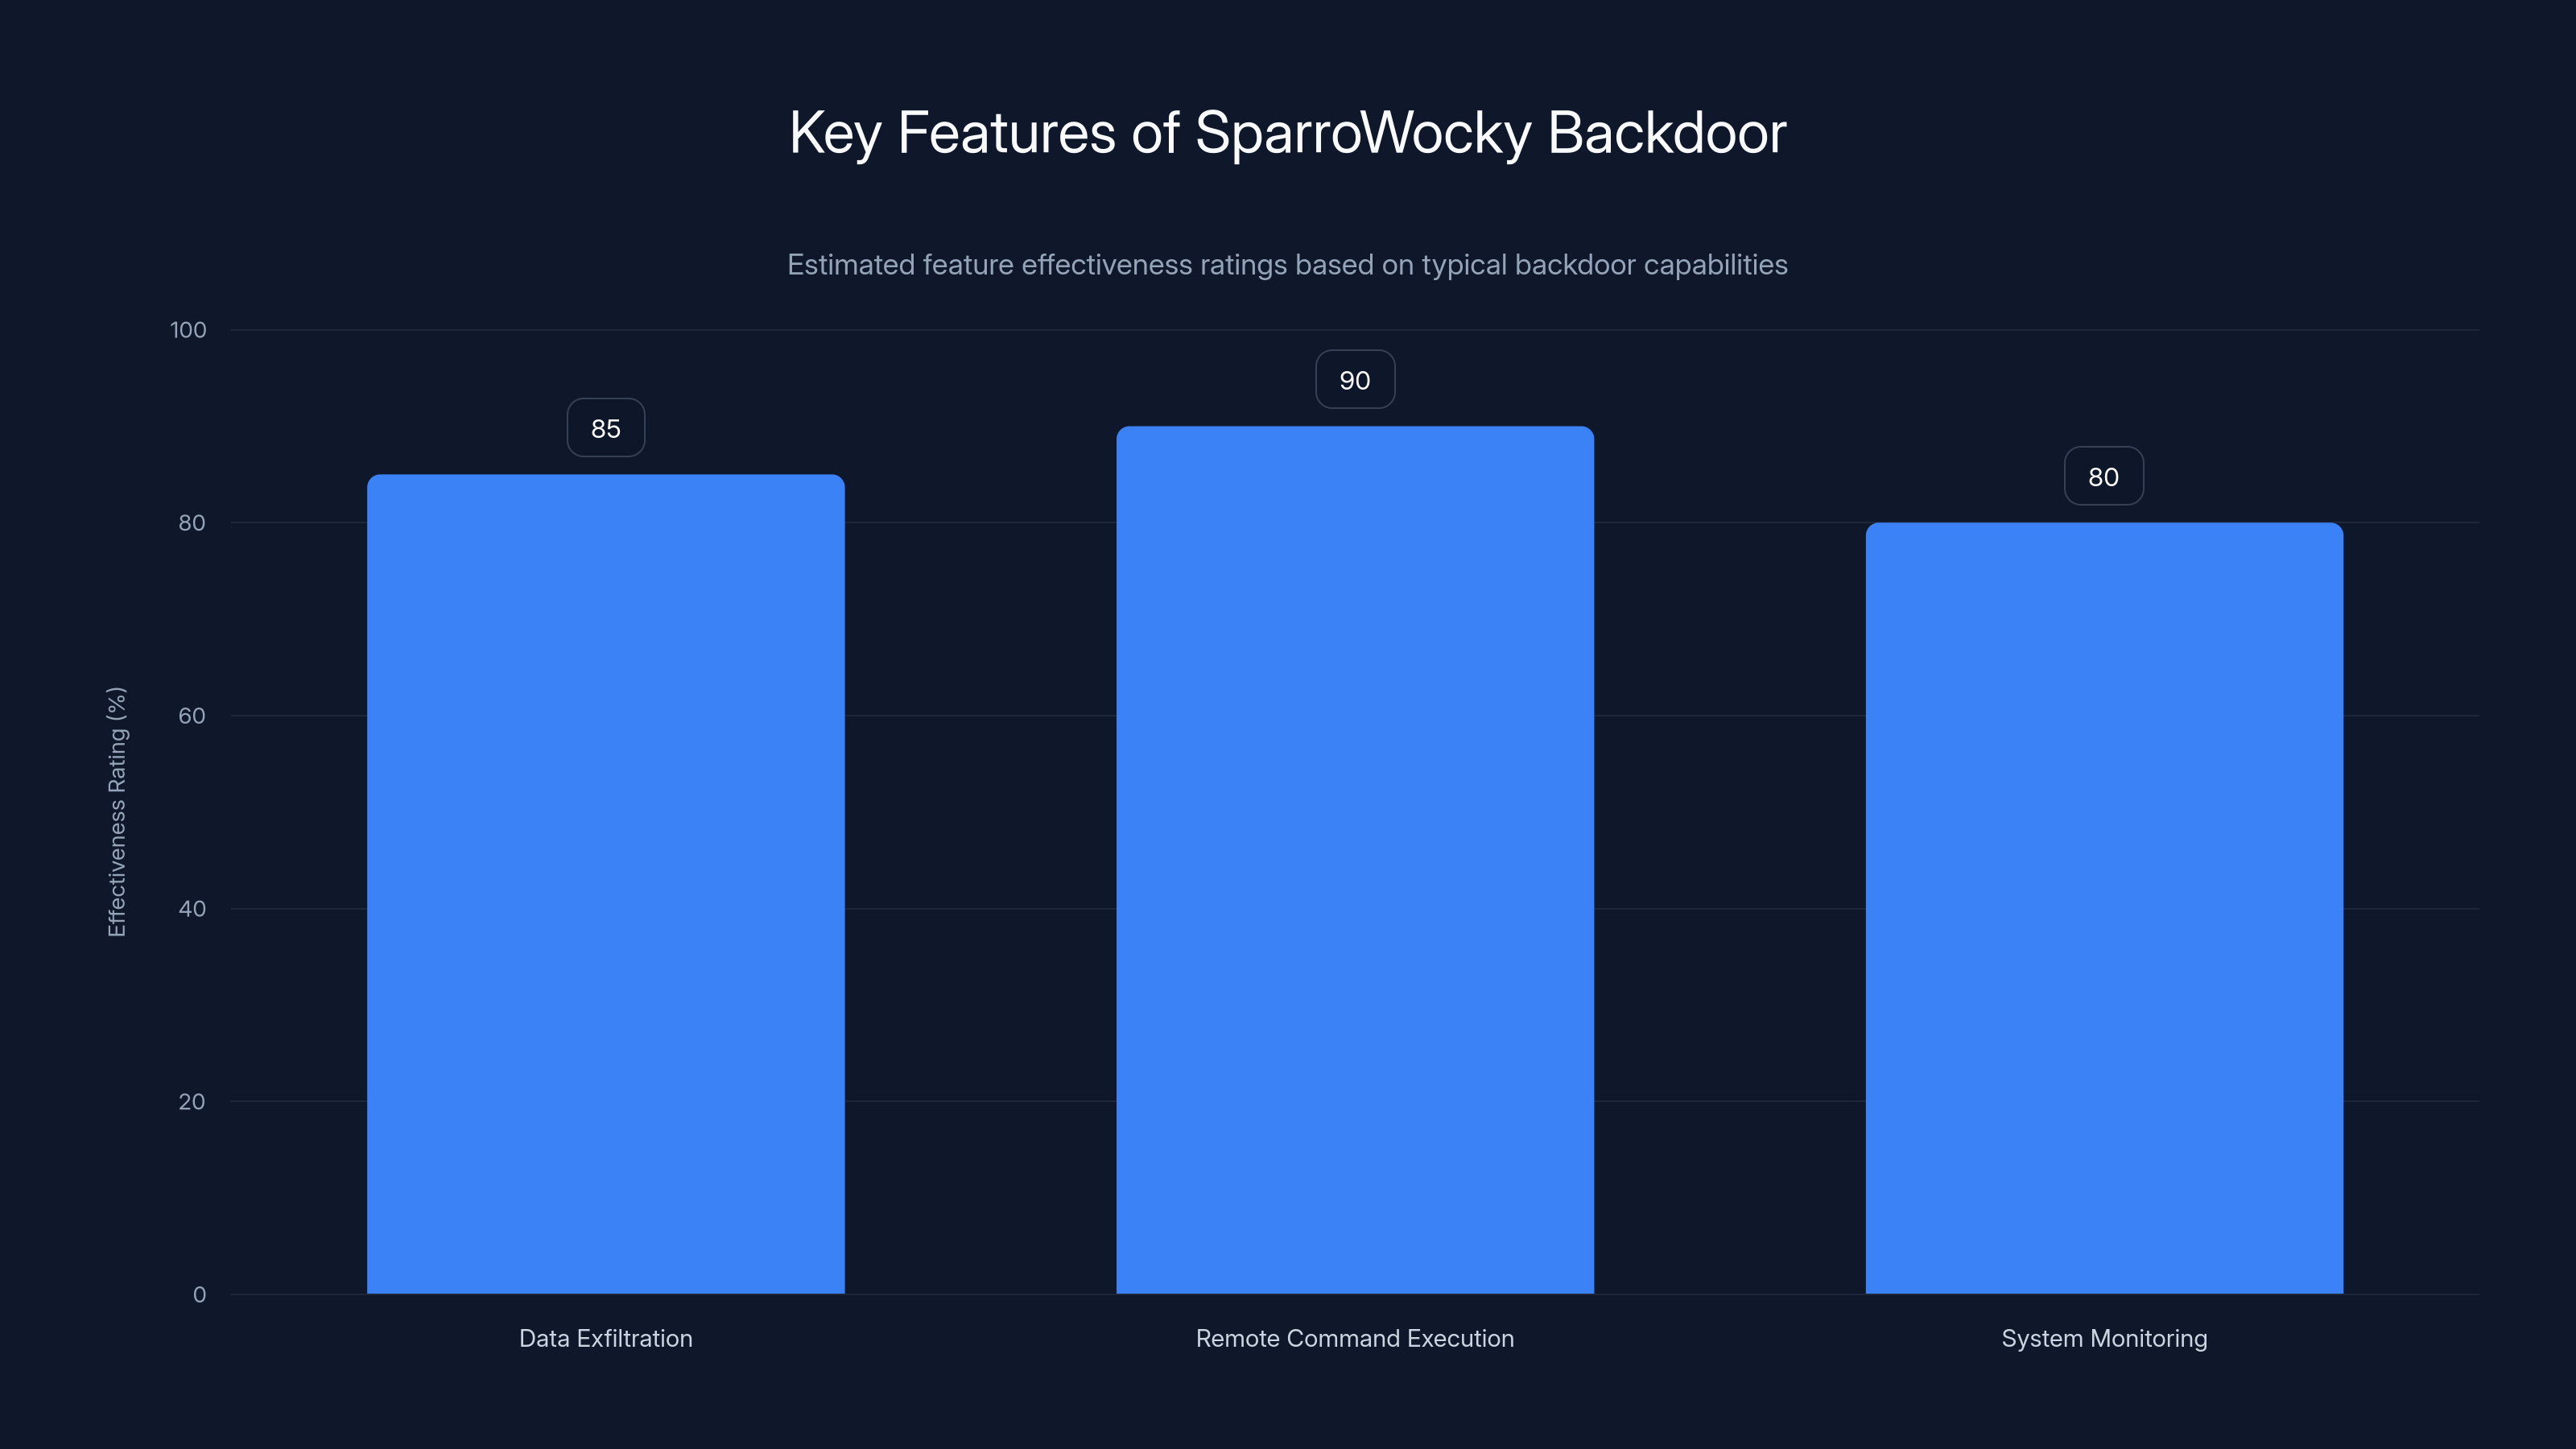
The SparroWocky backdoor excels in remote command execution and data exfiltration, with high effectiveness ratings across its key features. (Estimated data)
Enter Sparro Wocky: The New Backdoor
The recent deployment of the Sparro Wocky backdoor marks a significant evolution in Salt Typhoon's capabilities. This tool is designed to provide comprehensive control over infected systems, allowing attackers to execute a range of malicious activities.
Sparro Wocky Features and Capabilities
The Sparro Wocky backdoor is equipped with over 30 commands that enable Salt Typhoon to perform a variety of operations on compromised systems. These operations include data exfiltration, system manipulation, and network reconnaissance.
Key Features of Sparro Wocky:
- Data Exfiltration: Capable of extracting large volumes of sensitive information.
- Remote Command Execution: Allows attackers to execute arbitrary commands on infected machines.
- System Monitoring: Provides real-time access to system activities and network traffic.
Technical Deep Dive: How Sparro Wocky Works
Initial Access
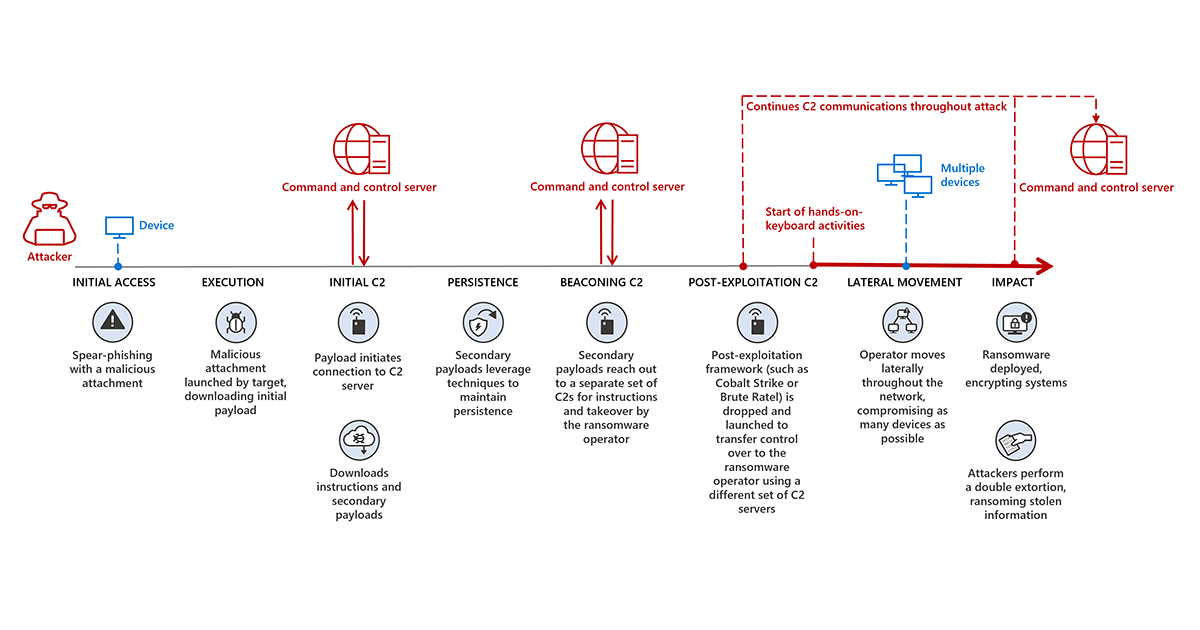
Salt Typhoon typically gains initial access through spear-phishing campaigns and exploiting known vulnerabilities in public-facing applications. Once inside, they deploy Sparro Wocky to establish a persistent foothold.
Command and Control (C2) Infrastructure
Sparro Wocky uses a sophisticated C2 infrastructure to maintain communication with the attackers. This infrastructure is designed to be resilient, using multiple layers of proxy servers to obfuscate the origin of the communication.
C2 Resilience Strategies:
- Domain Fronting: Leverages legitimate services to mask C2 traffic.
- Encrypted Channels: Ensures all communications are encrypted to prevent detection.
Persistence Mechanisms
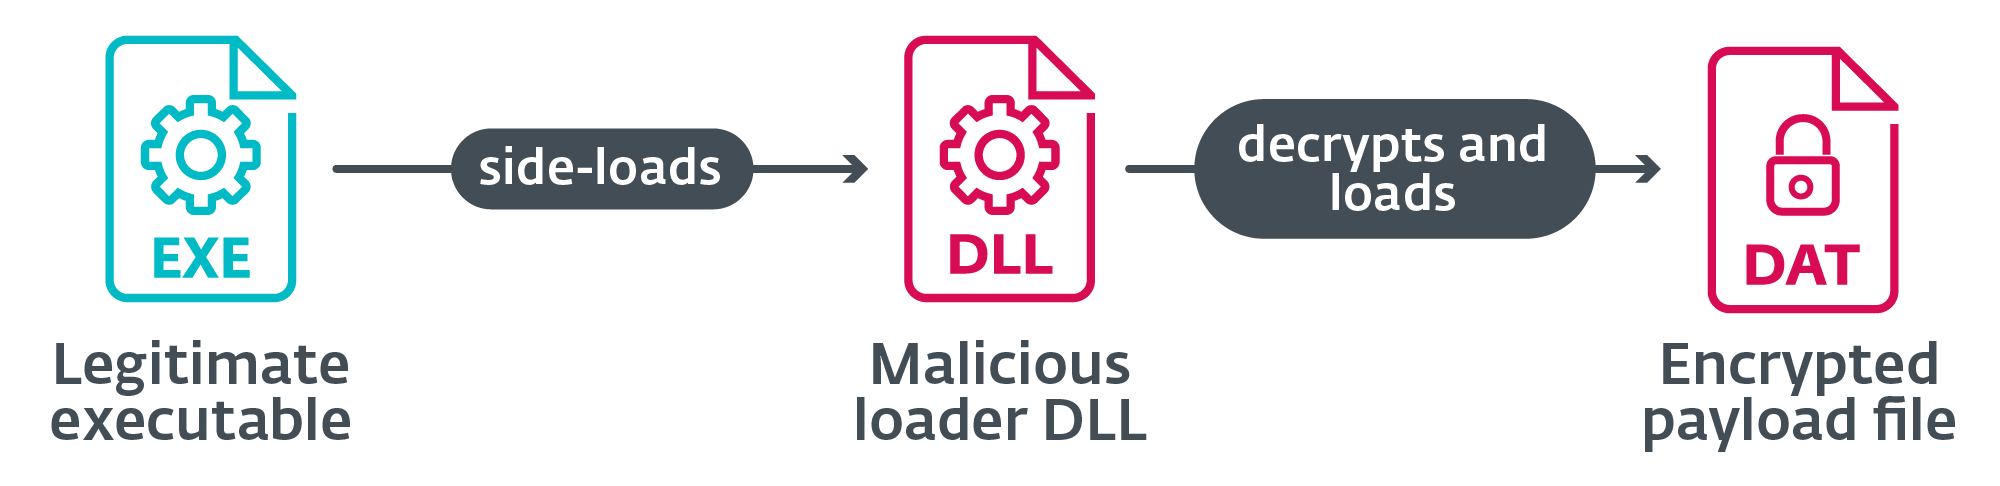
To remain undetected, Sparro Wocky employs several persistence mechanisms that allow it to survive system reboots and software updates. These mechanisms include registry modifications and scheduled tasks.
Persistence Tactics:
- Registry Keys: Alters registry keys to execute on startup.
- Task Scheduler: Creates hidden tasks to ensure continued execution.
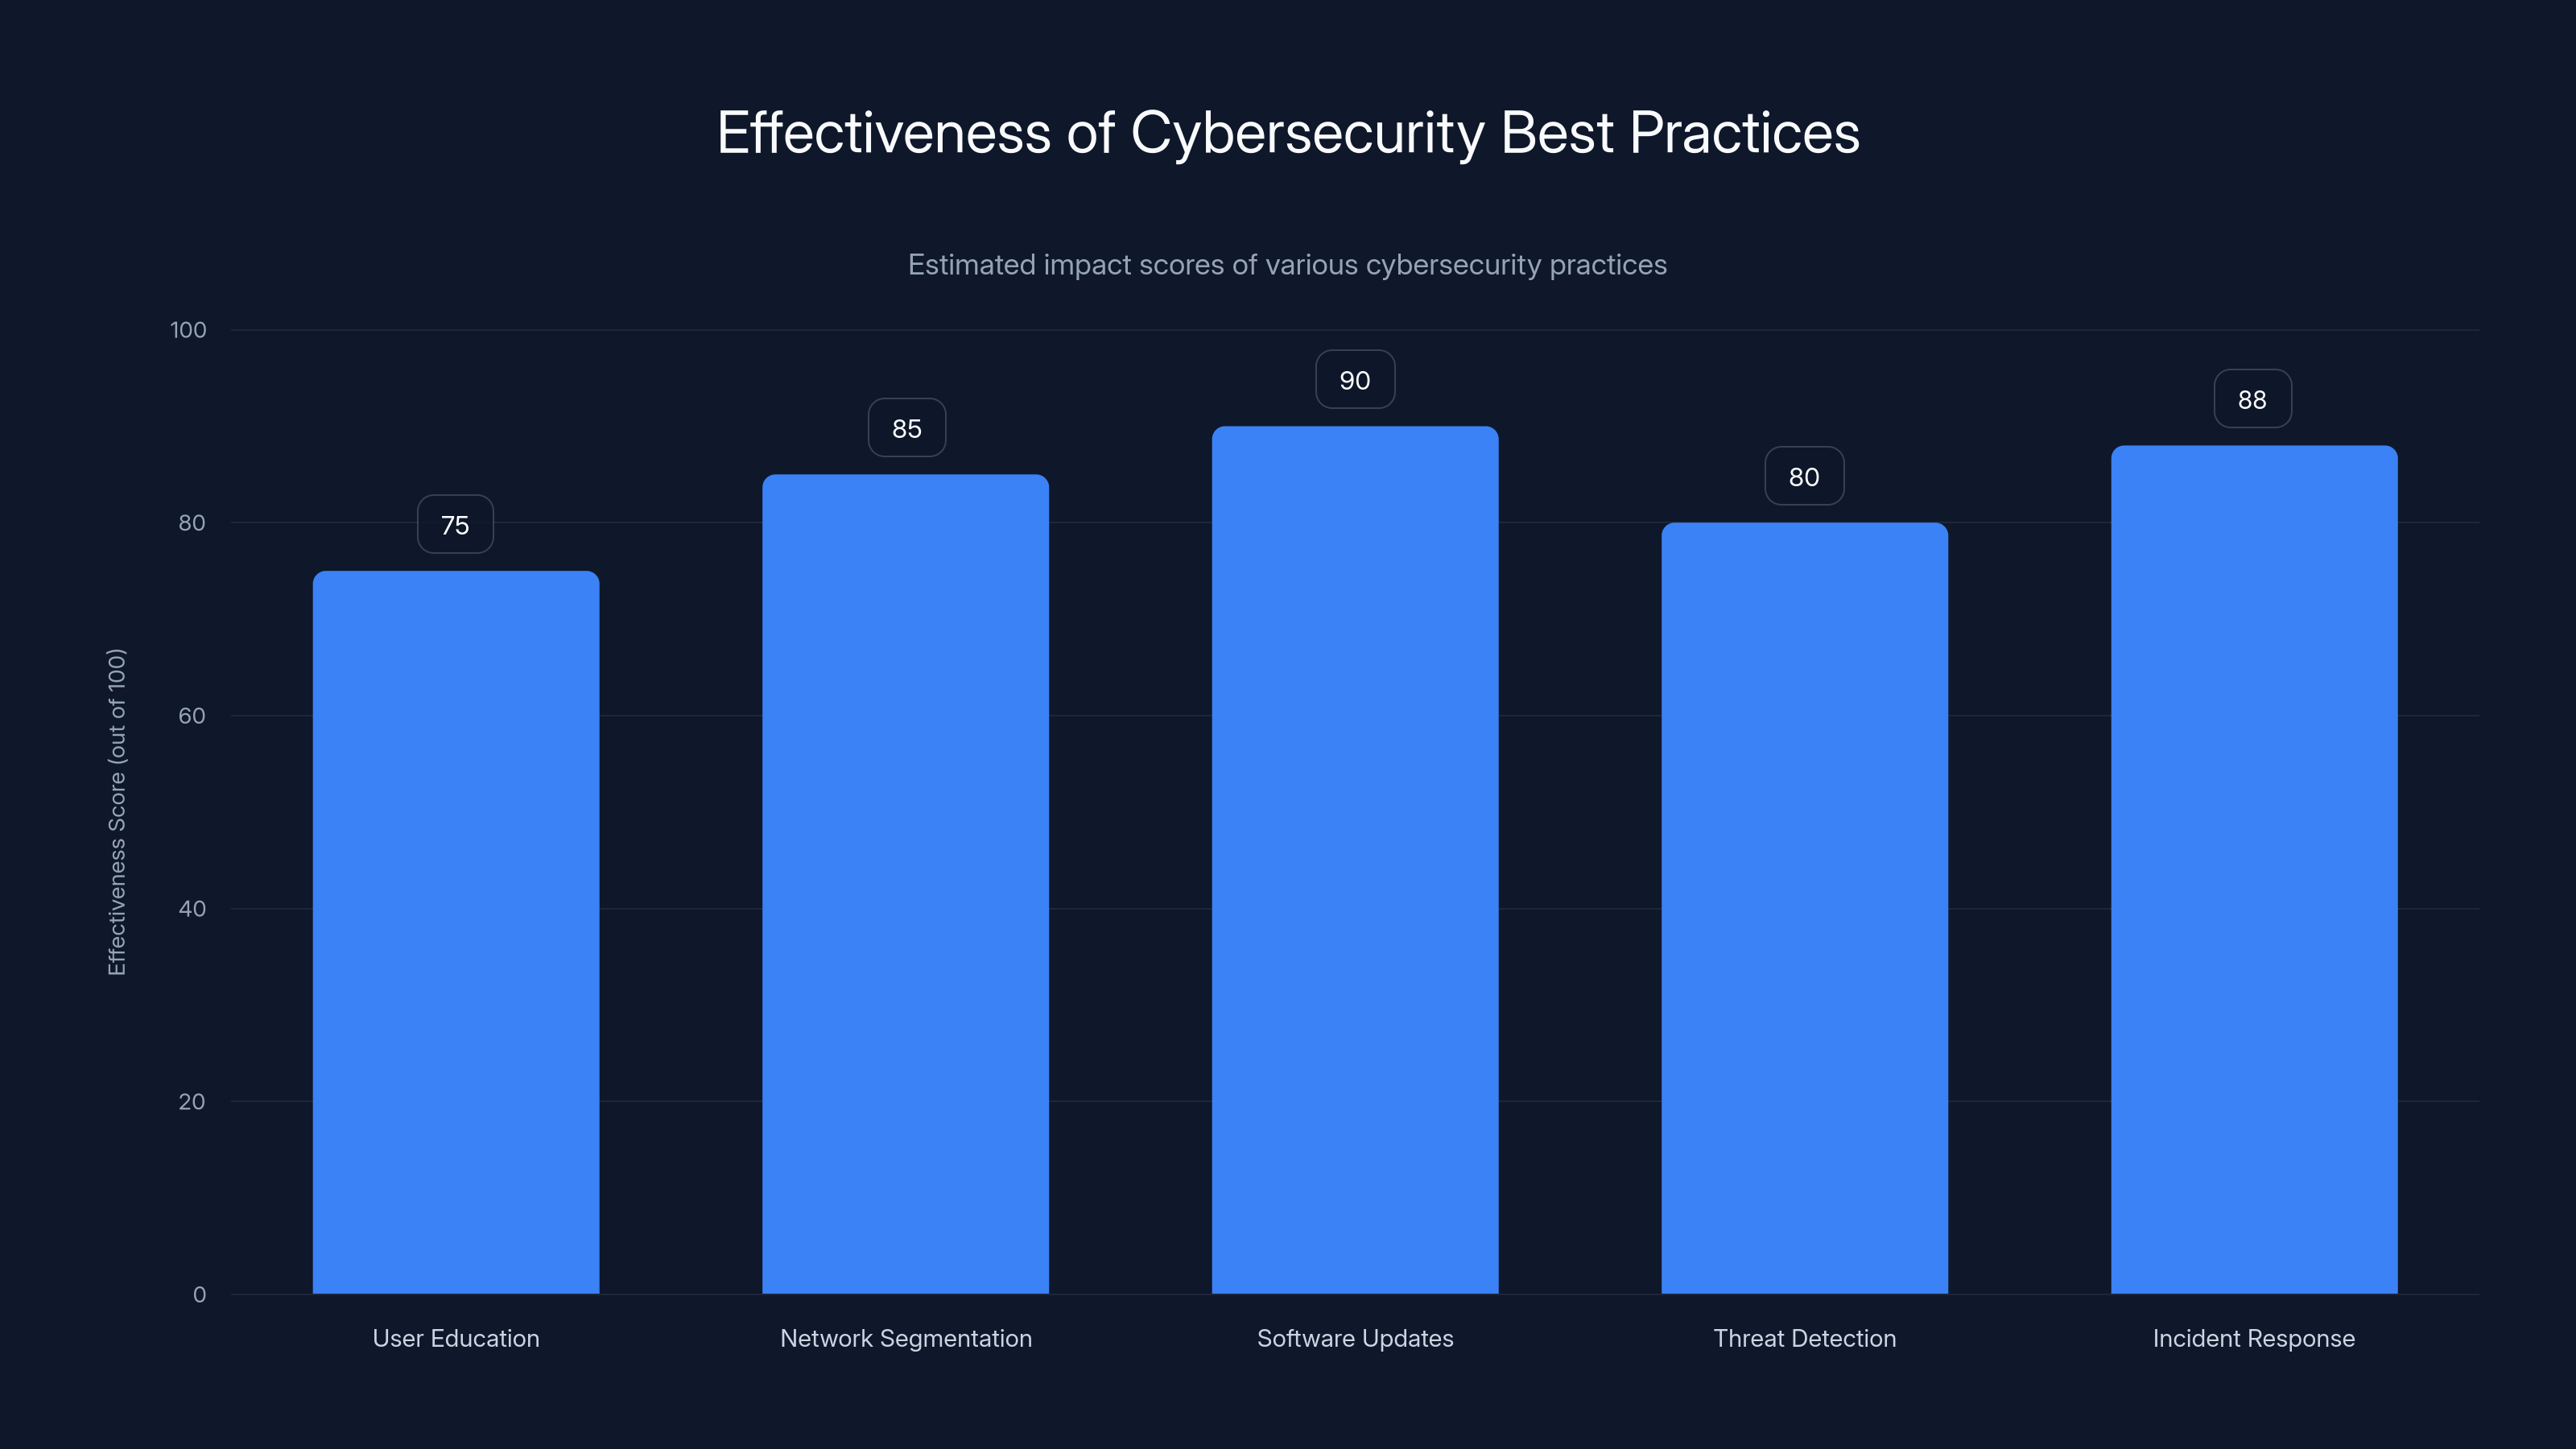
Estimated data suggests that regular software updates and incident response planning are among the most effective cybersecurity practices, scoring 90 and 88 out of 100 respectively.
The Latin American Focus: Why It Matters
Salt Typhoon's shift towards Latin America is strategic. The region's increasing geopolitical influence and economic growth make it a prime target for intelligence gathering. By infiltrating governmental systems, Salt Typhoon aims to gain insights into political strategies, economic policies, and regional alliances.
Targeted Countries
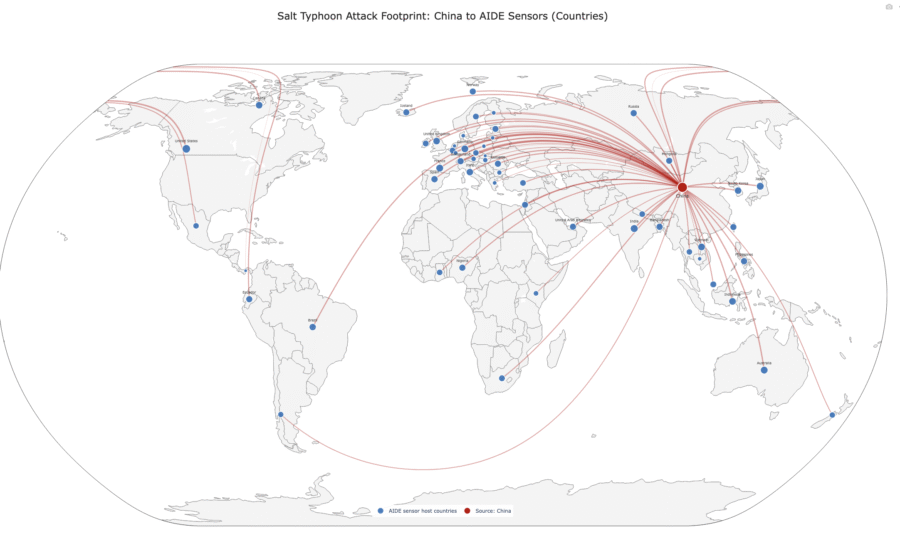
Recent reports indicate that Salt Typhoon has been actively targeting government entities in Argentina, Peru, Venezuela, and other Latin American nations. These countries are of particular interest due to their involvement in international trade agreements and regional political dynamics.
Potential Motivations:
- Economic Intelligence: Understanding trade policies and economic strategies.
- Political Insights: Gaining insights into diplomatic relations and policy-making.
- Technology Acquisition: Stealing intellectual property and technological advancements.
Cybersecurity Implications and Best Practices
The activities of Salt Typhoon and the deployment of tools like Sparro Wocky highlight the critical need for robust cybersecurity measures. Governments and organizations must prioritize the development and implementation of comprehensive security frameworks.
Best Practices for Mitigating Threats
- User Education: Conduct regular training sessions to educate employees about phishing attacks and social engineering tactics.
- Network Segmentation: Implement network segmentation to limit lateral movement within the network.
- Regular Software Updates: Ensure all systems and applications are updated to patch known vulnerabilities.
- Advanced Threat Detection: Deploy advanced threat detection tools to identify and respond to suspicious activities.
- Incident Response Planning: Develop and regularly update incident response plans to effectively manage and mitigate breaches.
Common Pitfalls and Solutions
Overreliance on Legacy Systems
Many organizations continue to rely on outdated systems that lack modern security features. This reliance creates vulnerabilities that can be easily exploited by groups like Salt Typhoon.
Solution:
- System Modernization: Invest in upgrading legacy systems to incorporate modern security protocols and features.
Inadequate Threat Intelligence
Failing to keep abreast of the latest threat intelligence can leave organizations vulnerable to emerging threats.
Solution:
- Threat Intelligence Integration: Subscribe to reputable threat intelligence services and integrate their data into security operations.
Poor Incident Response
Without a well-defined incident response plan, organizations may struggle to respond effectively to breaches, resulting in prolonged exposure and damage.
Solution:
- Regular Drills and Testing: Conduct regular incident response drills to ensure teams are prepared to act swiftly and effectively.
Future Trends in Cyber Espionage
The landscape of cyber espionage is continually evolving, with threat actors adopting more sophisticated tactics and tools. Looking ahead, several trends are likely to shape the future of cyber espionage.
Increasing Use of AI and Machine Learning
Threat actors are expected to leverage AI and machine learning to enhance their capabilities. These technologies can be used to automate reconnaissance, improve malware evasion techniques, and optimize attack strategies.
Rise of Supply Chain Attacks
Supply chain attacks are becoming more prevalent as attackers target third-party vendors to gain access to larger networks. Organizations will need to scrutinize their supply chains and implement stringent security measures.
Greater Focus on Data-Driven Espionage
As data becomes an increasingly valuable asset, cyber espionage efforts will focus on data theft and manipulation to influence political and economic outcomes.
Recommendations for Governments and Organizations
- Enhance International Cooperation: Foster collaboration between nations to share intelligence and coordinate responses to cyber threats.
- Invest in Cybersecurity Research: Support research initiatives to develop advanced cybersecurity technologies and methodologies.
- Promote Cyber Hygiene: Encourage best practices in cybersecurity across all sectors to reduce vulnerabilities and improve resilience.
- Strengthen Legal Frameworks: Develop and enforce legal frameworks to deter cybercriminal activities and hold perpetrators accountable.
Conclusion
The emergence of the Sparro Wocky backdoor and Salt Typhoon's focus on Latin America underscore the evolving nature of cyber espionage. As threat actors become more sophisticated, the need for robust cybersecurity frameworks and international cooperation becomes increasingly urgent. By staying informed, investing in advanced technologies, and fostering collaboration, governments and organizations can better protect themselves from cyber threats.
FAQ
What is Salt Typhoon?
Salt Typhoon is a state-sponsored cyber-espionage group believed to be backed by China, known for targeting government entities and critical infrastructure worldwide.
How does the Sparro Wocky backdoor work?
Sparro Wocky is a sophisticated tool that provides attackers with comprehensive control over infected systems, enabling data exfiltration, command execution, and system monitoring.
Why is Latin America a target for Salt Typhoon?
Latin America's growing geopolitical influence and economic significance make it a prime target for intelligence gathering and espionage activities.
What are the best practices for mitigating cyber threats?
Best practices include user education, network segmentation, regular software updates, advanced threat detection, and incident response planning.
What are the future trends in cyber espionage?
Future trends include the increased use of AI and machine learning, a rise in supply chain attacks, and a greater focus on data-driven espionage.
How can organizations improve their cybersecurity posture?
Organizations can enhance their cybersecurity by investing in research, promoting cyber hygiene, strengthening legal frameworks, and fostering international cooperation.
What role does international cooperation play in cybersecurity?
International cooperation is crucial for sharing intelligence, coordinating responses to cyber threats, and deterring cybercriminal activities through collective action.
Key Takeaways
- Salt Typhoon's focus on Latin America highlights the geopolitical importance of the region.
- SparroWocky backdoor exemplifies advanced cyber-espionage tools with over 30 commands.
- Organizations need robust cybersecurity frameworks to counter sophisticated threats.
- Future trends point to increased use of AI in cyber-espionage and more supply chain attacks.
- International cooperation is essential for effective defense against state-sponsored cyber threats.
Related Articles
- A Comprehensive Guide to VPNs: Navigating Security, Privacy, and Best Practices [2025]
- Why Zero Trust is the Practical Enterprise Access and Security Model [2025]
- Understanding the ClickFix Campaign: A Deep Dive into Windows Terminal and PowerShell Malware [2025]
- Obscura VPN's Arrival on Windows: Revolutionizing Privacy for PC Users [2025]
- Understanding TP-Link Tapo Camera Vulnerabilities and How to Safeguard Your Privacy [2025]
- ExpressVPN's Fortify Router: A Comprehensive Guide [2025]


