
Cisco Zero-Day Exploit on Identity Services Engine: Secure Your Network Now [2025]
Last month, a security alert rocked the cybersecurity world. Cisco's Identity Services Engine (ISE) was hit by a zero-day exploit (CVE‑2026‑76460) that could bypass API authentication, exposing networks to unauthorized access. If you're running Cisco ISE, it's time to take action.
TL; DR
- Max Severity Zero-Day: Cisco ISE vulnerability allows unauthenticated access.
- Patch Immediately: No workarounds exist; patching is critical.
- Risk Assessment: Evaluate your exposure and prioritize updates.
- Best Practices: Implement strict access controls and continuous monitoring.
- Future Trends: Expect more sophisticated exploits; stay proactive.
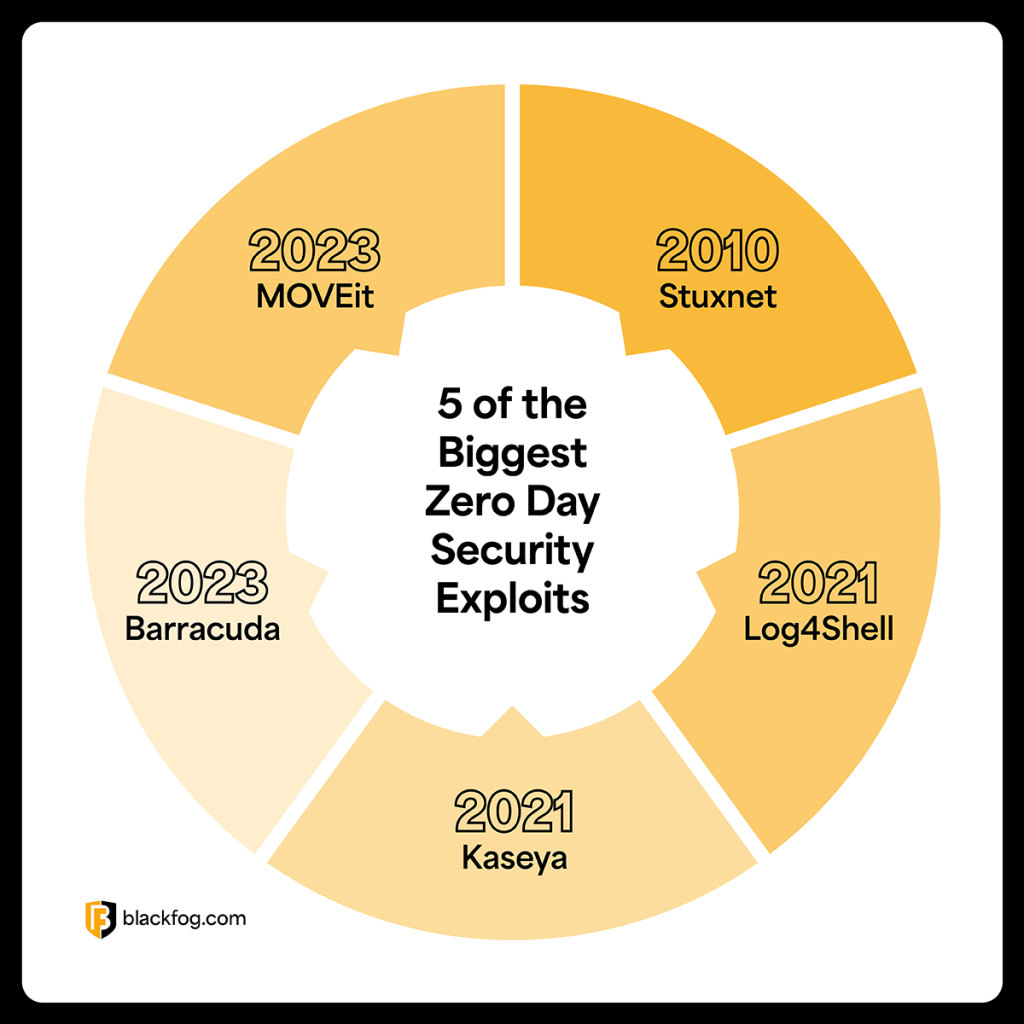
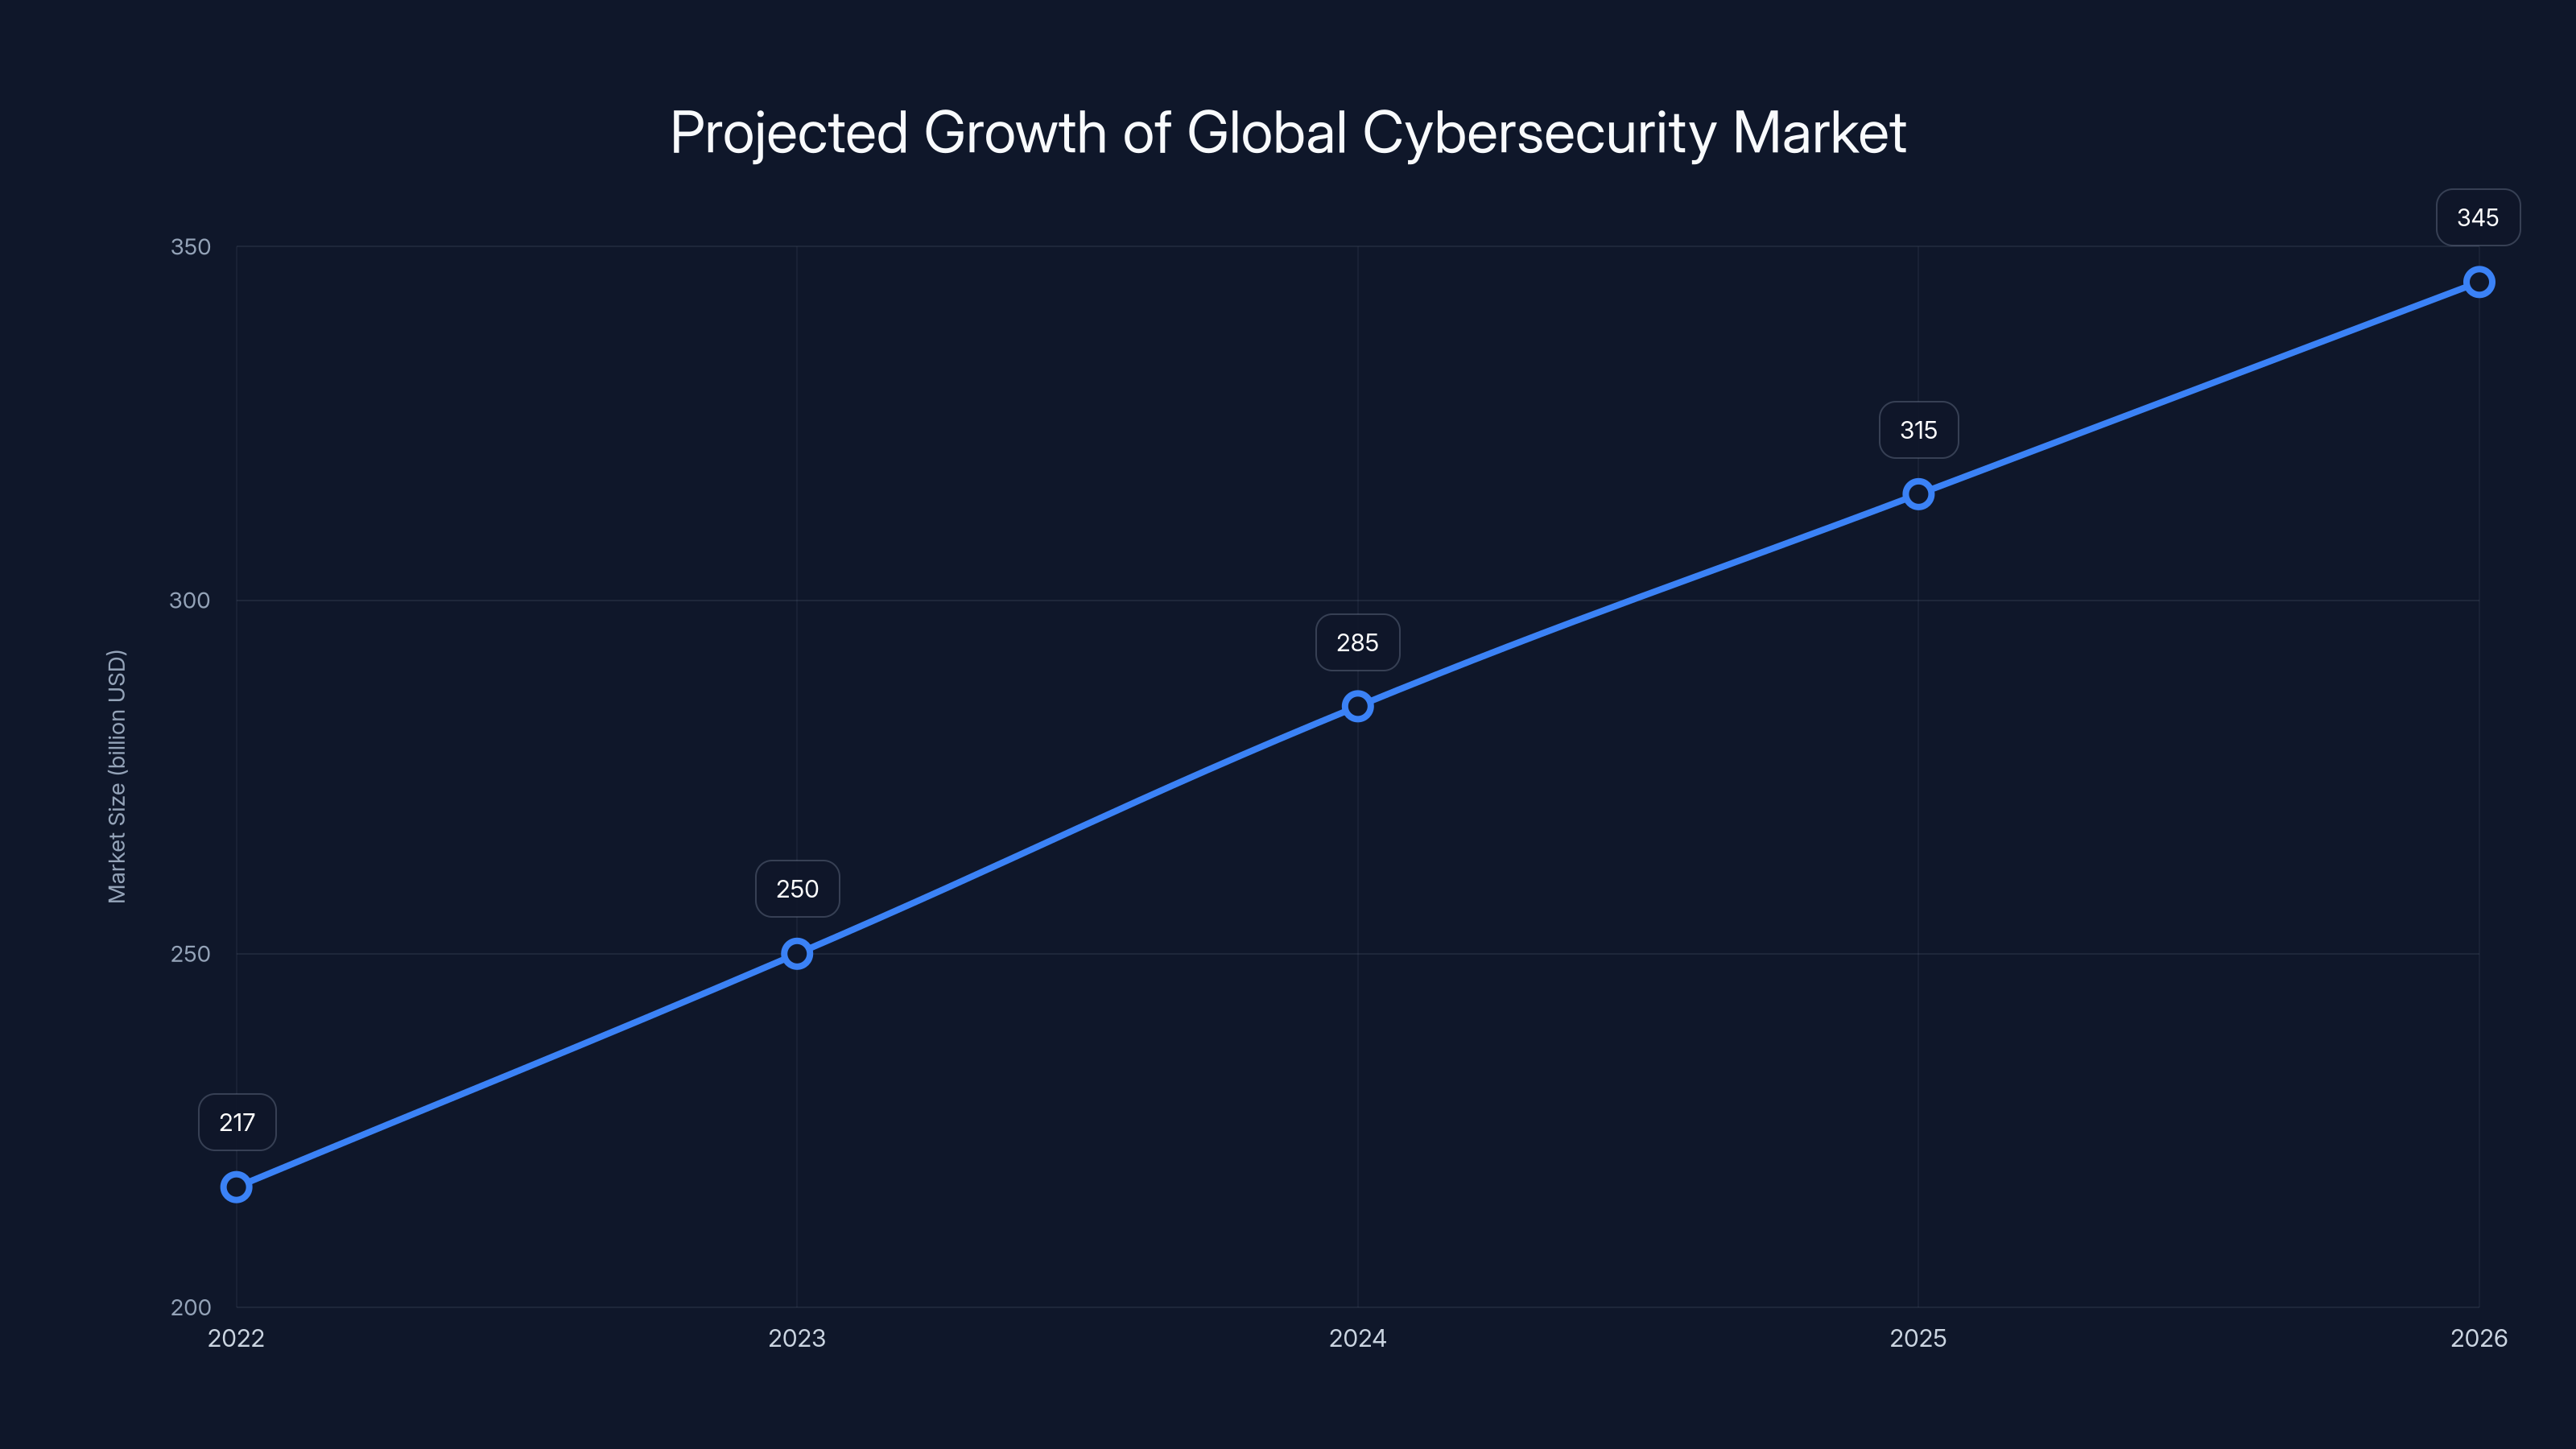
The global cybersecurity market is projected to grow significantly, reaching $345 billion by 2026. Estimated data based on industry trends.
Understanding the Cisco ISE Vulnerability
The vulnerability in question affects Cisco's ISE, a core component in many enterprise security architectures. The flaw allows unauthenticated users to bypass API authentication, gaining unauthorized access to sensitive network operations. This exploit, CVE‑2026‑76460, has been given a max severity rating, highlighting the critical nature of the threat.
What is Cisco ISE?
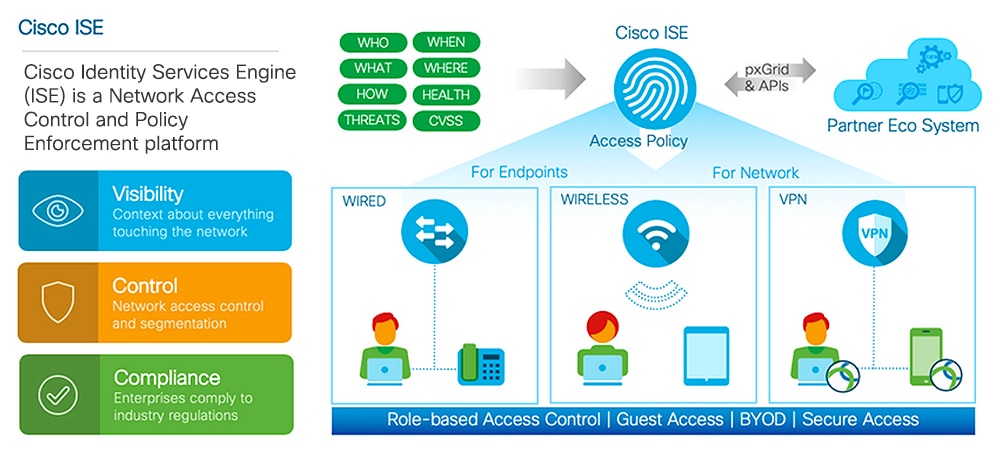
Cisco Identity Services Engine (ISE) is a security policy management platform that offers automated access control to network resources. It plays a crucial role in managing identity and access policies, making it a prime target for malicious actors.
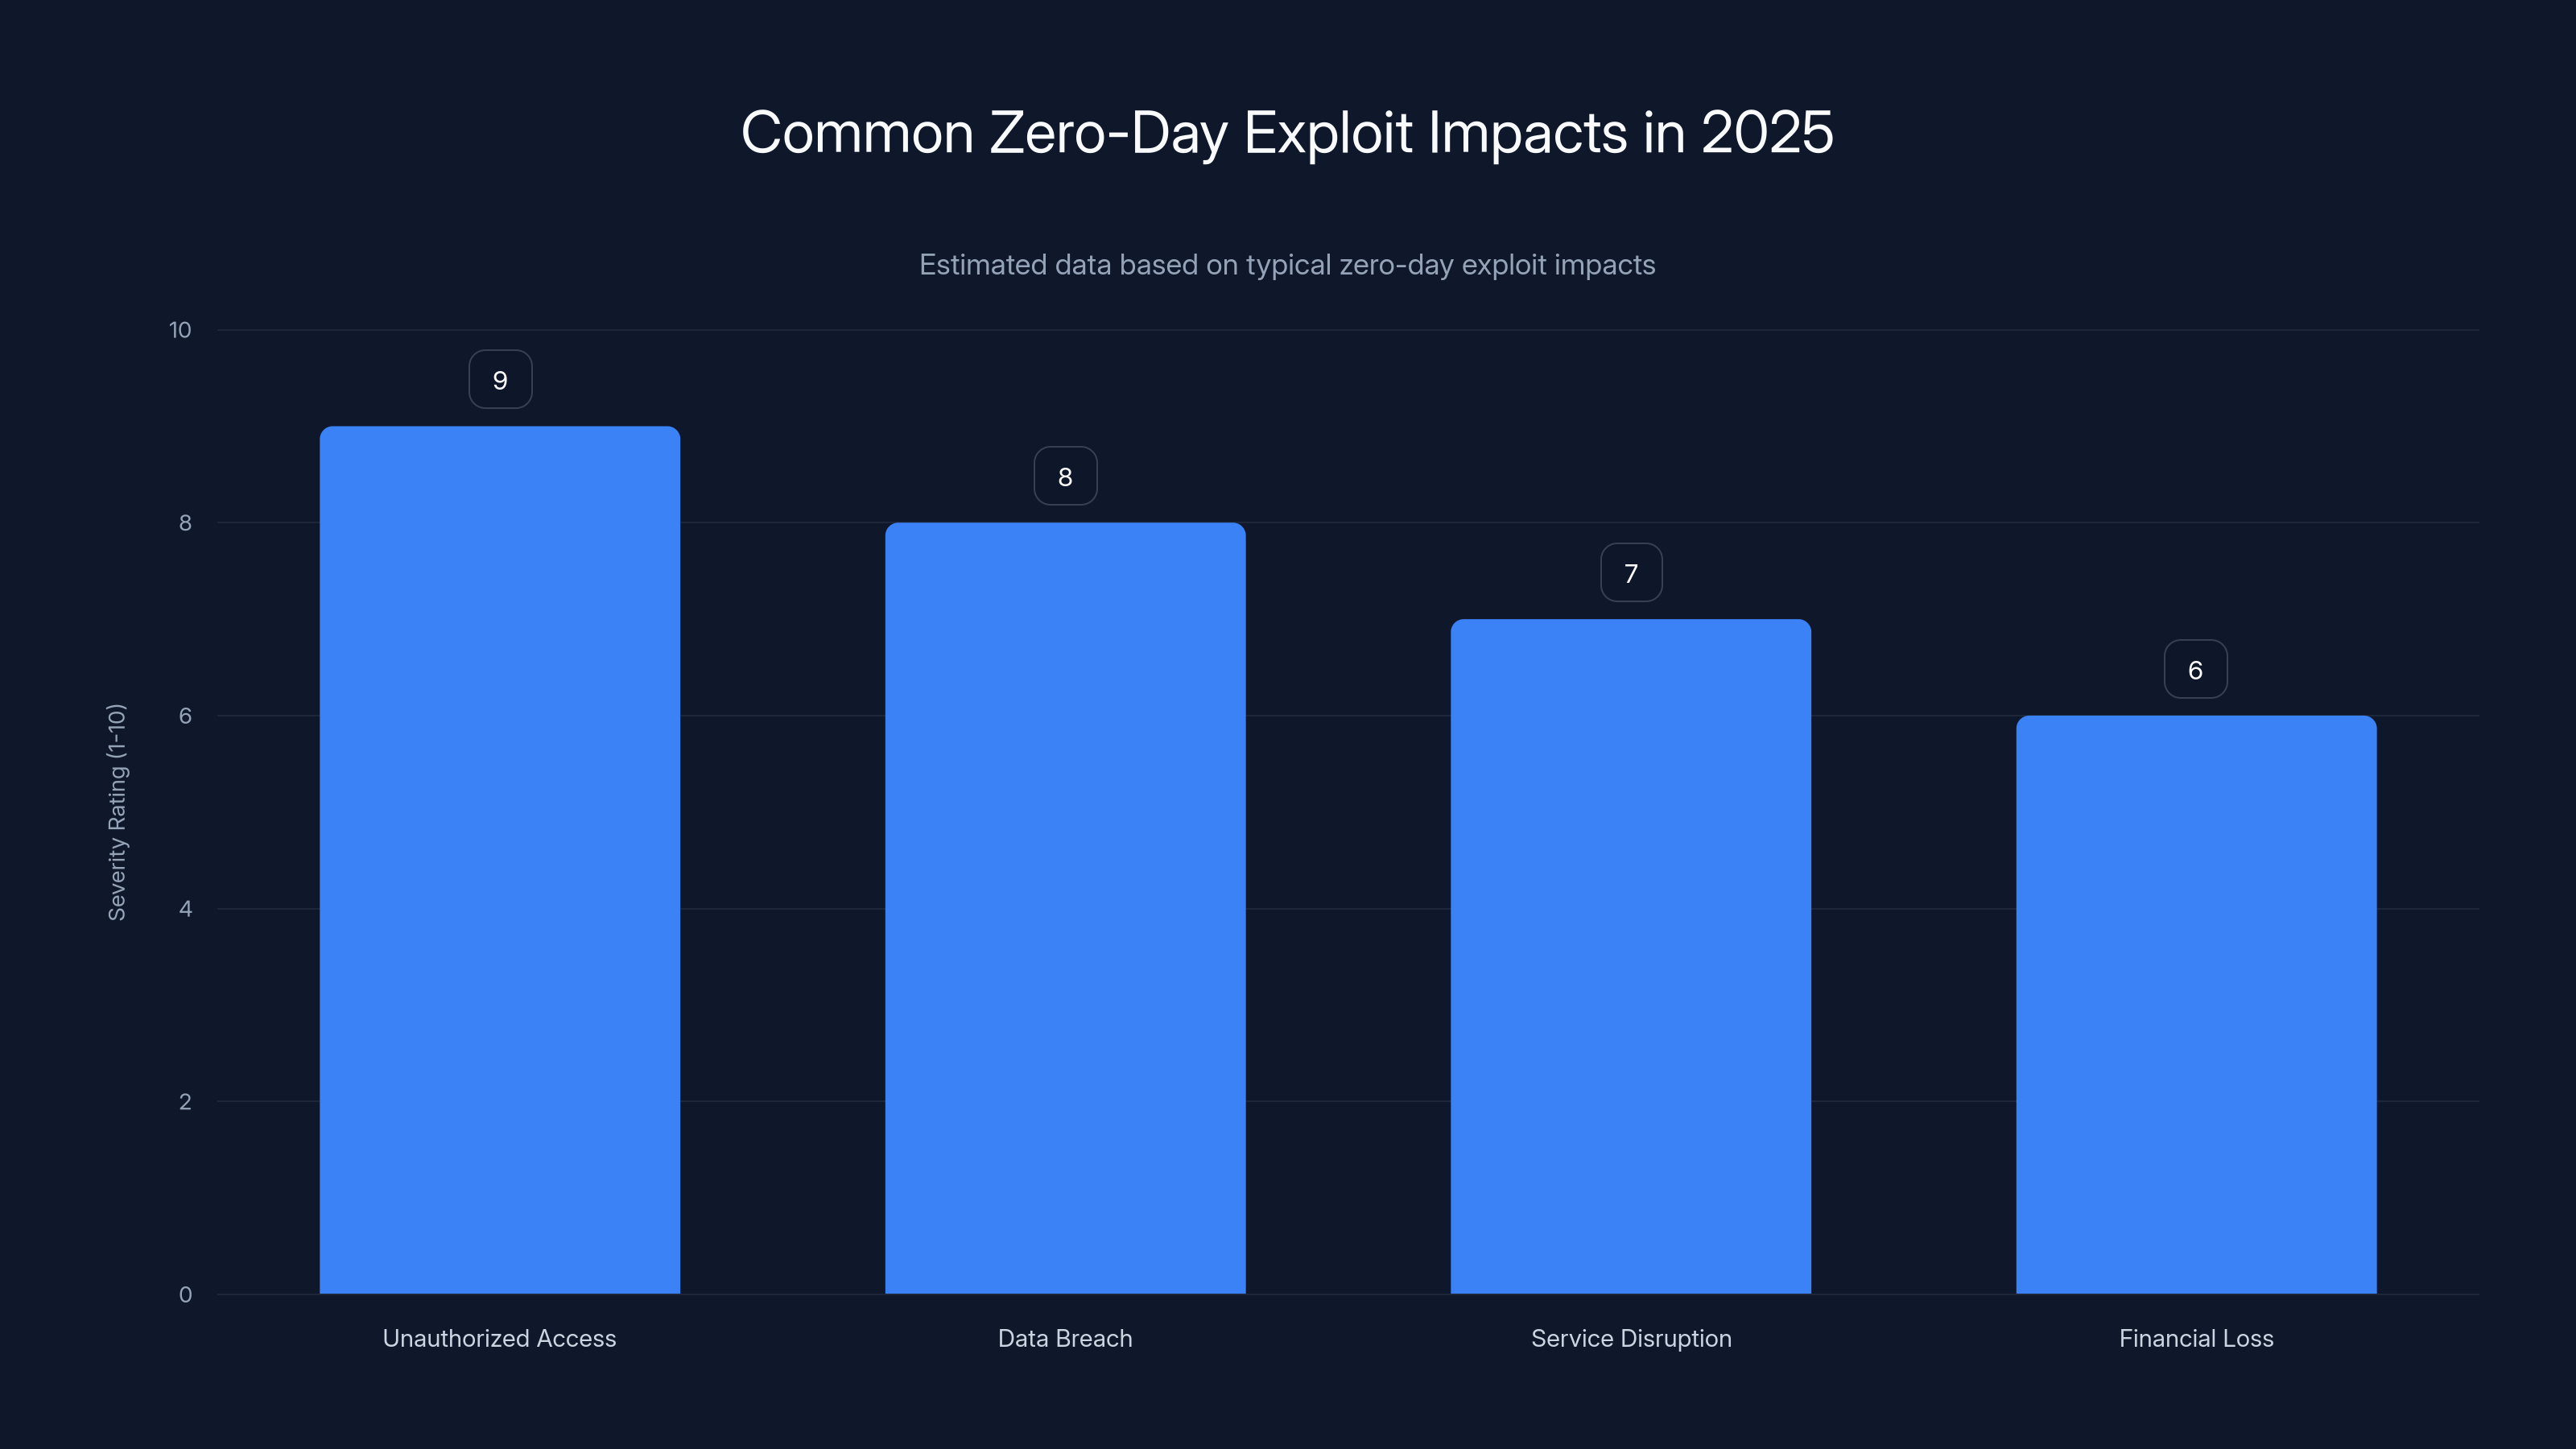
Unauthorized access is the most severe impact of zero-day exploits, with a high severity rating of 9. Estimated data based on typical impacts.
The Severity of CVE‑2026‑76460
CVE‑2026‑76460 is not just another minor bug. It's a doorway into your network's core. When exploited, this vulnerability allows attackers to execute arbitrary commands with elevated privileges. The lack of authentication checks makes it even more dangerous as it can be exploited remotely without needing valid credentials.
Why This Matters
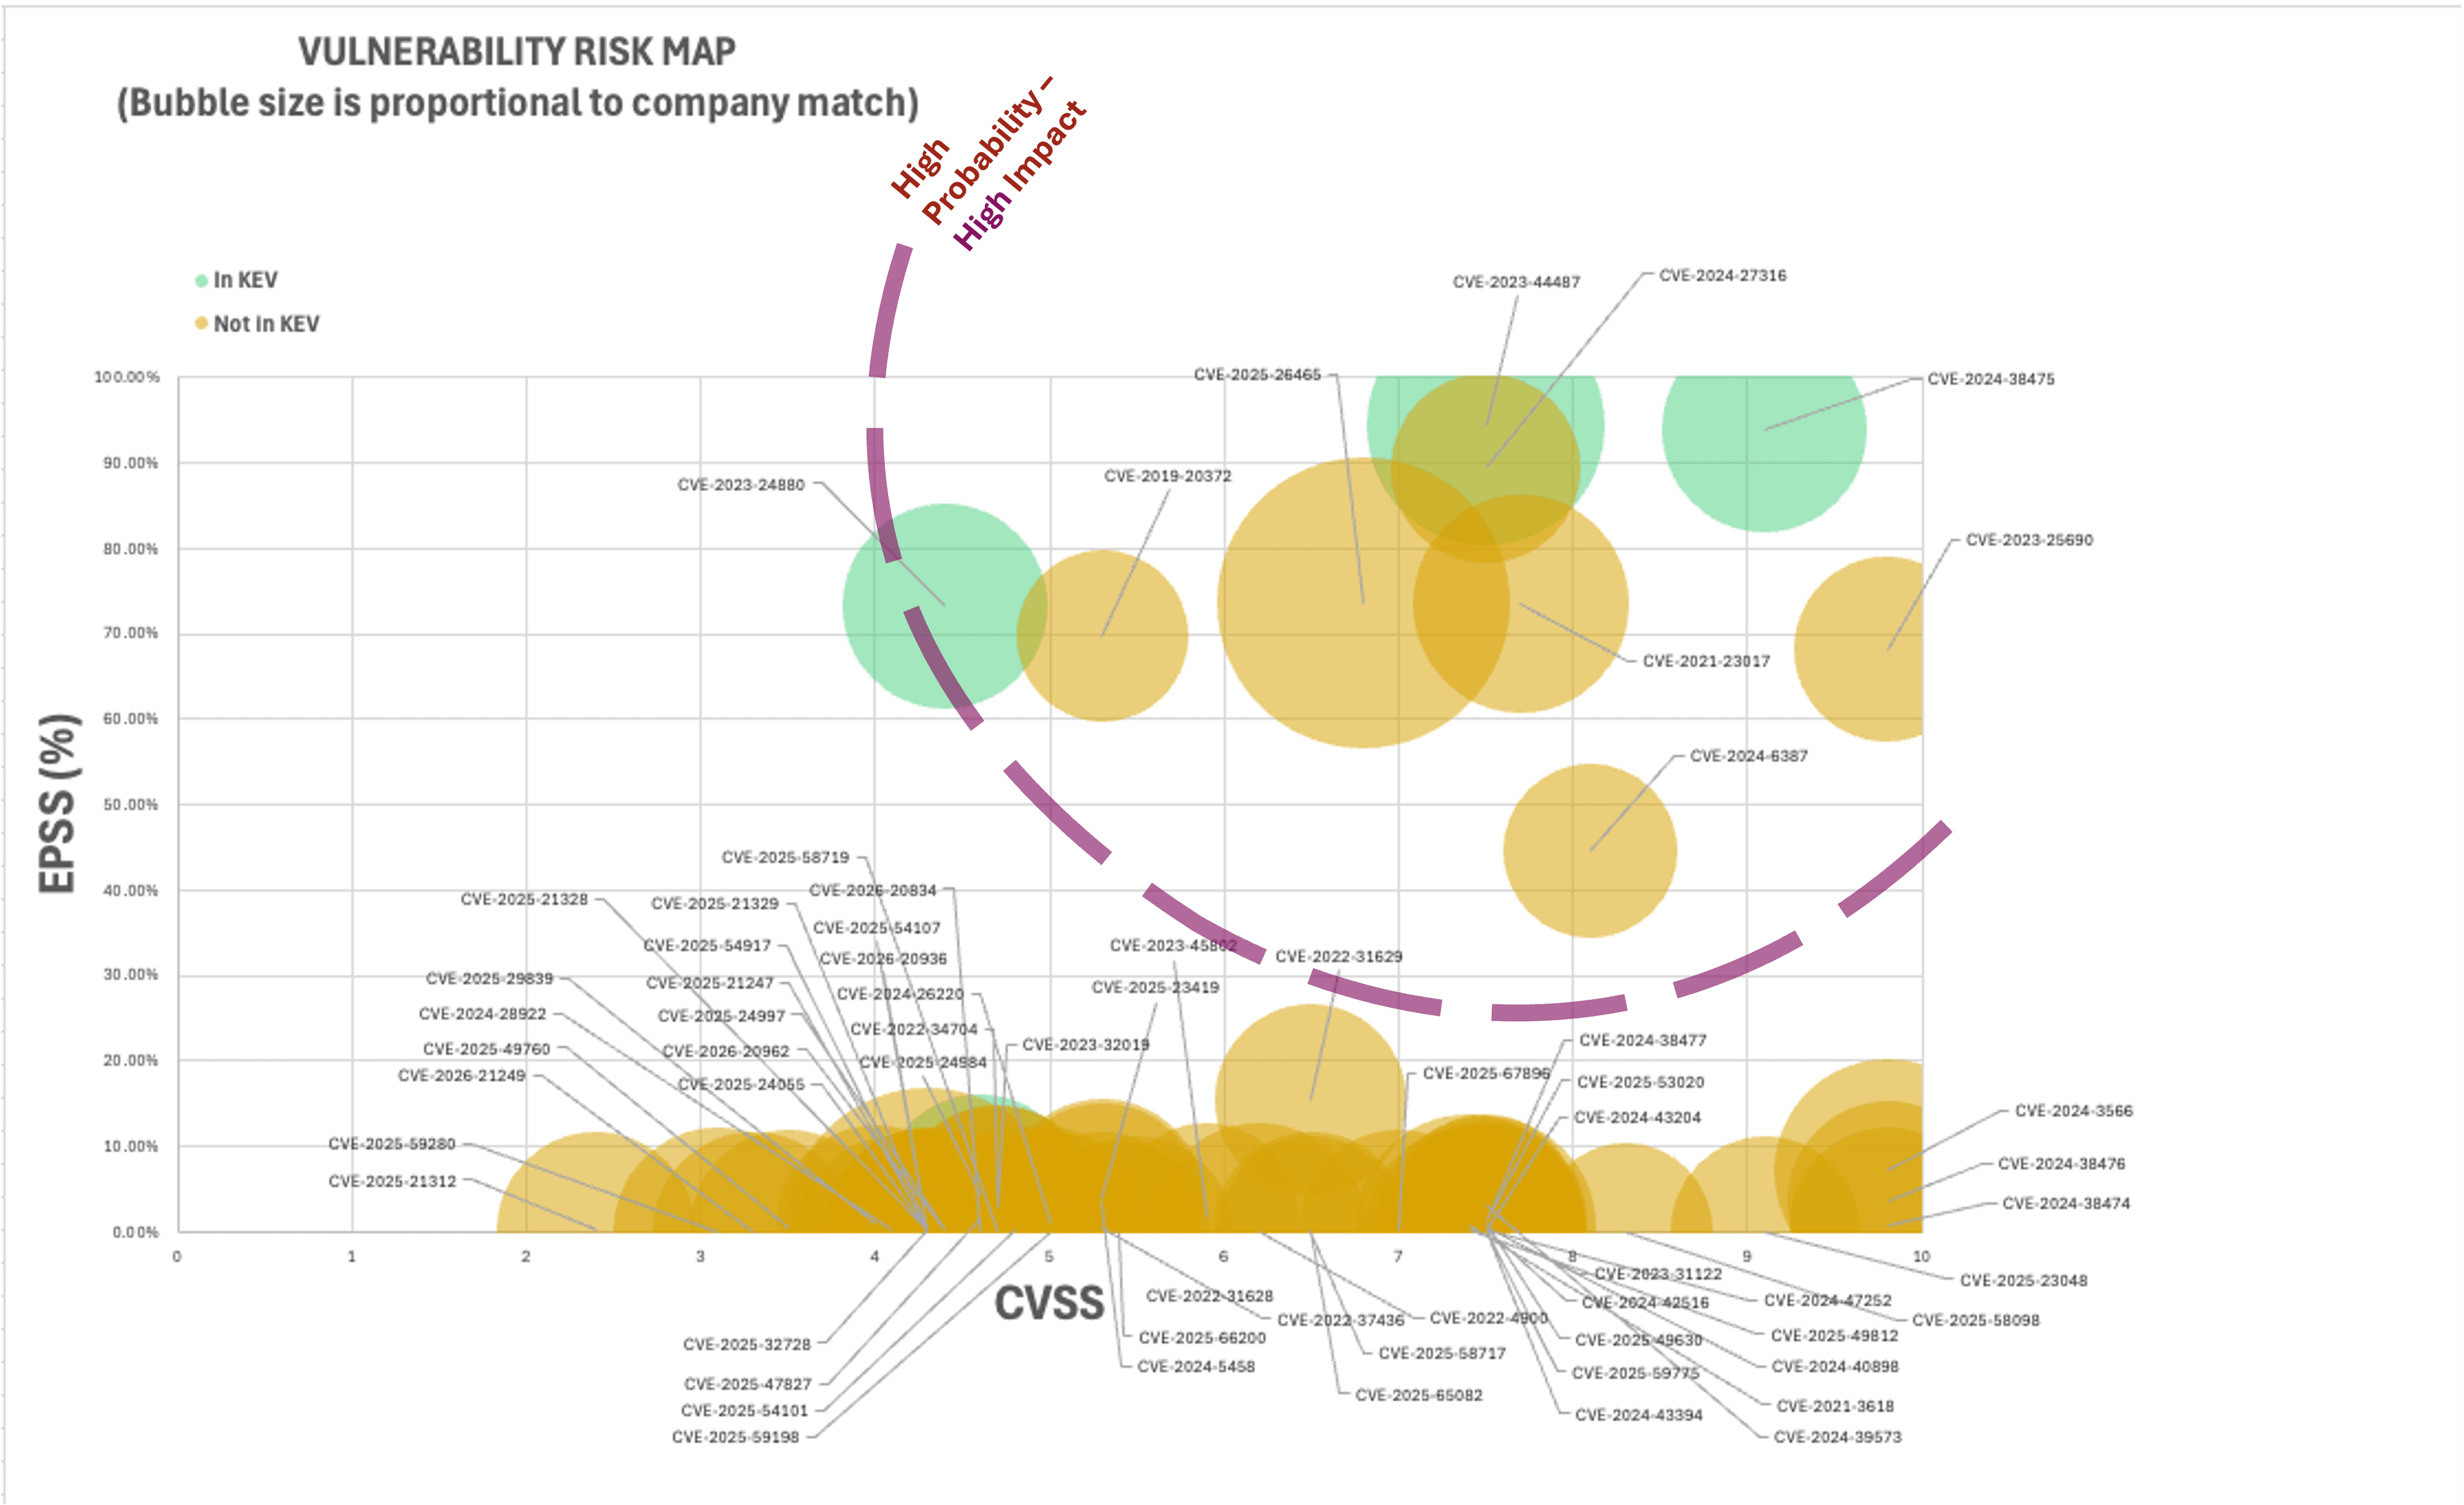
The API authentication bypass can lead to data breaches, unauthorized data manipulation, and potentially full control over network devices. With today's interconnected systems, a breach in one area can quickly spread, affecting entire network infrastructures.
Immediate Actions: Patch Your Systems
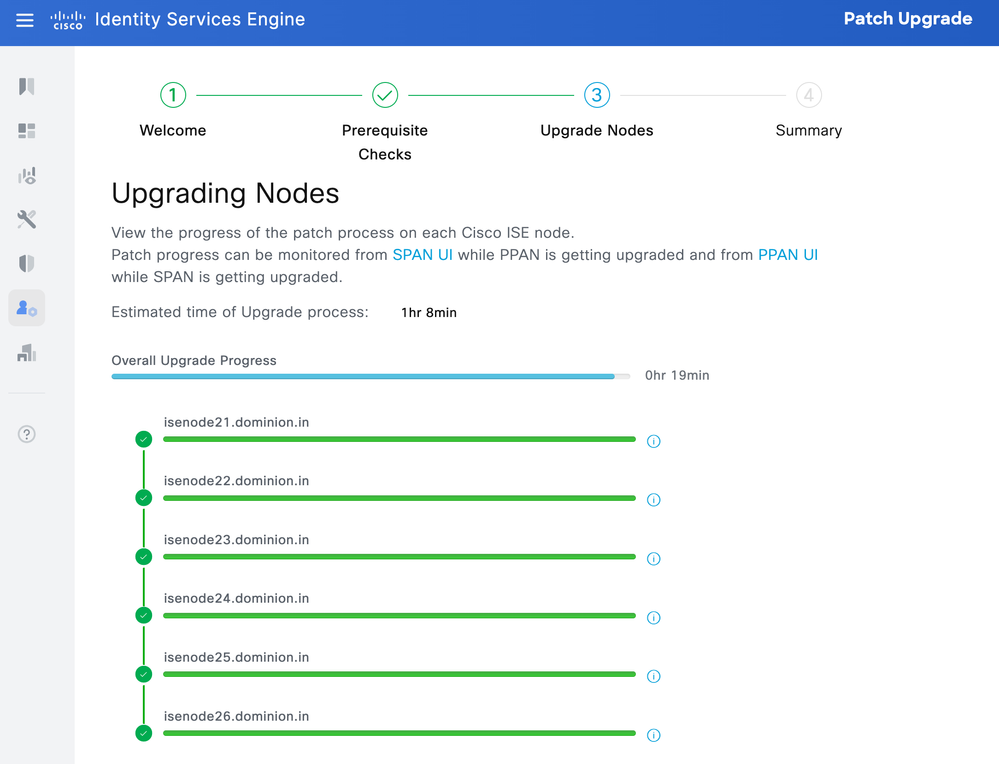
Cisco has released a patch addressing this vulnerability. Given the exploit's severity, the recommendation is clear: patch immediately.
How to Apply the Patch
- Identify Affected Systems: Check which systems in your network are running the affected versions of Cisco ISE.
- Download the Patch: Visit Cisco's official site to download the security patch.
- Test in a Controlled Environment: Before deploying widely, test the patch in a non-production environment to ensure no disruptions.
- Deploy the Patch: Roll out the patch across your network, prioritizing critical systems.
- Verify Successful Installation: Confirm that the patch has been applied successfully and monitor for any anomalies.
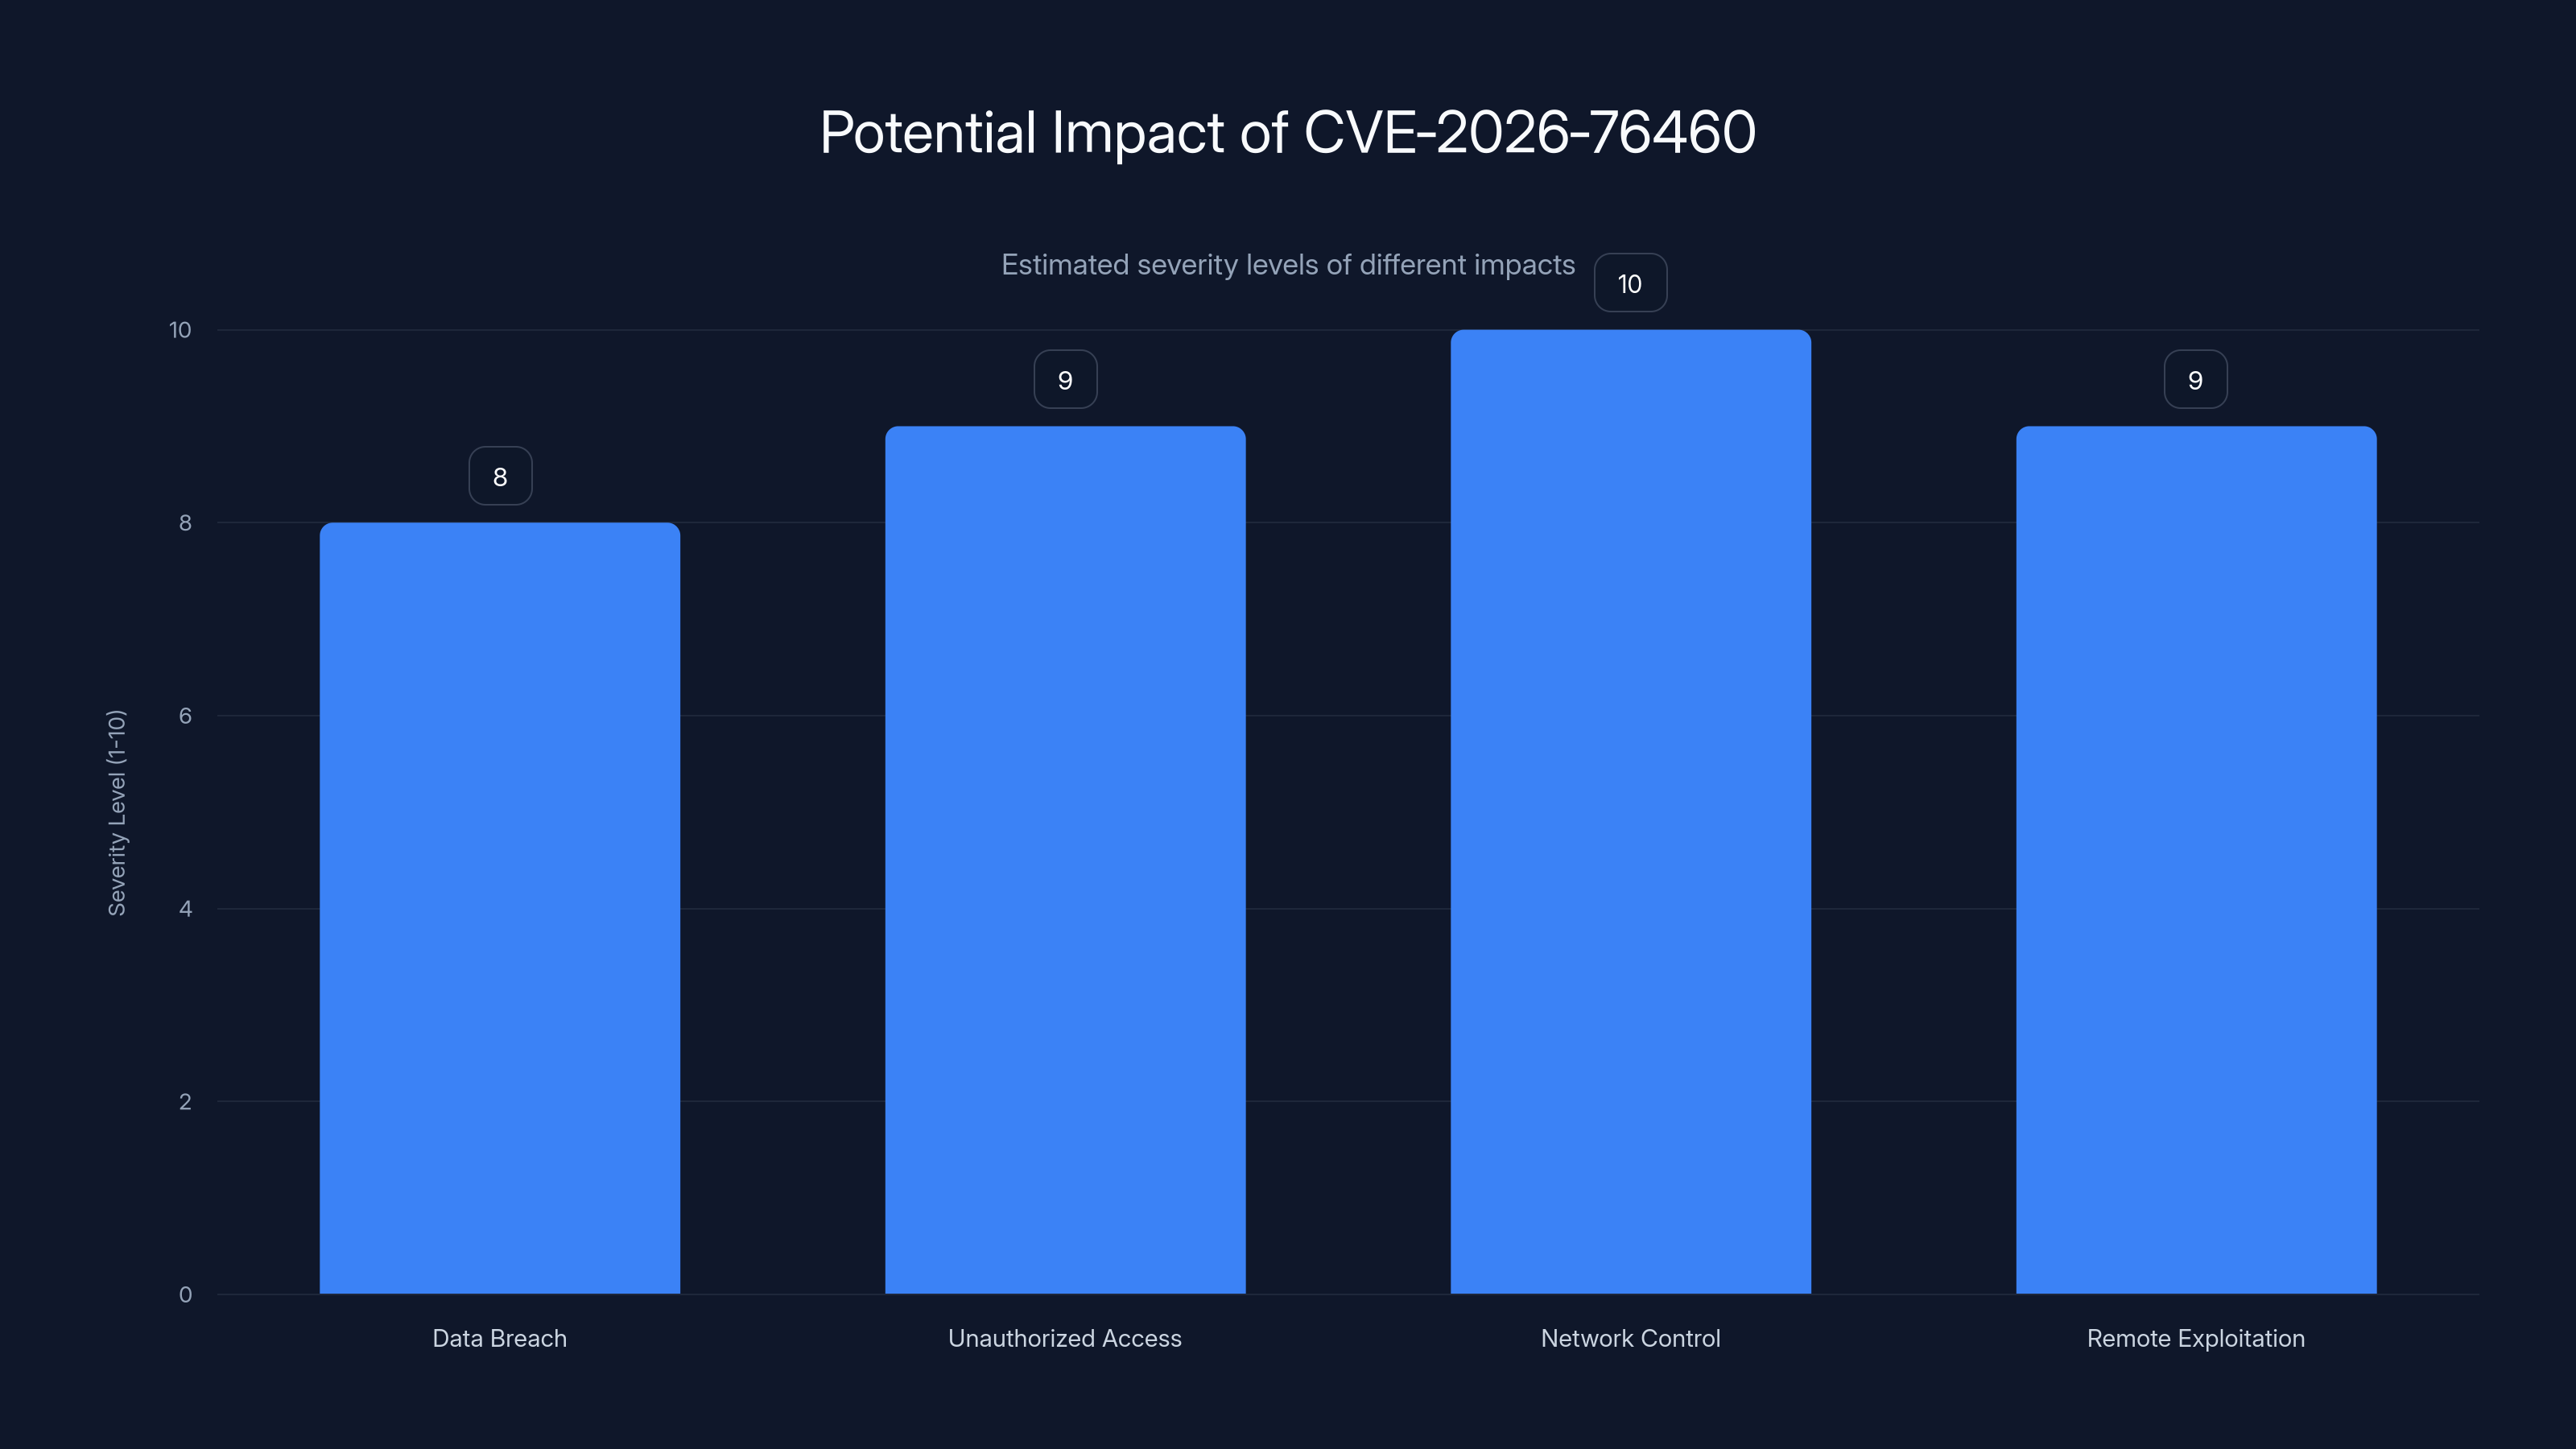
The CVE‑2026‑76460 vulnerability poses high severity risks, particularly in network control and remote exploitation. Estimated data.
Common Pitfalls and Solutions
While patching is straightforward, there are common issues that can arise:
- Compatibility Issues: Ensure all system dependencies are compatible with the new patch.
- Downtime Concerns: Plan patch deployment during off-peak hours to minimize disruption.
- Verification: Post-patch verification is crucial to ensure the vulnerability is closed effectively.
Strengthening Your Network's Security Posture
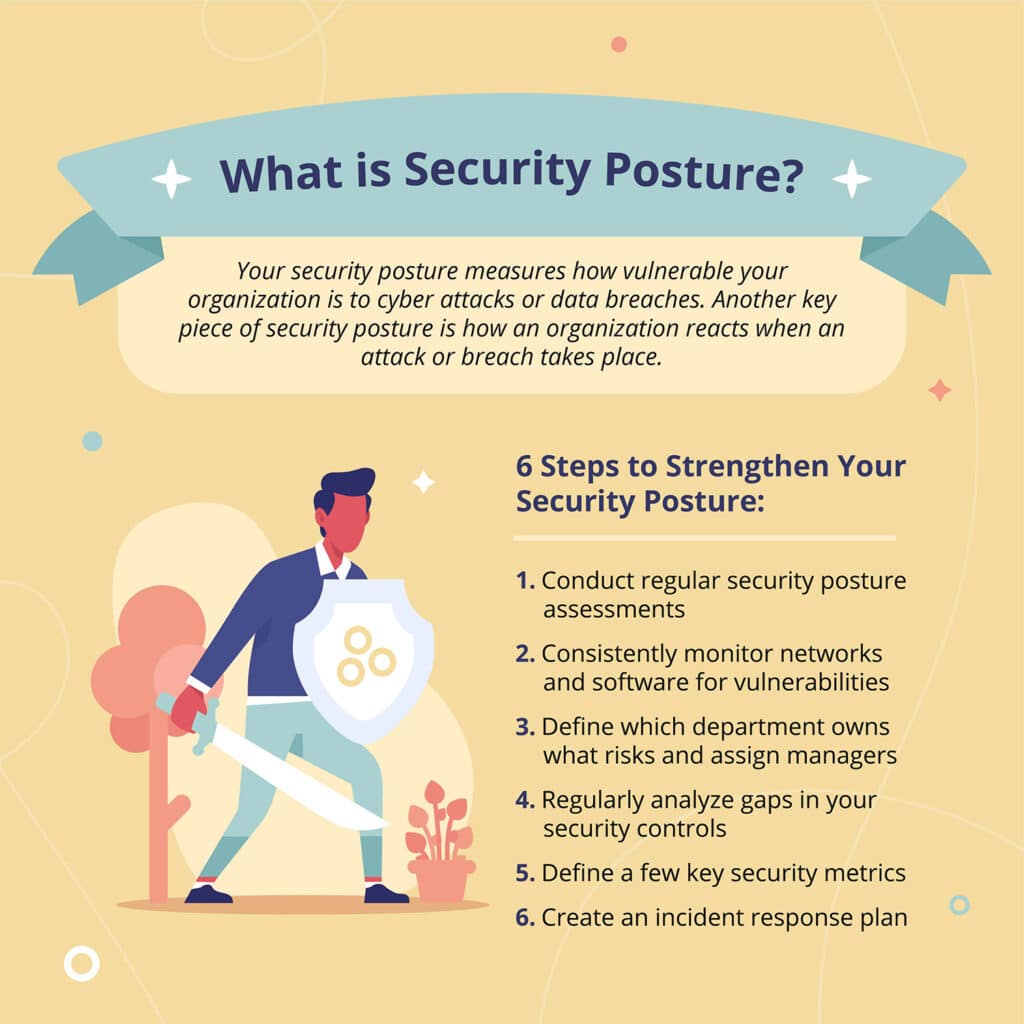
Patching is just one part of a comprehensive security strategy. Here are additional measures to fortify your network:
Implement Multi-Factor Authentication (MFA)
Adding an extra layer of security with MFA can prevent unauthorized access even if credentials are compromised.
Conduct Regular Security Audits
Routine audits help identify potential vulnerabilities and ensure compliance with best practices.
Utilize Network Segmentation
Divide your network into segments to contain any breaches and limit the movement of unauthorized users.
Future Trends in Network Security
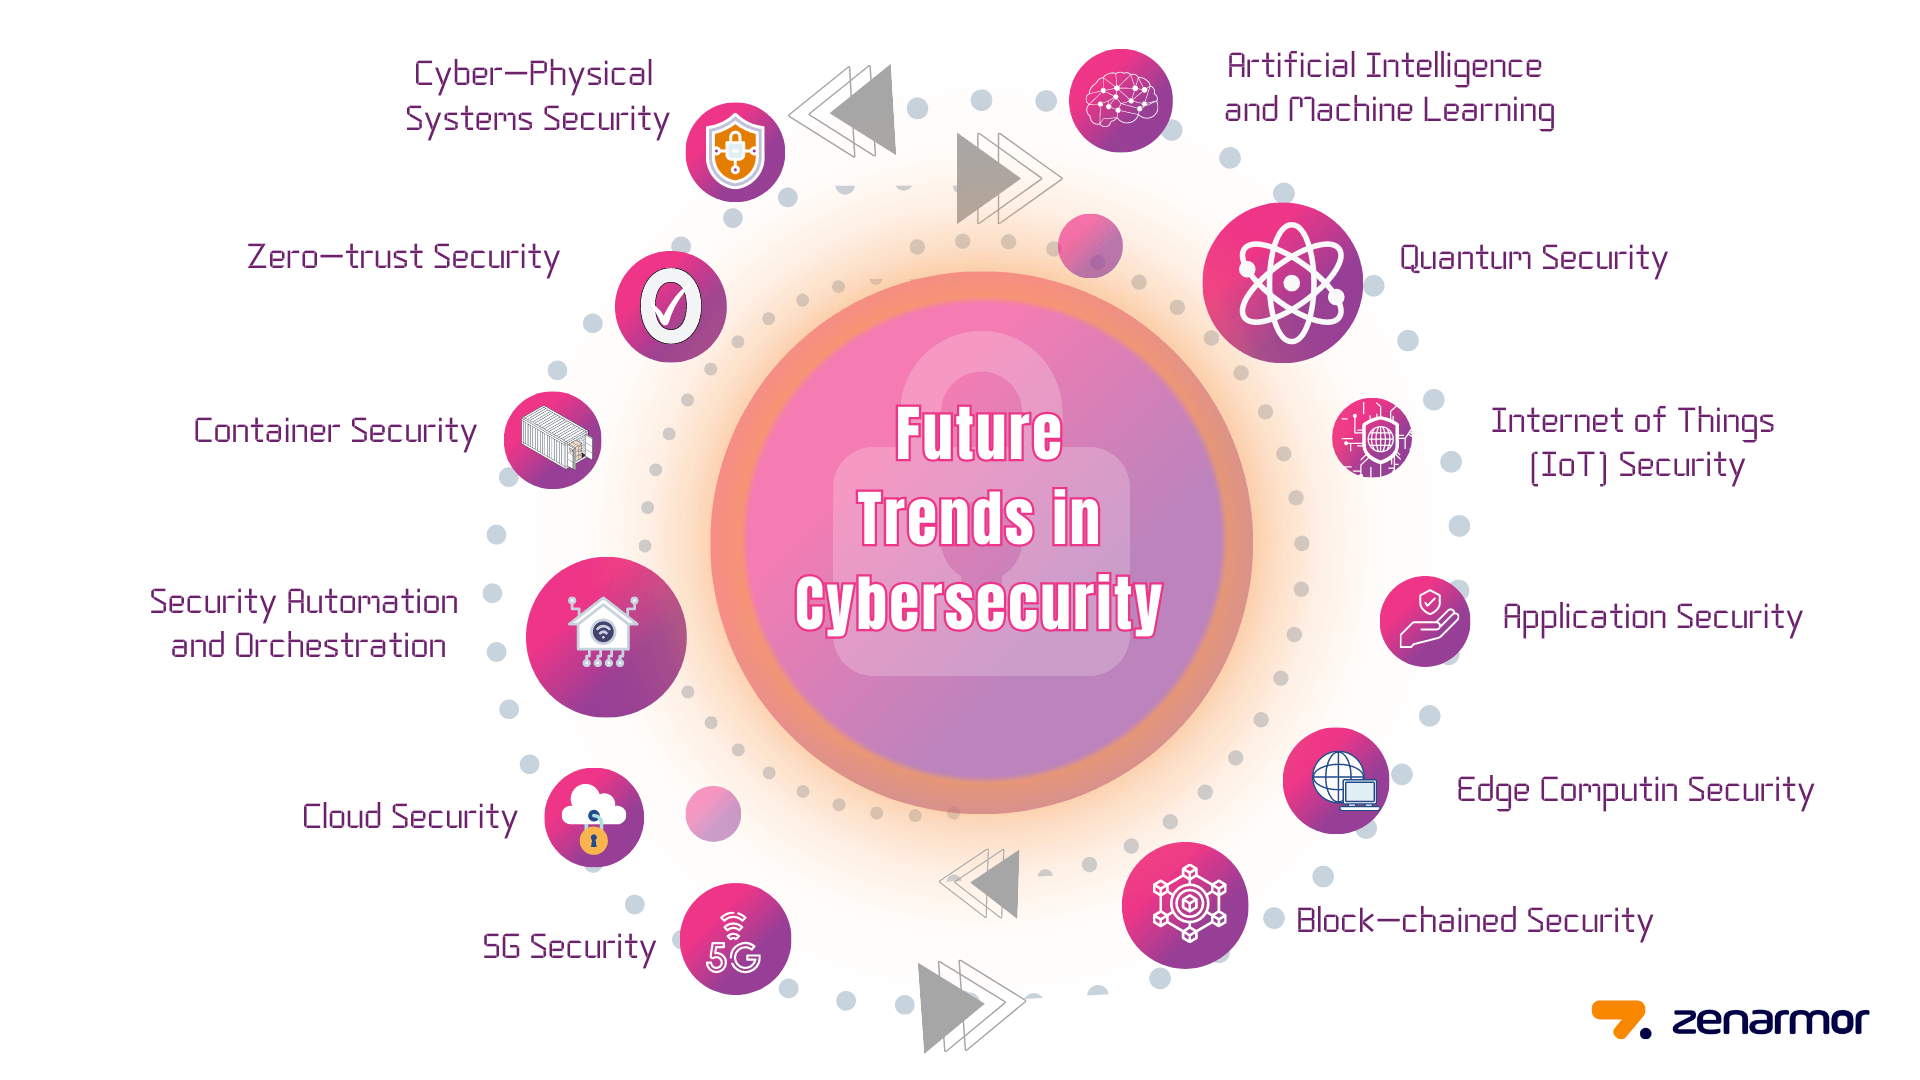
The landscape of cybersecurity is constantly evolving. Here are some trends to watch:
AI and Machine Learning
AI-driven security solutions are becoming more prevalent, providing real-time threat detection and response.
Increased Collaboration
Expect more partnerships between cybersecurity firms and tech giants to address emerging threats collectively.
Rise of Zero Trust Architectures
Adopting a zero-trust model ensures that no user or device is trusted by default, reducing the risk of insider threats.
Conclusion: Stay Vigilant
The Cisco ISE zero-day exploit is a reminder of the ever-present threats in today's digital world. By staying informed and proactive, you can protect your network and ensure business continuity.
FAQ
What is a zero-day exploit?
A zero-day exploit is a vulnerability that is actively exploited by attackers before the software vendor has released a patch or fix.
How does the Cisco ISE vulnerability affect my network?
It allows unauthenticated API access, potentially leading to data breaches and unauthorized control over network devices.
What are the best practices for securing my network?
Implement multi-factor authentication, conduct regular security audits, and use network segmentation to enhance security.
Are there any workarounds for CVE‑2026‑76460?
No, there are no workarounds. Patching your systems is the only effective mitigation.
How can I stay updated on future vulnerabilities?
Subscribe to security bulletins from vendors like Cisco, and follow industry news for the latest updates and patches.
Key Takeaways
- Max Severity Threat: Cisco ISE's zero-day exploit poses significant risks.
- Immediate Patching: Apply the patch now to secure your systems.
- Enhanced Security: Use MFA, regular audits, and network segmentation.
- Stay Informed: Follow industry trends and updates.
- Proactive Measures: Adopt zero-trust architectures for future protection.
The Road Ahead
As cyber threats continue to evolve, so must our defenses. By staying informed and adopting best practices, organizations can mitigate risks and protect their digital assets effectively. Remember, cybersecurity is not a one-time fix but an ongoing commitment.
Related Articles
- Understanding Zero-Day Attacks: Lessons from the Pixel Phone Hack [2025]
- AI and Digital Sovereignty: Navigating the Data Control Landscape for UK Businesses [2025]
- Agentic AI: The Future of Security and Compliance [2025]
- Meteor Tracking Nonprofit's Cyberattack: Lessons and Future Resilience [2025]
- Understanding Google's MCP Support for Third-Party AI Agents [2025]
- Unmasking AI-Powered Dating App Scams: The New Age of Romance Deception [2025]


