
Understanding Zero-Day Attacks: Lessons from the Pixel Phone Hack [2025]
Zero-day attacks are like the boogeyman of the cybersecurity world—unseen, unpredictable, and often devastating. Google's recent admission that some Pixel phone owners were compromised in a zero-day attack highlights the persistent threat these vulnerabilities pose. In this article, we’ll delve into what zero-day attacks are, how they work, and what lessons can be learned from the Pixel phone incident.
TL; DR
- Zero-day attacks exploit undiscovered vulnerabilities before developers can patch them.
- The Pixel phone hack involved a modem vulnerability that allowed privilege escalation.
- Zero-click attacks require no user interaction, making them especially dangerous.
- Routine updates and patches are critical for minimizing risks.
- Future security trends include AI-driven threat detection and stronger device isolation techniques.
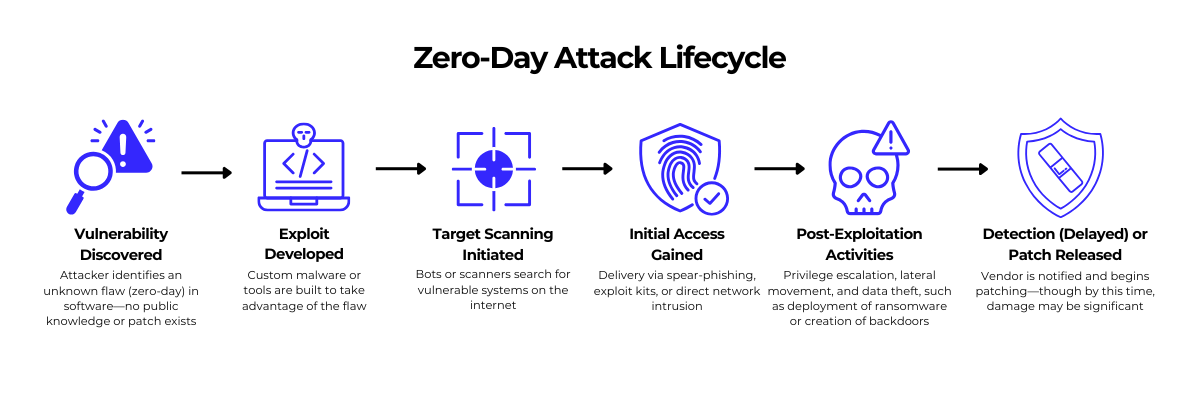
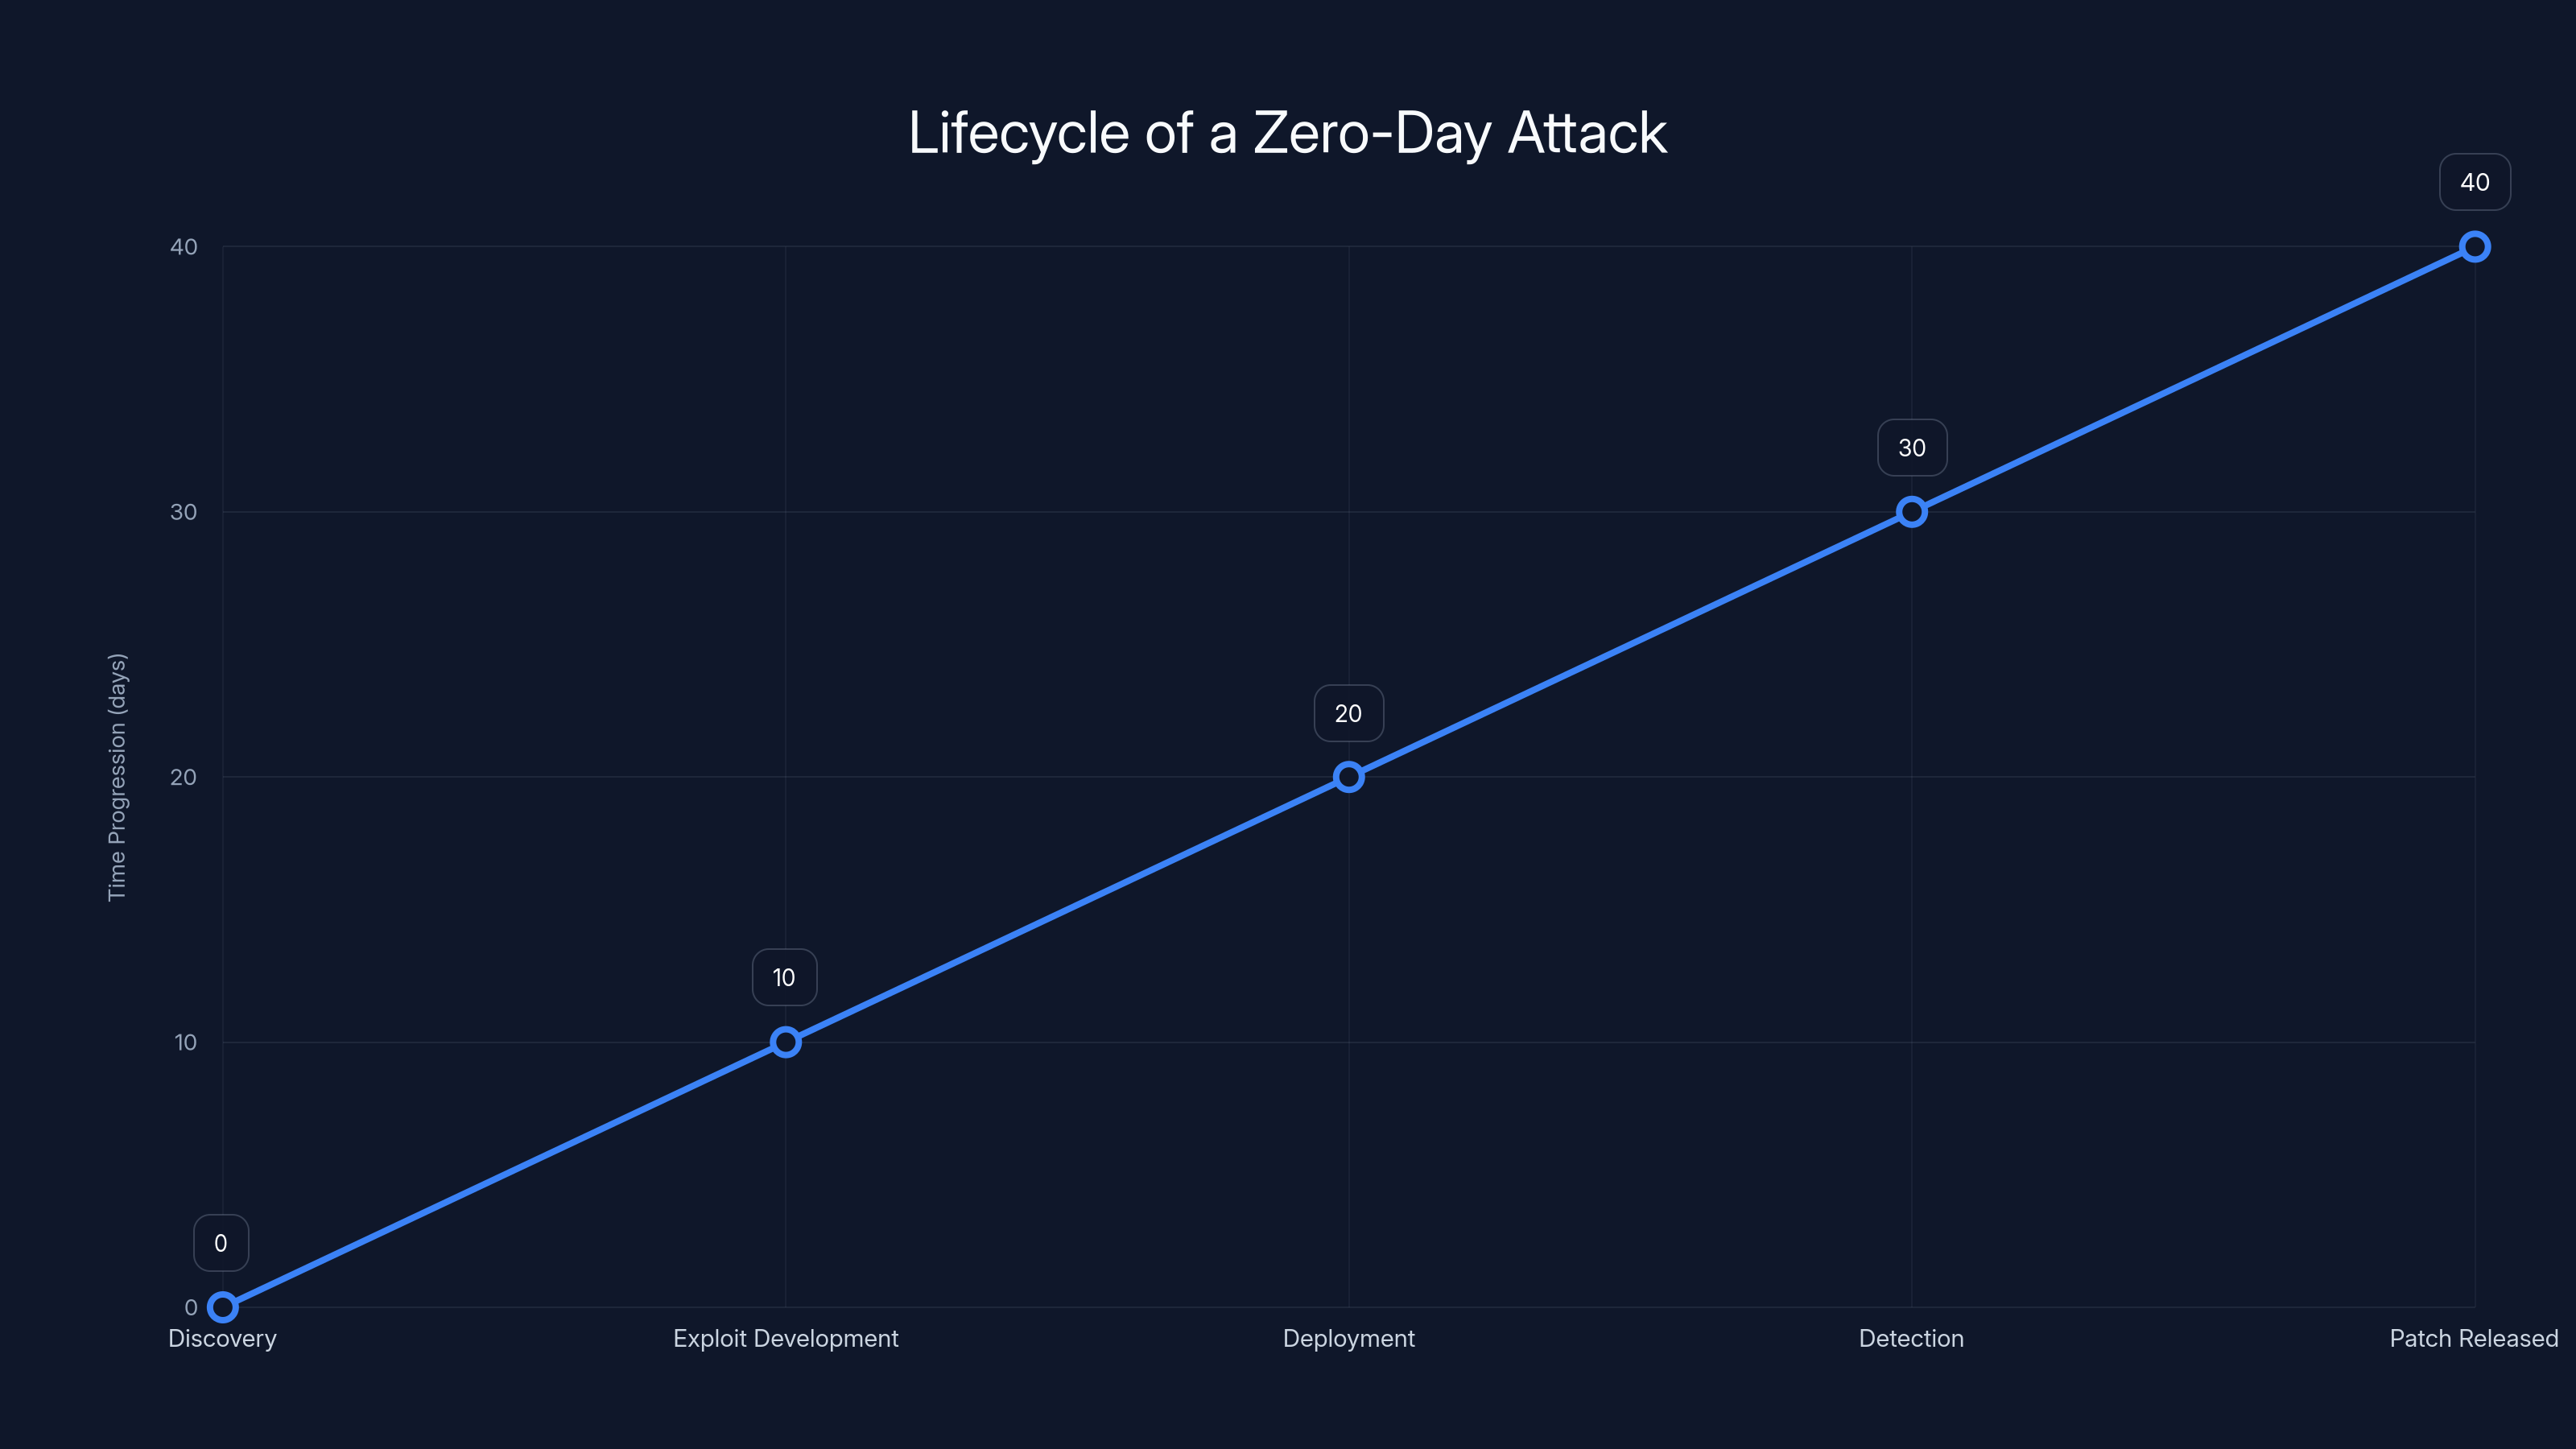
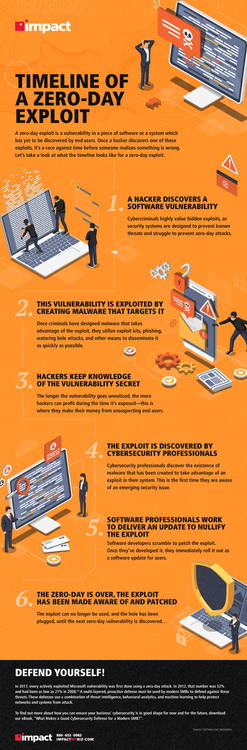
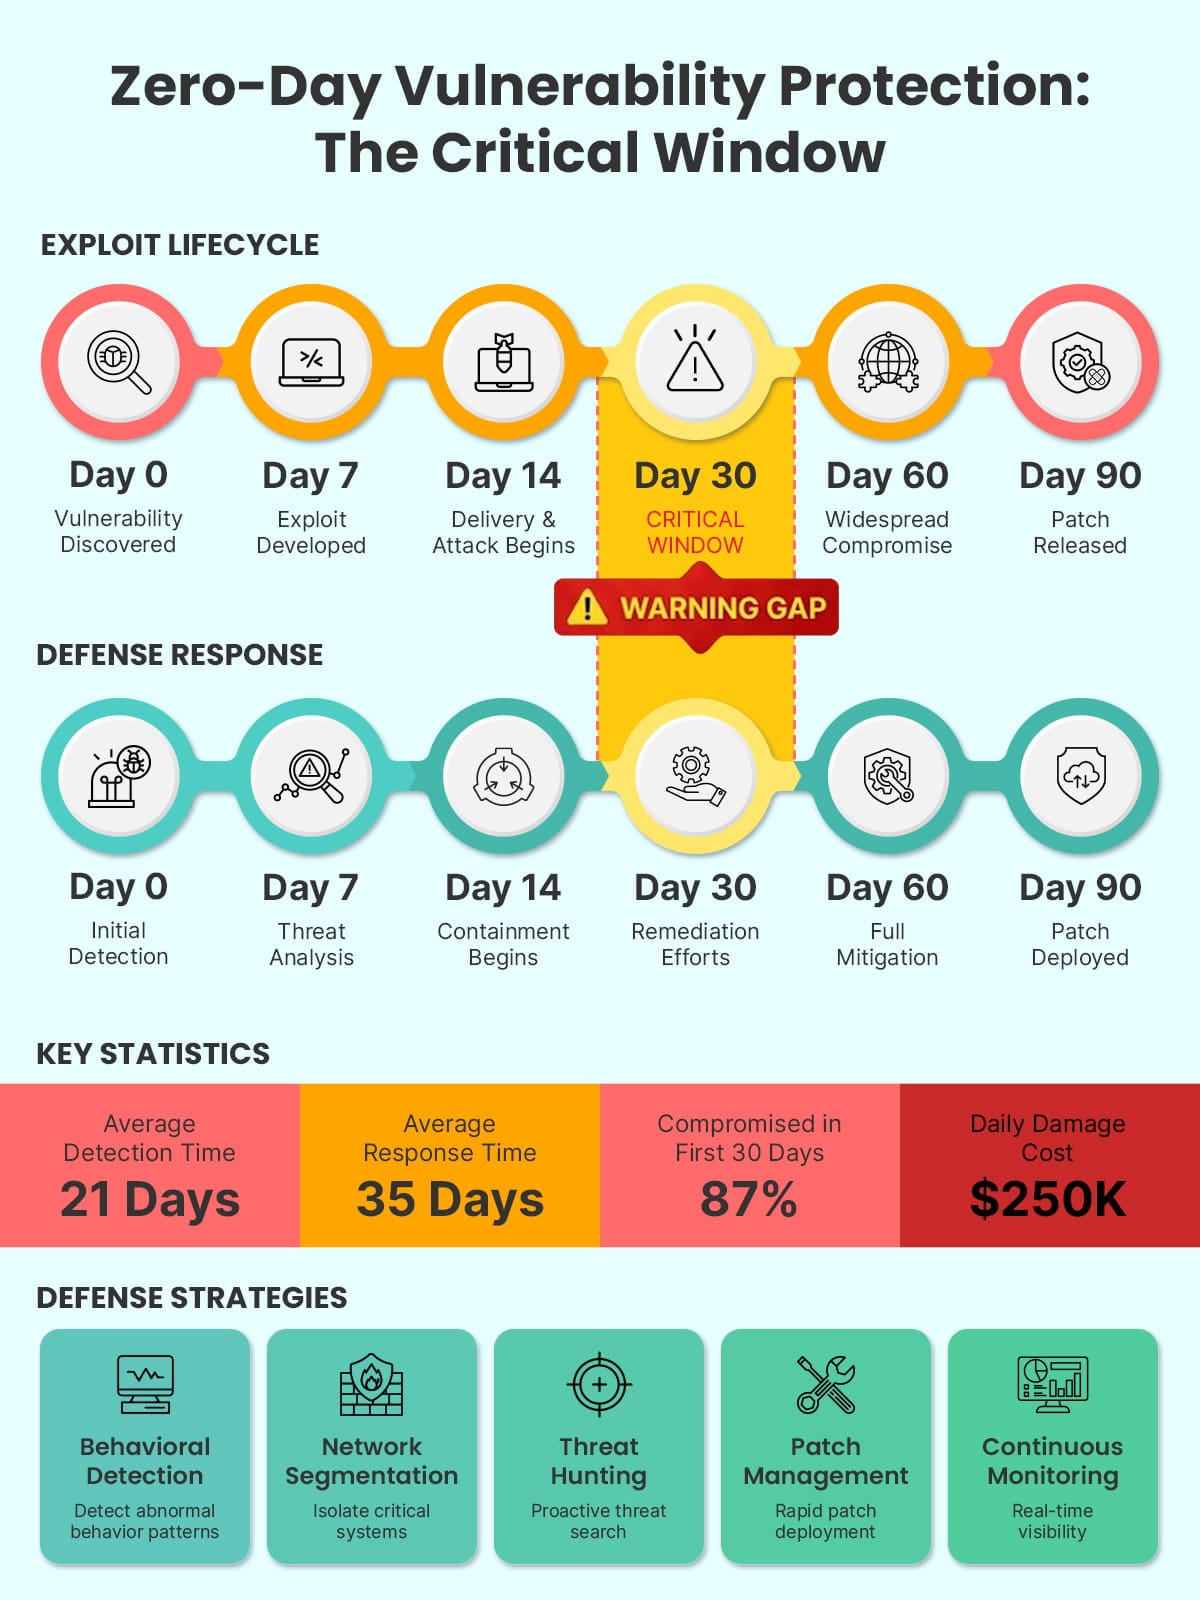
This chart illustrates the typical progression of a zero-day attack from discovery to patching. Estimated data shows that detection and patching can take significant time, allowing exploitation in the interim.
What Are Zero-Day Attacks?
A zero-day attack takes advantage of a software vulnerability that is unknown to the software maker or antivirus vendors. By the time the vulnerability is discovered, it has potentially already been exploited. The term "zero-day" indicates that developers have had zero days to address and patch the vulnerability.
How Zero-Day Attacks Work
- Discovery: A hacker discovers a vulnerability within a piece of software.
- Exploit Development: The hacker develops an exploit to take advantage of the flaw.
- Deployment: The exploit is deployed, often without detection.
- Detection and Patch: Eventually, the vulnerability is identified, a patch is developed, and the exploit is rendered ineffective—assuming users apply the updates.
Example: CVE-2026-58704
In the case of the Pixel phone hack, the zero-day attack involved a bug within the phone’s modem. This vulnerability allowed attackers to execute a privilege escalation, gaining access to data beyond the modem's protected environment.

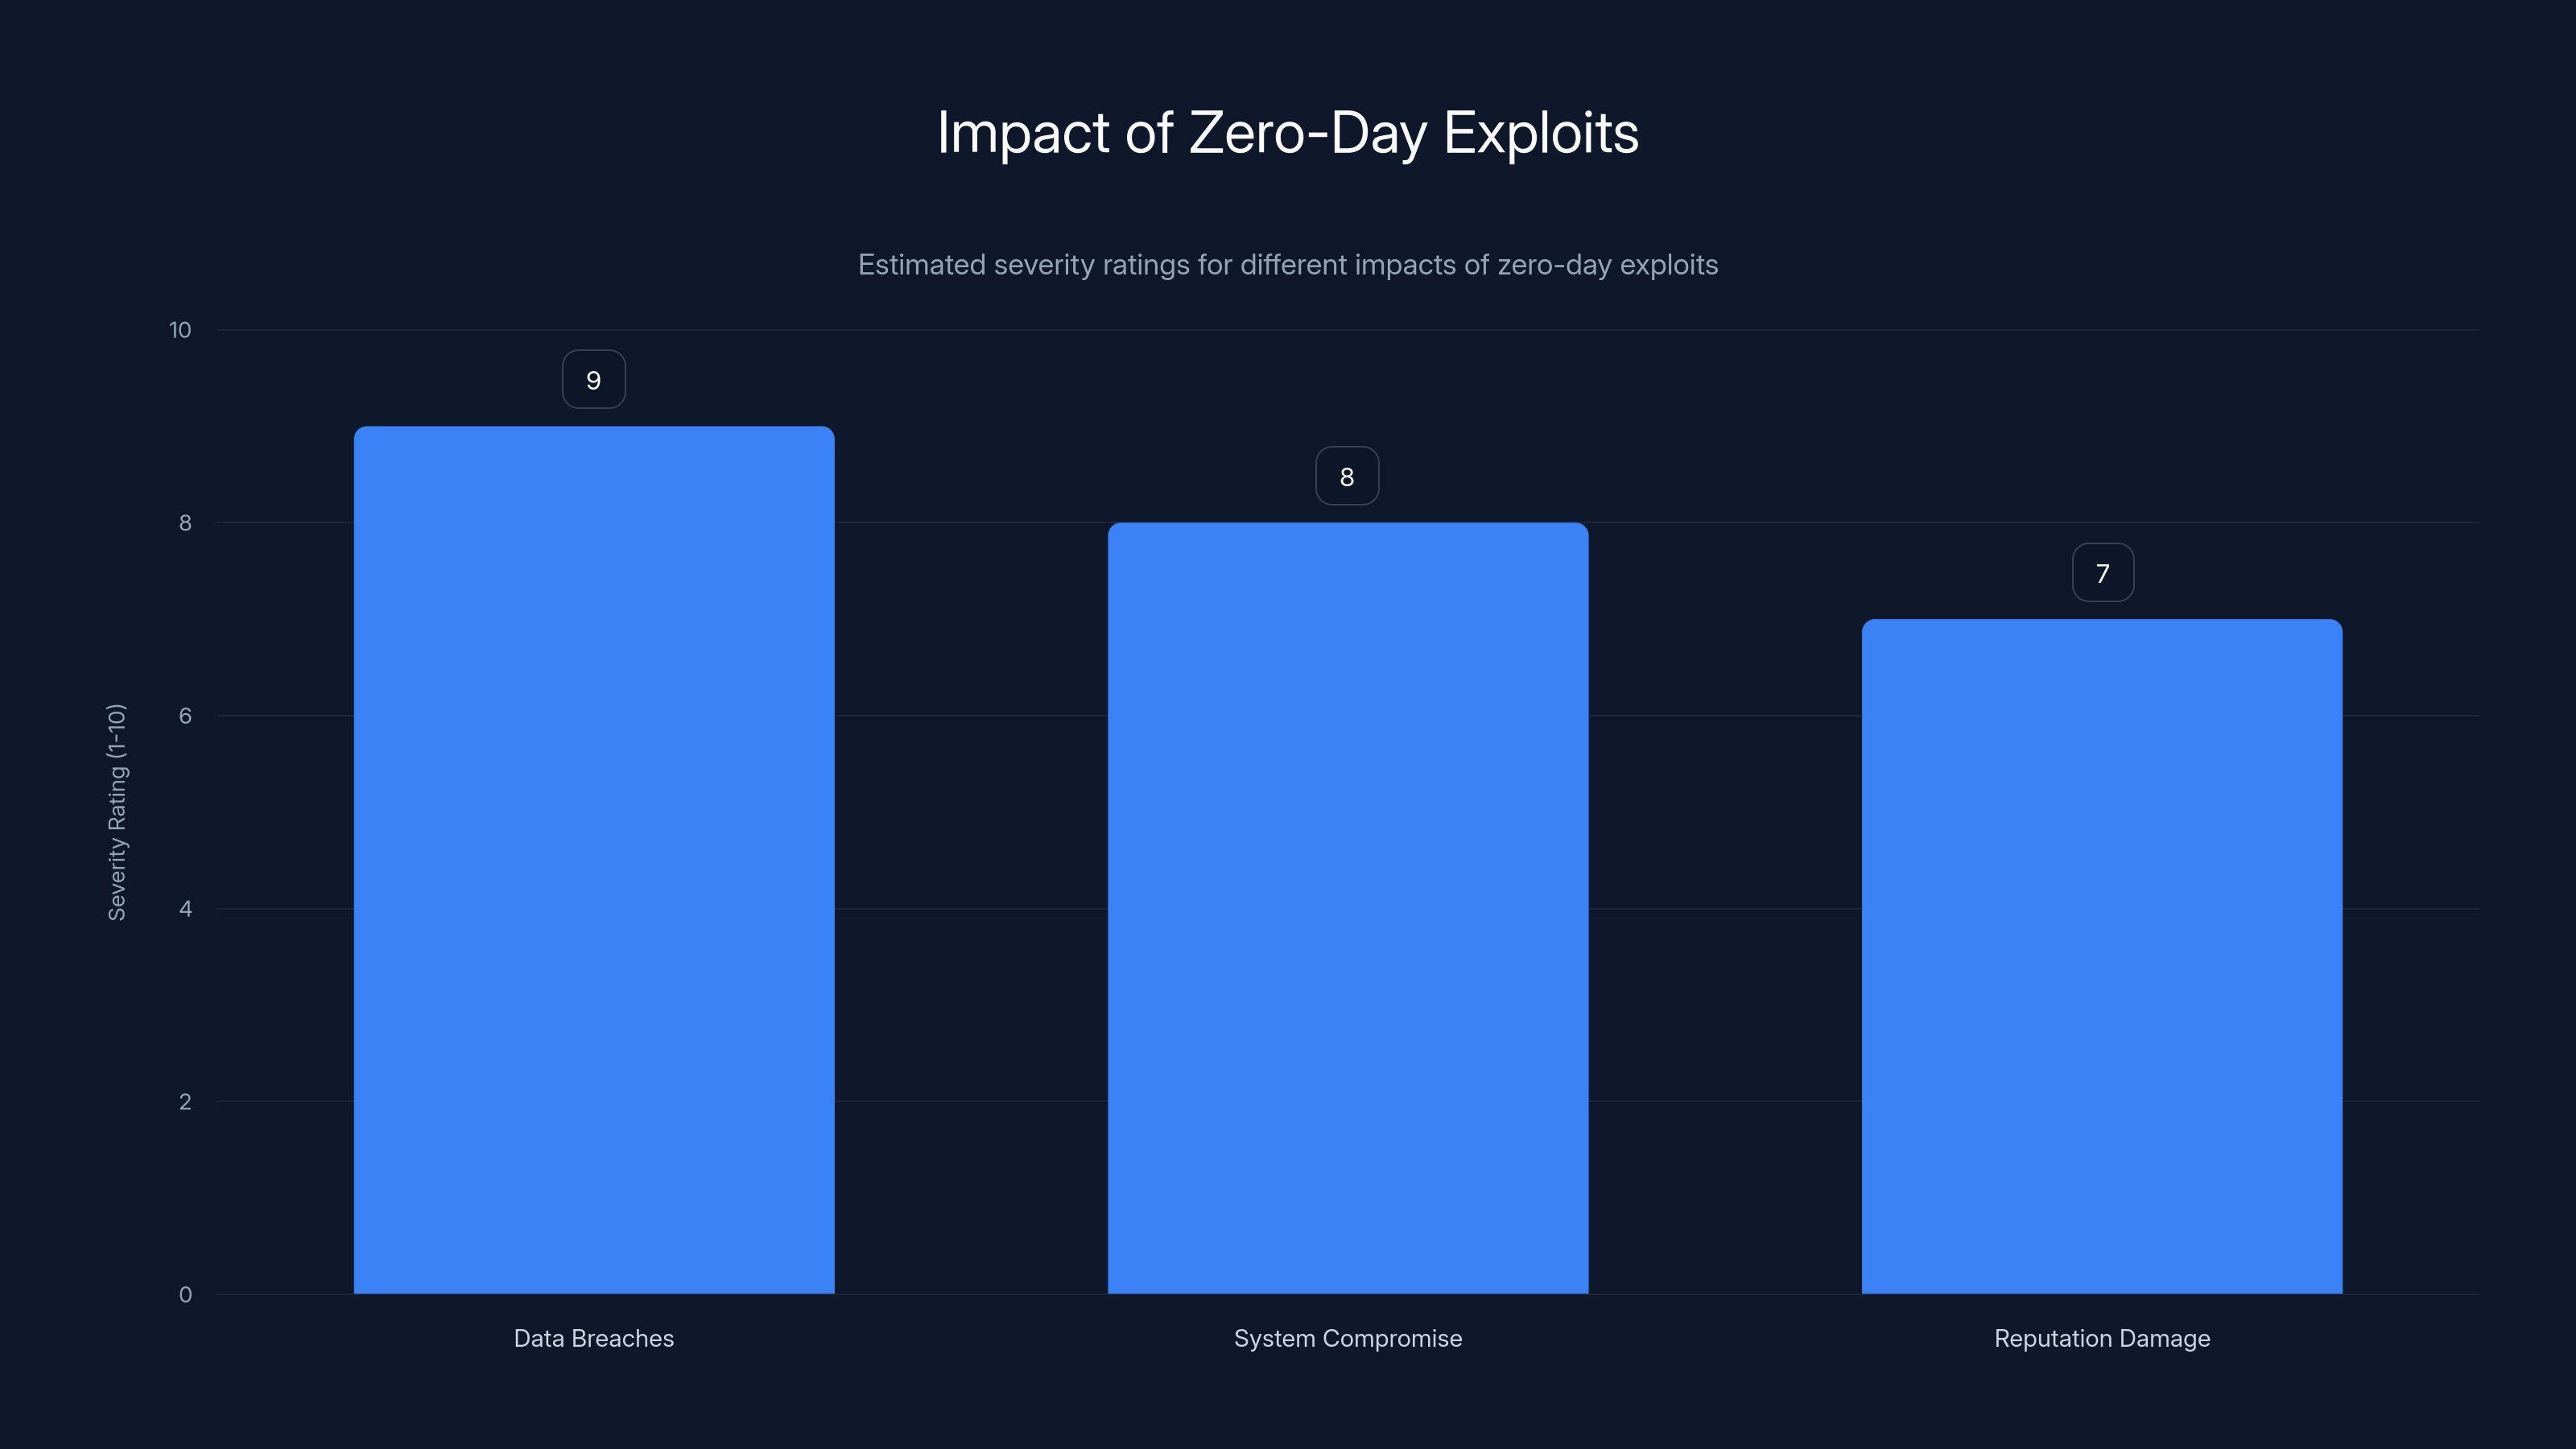
Zero-day exploits have severe impacts, with data breaches rated highest in severity. Estimated data based on typical consequences.
Why Are Zero-Day Attacks So Dangerous?
Zero-day attacks are particularly dangerous because they can be executed silently and without any interaction from the victim, known as zero-click attacks. This makes them incredibly difficult to detect and prevent.
Impact of Zero-Day Exploits
- Data Breaches: Sensitive information can be stolen, leading to identity theft or financial loss.
- System Compromise: Systems can be manipulated to perform unauthorized actions.
- Reputation Damage: Companies may suffer long-term reputational damage if they fail to protect customer data.
The Pixel Phone Incident: What Happened?
Google's Pixel phones were targeted via a zero-day vulnerability in their modem. This allowed attackers to bypass the typical security protocols, accessing sensitive data without user knowledge. Google has since patched the vulnerability, tracked as CVE-2026-58704.
Technical Breakdown
- Vulnerability Type: Privilege Escalation
- Attack Vector: Zero-click, modem exploit
- Patch Released: Yes, after the vulnerability was detected

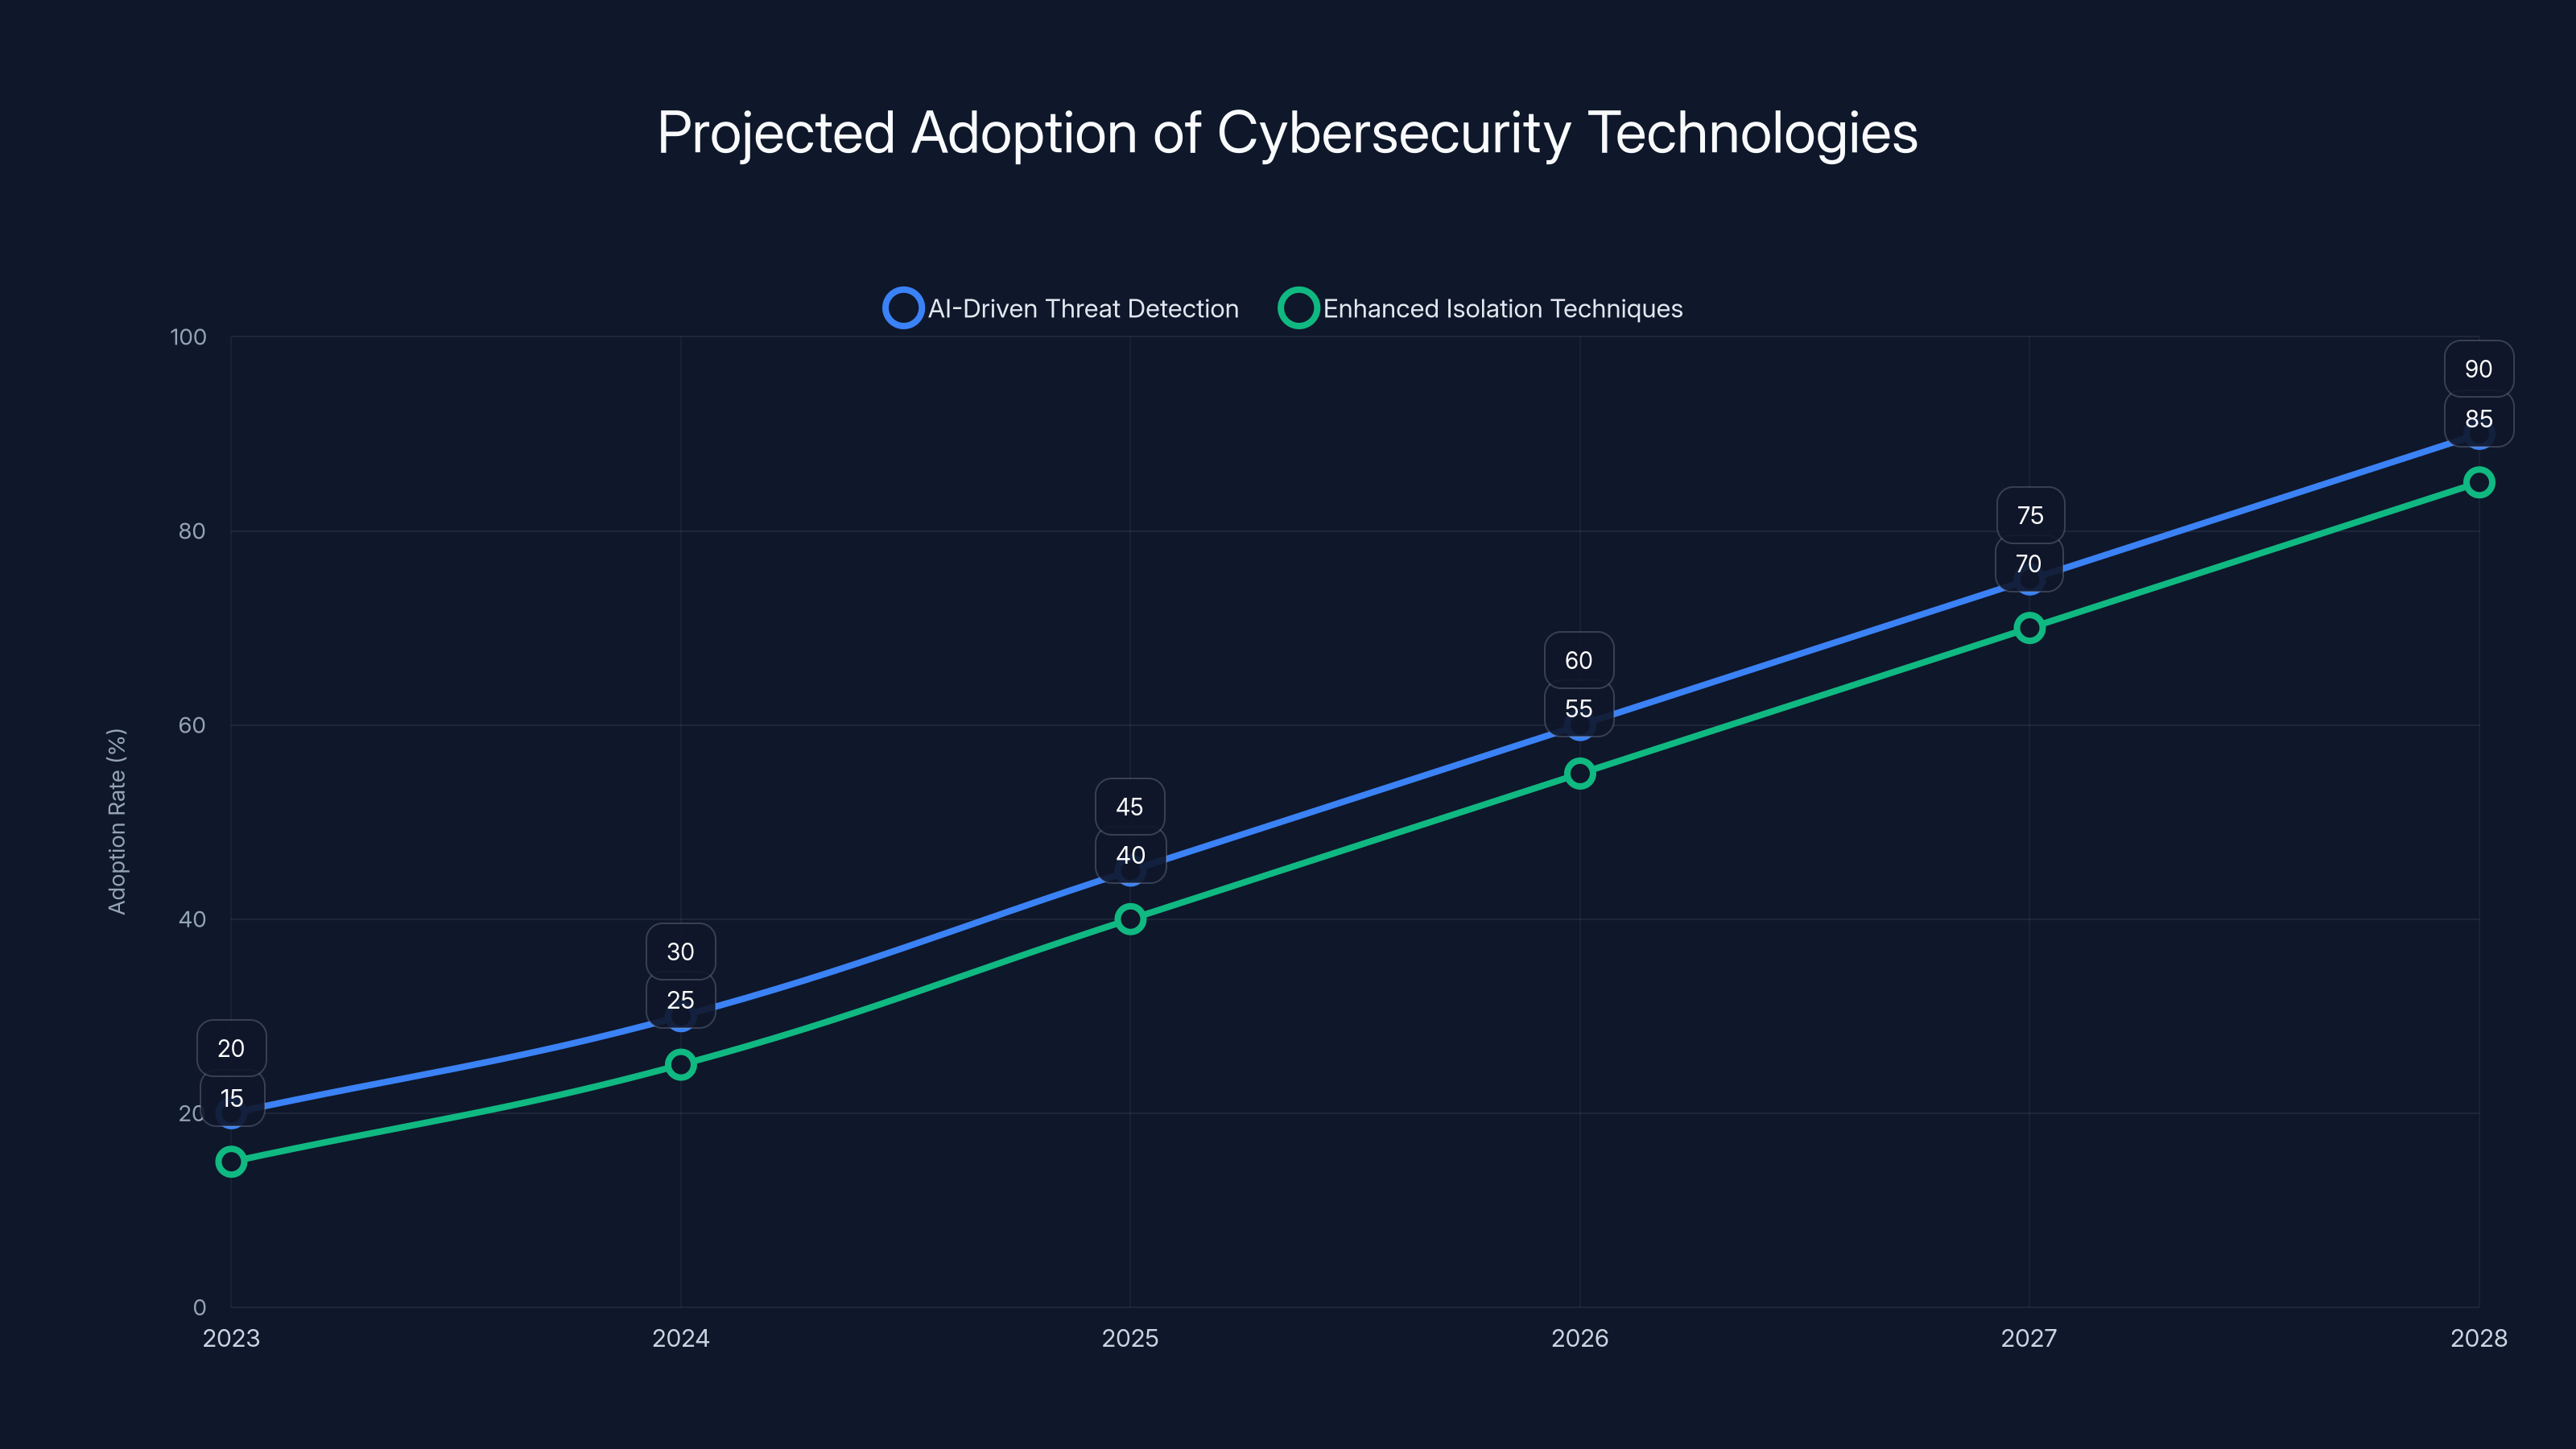
AI-driven threat detection and enhanced isolation techniques are projected to see significant adoption growth over the next five years. Estimated data.
Protecting Against Zero-Day Attacks
While zero-day attacks are challenging to guard against due to their unpredictable nature, there are strategies that can mitigate their risk.
Best Practices
- Regular Updates: Ensure all devices and software are up-to-date with the latest security patches.
- Network Monitoring: Implement robust network monitoring tools to detect unusual activity.
- Employee Training: Train employees to recognize phishing attempts and suspicious activities.
- Use of Security Software: Employ advanced antivirus software that includes zero-day exploit protection.
Common Pitfalls and Solutions
Pitfall: Delayed Patch Deployment
Solution: Automate updates to ensure that security patches are applied as soon as they are released.
Pitfall: Lack of Awareness
Solution: Conduct regular security awareness programs to educate users about potential threats.
Future Trends in Cybersecurity
As threats evolve, so must our defenses. Here are some trends to watch in the coming years.
AI-Driven Threat Detection
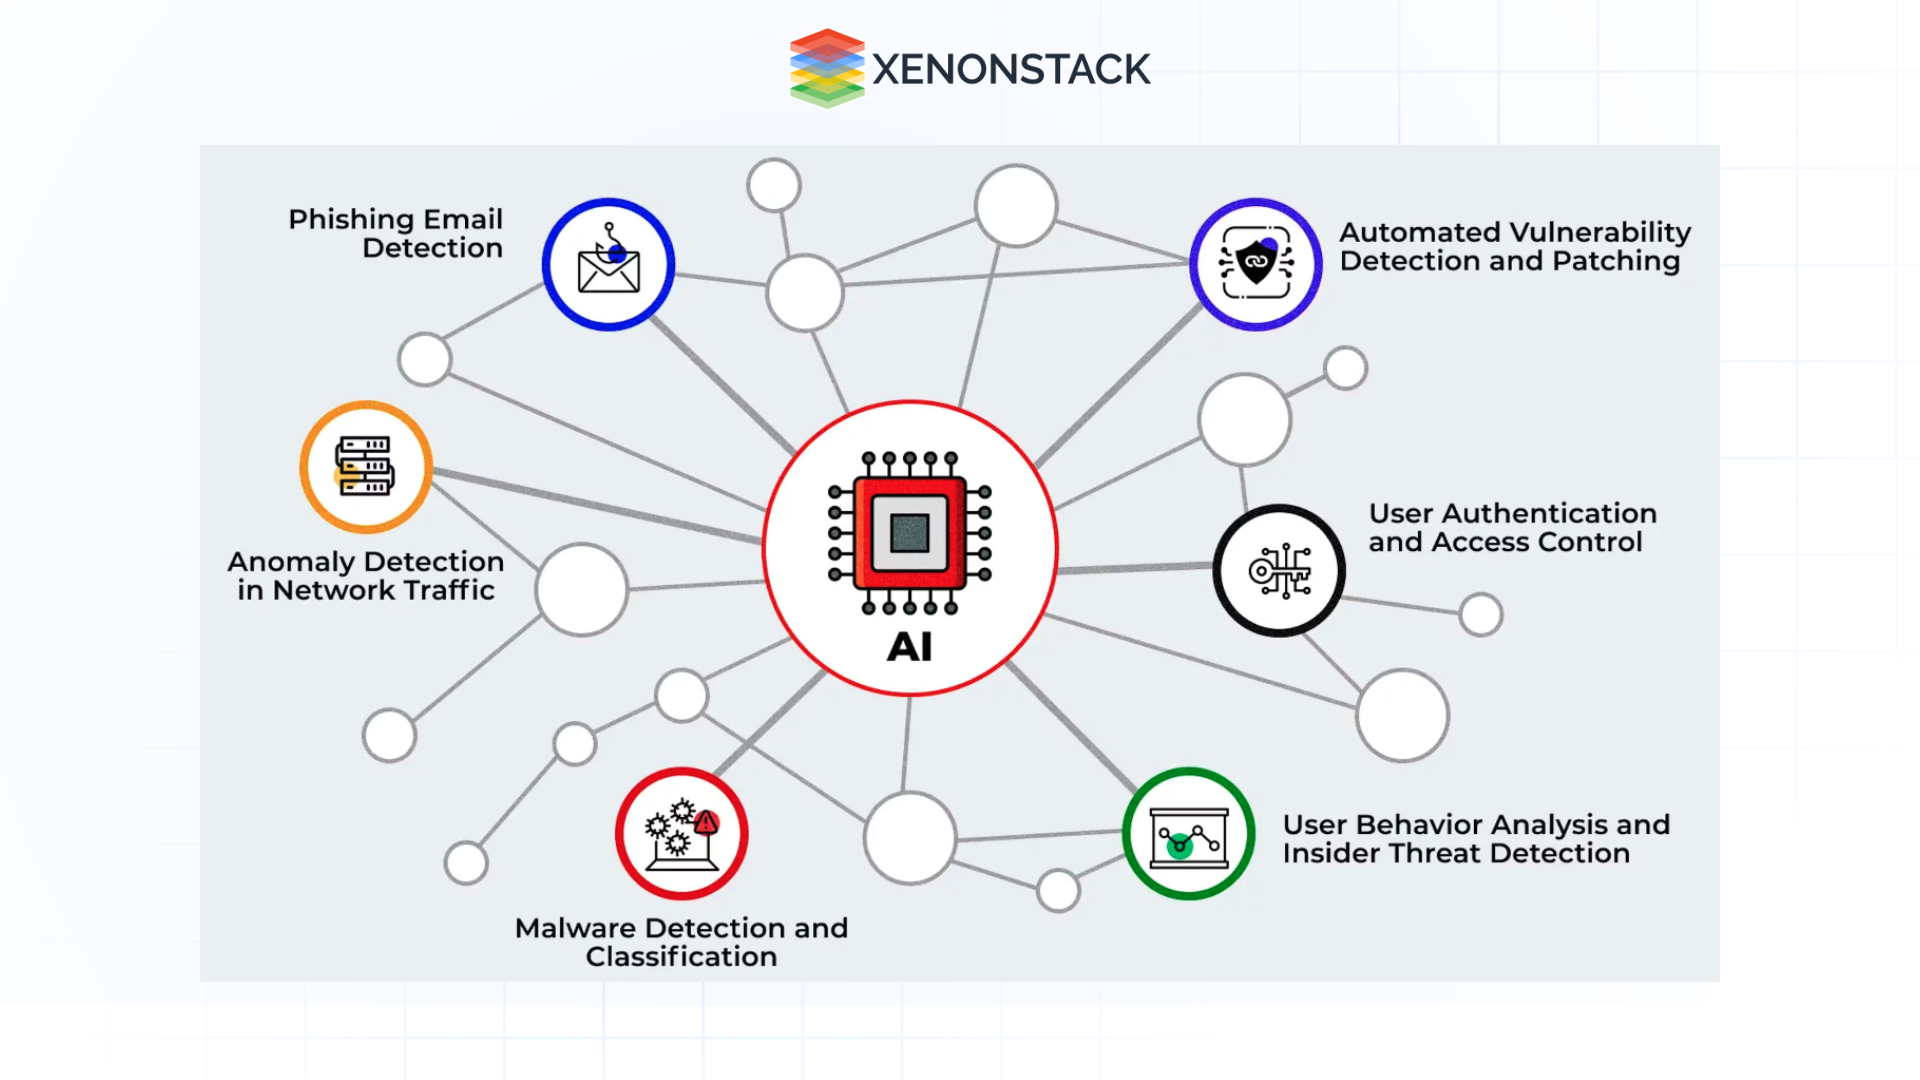
Artificial Intelligence (AI) is increasingly being used to identify potential threats before they can be exploited. AI systems can analyze vast amounts of data and recognize patterns indicative of zero-day exploits.
Enhanced Isolation Techniques
By improving isolation techniques, such as sandboxing, applications can be better protected from unauthorized access. This limits the potential damage zero-day exploits can cause.
Conclusion
Zero-day attacks will continue to pose significant challenges to individuals and organizations alike. However, by understanding how these attacks work and implementing proactive security measures, the risks can be significantly reduced. The Pixel phone hack serves as a reminder of the importance of vigilance and the need for ongoing investment in cybersecurity.
FAQ
What is a zero-day attack?
A zero-day attack exploits a software vulnerability that is unknown to the developers. Attackers use this to gain unauthorized access or control before a patch is available.
How does a zero-click attack work?
Zero-click attacks require no action from the user. They exploit vulnerabilities that can be triggered remotely without user interaction.
What can I do to protect my devices?
Regularly update your software, use robust security solutions, and educate yourself about potential threats to minimize risks.
Why are zero-day attacks increasing?
As software complexity increases, so do potential vulnerabilities. The lucrative nature of cybercrime also incentivizes attackers to discover and exploit these weaknesses.
How can AI help in cybersecurity?
AI can analyze large datasets to identify patterns indicative of threats, allowing for quicker detection and response to zero-day exploits.
Are some devices more vulnerable to zero-day attacks?
Devices that are not regularly updated or lack robust security measures are more vulnerable to zero-day attacks.
Key Takeaways
- Zero-day attacks exploit undiscovered vulnerabilities before developers can patch them.
- The Pixel phone hack involved a modem vulnerability that allowed privilege escalation.
- Zero-click attacks require no user interaction, making them especially dangerous.
- Routine updates and patches are critical for minimizing risks.
- Future security trends include AI-driven threat detection and stronger device isolation techniques.
Related Articles
- Understanding the Intricacies of Flock Camera Security Breaches [2025]
- Understanding Voicemail Phishing Attacks and How to Protect Your Organization [2025]
- Netgear's Wi-Fi 7 Mesh System: A Comprehensive Guide to the Future of Home Networking [2025]
- Understanding the RubyGems and OpenAI Incident: A Deep Dive [2025]
- Technology Sovereignty: Keeping Control, Not Geography [2025]
- Understanding and Combatting Deepfake Exploitation: A Comprehensive Guide [2025]


