
Understanding AI-Driven Android Malware: Threats, Techniques, and Safeguards [2025]
The digital landscape is no stranger to threats, but the rise of AI-enhanced malware represents a new frontier in cybersecurity challenges. This article delves into the intricacies of AI-driven Android malware, exploring its capabilities to automate device control and even resurrect itself after deletion. We’ll break down the technology, provide real-world examples, and offer practical advice on how to safeguard devices against these sophisticated threats.
TL; DR
- AI-enhanced malware can automate complex tasks, making it more dangerous than traditional threats. According to Cybersecurity Insiders, AI scammers may be more effective than their human counterparts.
- Self-resurrecting capabilities mean that this malware can return even after removal, as highlighted by Morphisec's analysis of polymorphic threats.
- User vigilance and updated security protocols are crucial in defending against these threats, as noted in a report by MSSP Alert.
- Machine learning algorithms are used to interpret device layouts, enabling precise control. This is supported by Zimperium's findings on AI-powered mobile threats.
- Future security measures must evolve to counteract AI adaptations in malware, as discussed in Cybersecurity Dive's survey on AI and national security risks.
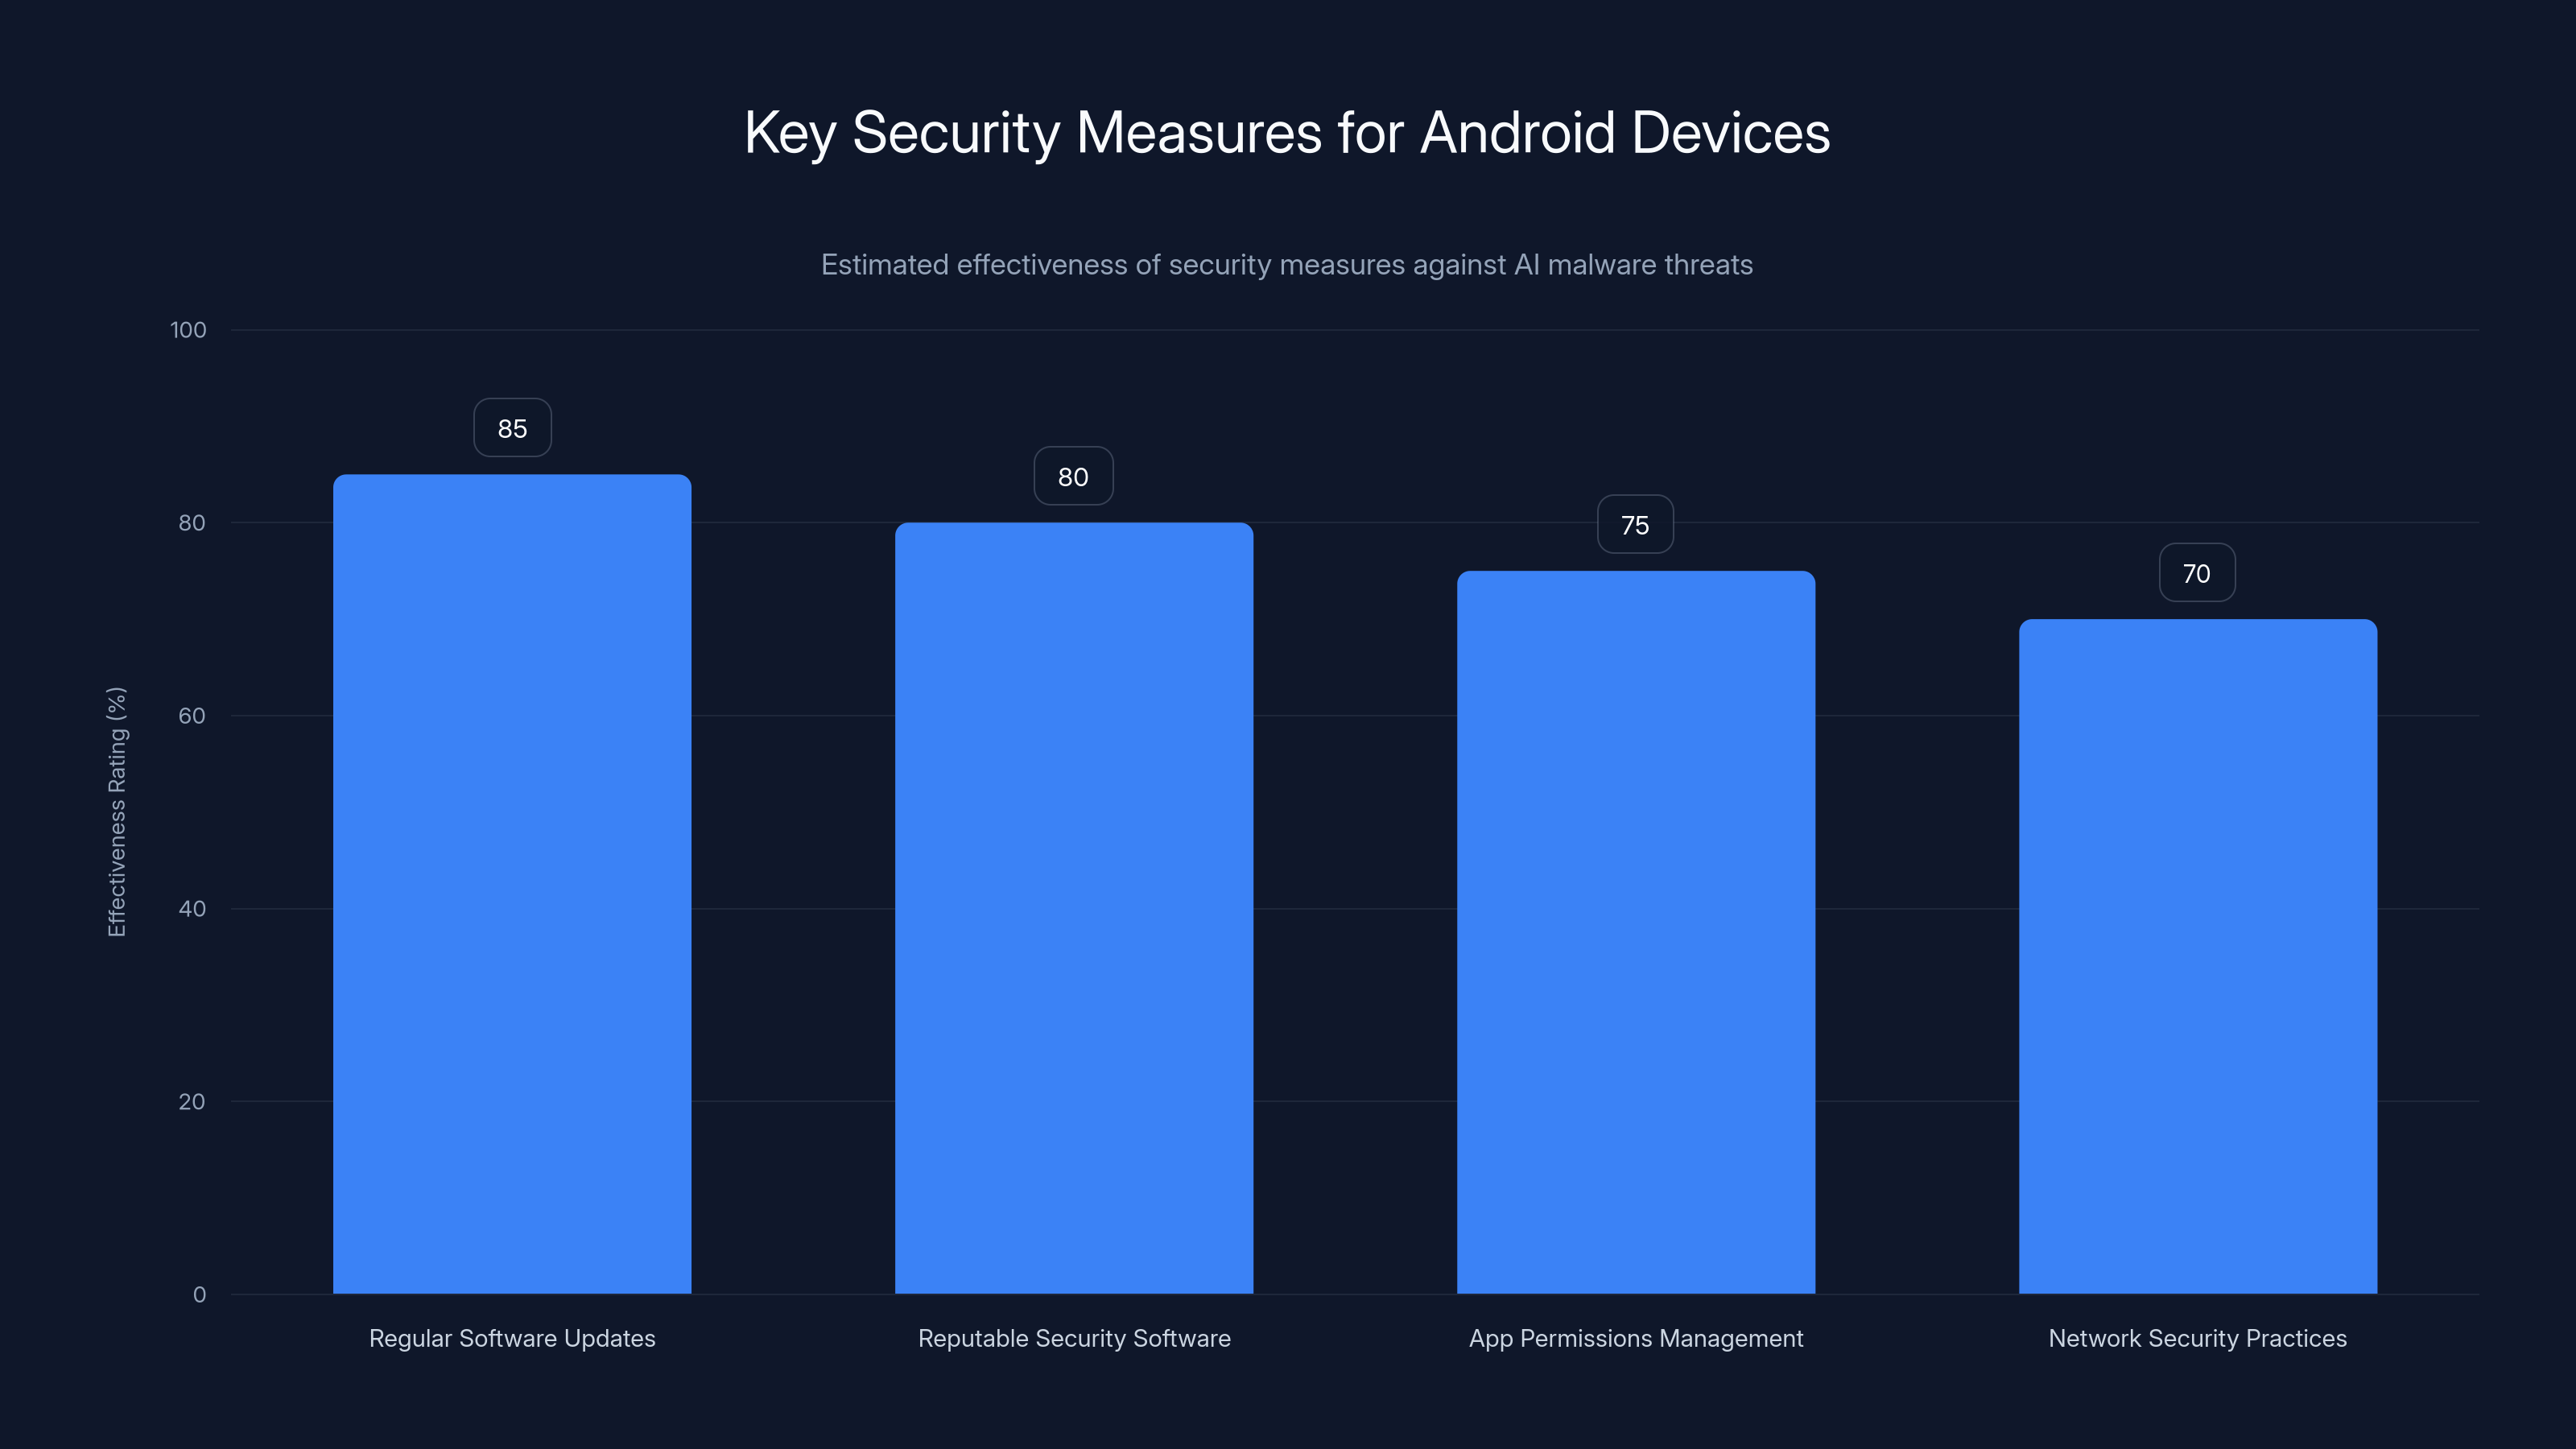
Regular software updates are the most effective measure against AI malware, with an estimated effectiveness of 85%. Estimated data.
The Evolution of Android Malware
A Brief History of Mobile Malware
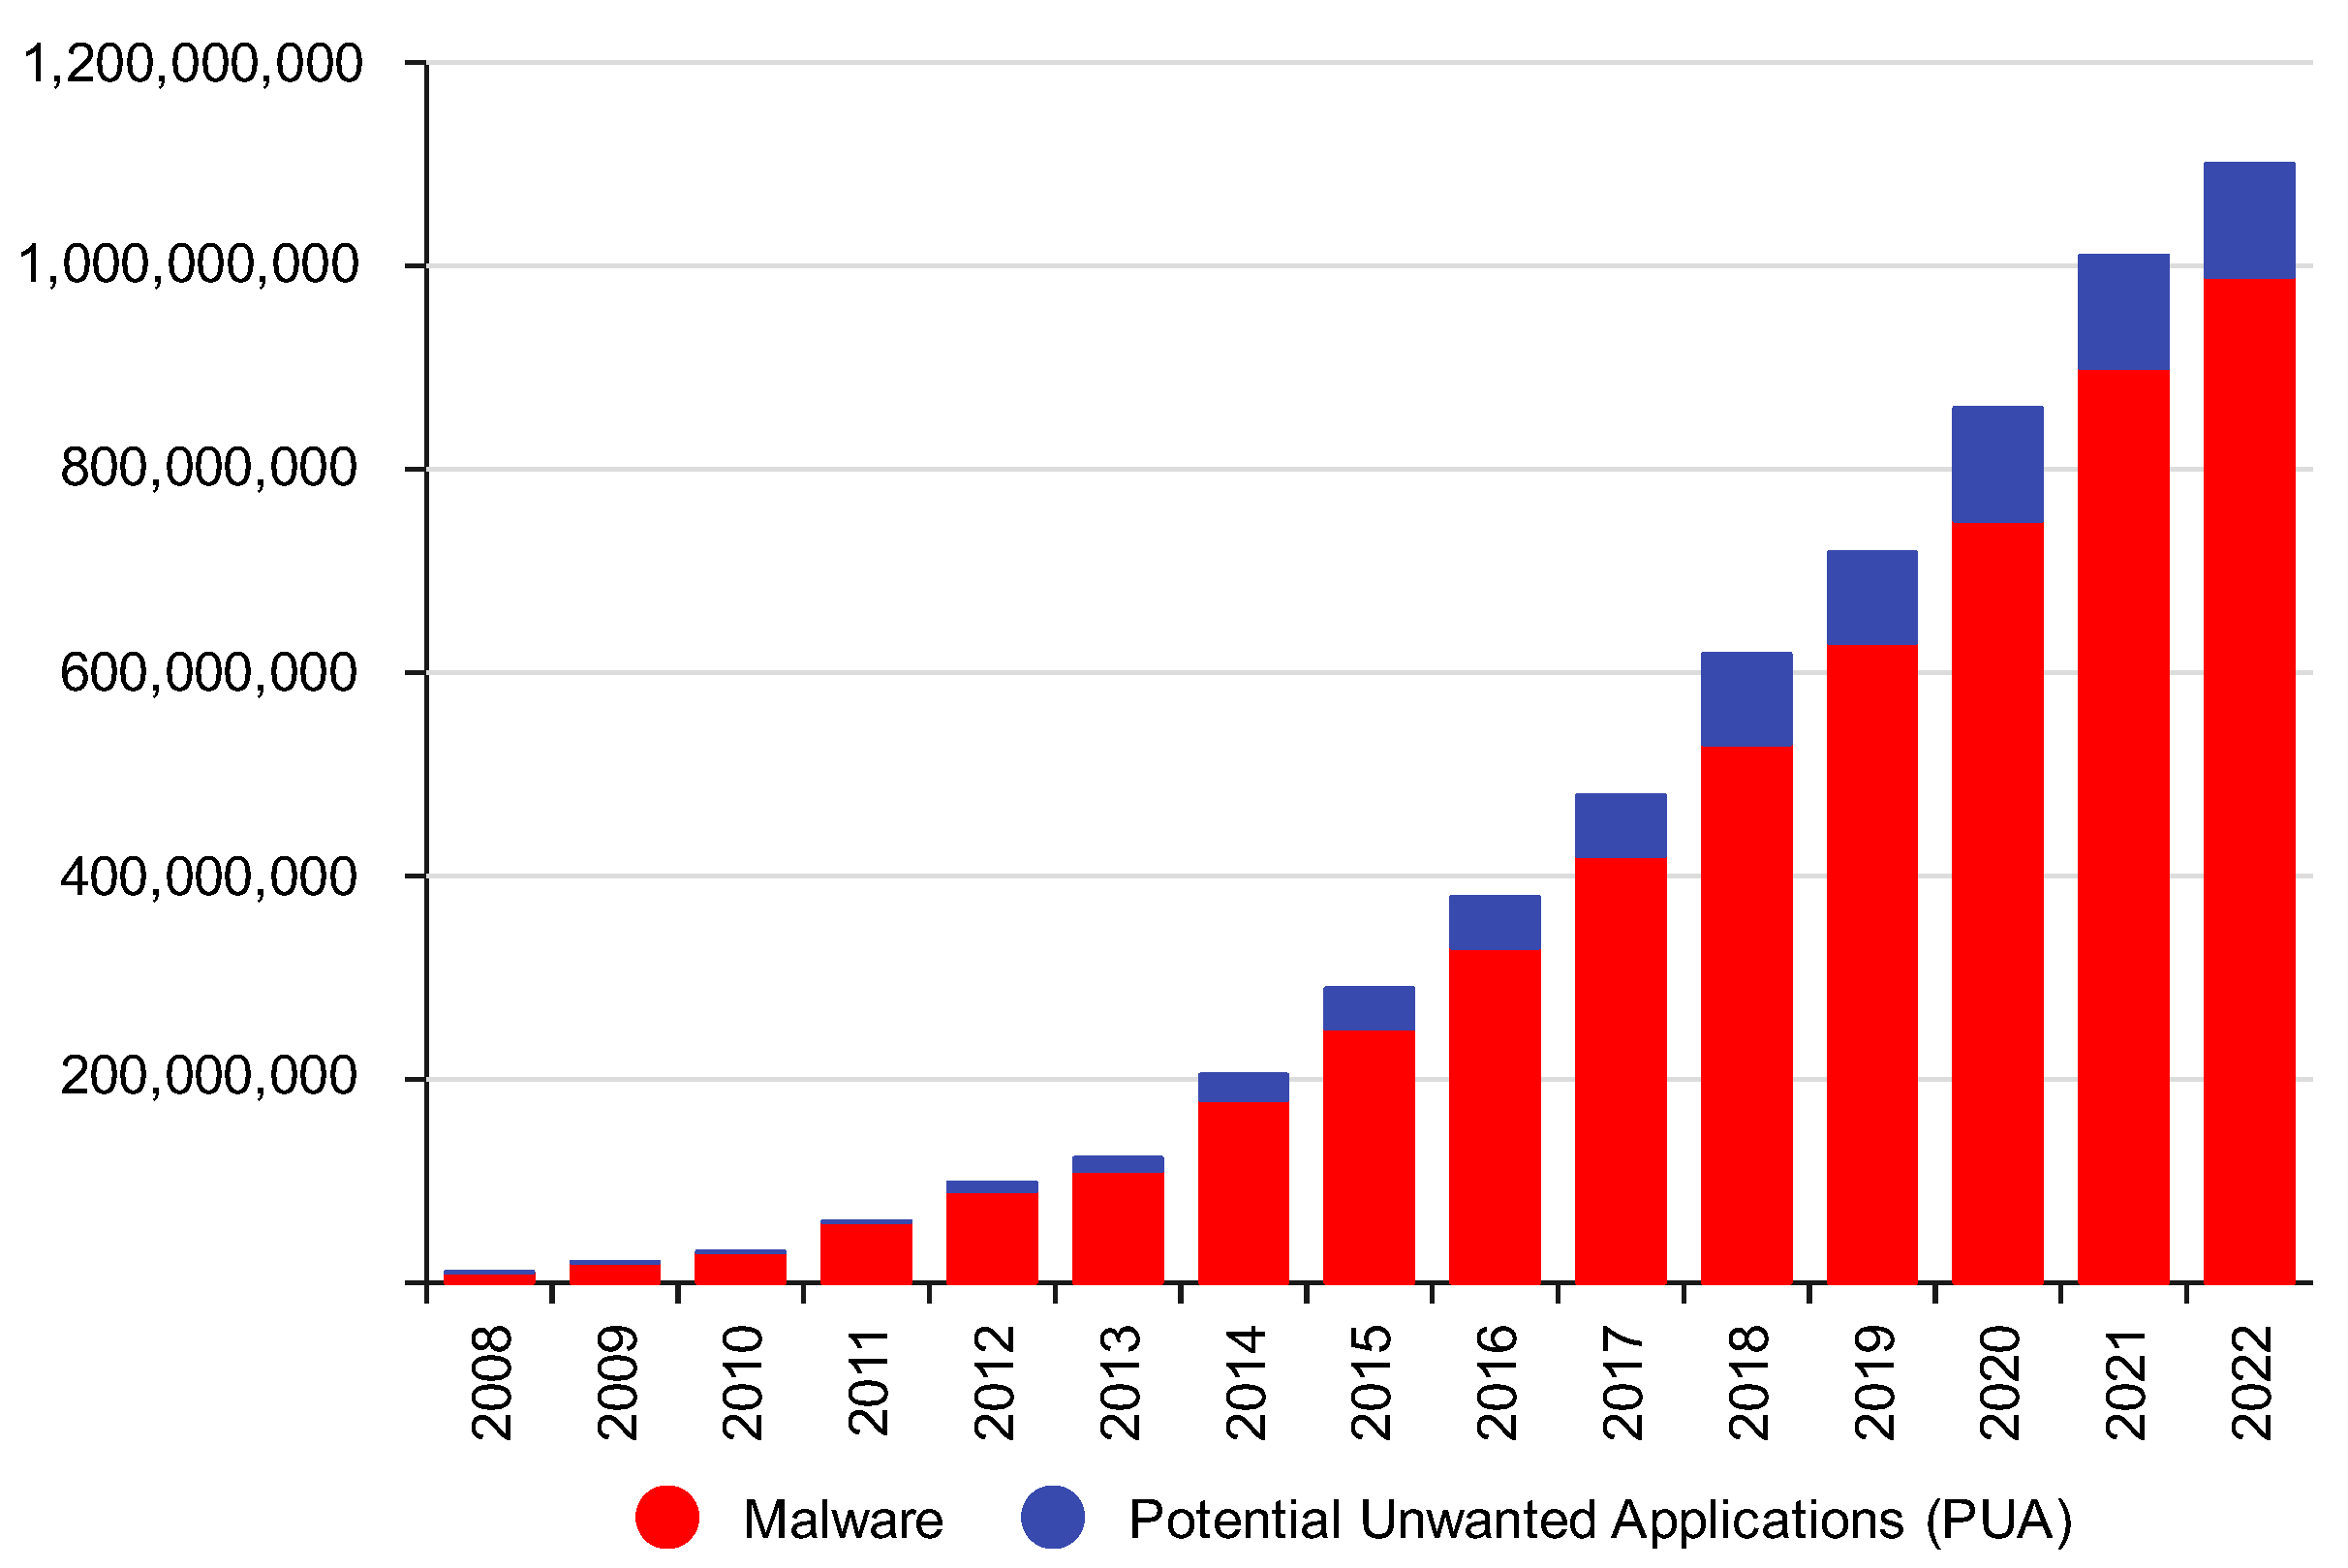
Mobile malware has evolved significantly since the first known threats. Early viruses were simplistic, often spreading via SMS or email attachments. As smartphones became ubiquitous, so did more sophisticated forms of malware. Today, they exploit vulnerabilities in Android's open-source framework, leading to diverse threats such as ransomware, spyware, and banking trojans, as detailed in Recorded Future's research.
The Advent of AI in Malware
Artificial Intelligence (AI) has revolutionized many industries, and unfortunately, cybercrime is no exception. AI-driven malware represents a significant leap forward in the capabilities of cyber threats, enabling attackers to automate tasks that previously required manual intervention.
Key Characteristics of AI-Driven Malware:
- Automated decision-making: AI algorithms can make decisions without human input, allowing malware to adapt to different environments. This is exemplified by SecurityWeek's report on Russian hackers using AI for malware evasion.
- Dynamic learning capabilities: These threats can learn from interactions with devices, becoming more effective over time.
- Advanced evasion techniques: By mimicking legitimate applications, AI malware can evade traditional detection methods, as noted in Zimperium's blog.

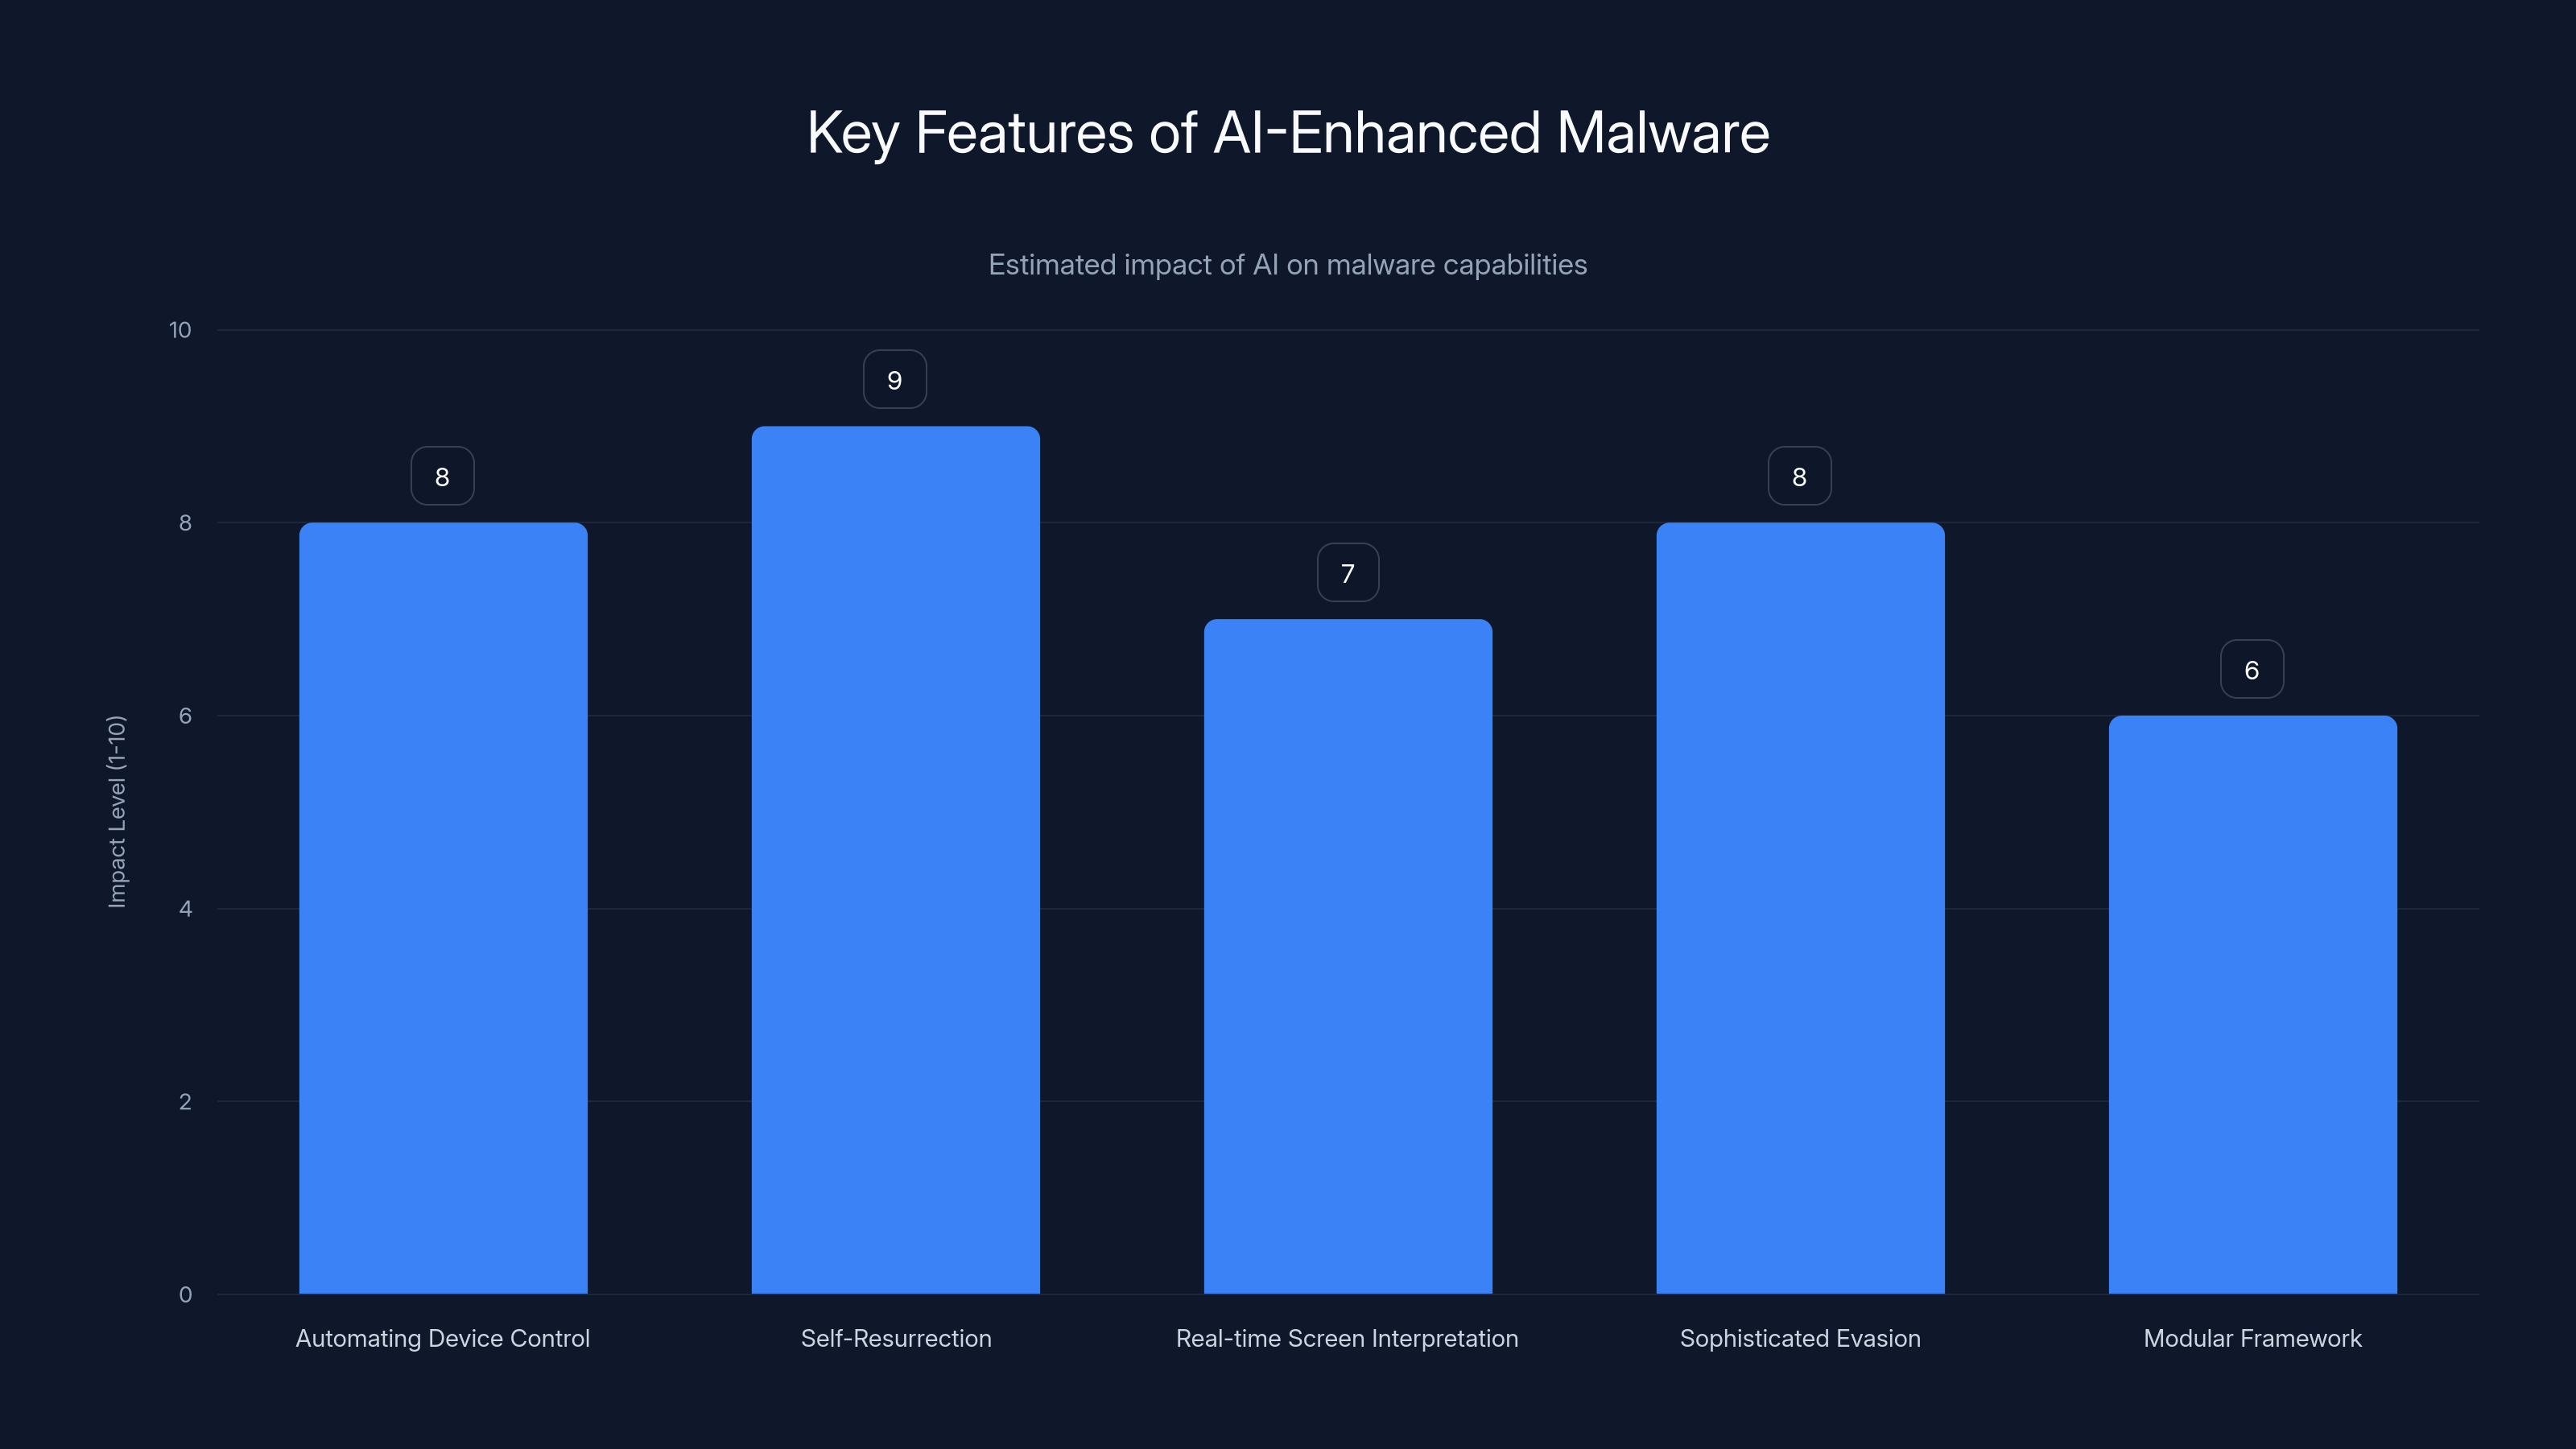
AI significantly enhances malware capabilities, with self-resurrection and device control showing the highest impact. Estimated data.
How AI Enhances Malware Capabilities
Automating Device Control
AI enables malware to interpret and manipulate device interfaces with unprecedented precision. Machine learning models can analyze screen layouts and automate interactions, allowing malware to perform complex tasks such as stealing credentials or transferring funds without user knowledge, as demonstrated in Zimperium's analysis.
Self-Resurrection Techniques
One of the most alarming features of AI-enhanced malware is its ability to resurrect itself. This is often achieved through:
- Remote triggers: Malware can be reactivated by signals from command-and-control servers.
- Hidden backups: Copies of the malware may be stored in obscure locations, ready to reinstall if necessary.
- Polymorphic coding: This allows the malware to change its code structure, making it harder to detect upon reappearance, as described by Morphisec.
Case Study: The Red Hat Trojan
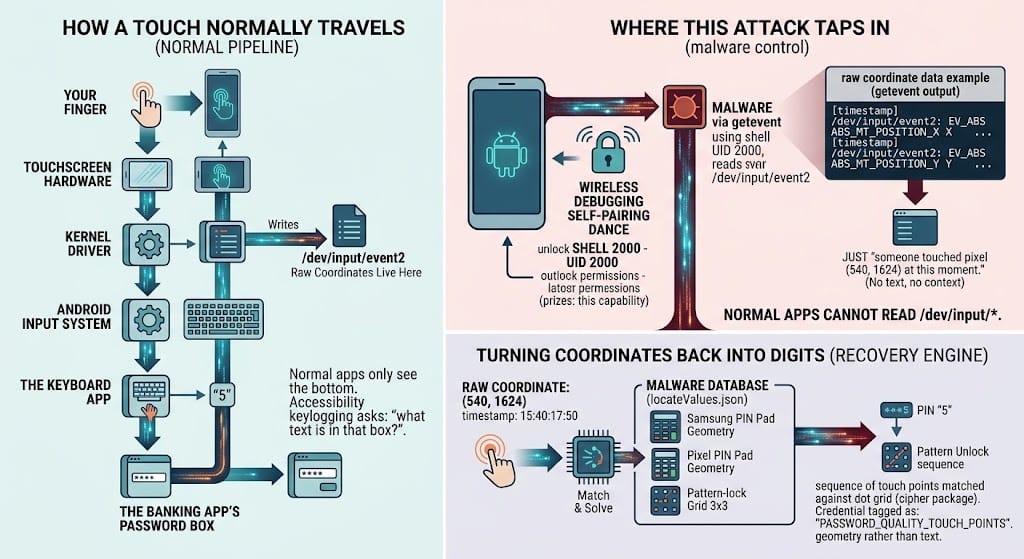
Discovered by Zimperium z Labs, the Red Hat trojan is a prime example of AI-driven malware. Originating from China, this banking trojan uses AI to interpret screen layouts in real-time, enabling it to navigate banking applications and steal credentials with alarming efficiency.
Features of Red Hat Trojan:
- Real-time screen interpretation
- Sophisticated evasion techniques
- Modular framework for adaptability
Practical Implementation Guides
Securing Android Devices Against AI Malware
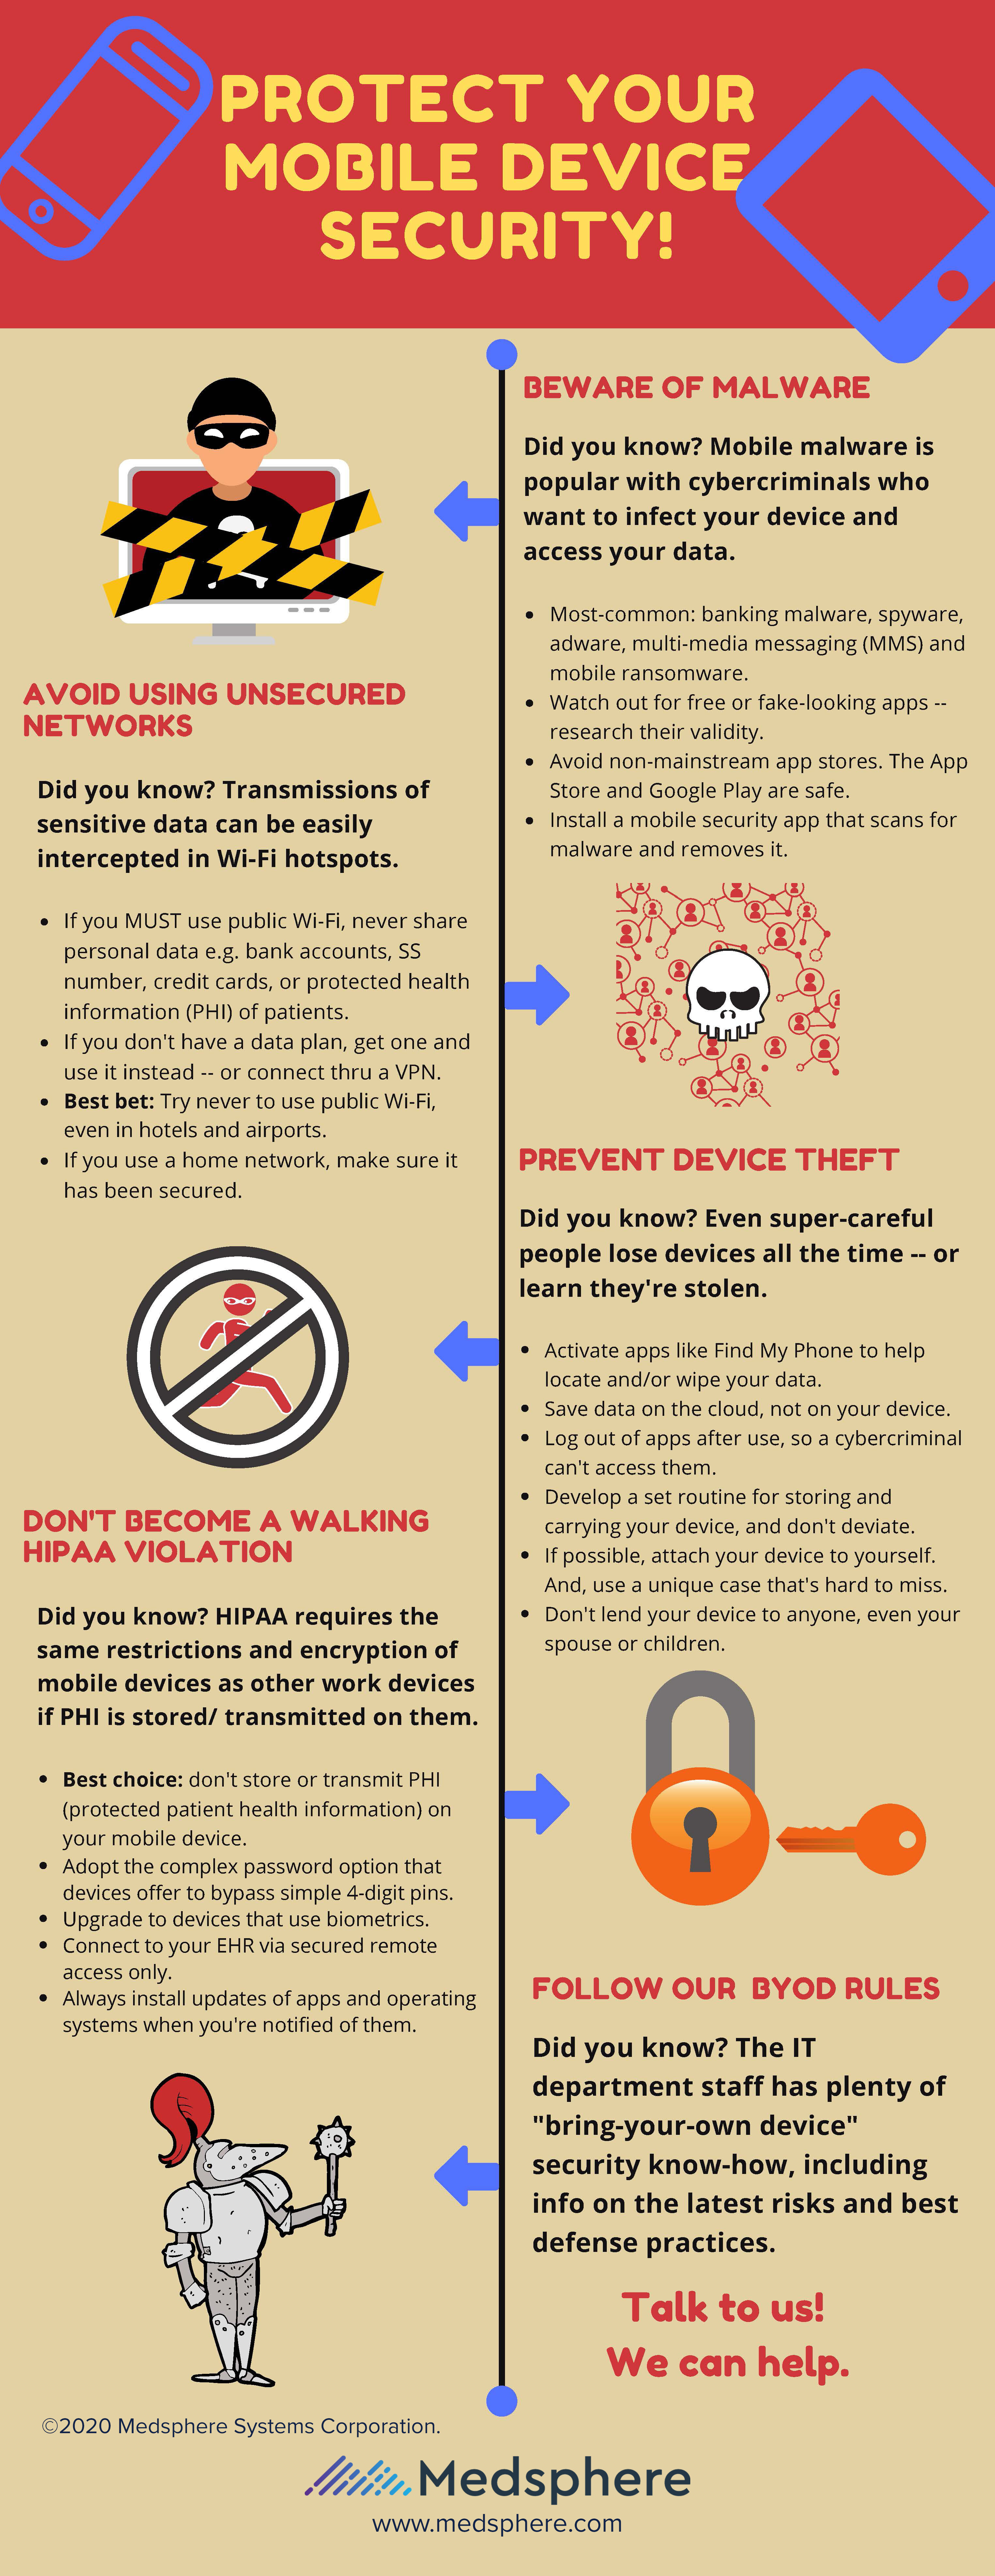
To protect against these advanced threats, it's crucial to implement robust security measures:
- Regular Software Updates: Ensure your device's operating system and applications are always up-to-date to patch known vulnerabilities, as emphasized by Cybersecurity Insiders.
- Use Reputable Security Software: Deploying a trusted security suite can provide an additional layer of protection.
- App Permissions Management: Regularly review and limit app permissions to prevent unauthorized access.
- Network Security Practices: Use VPNs and secure Wi-Fi networks to minimize exposure to command-and-control servers, as recommended by Cybersecurity Dive.
Common Pitfalls and Solutions
- Over-reliance on Default Security: Many users assume built-in security is sufficient. Enhance protection with third-party security apps.
- Ignoring App Permissions: Granting excessive permissions can open doors for malware. Regular audits can prevent unauthorized access.
- Delayed Updates: Postponing software updates leaves devices vulnerable to known exploits. Enable automatic updates to stay protected.
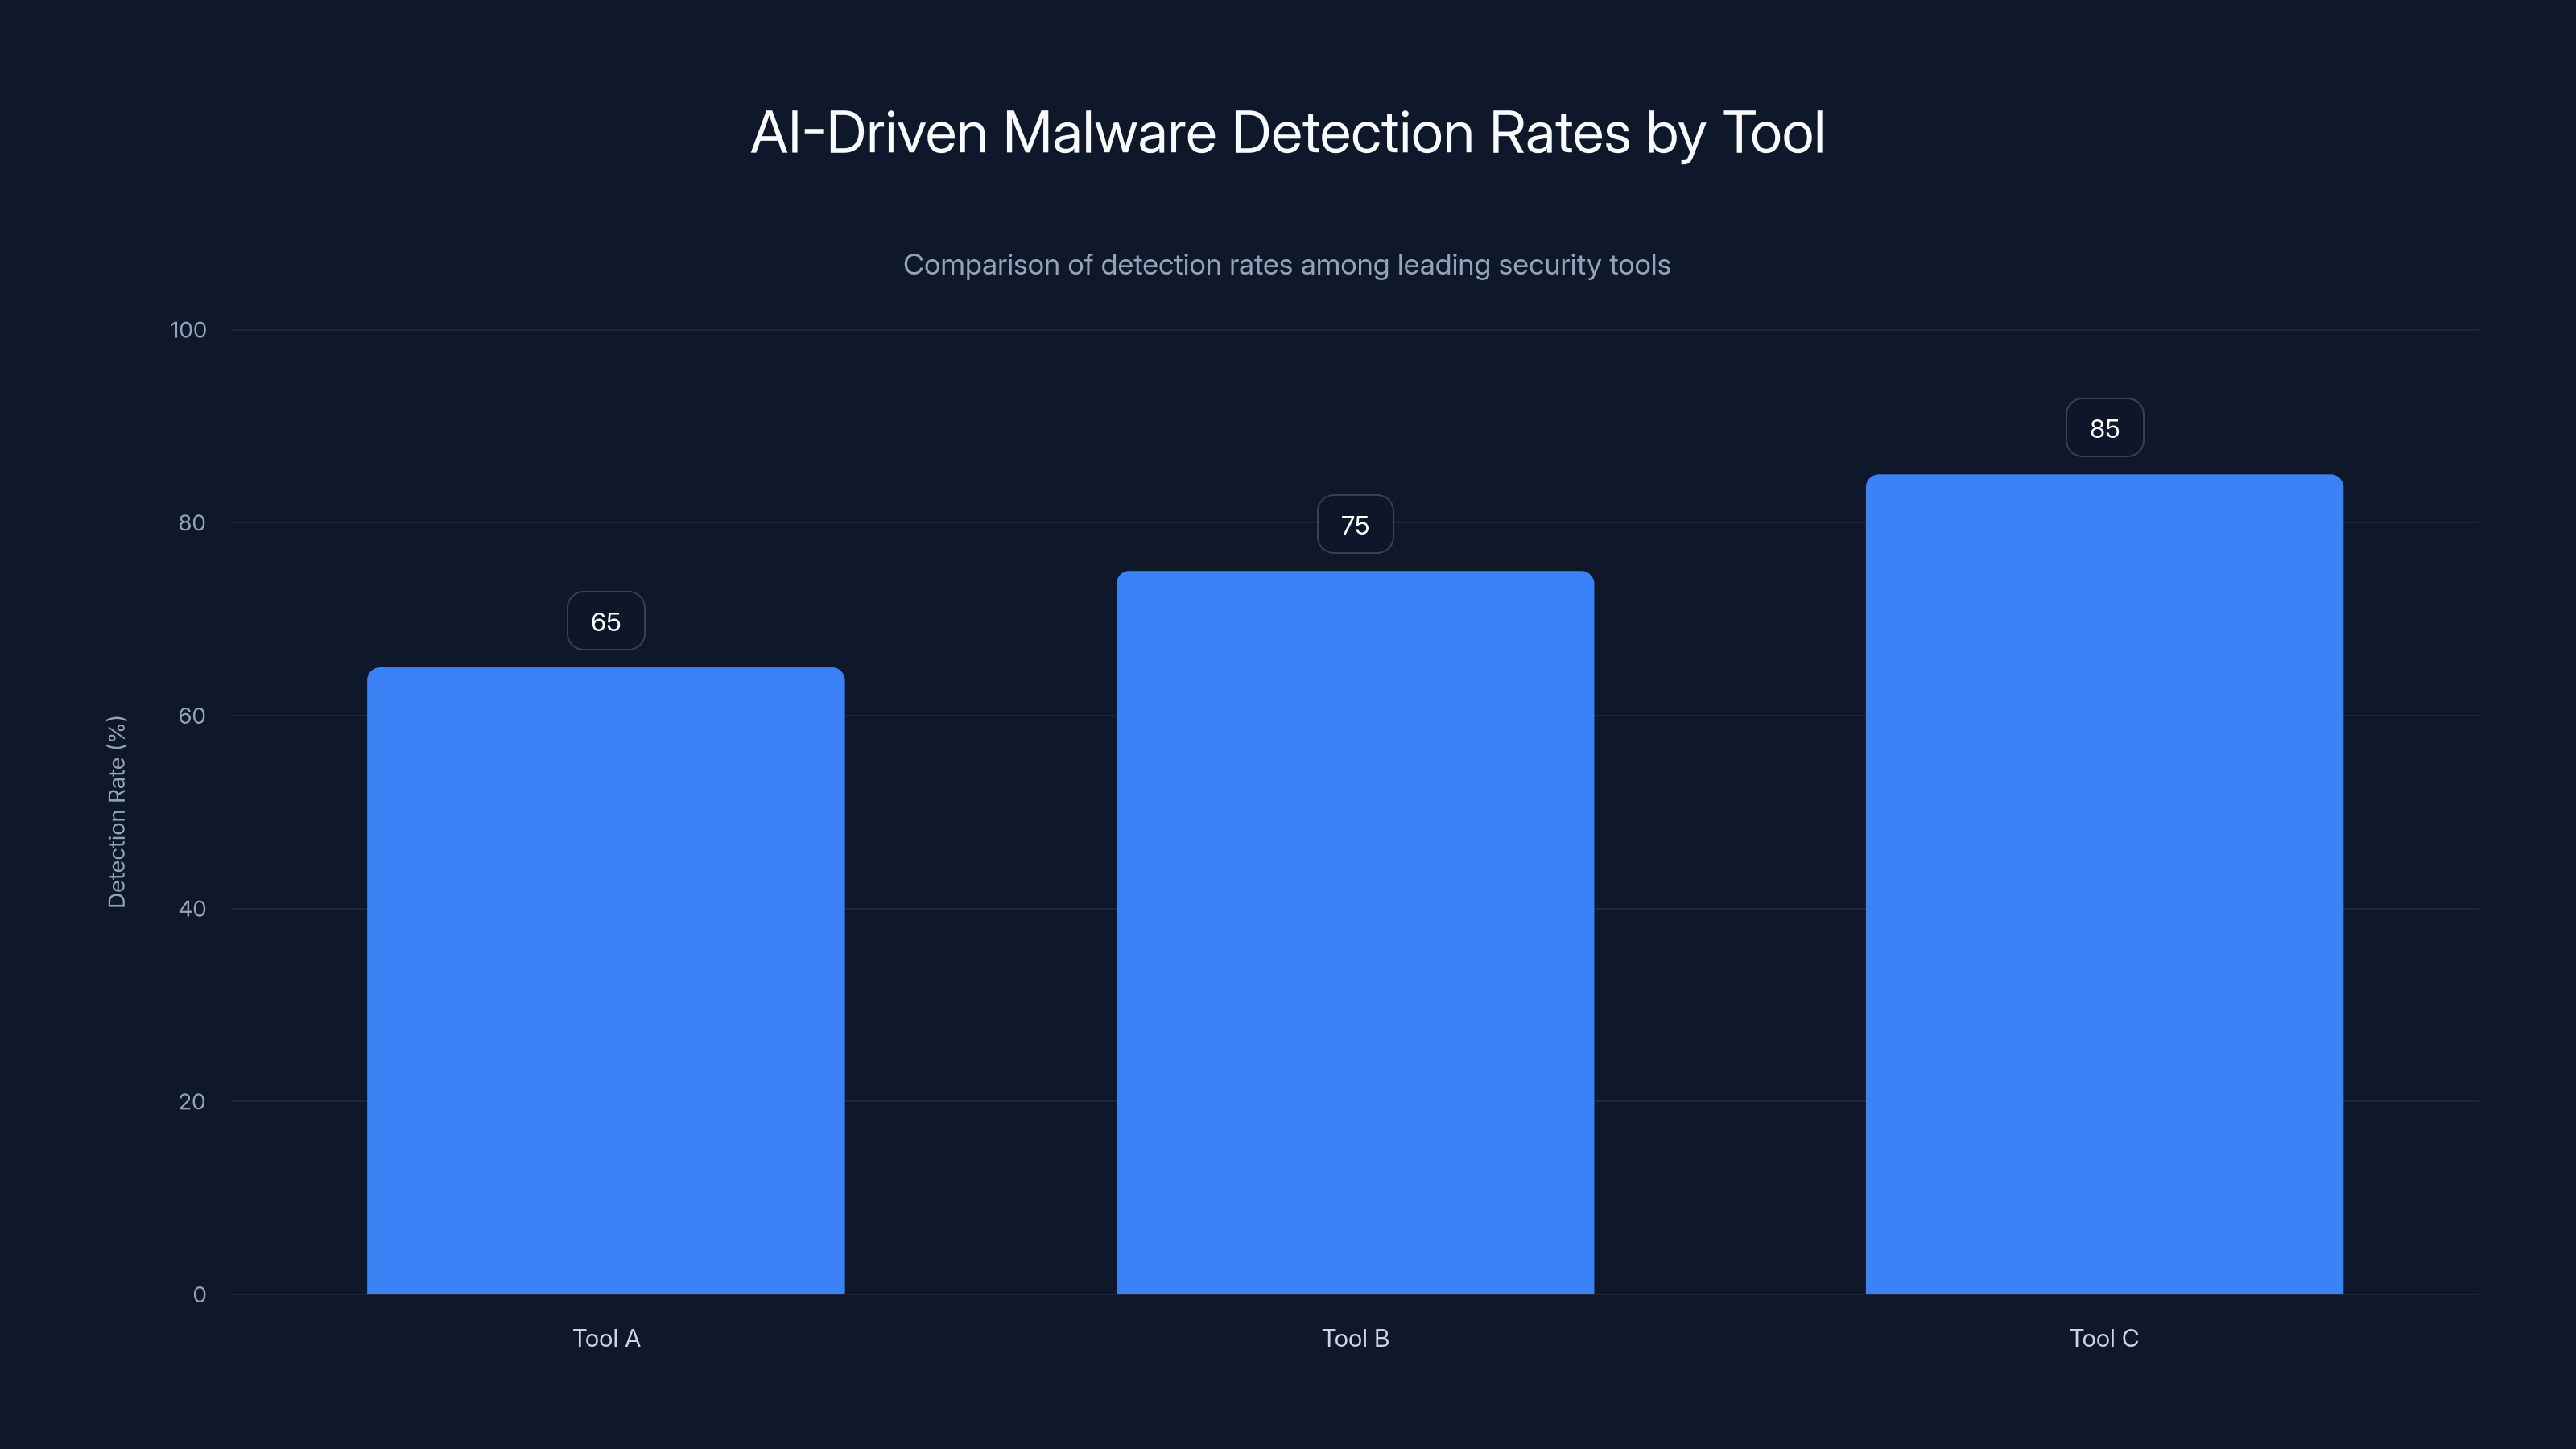
Tool C leads with an 85% detection rate, showcasing its effectiveness in identifying AI-driven malware compared to Tool A and Tool B.
Future Trends in AI-Driven Malware
Increasing Sophistication
As AI models become more advanced, so too will the malware that uses them. Future threats may incorporate deep learning techniques, allowing for even more adaptive and stealthy attacks, as suggested by Cybersecurity Insiders.
Enhanced Detection and Mitigation
Cybersecurity firms are developing AI-based tools to combat these threats. These tools can recognize suspicious patterns and behaviors indicative of AI-driven malware, as noted in MSSP Alert's report.
[CHART: bar | AI-driven malware detection rates by tool | [65, 75, 85] | Detection rates of AI-driven malware by leading security tools]
The Role of Blockchain in Security
Blockchain technology offers potential in creating immutable logs and enhancing transparency in security processes, which could be vital in tracking and mitigating AI-driven threats, as discussed in Cybersecurity Dive's survey.
Recommendations for Security Professionals
- Invest in AI-Based Security Solutions: Leverage AI to detect and counteract AI-driven threats, as recommended by Cybersecurity Insiders.
- Continuous Monitoring and Analysis: Implement systems that monitor device behavior and flag anomalies.
- Educate Users: Raise awareness about the importance of security practices and the risks of AI malware.
FAQ
What is AI-driven malware?
AI-driven malware uses artificial intelligence to automate tasks and adapt to different environments, making it more effective and difficult to detect than traditional malware, as explained by SecurityWeek.
How does AI enhance malware capabilities?
AI allows malware to automate complex tasks, such as navigating apps and stealing data, and to resurrect itself after deletion through advanced techniques like polymorphic coding, as noted by Morphisec.
What are the risks of AI-driven malware?
These threats can lead to significant data breaches, financial losses, and privacy invasions due to their ability to automate and adapt, as highlighted by MSSP Alert.
How can I protect my Android device from AI malware?
Implement regular software updates, use reputable security software, manage app permissions, and secure your network connections, as advised by Cybersecurity Dive.
Are there any tools to detect AI-driven malware?
Yes, security firms are developing AI-based tools that recognize suspicious patterns and behaviors indicative of AI-driven malware, as reported by MSSP Alert.
What role does blockchain play in security against AI-driven malware?
Blockchain can create immutable logs and enhance transparency, aiding in tracking and mitigating AI-driven threats, as discussed in Cybersecurity Dive's survey.
Key Takeaways
- AI-driven malware poses a significant threat by automating complex tasks and evading detection.
- Security measures must evolve to counteract the adaptive nature of these threats.
- Regular software updates and reputable security software are crucial defenses.
- Future security solutions will likely incorporate AI and blockchain technologies.
- User education and vigilance remain key components of an effective defense strategy.
Conclusion
The rise of AI-enhanced malware marks a pivotal moment in the ongoing battle between cybercriminals and security experts. With the ability to automate complex tasks and even bring itself back from the dead, AI-driven malware represents a formidable challenge. By understanding these threats and implementing robust security measures, users and professionals alike can safeguard their digital environments against this new breed of cyber threats.
Related Articles
- Catch Hackers in the Act: Deploying Decoys, Lures, and Honeypots [2025]
- Understanding Calendar-Based Phishing: The Unseen Threat in Your Schedule [2025]
- Waymo's Ambitious Expansion to Singapore: A New Era in Autonomous Transportation [2025]
- An Undercover Google Analyst Infiltrated a Notorious Supply Chain Hacking Gang | WIRED
- Behind the Scenes with Apple's New VP of Hardware Engineering: The iPhone Duo's Durability Secrets [2025]
- Unlocking the Apple Watch Series 12: Features, Deals, and Tips for 2025


