
Understanding Calendar-Based Phishing: The Unseen Threat in Your Schedule [2025]
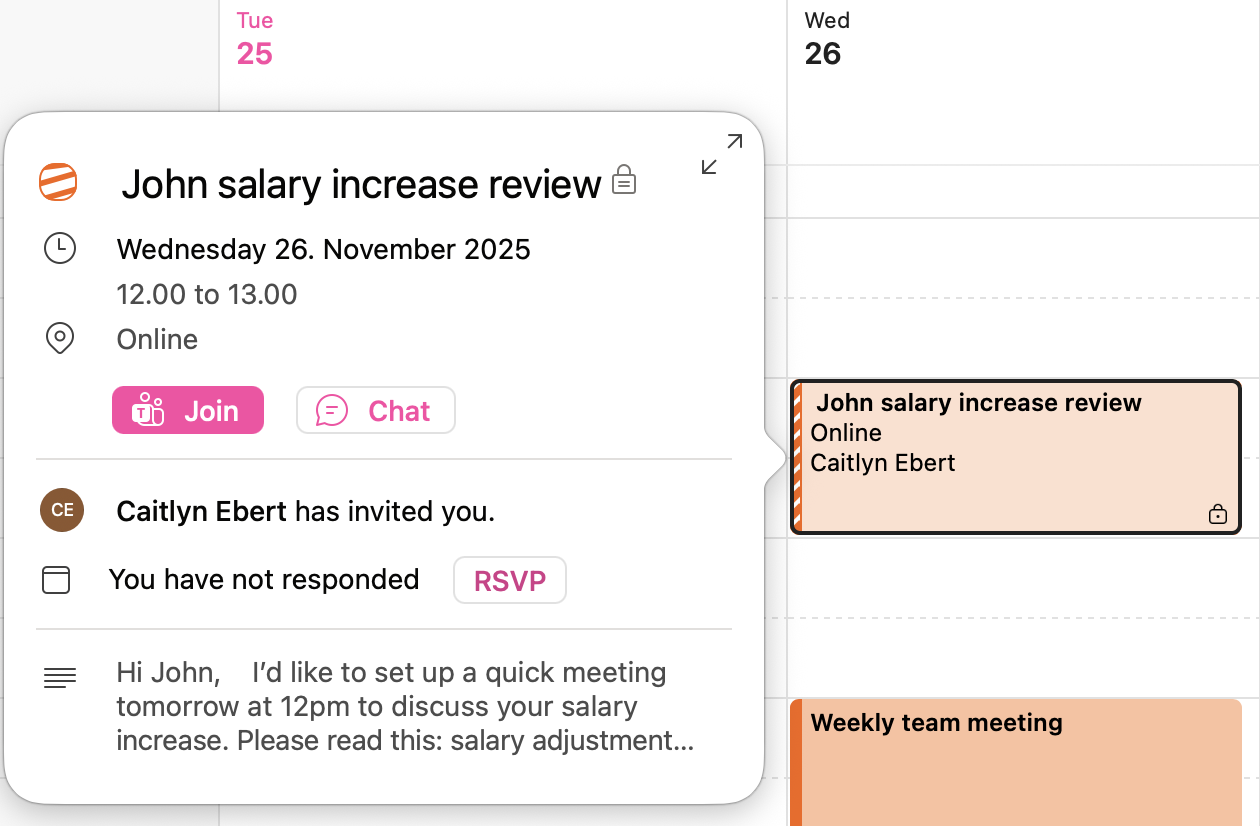
Last month, a tech-savvy friend of mine noticed a peculiar invitation on his calendar: a meeting titled "Urgent: Secure Your Account". Surprisingly, it came from an unverified sender. Digging deeper, we discovered it's part of a surging trend in what's now known as calendar-based phishing. This threat has skyrocketed by an alarming 33,000% since May, catching many off guard.
TL; DR
- Calendar-Based Phishing: A new wave of cyberattacks exploiting calendar invites.
- 33,000% Increase: Rapid rise in incidents since May 2025.
- Bypasses Email Filters: Works even if phishing emails are flagged as spam.
- User Awareness: Crucial for prevention and protection.
- Future Trends: Anticipate more sophisticated attacks involving AI.
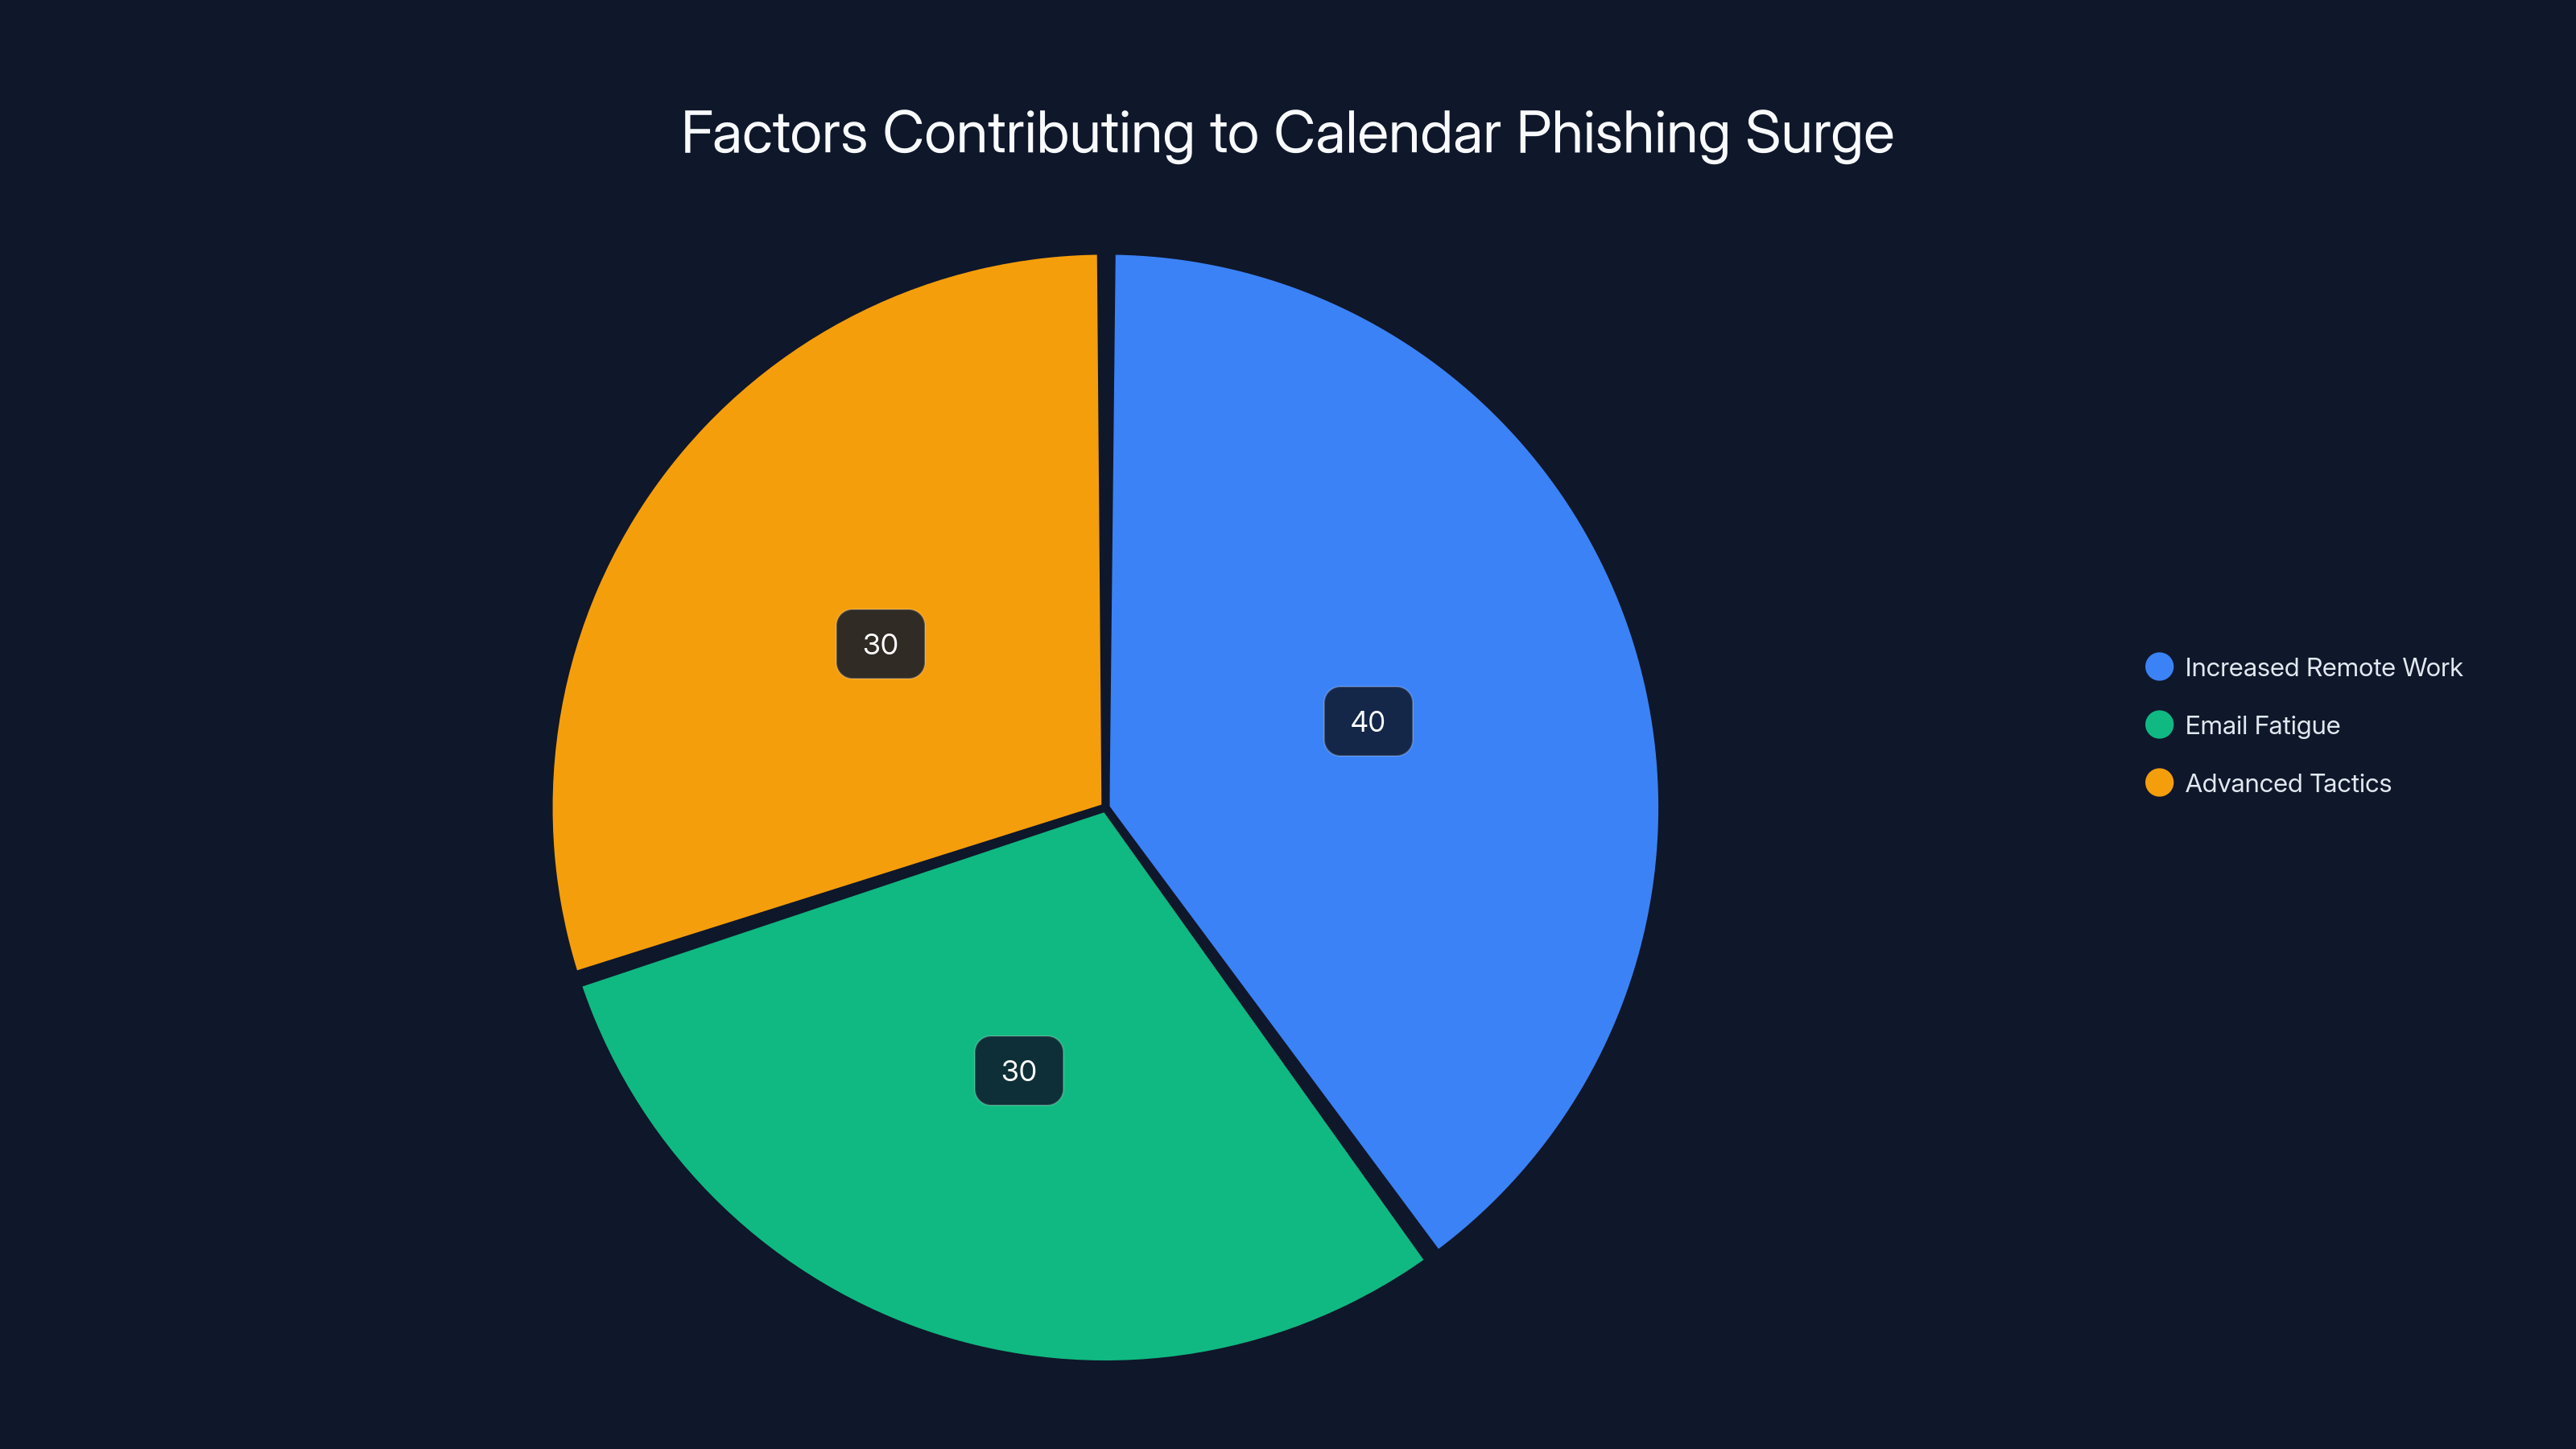
Estimated data shows that increased remote work, email fatigue, and advanced tactics equally contribute to the surge in calendar phishing incidents.
What is Calendar-Based Phishing?
Calendar-based phishing, also known as ICS (Internet Calendar Standard) phishing, involves attackers sending malicious calendar invites to potential victims. These invites often contain links or prompts urging users to click or provide sensitive information.
How It Works
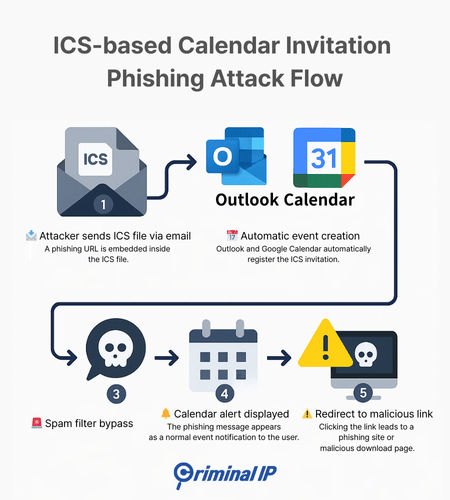
When you receive an email with a calendar invite, many services automatically add the event to your calendar. This is where the attackers capitalize. The event might look legitimate, but clicking on it or following the links can lead to phishing sites or malware downloads.
Key Characteristics:
- Legitimate Appearance: Mimics genuine calendar events.
- Automatic Addition: Appears in your calendar without consent.
- Action-Oriented: Invites often urge immediate action.
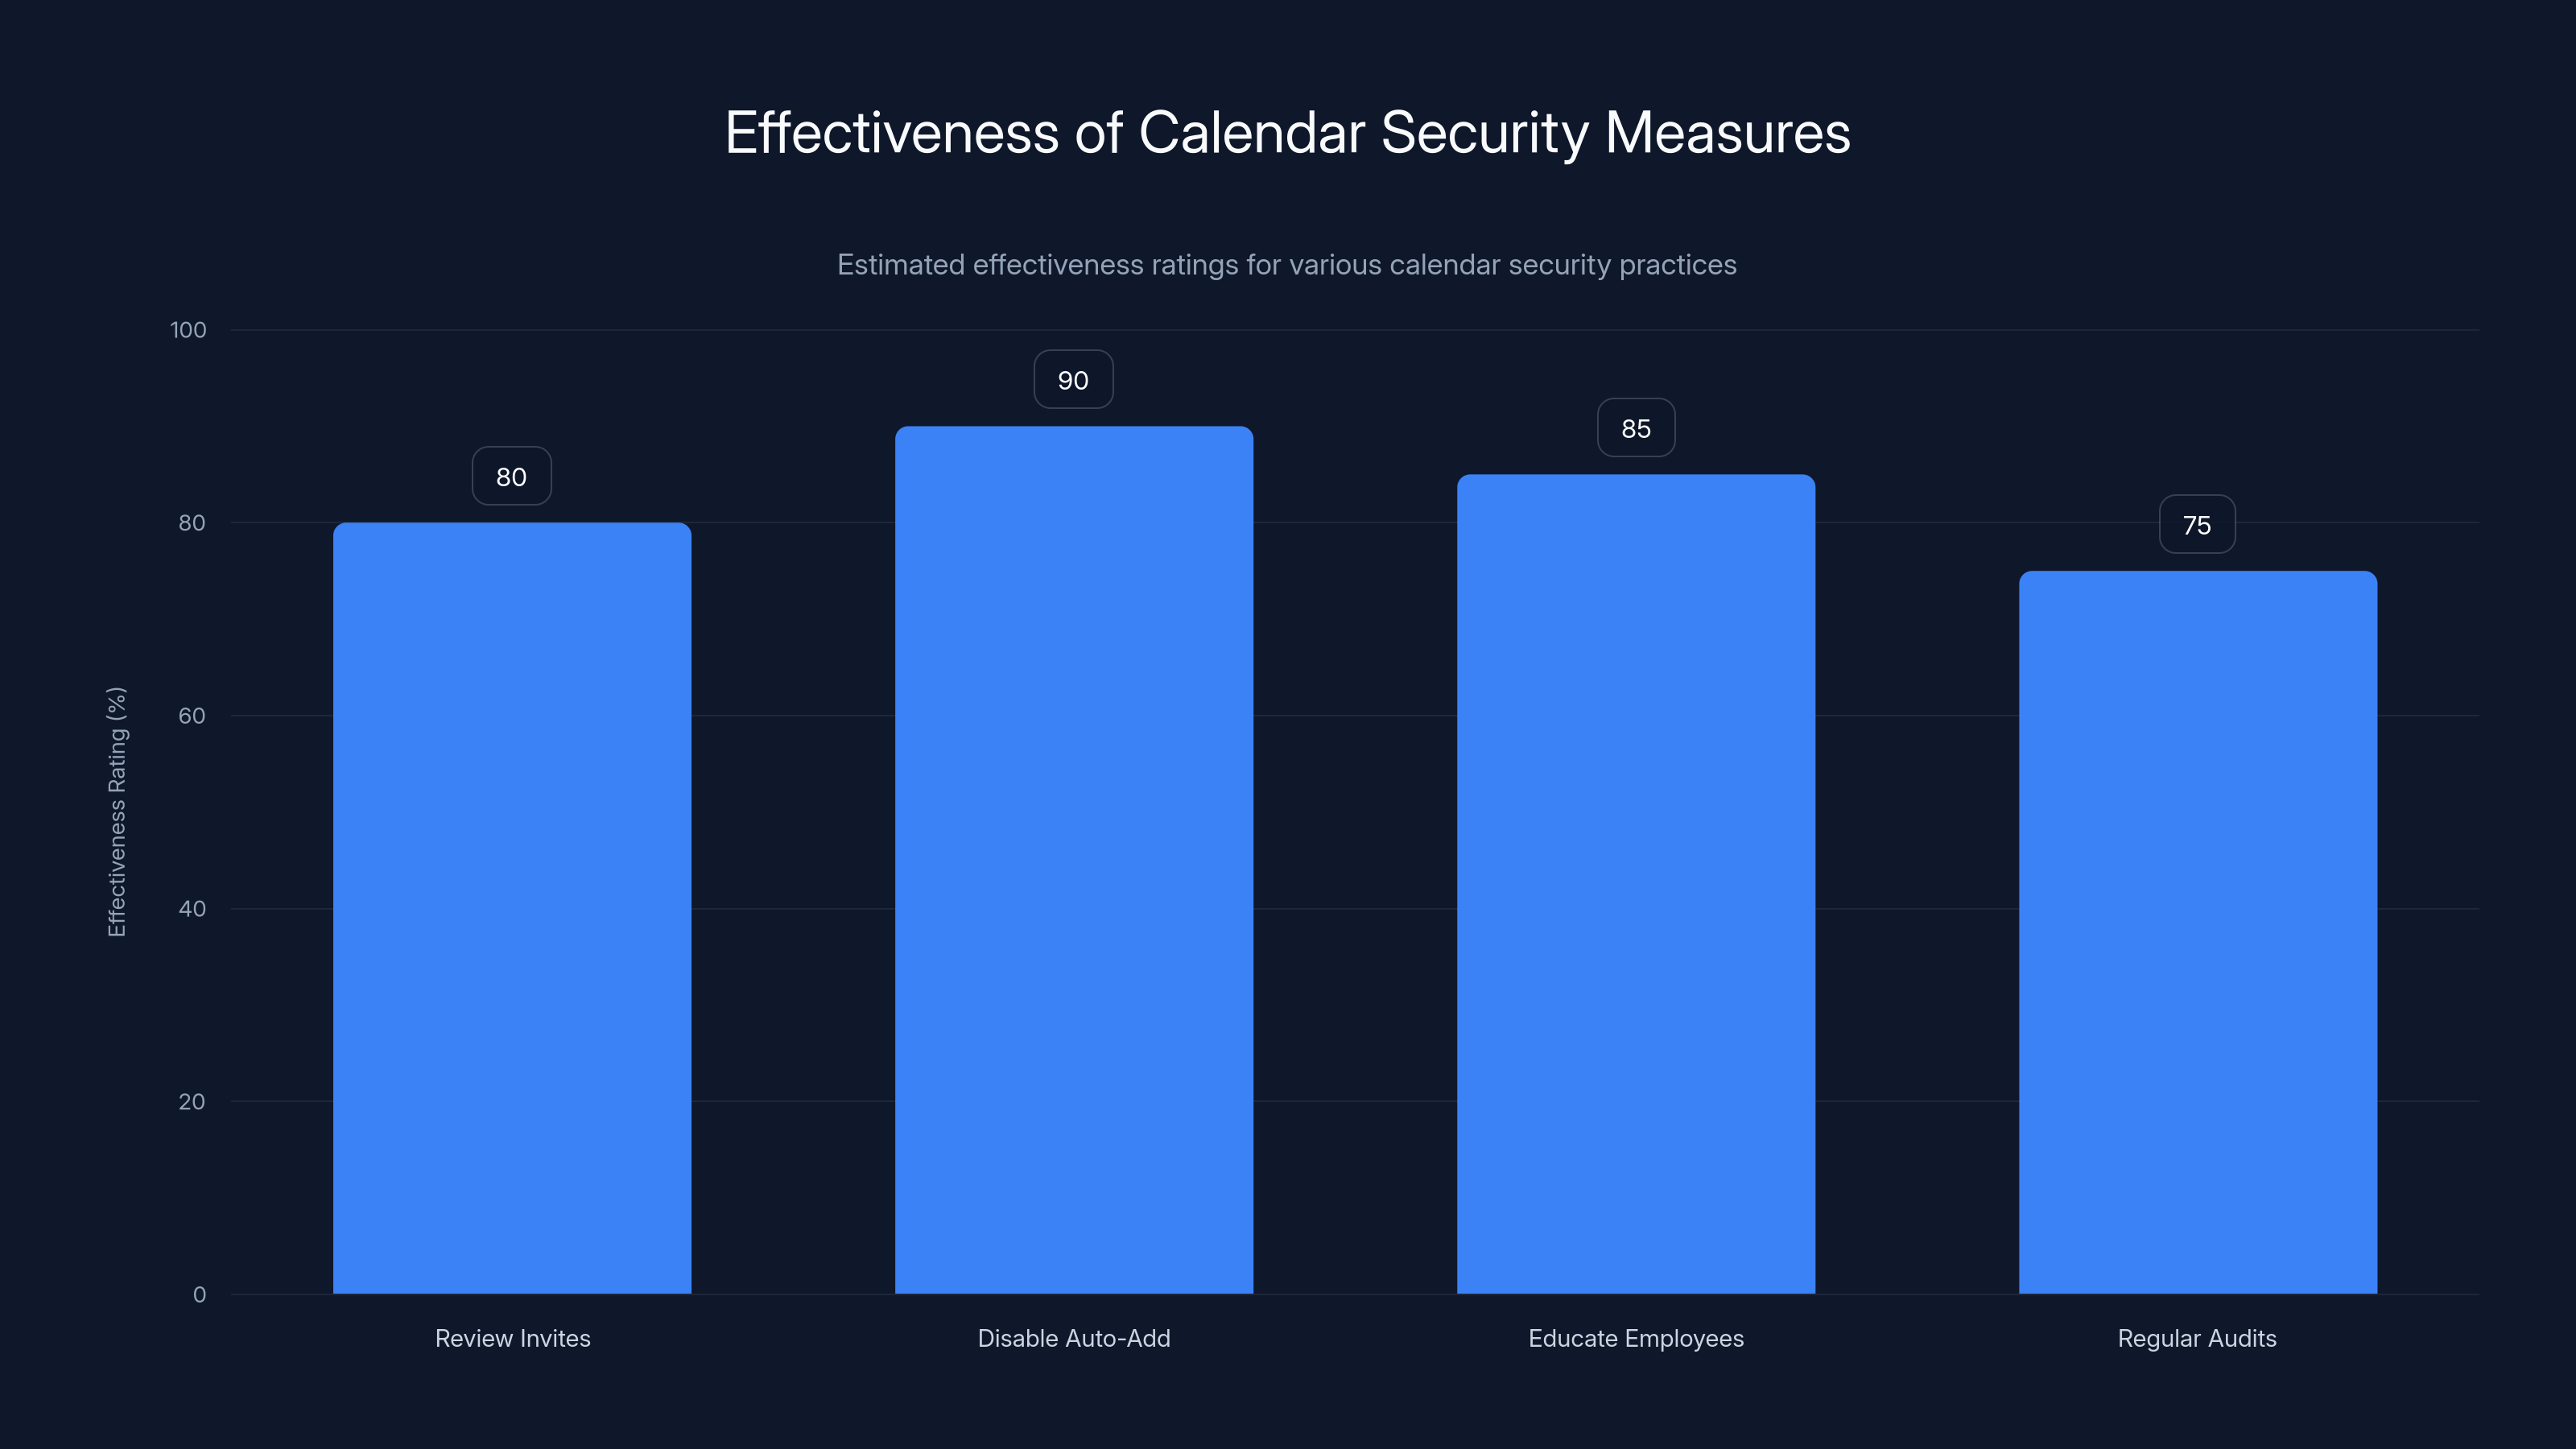
Disabling auto-add is estimated to be the most effective measure at 90%, followed by educating employees at 85%. Estimated data.
Why the Surge?
The dramatic increase in calendar phishing incidents can be attributed to several factors:
- Increased Remote Work: More reliance on digital communication tools.
- Email Fatigue: Users overwhelmed by emails, less scrutiny of calendar invites.
- Advanced Tactics: Attackers using more sophisticated methods to bypass traditional filters.
Real-World Implications
Imagine scheduling a meeting with a new client. You receive a calendar invite, click the link, and unknowingly download malware that compromises your system. This scenario isn't rare anymore.
Case Study: A Small Business's Close Call
A small marketing firm in New York faced a similar issue. An employee clicked on a calendar invite for a "Client Presentation", leading to malware that encrypted their files. Luckily, they had backups, but the downtime cost them two days of productivity.
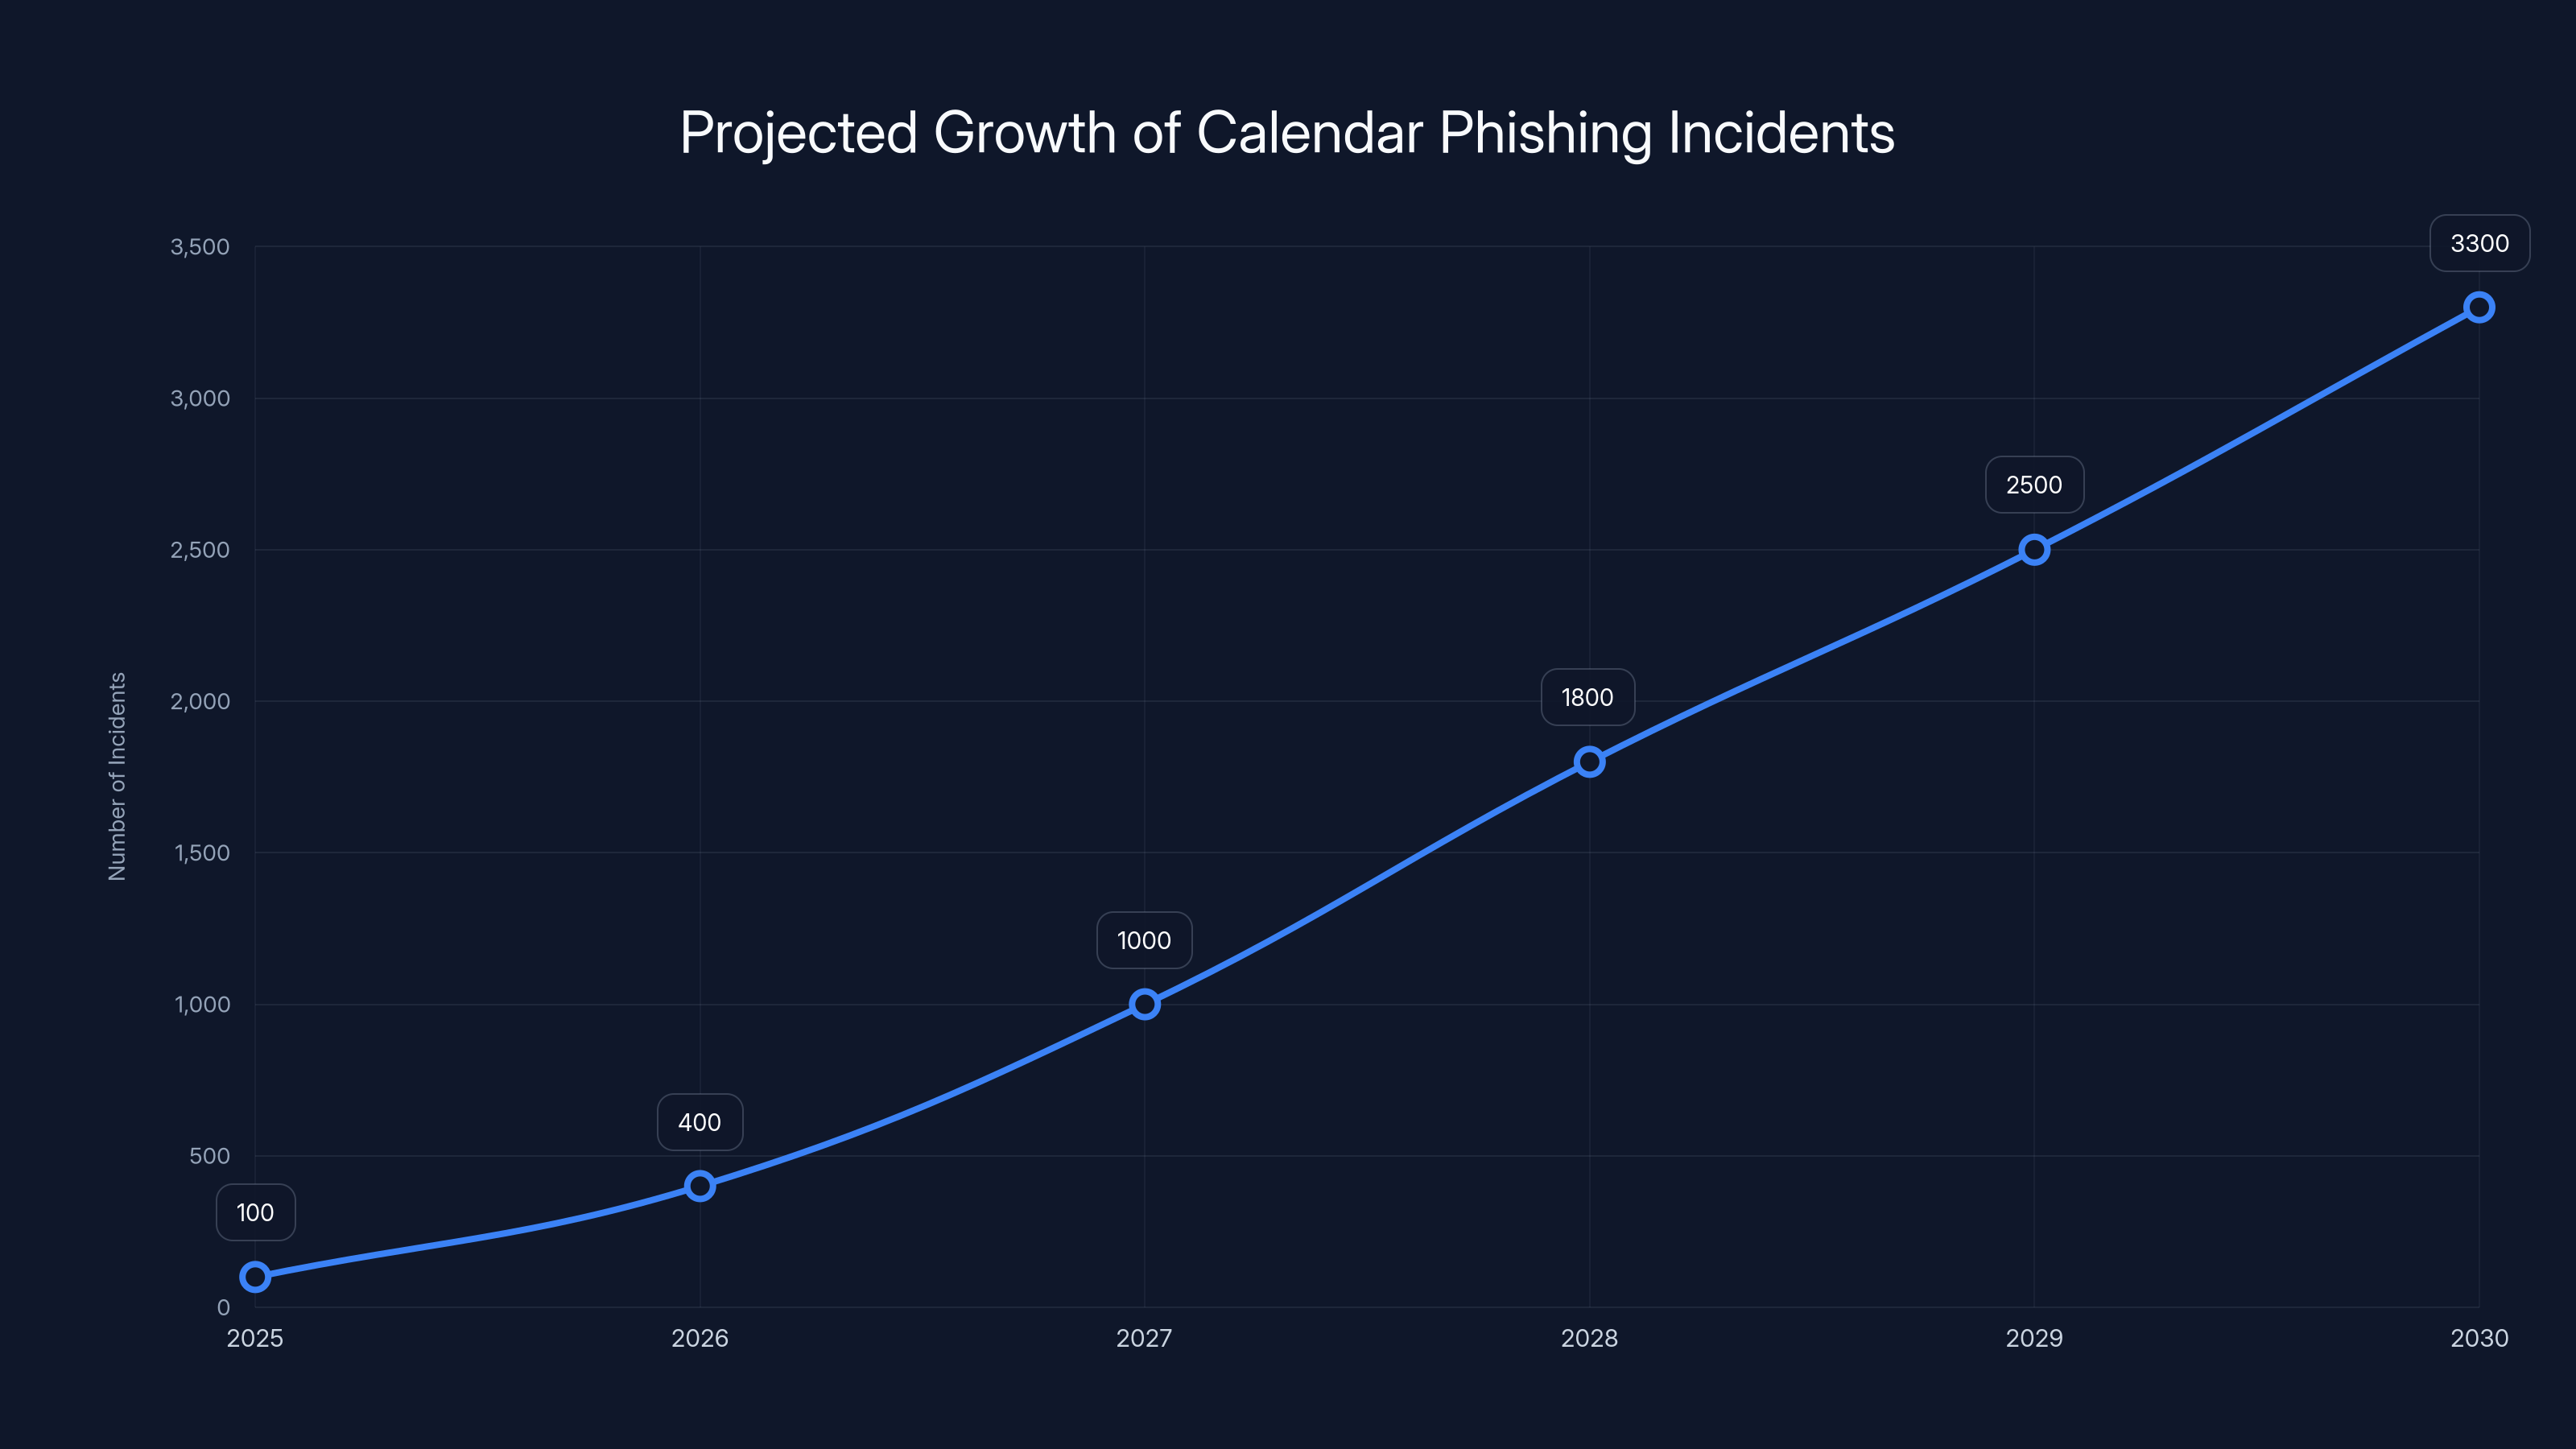
Calendar phishing incidents are projected to grow significantly, reaching 3,300 incidents by 2030. Estimated data suggests a sharp increase due to evolving tactics.
Technical Breakdown
Understanding the technical underpinnings of calendar phishing can empower you to defend against it.
The ICS Format
The ICS format is a universal calendar file format used to share meeting requests. Attackers exploit its widespread use and the fact that many email clients automatically process ICS files.
- .ics Files: Plain text files that contain event details.
- Email Integration: Most email clients support .ics files, adding events directly to calendars.
Bypassing Security
Many email clients and calendar apps prioritize usability, often leading to security oversights. Attackers exploit automatic event additions and leverage links embedded within event descriptions.
Practical Prevention Measures
To safeguard your calendar and data, consider these best practices:
- Review All Invites: Scrutinize unexpected or suspicious calendar invites.
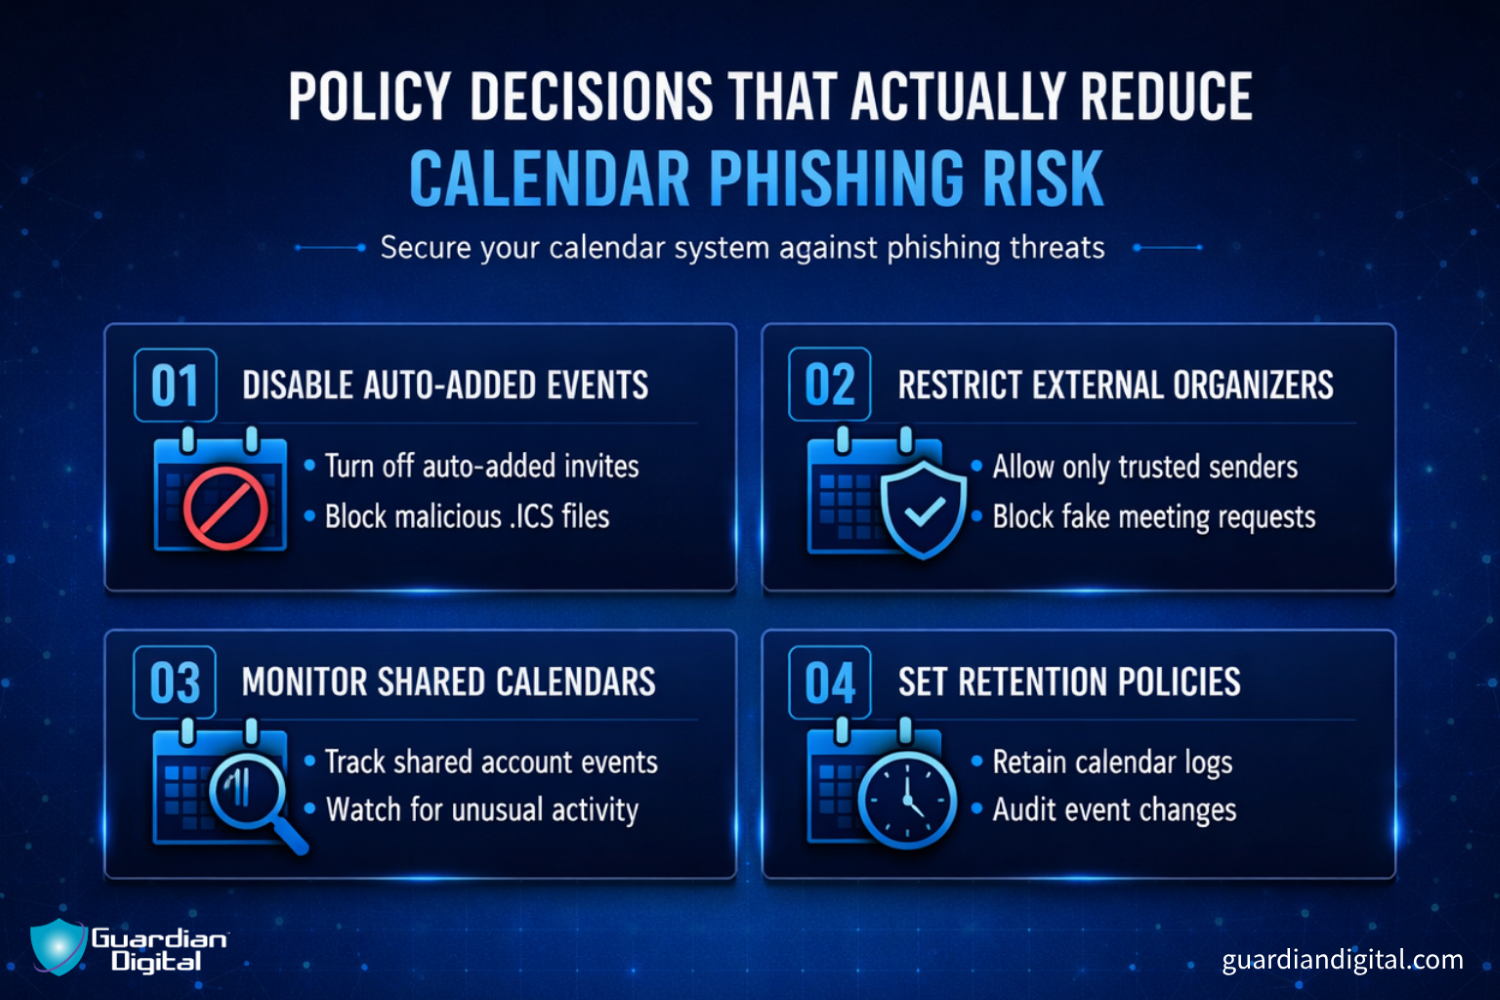
- Disable Auto-Add: Turn off automatic calendar event additions from emails.
- Educate Employees: Conduct training sessions on identifying phishing attempts.
Step-By-Step: Disabling Auto-Add
- Open your calendar app settings.
- Navigate to 'Event Settings' or similar.
- Find the option for automatic event addition.
- Disable this feature to prevent unwanted calendar entries.
Common Pitfalls and Solutions
While many are aware of email phishing, calendar-based tactics often fly under the radar, leading to common mistakes.
Mistake 1: Assuming All Calendar Events are Safe
Solution: Treat unexpected invites with the same suspicion as unfamiliar emails. Verify the sender before interacting.
Mistake 2: Ignoring Security Updates
Solution: Ensure your calendar and email apps are up to date with the latest security patches.
Mistake 3: Lack of Awareness Training
Solution: Implement regular cybersecurity training to keep all team members informed about the latest threats.

Looking Ahead: Future Trends
As cybercriminals become more sophisticated, calendar-based phishing tactics are expected to evolve.
AI-Driven Phishing
Expect attackers to leverage AI to craft even more convincing calendar invites, using natural language processing to mimic human communication styles.
Integrated Security Solutions
Future calendar apps may incorporate advanced AI-driven security features to detect and neutralize phishing attempts before they reach users.
Recommendations for Businesses
Businesses must stay proactive in their security measures to combat calendar phishing.
- Implement Multi-Factor Authentication: Adds an extra layer of security.
- Regular Security Audits: Identify potential vulnerabilities in your systems.
- Use AI Tools: Employ AI-based security tools to monitor for suspicious activity.
Conclusion
Calendar-based phishing is a growing threat that exploits our reliance on digital tools. By understanding how these attacks work and implementing robust security measures, individuals and businesses can protect themselves. Stay vigilant, stay informed, and keep your calendar secure.
FAQ
What is calendar-based phishing?
Calendar-based phishing involves sending malicious calendar invites to trick users into clicking links or providing sensitive information.
How does calendar-based phishing work?
Attackers send invites that automatically appear on calendars, tricking users into interacting with deceptive events.
What are the signs of calendar phishing?
Look for unexpected invites, events urging immediate action, and links from unknown senders.
How can I protect myself from calendar phishing?
Disable automatic event additions, verify invite senders, and educate yourself and your team about phishing tactics.
Are calendar apps doing enough to prevent phishing?
Many are improving, but users should still take personal precautions to stay safe.
What should businesses do to prevent calendar phishing?
Regularly update security measures, educate employees, and use AI tools to detect threats.
Will calendar phishing continue to rise?
As long as attackers find success, calendar phishing will likely evolve and persist.
Can AI help in preventing calendar phishing?
Yes, AI tools can analyze patterns and detect anomalies that might indicate phishing attempts.
This comprehensive guide delves into the intricacies of calendar-based phishing, its rise, and the measures you can take to protect yourself from this evolving threat. Keep your digital calendar safe by staying informed and proactive.
Key Takeaways
- Calendar-based phishing exploits calendar invites for attacks.
- Incidents have surged by 33,000% since May 2025.
- Automatic event addition increases vulnerability.
- User awareness and education are crucial for prevention.
- AI-driven tools can help detect and prevent phishing.
Related Articles
- Building Enterprise Resilience Against Growing AI Risks [2025]
- The AI Slowdown Debate Crashed Salesforce’s Party | WIRED
- Your Robotaxi Might Be a Narc: Navigating the Future of Autonomous Vehicle Surveillance [2025]
- Cisco Zero-Day Exploit on Identity Services Engine: Secure Your Network Now [2025]
- AI and Digital Sovereignty: Navigating the Data Control Landscape for UK Businesses [2025]
- Agentic AI: The Future of Security and Compliance [2025]


