
Catch Hackers in the Act: Deploying Decoys, Lures, and Honeypots [2025]
Cybersecurity is a cat-and-mouse game, always evolving as hackers innovate new methods to breach networks. The stakes are high: data breaches can cost millions and damage reputations. Amid this turbulent landscape, the Cybersecurity and Infrastructure Security Agency (CISA) has urged businesses to bolster their defenses with decoys, lures, and honeypots. These tools aren't just tech jargon—they're crucial components of a proactive security strategy.
TL; DR
- Decoys and honeypots: Effective tools for catching hackers by mimicking real systems.
- Lures: Trick attackers into revealing themselves and their methods.
- Integration with Zero Trust: Enhances security by detecting lateral movement.
- Implementation tips: Focus on realism and strategic placement.
- Future trends: AI-driven honeypots and adaptive security systems.

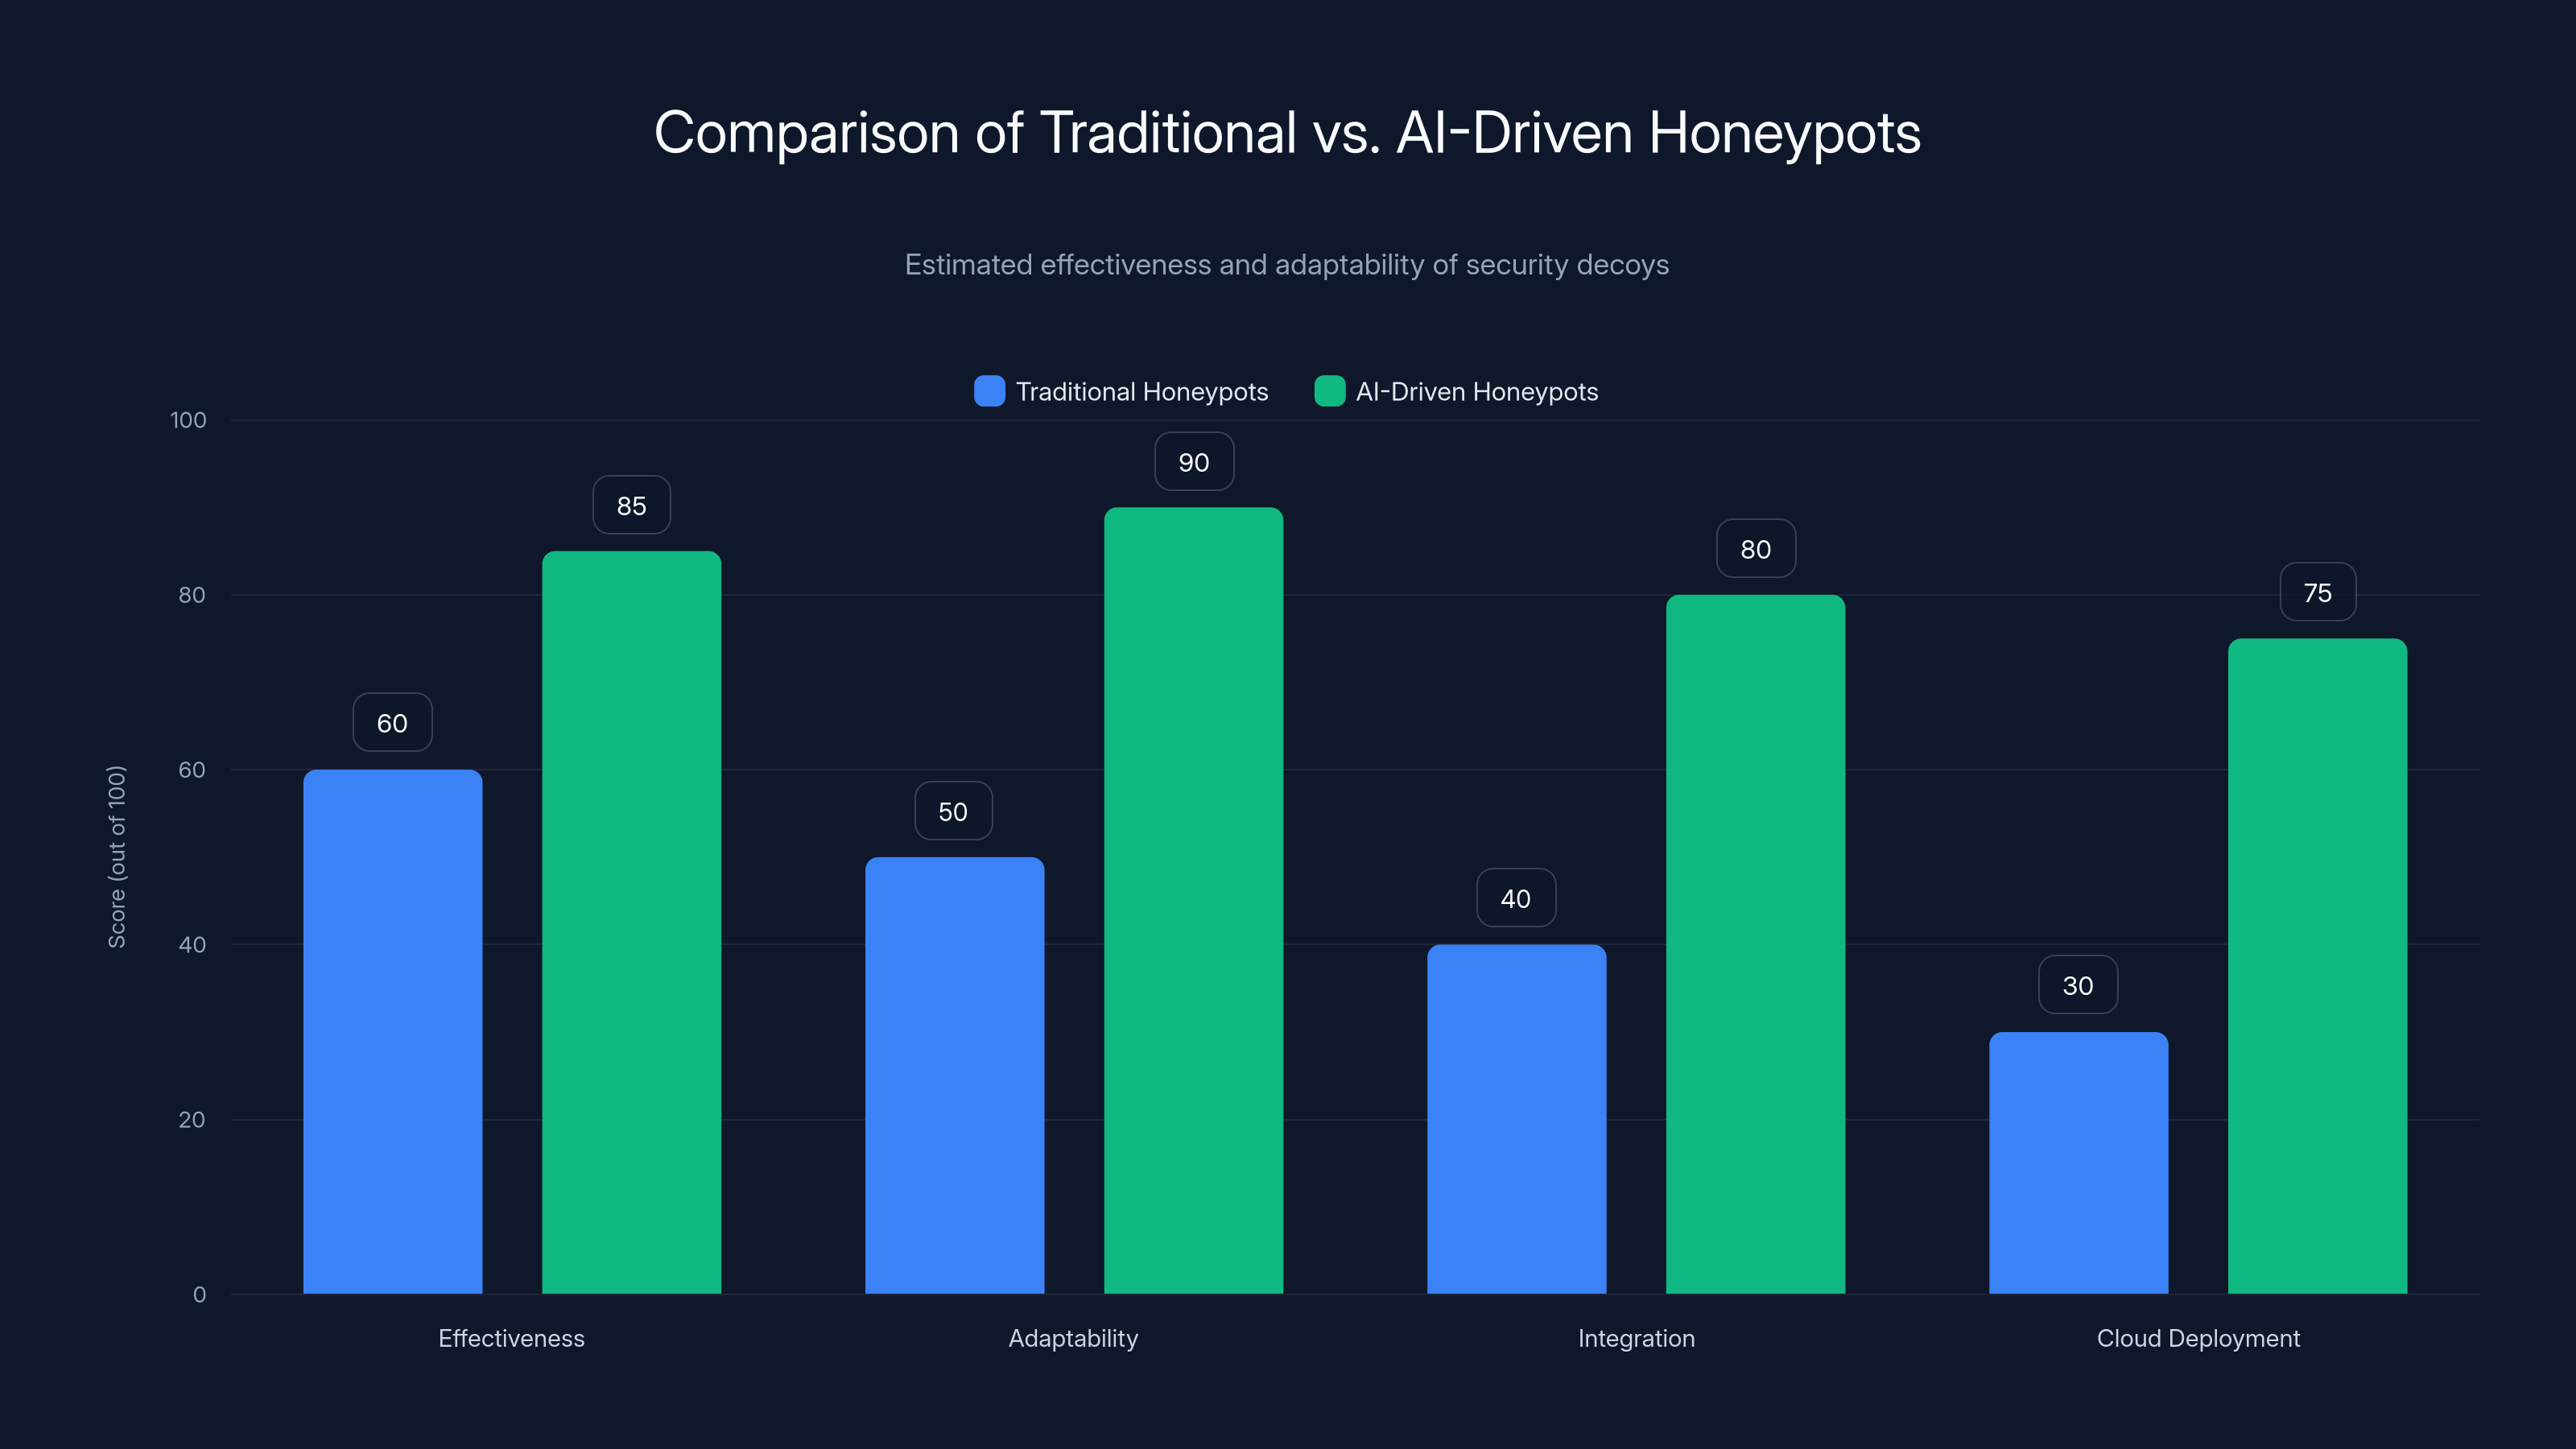
AI-driven honeypots are projected to outperform traditional honeypots in effectiveness, adaptability, integration, and cloud deployment. Estimated data.
Understanding Decoys, Lures, and Honeypots
What Are Decoys?
Decoys are fake systems or data designed to appear legitimate to an attacker. They act as traps, diverting cybercriminals away from real assets and allowing security teams to detect unauthorized access attempts. For example, a decoy might be a clone of a company's website with login portals that record unauthorized login attempts.
The Role of Lures
Lures are tactics used to entice hackers into interacting with decoys and honeypots. These could be fake credentials, seemingly valuable but bogus files, or misleading links that lead attackers into decoy environments. The goal is to bait attackers into revealing their presence and methods.
Honeypots and Their Purpose
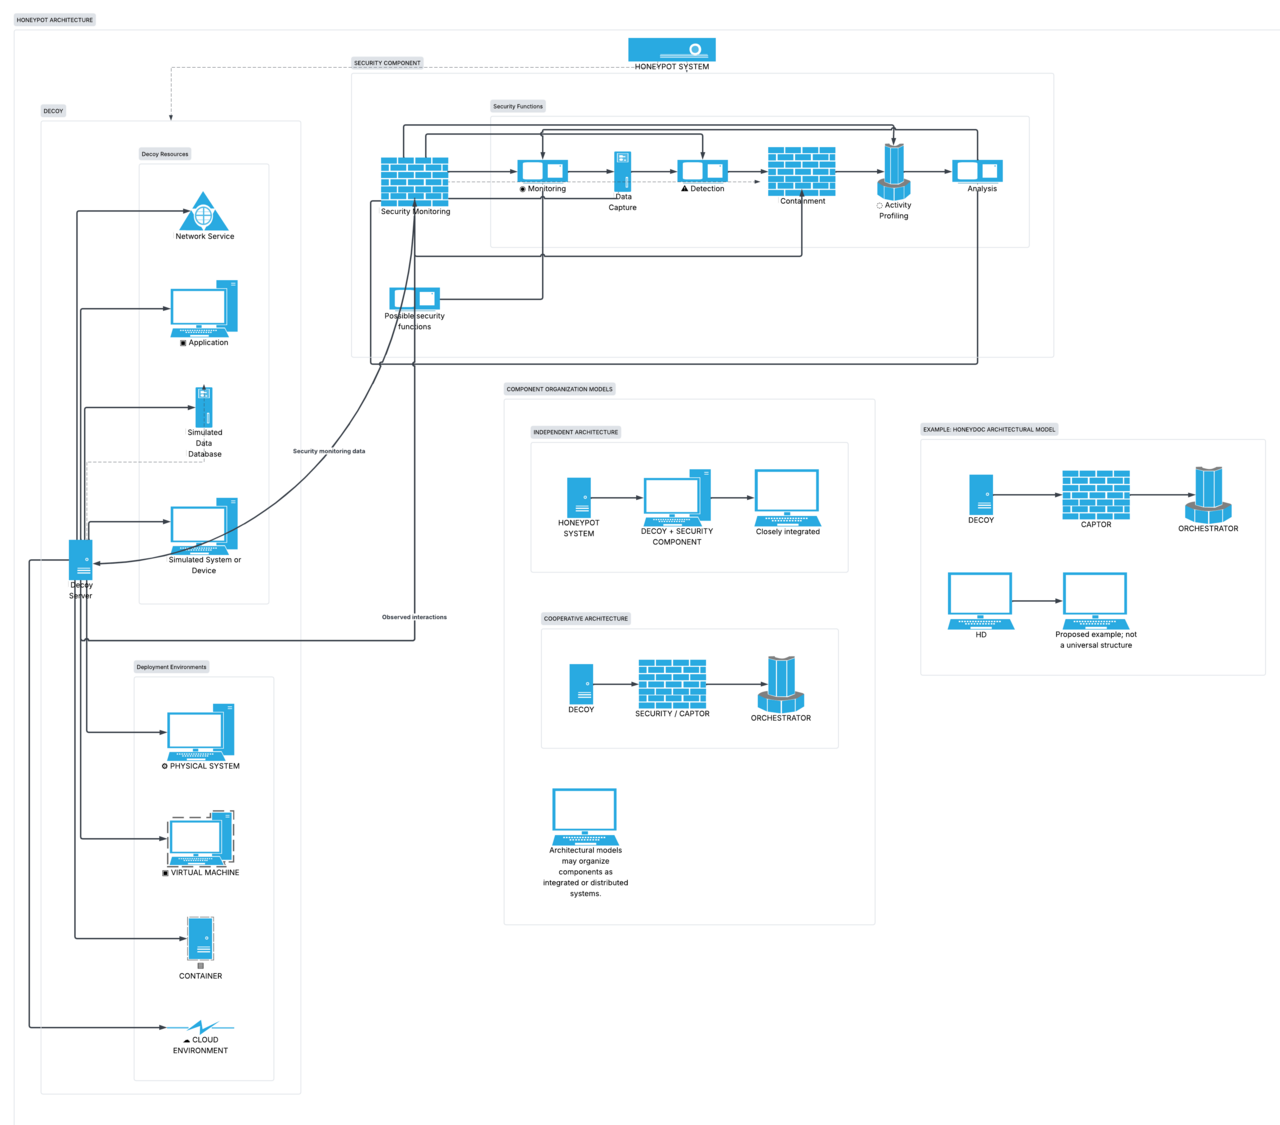
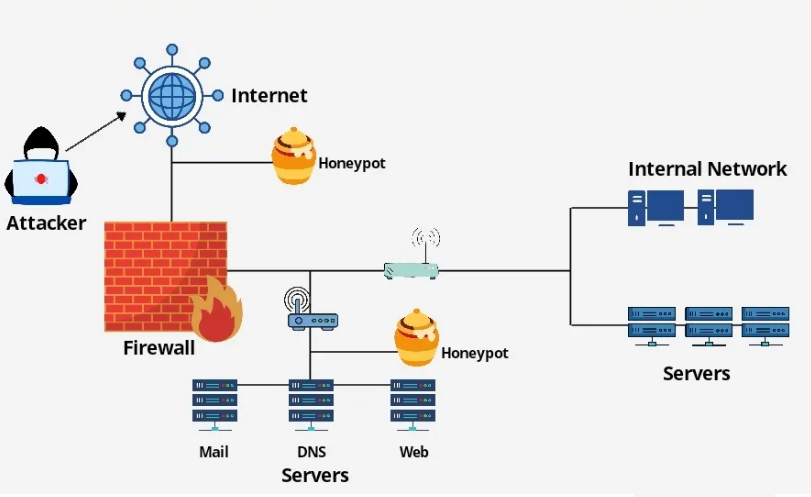
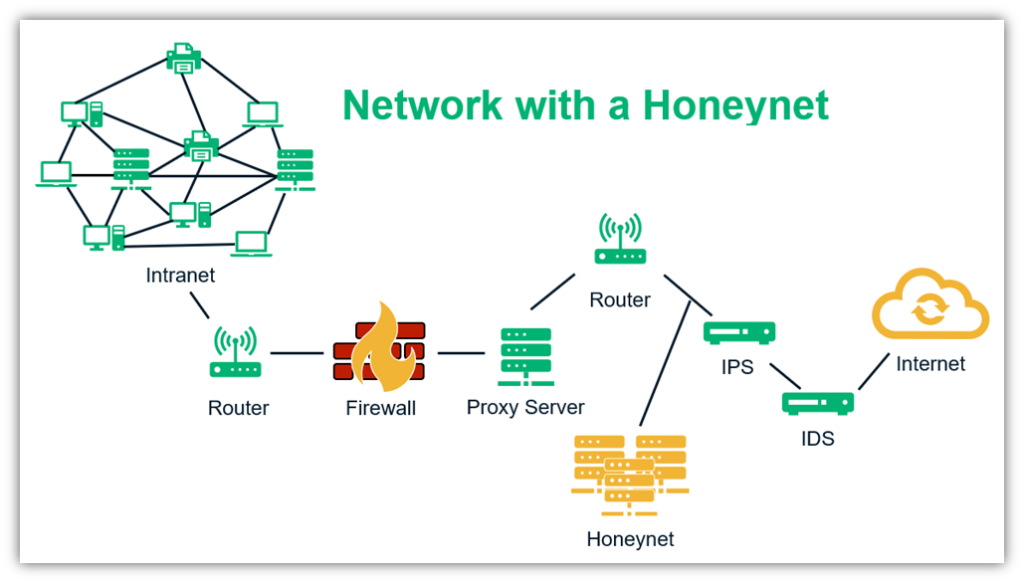
Honeypots are systems specifically designed to attract, detect, and analyze malicious activities. They simulate real network environments to catch attackers in the act. By studying the techniques used against honeypots, organizations can strengthen their defenses against future attacks.
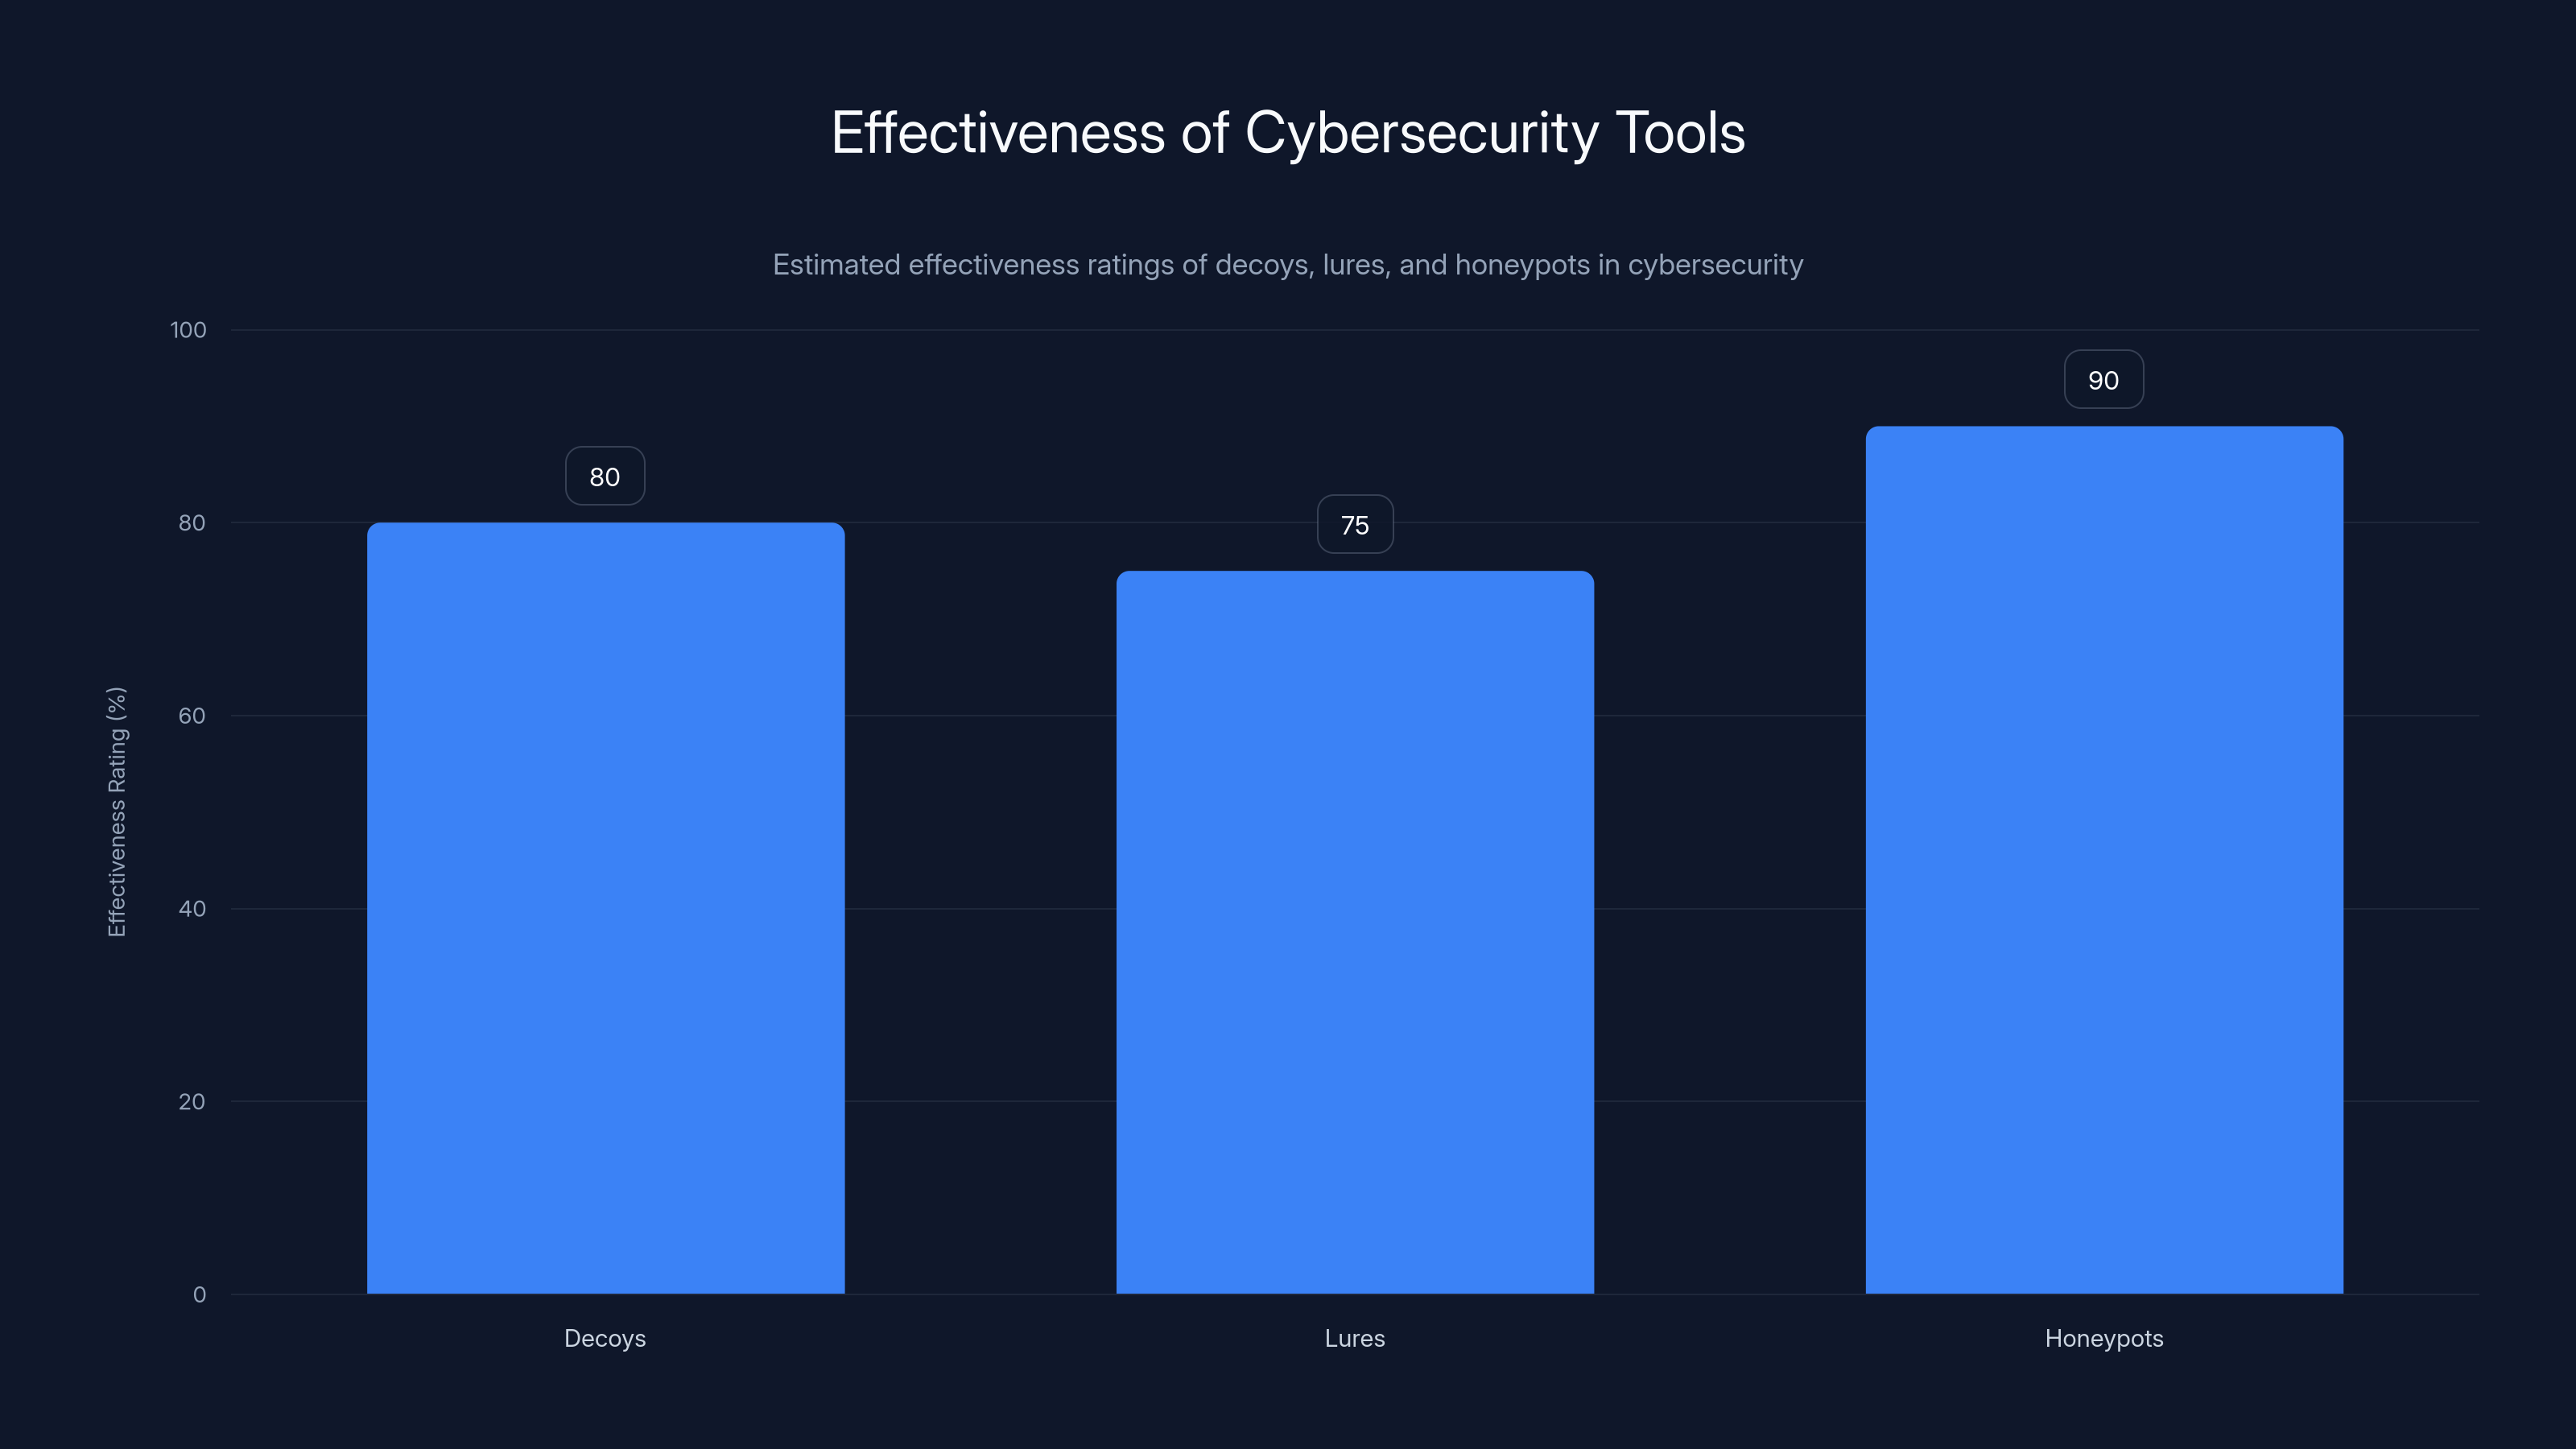
Honeypots are estimated to be the most effective tool in detecting and deterring cyber threats, followed by decoys and lures. Estimated data based on typical cybersecurity assessments.
Why CISA Recommends These Tools
Enhancing Detection with High-Fidelity Alerts
CISA emphasizes the use of decoys and honeypots to generate high-fidelity alerts. Unlike traditional security systems that may produce false positives, these tools trigger alerts only when real threats are detected. This precision helps security teams focus on genuine threats instead of sifting through noise.
Complementing Zero Trust Architecture
Zero Trust is a security framework centered around the principle of "never trust, always verify." While effective, it can benefit from the addition of honeypots and decoys, which specifically target lateral movement within a network. By placing decoys strategically, organizations can detect when an attacker attempts to move laterally, thereby identifying threats that have bypassed perimeter defenses.
Practical Implementation Guides
Setting Up Decoys
- Identify Key Assets: Determine which assets need protection and create decoys that mimic these resources.
- Ensure Realism: A decoy must convincingly replicate the behavior and appearance of real systems.
- Strategic Placement: Place decoys in locations where attackers are likely to target, such as sensitive data stores.
Deploying Honeypots Effectively
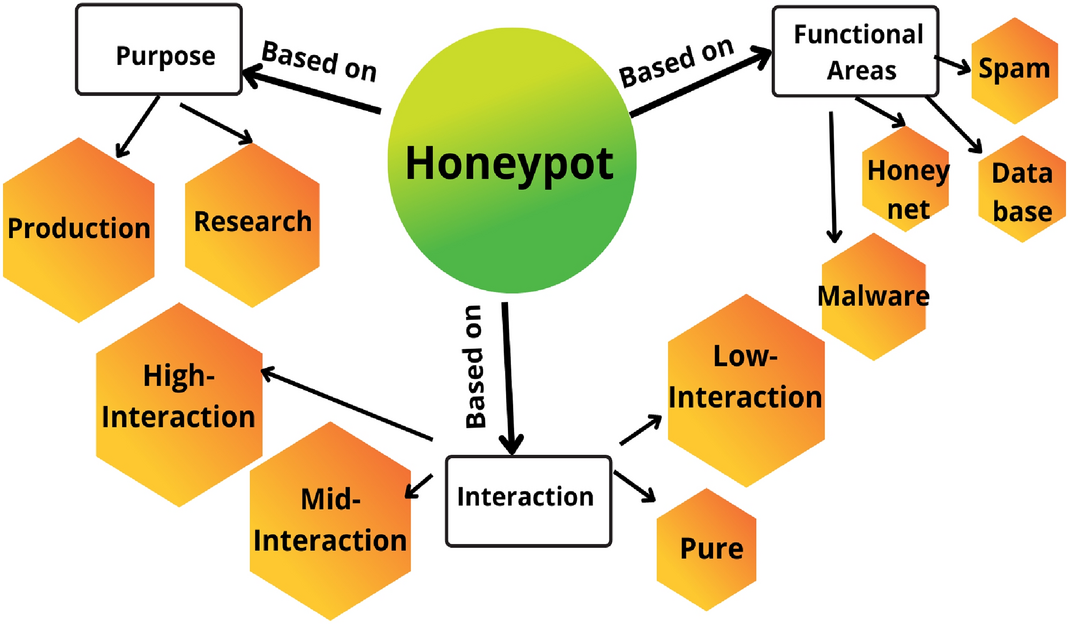
- Types of Honeypots: Choose between low-interaction honeypots, which simulate only certain aspects, and high-interaction honeypots, which replicate entire systems.
- Network Integration: Seamlessly integrate honeypots into the network to avoid detection by attackers.
- Regular Updates: Continuously update honeypots to reflect the latest security threats and attacker techniques.
Using Lures to Guide Attackers
- Crafting Lures: Develop fake credentials, data, and links that appear authentic and valuable.
- Placement Strategy: Position lures in accessible areas that an attacker might encounter during reconnaissance.
- Monitoring Interactions: Set up alerts for when lures are accessed, indicating a potential breach.
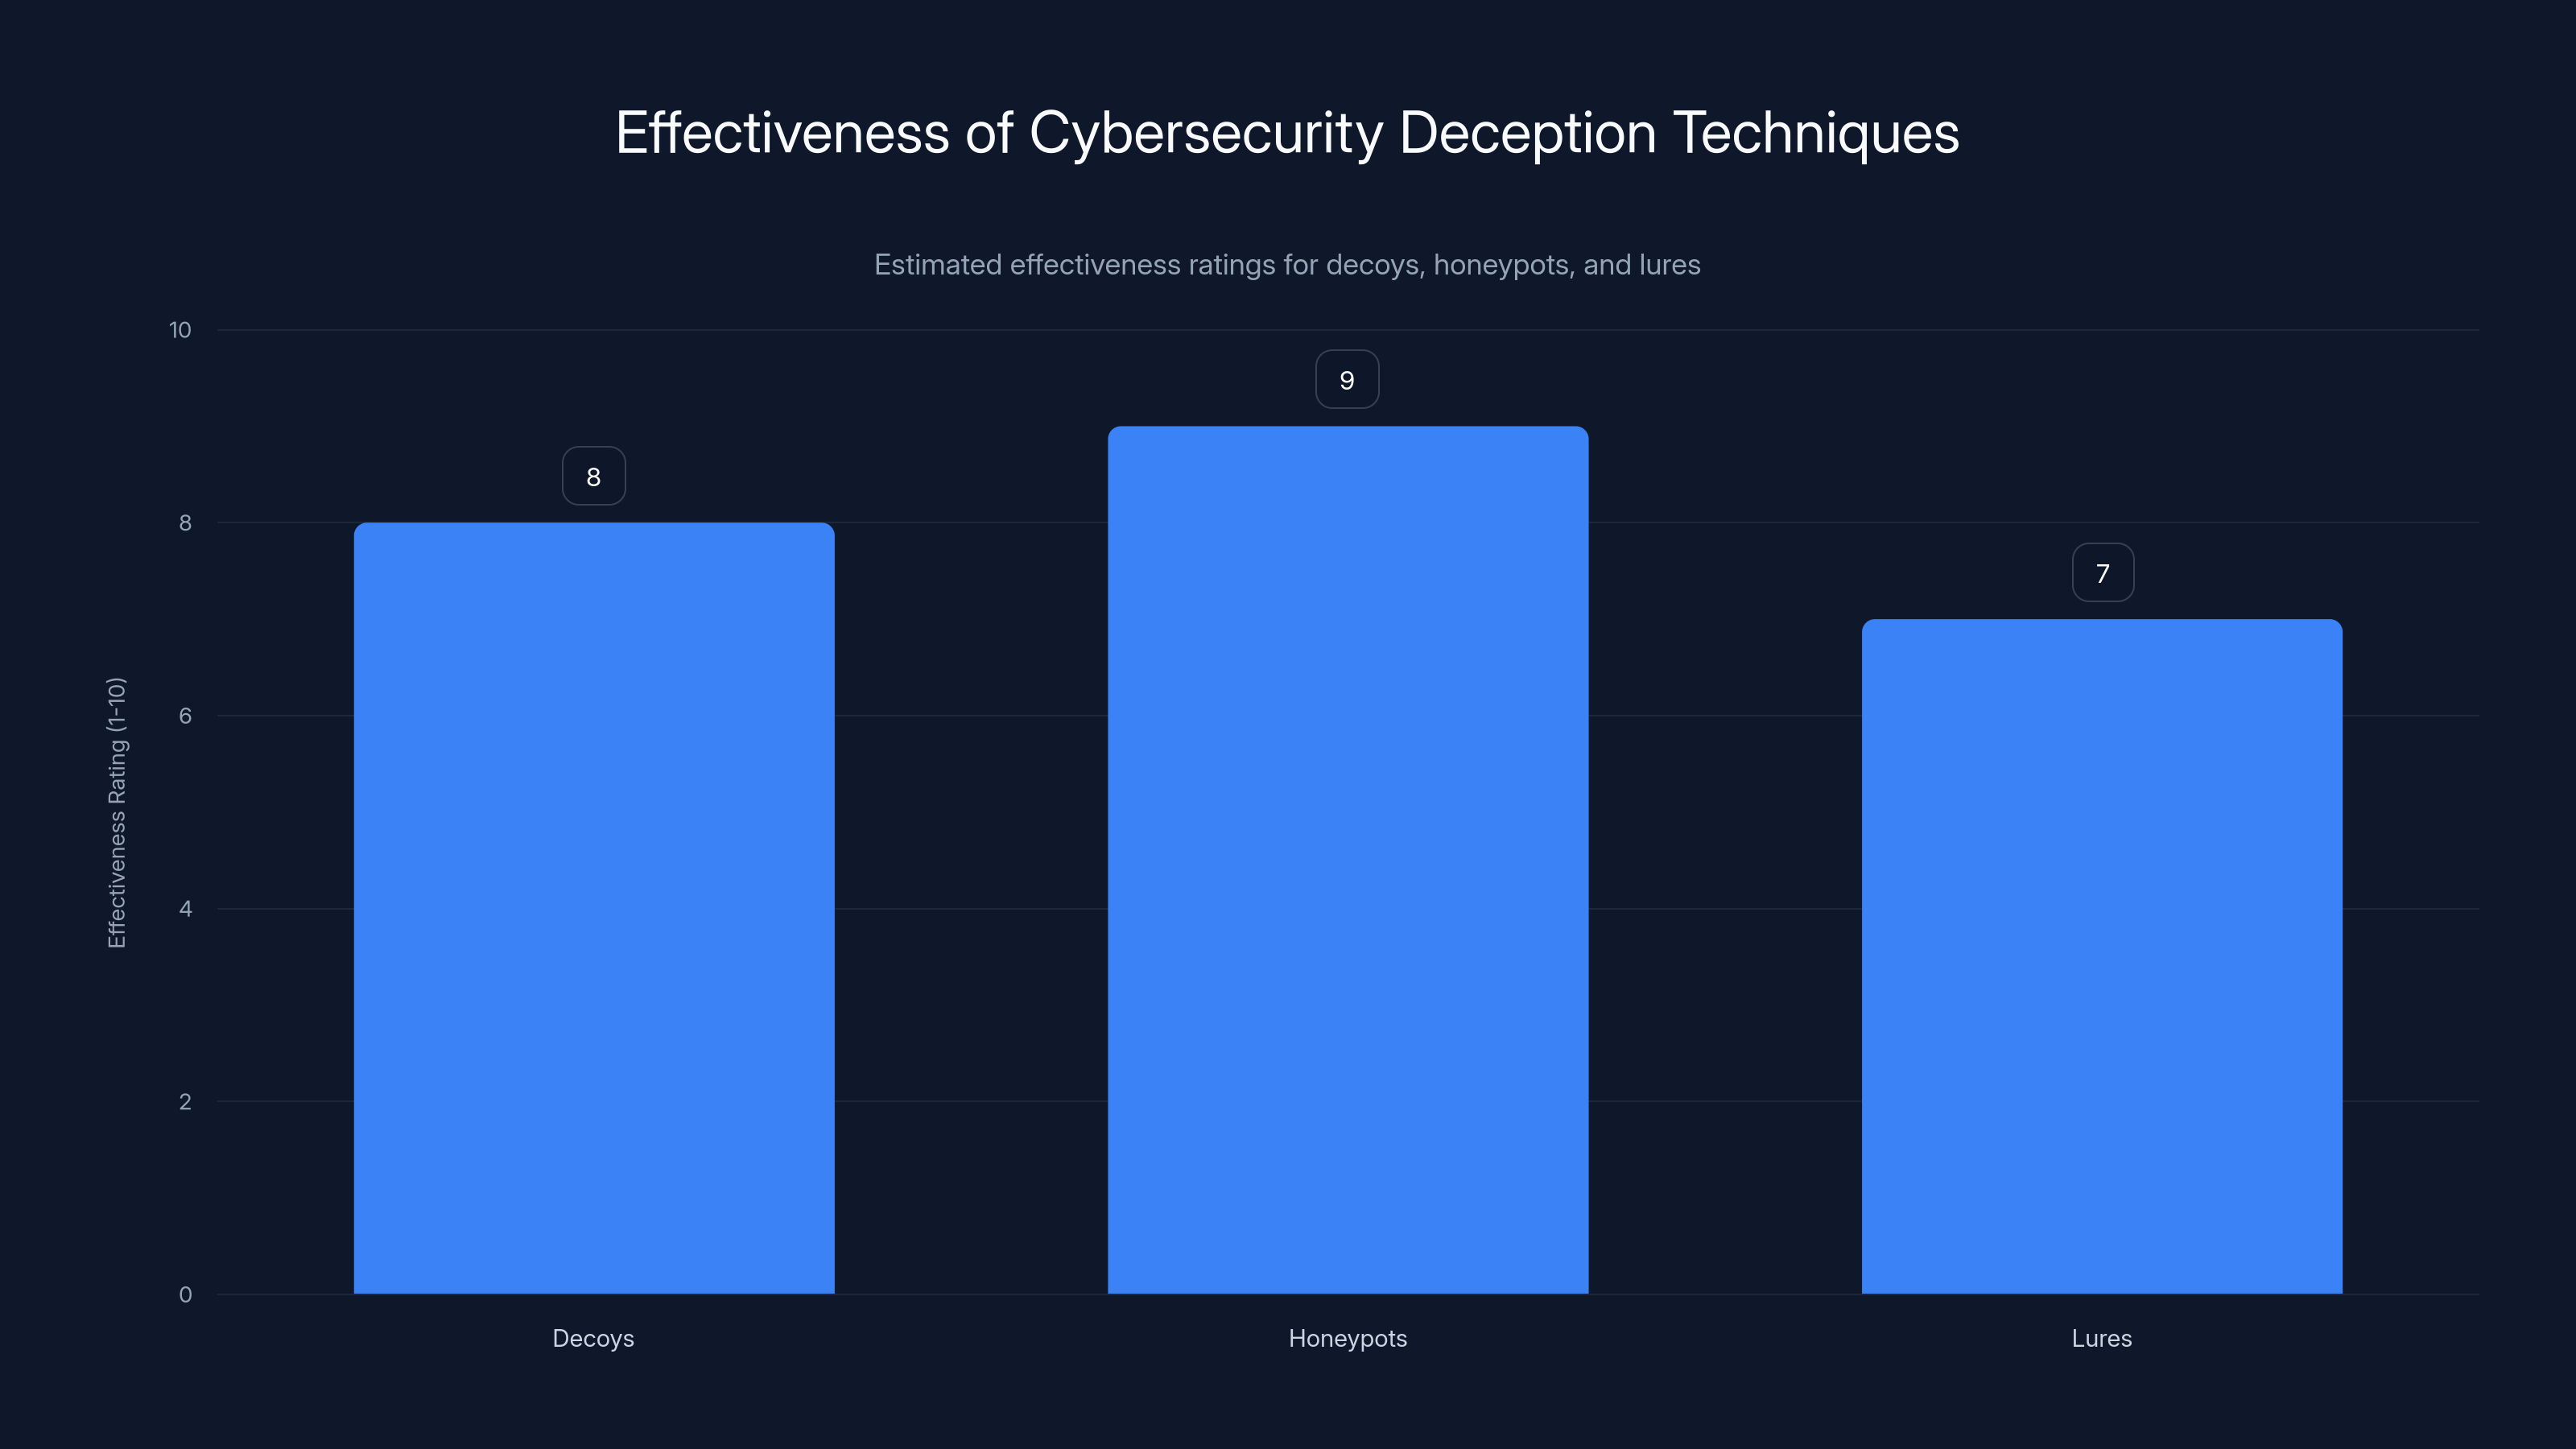
Honeypots are estimated to be the most effective deception technique with a rating of 9, followed by decoys and lures. Estimated data.
Common Pitfalls and Solutions
Overly Complex Deployments
Many organizations overcomplicate their honeypot setups, leading to operational challenges. Solution: Start simple and scale complexity as you gain experience in managing these systems.
Lack of Realism
If decoys and honeypots aren't convincing, skilled attackers will see through them. Solution: Continually refine decoys to match real systems as closely as possible.
Insufficient Monitoring
Deploying a honeypot is only half the battle; monitoring it is crucial. Solution: Set up automated alerts and regularly review activity logs to catch suspicious behavior promptly.

Future Trends in Security Decoys
AI and Machine Learning
The next generation of honeypots will leverage AI to create adaptive environments that evolve in response to attacker tactics. Machine learning can help honeypots anticipate and adapt to new threat vectors, improving their efficacy.
Integration with Threat Intelligence
Expect to see more integration between honeypots and threat intelligence platforms. This will enable real-time updates and adjustments to honeypot configurations based on the latest threat data.
Increased Use of Virtual and Cloud-Based Honeypots
As more businesses move to the cloud, the deployment of virtual honeypots within cloud environments will become standard practice. These honeypots can mimic entire cloud services, providing deeper insights into cloud-specific attack methods.

Best Practices for Deployment
- Define Clear Objectives: Understand what you want to achieve with your decoy and honeypot deployment.
- Ensure Legal Compliance: Verify that your deployment complies with applicable laws and regulations regarding data collection and monitoring.
- Regularly Review and Update: Continuously assess the effectiveness of your decoys and honeypots and make necessary adjustments.
- Integrate with Existing Security Measures: Ensure that your decoys and honeypots complement your current security infrastructure.
Conclusion
Decoys, lures, and honeypots are more than just buzzwords—they're vital components of a robust cybersecurity strategy. By incorporating these tools, organizations can not only detect and deter cyber threats but also gain valuable insights into attacker methods. As cyber threats continue to evolve, so too must our defenses. Deploying these tools effectively can be the difference between a minor incident and a major breach.
Use Case: Automate the deployment and monitoring of honeypots with AI to catch attackers before they reach sensitive systems.
Try Runable For Free
FAQ
What is a honeypot in cybersecurity?
A honeypot is a security mechanism set up to attract and trap cyber attackers. It mimics a legitimate system to capture the techniques and methods used by hackers.
How do decoys improve security?
Decoys divert attackers from real assets and allow security teams to detect unauthorized access attempts, providing valuable insights into potential breaches.
What is the role of lures in cybersecurity?
Lures are used to entice attackers into revealing themselves by interacting with fake data or systems, which can then be monitored for malicious activity.
How do honeypots complement Zero Trust?
Honeypots within a Zero Trust architecture can detect lateral movement, helping to identify threats that bypass perimeter defenses.
Are there risks to using honeypots?
Yes, if not properly configured, honeypots can be identified by attackers, potentially leading to evasion or exploitation.
What future advancements are expected for honeypots?
Future advancements include AI-driven adaptive honeypots and increased integration with threat intelligence platforms to improve detection and response.
How should businesses start deploying honeypots?
Start by identifying key assets, choosing between low- and high-interaction honeypots, and ensuring realistic deployment and monitoring.
Key Takeaways
- Decoys and honeypots provide high-fidelity alerts for genuine threats.
- Integration with Zero Trust enhances lateral movement detection.
- AI-driven honeypots can adapt to new attacker strategies.
- Strategic deployment of lures can reveal attacker methods.
- Future trends include AI integration and cloud-based honeypots.
- Effective monitoring and realism are critical for honeypot success.
- Honeypots offer insights into attacker behavior, strengthening defenses.
Related Articles
- Understanding Zero-Day Attacks: Lessons from the Pixel Phone Hack [2025]
- Understanding Calendar-Based Phishing: The Unseen Threat in Your Schedule [2025]
- Cisco Zero-Day Exploit on Identity Services Engine: Secure Your Network Now [2025]
- Building Enterprise Resilience Against Growing AI Risks [2025]
- The AI Slowdown Debate Crashed Salesforce’s Party | WIRED
- Your Robotaxi Might Be a Narc: Navigating the Future of Autonomous Vehicle Surveillance [2025]


