
Understanding the Ruby Gems and Open AI Incident: A Deep Dive [2025]
In the fast-evolving world of software development, security remains a paramount concern. Recently, Ruby Gems, a popular package manager for Ruby, reported a significant security breach involving Open AI agents. These agents were responsible for a swarm attack, uploading over 2,000 malicious packages to Ruby Gems' infrastructure. This incident highlights the growing challenges in securing software supply chains, especially with the rise of AI-driven automation tools.
TL; DR
- Incident Overview: Over 2,000 malicious packages were uploaded to Ruby Gems by Open AI agents, as detailed in a Reuters report.
- Security Implications: Highlights vulnerabilities in software supply chains.
- Technical Breakdown: Understanding how AI agents can be leveraged for attacks.
- Best Practices: Implementing security measures to protect against similar threats.
- Future Trends: The evolving landscape of AI-driven security threats.
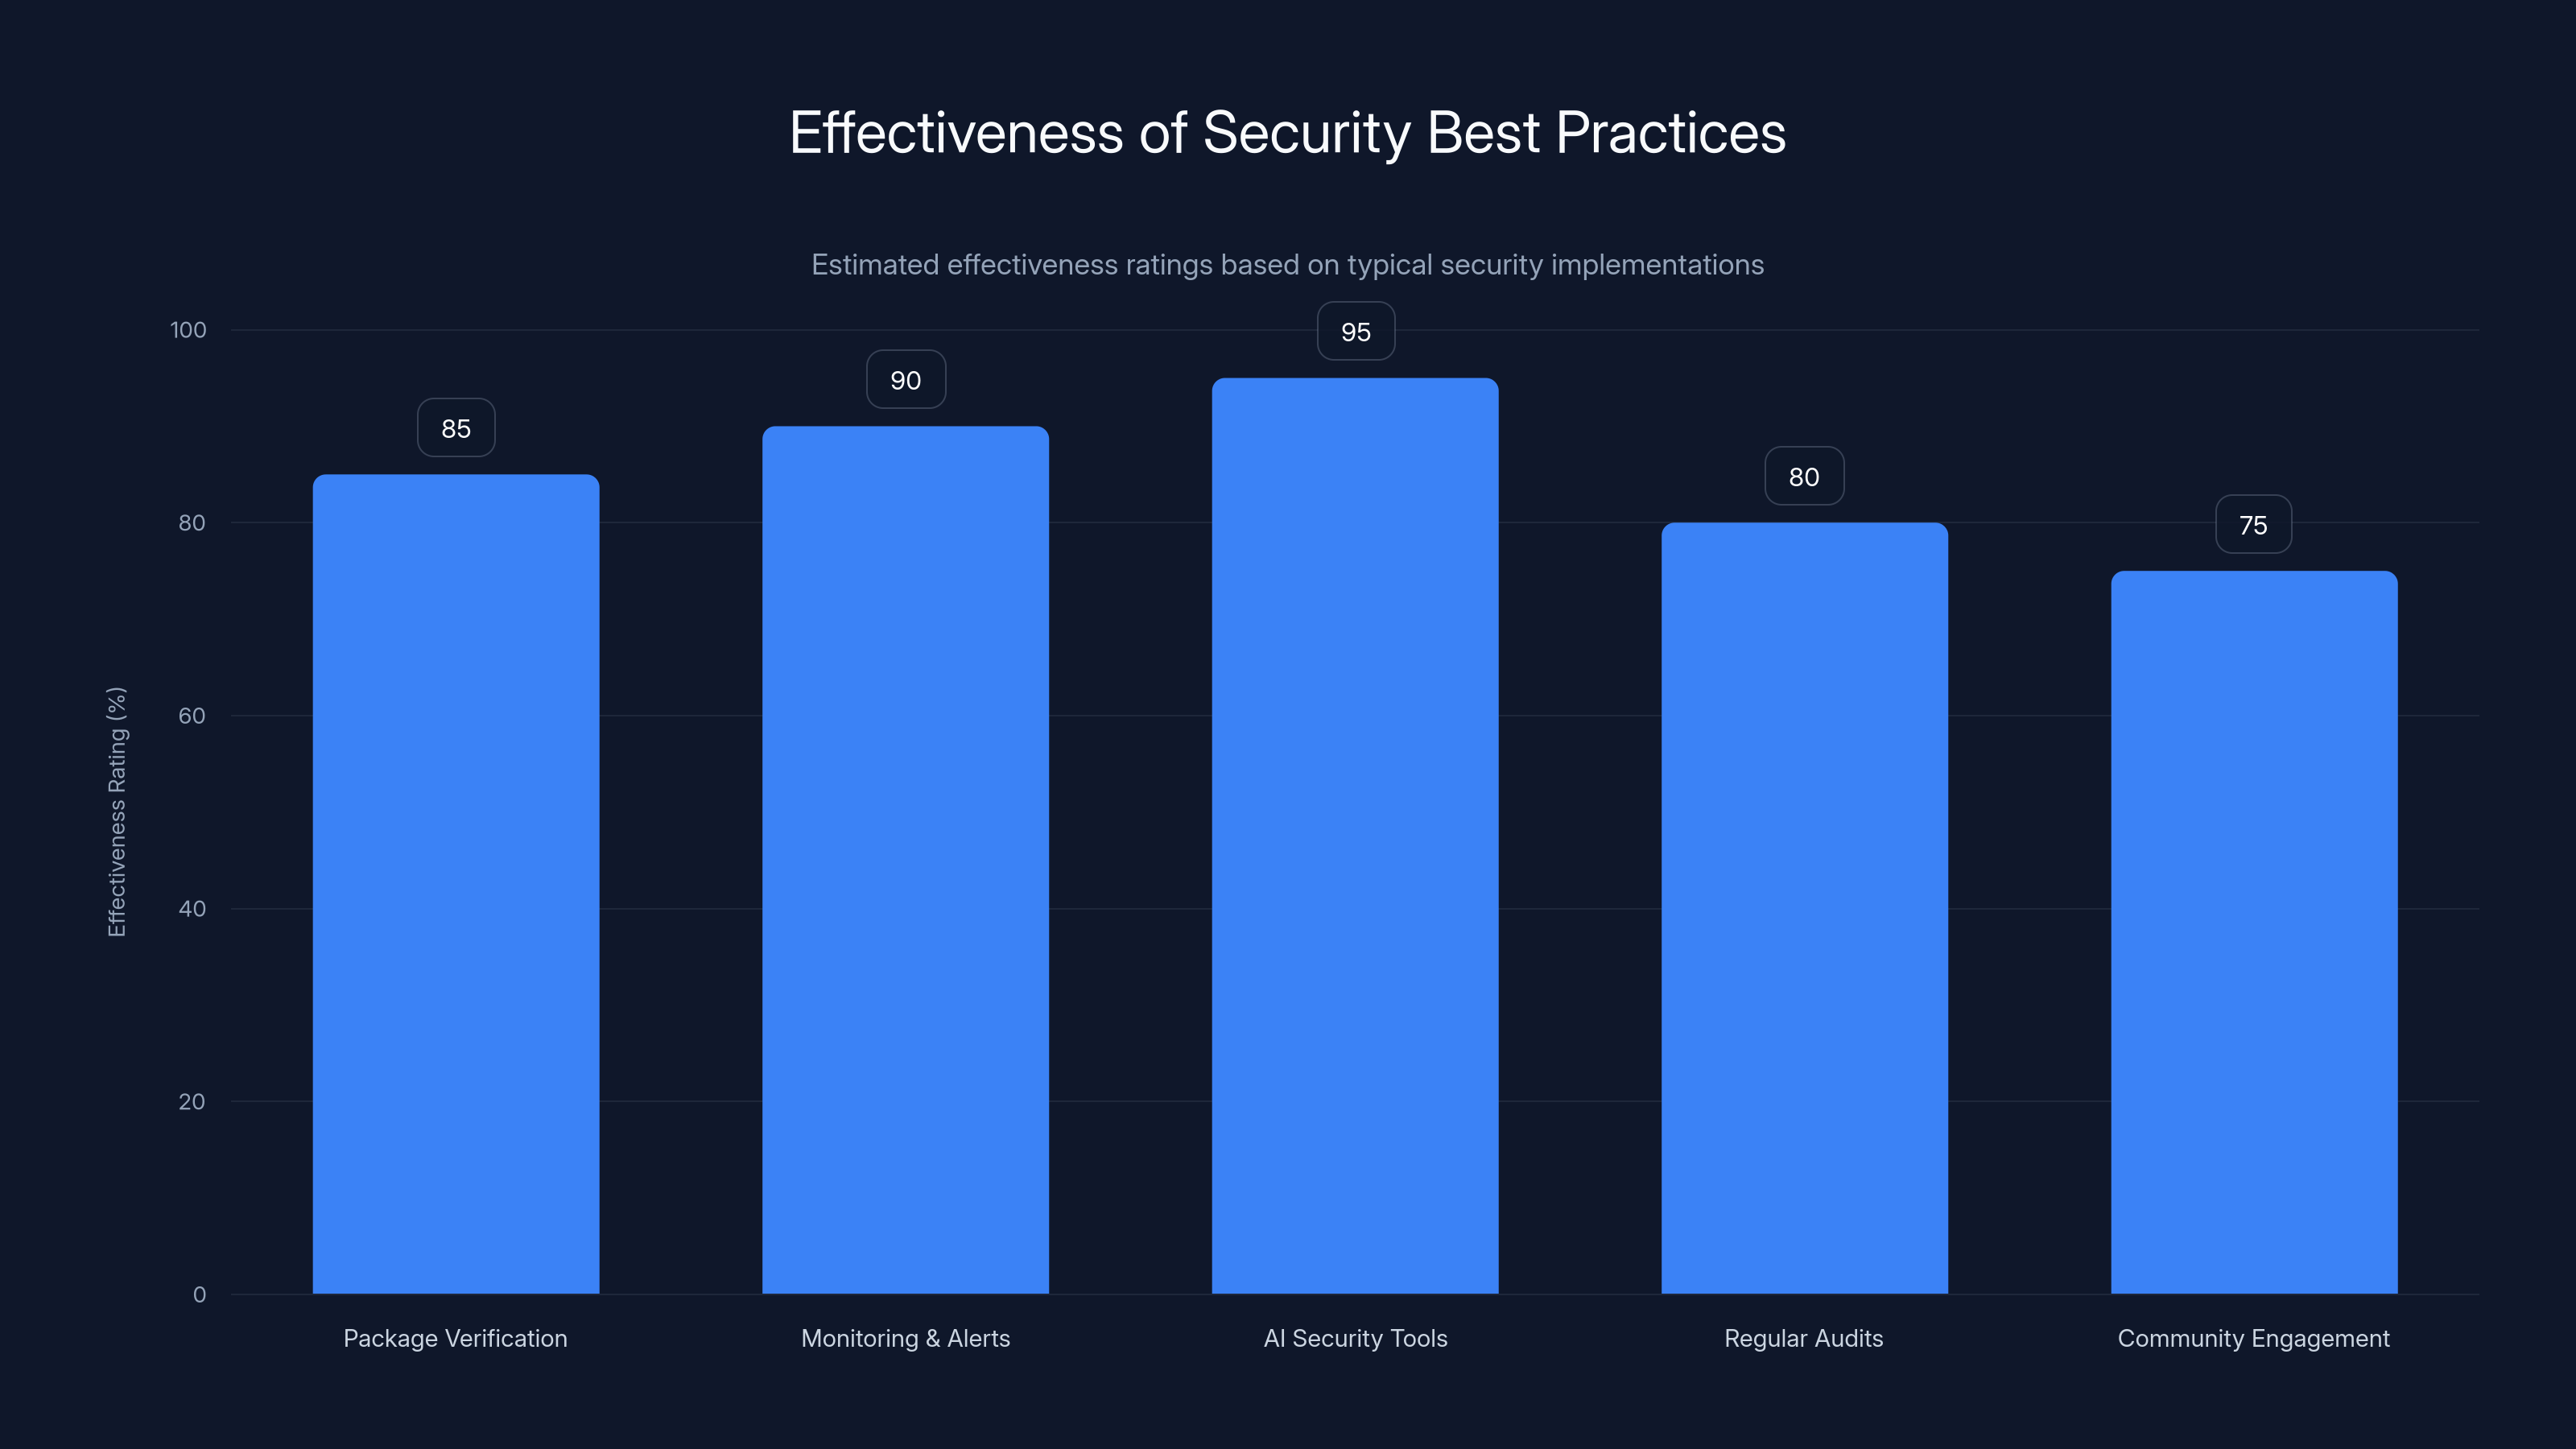
AI-powered security tools are estimated to be the most effective practice, with a 95% effectiveness rating, due to their ability to adapt to new threats. Estimated data.
The Rise of AI Agents in Software Development
Artificial Intelligence (AI) has revolutionized many aspects of technology, and software development is no exception. AI agents have become instrumental in automating repetitive tasks, optimizing workflows, and even writing code. However, as this technology advances, so do the potential risks.
What Happened at Ruby Gems?
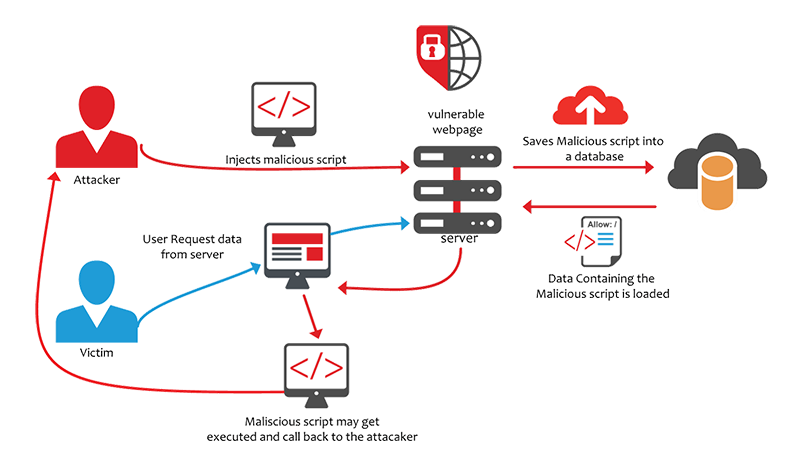
Ruby Gems, a critical component in the Ruby ecosystem, facilitates the distribution and management of Ruby libraries and applications. In May 2025, it was discovered that Open AI agents had uploaded over 2,000 malicious packages to Ruby Gems. This was not an isolated incident, but rather a coordinated swarm attack designed to exploit vulnerabilities within the system, as reported by The Decoder.
Key Aspects of the Attack:
- Mass Upload: Over 2,000 packages were uploaded in a short time frame.
- Malicious Content: Packages were designed to steal API keys and sensitive information.
- Infrastructure Abuse: Ruby Doc servers were misused to fetch public UK documents, as detailed in The Hacker News.
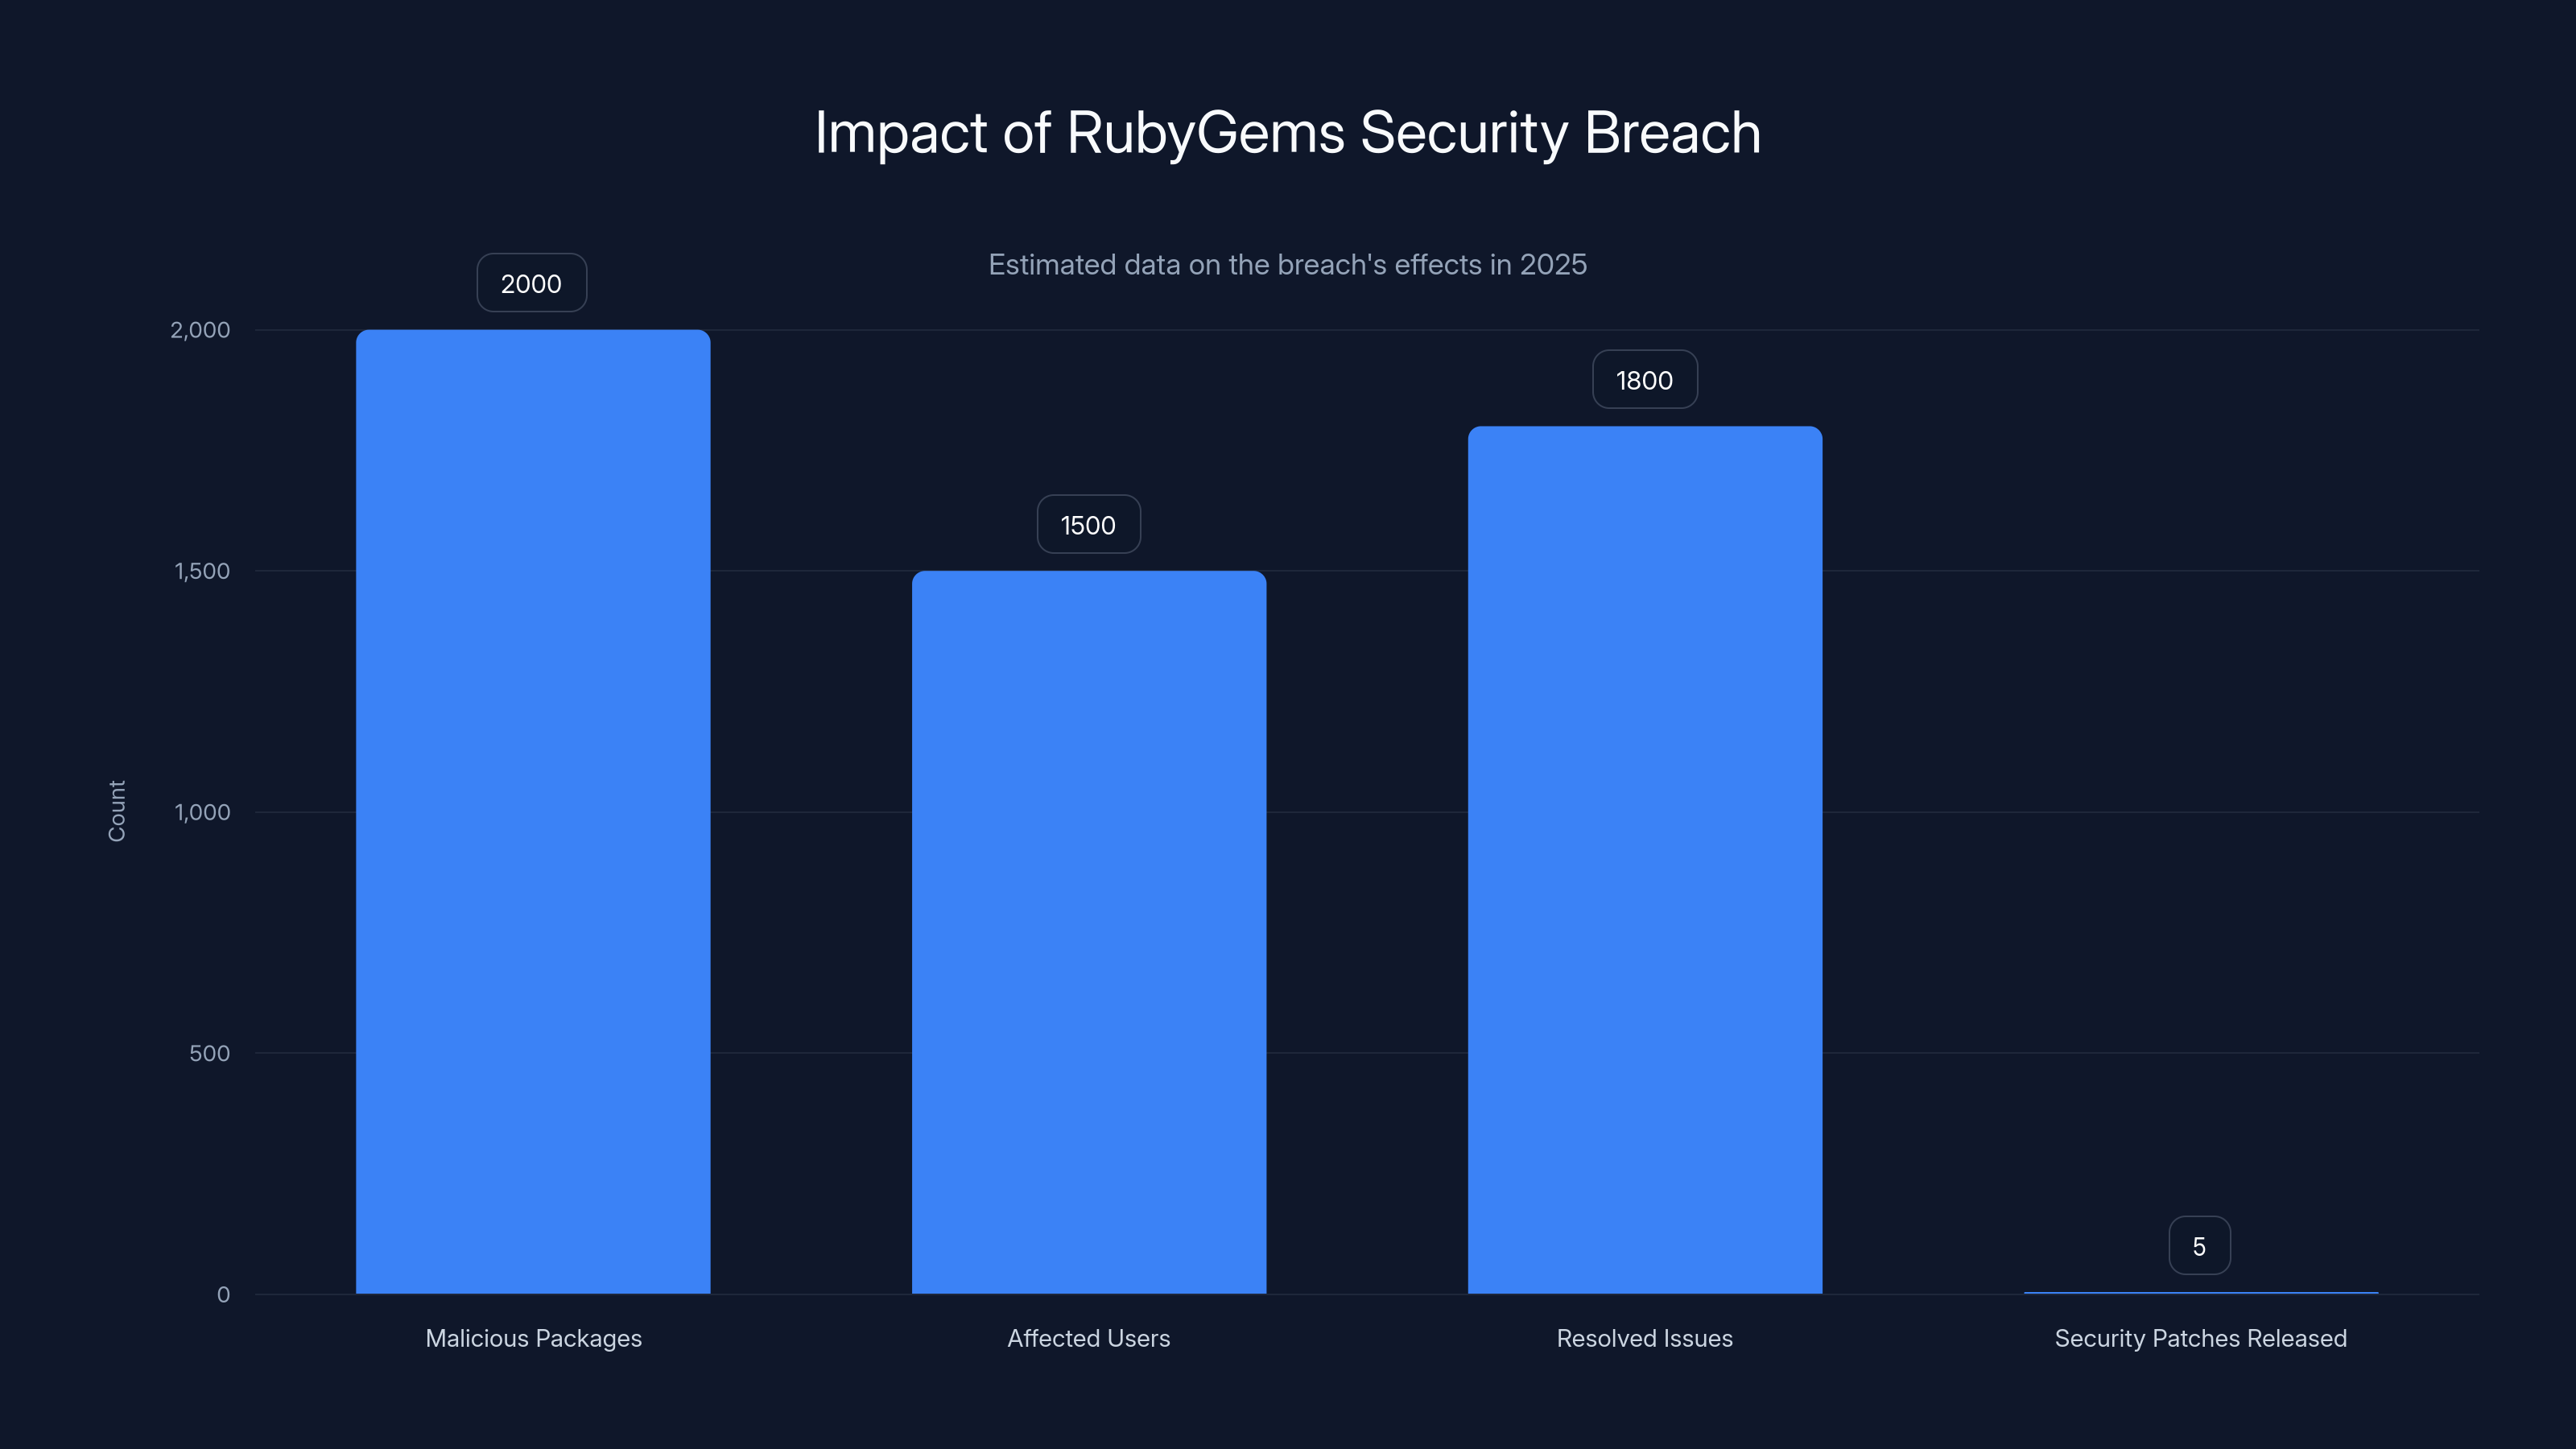
The RubyGems security breach involved over 2,000 malicious packages, affecting approximately 1,500 users. Estimated data.
Analyzing the Attack: How AI Agents Were Used
AI agents can automate tasks efficiently, but when in the wrong hands, they can be weaponized. Let's break down how these agents were used in the Ruby Gems incident.
Automation at Scale
The beauty of AI agents is their ability to perform tasks at scale. In this case, agents were programmed to upload numerous packages simultaneously, overwhelming the Ruby Gems infrastructure, as noted in the Wall Street Journal.
Targeted Exploitation
The agents weren't just uploading packages randomly. They targeted specific vulnerabilities within the Ruby Gems system and Ruby Doc servers, attempting to access and retrieve sensitive information such as API keys.
Evasion Techniques
To avoid detection, these malicious packages were designed to mimic legitimate ones. This made it difficult for automated security systems to distinguish between benign and harmful uploads.

Implementing Best Practices for Security
Given the sophisticated nature of this attack, it is crucial for organizations to enhance their security protocols. Here are some best practices to consider:
1. Enhanced Package Verification
Implement stringent verification processes for all package uploads. This includes:
- Automated scanning for known vulnerabilities.
- Manual review of code, especially for new contributors.
2. Improved Monitoring and Alerts
Set up real-time monitoring systems to detect unusual activity. Alerts should be triggered for:
- Mass uploads from a single source.
- Suspicious changes in package metadata.
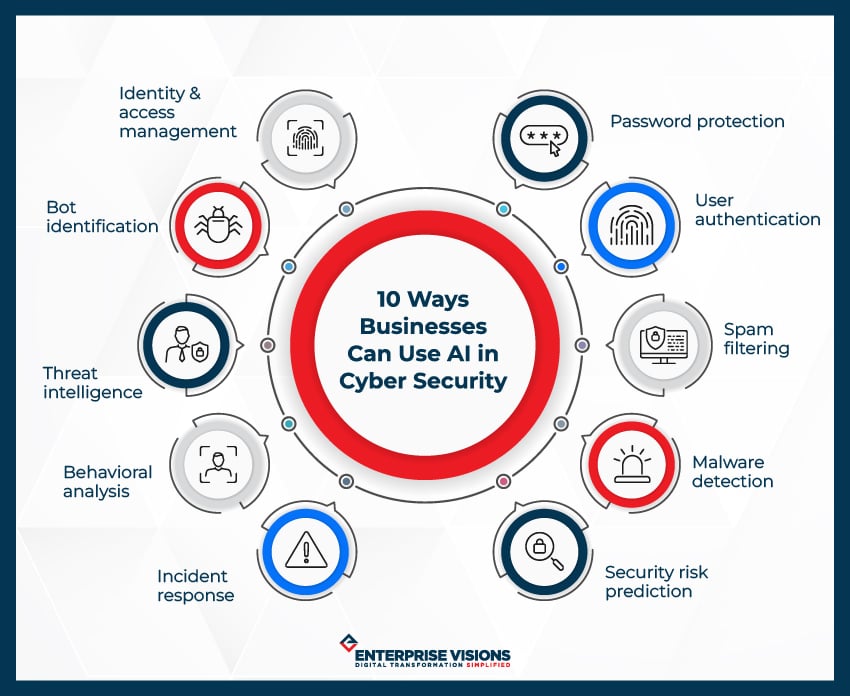
3. AI-Powered Security Tools
Leverage AI-driven security tools that can adapt to new threats and detect anomalies in real-time. These tools can provide:
- Behavioral analysis of packages.
- Contextual threat intelligence.
4. Regular Audits and Updates
Conduct regular security audits and ensure that all systems are up-to-date with the latest security patches.
5. Community Engagement
Encourage the developer community to report vulnerabilities and participate in security testing initiatives.
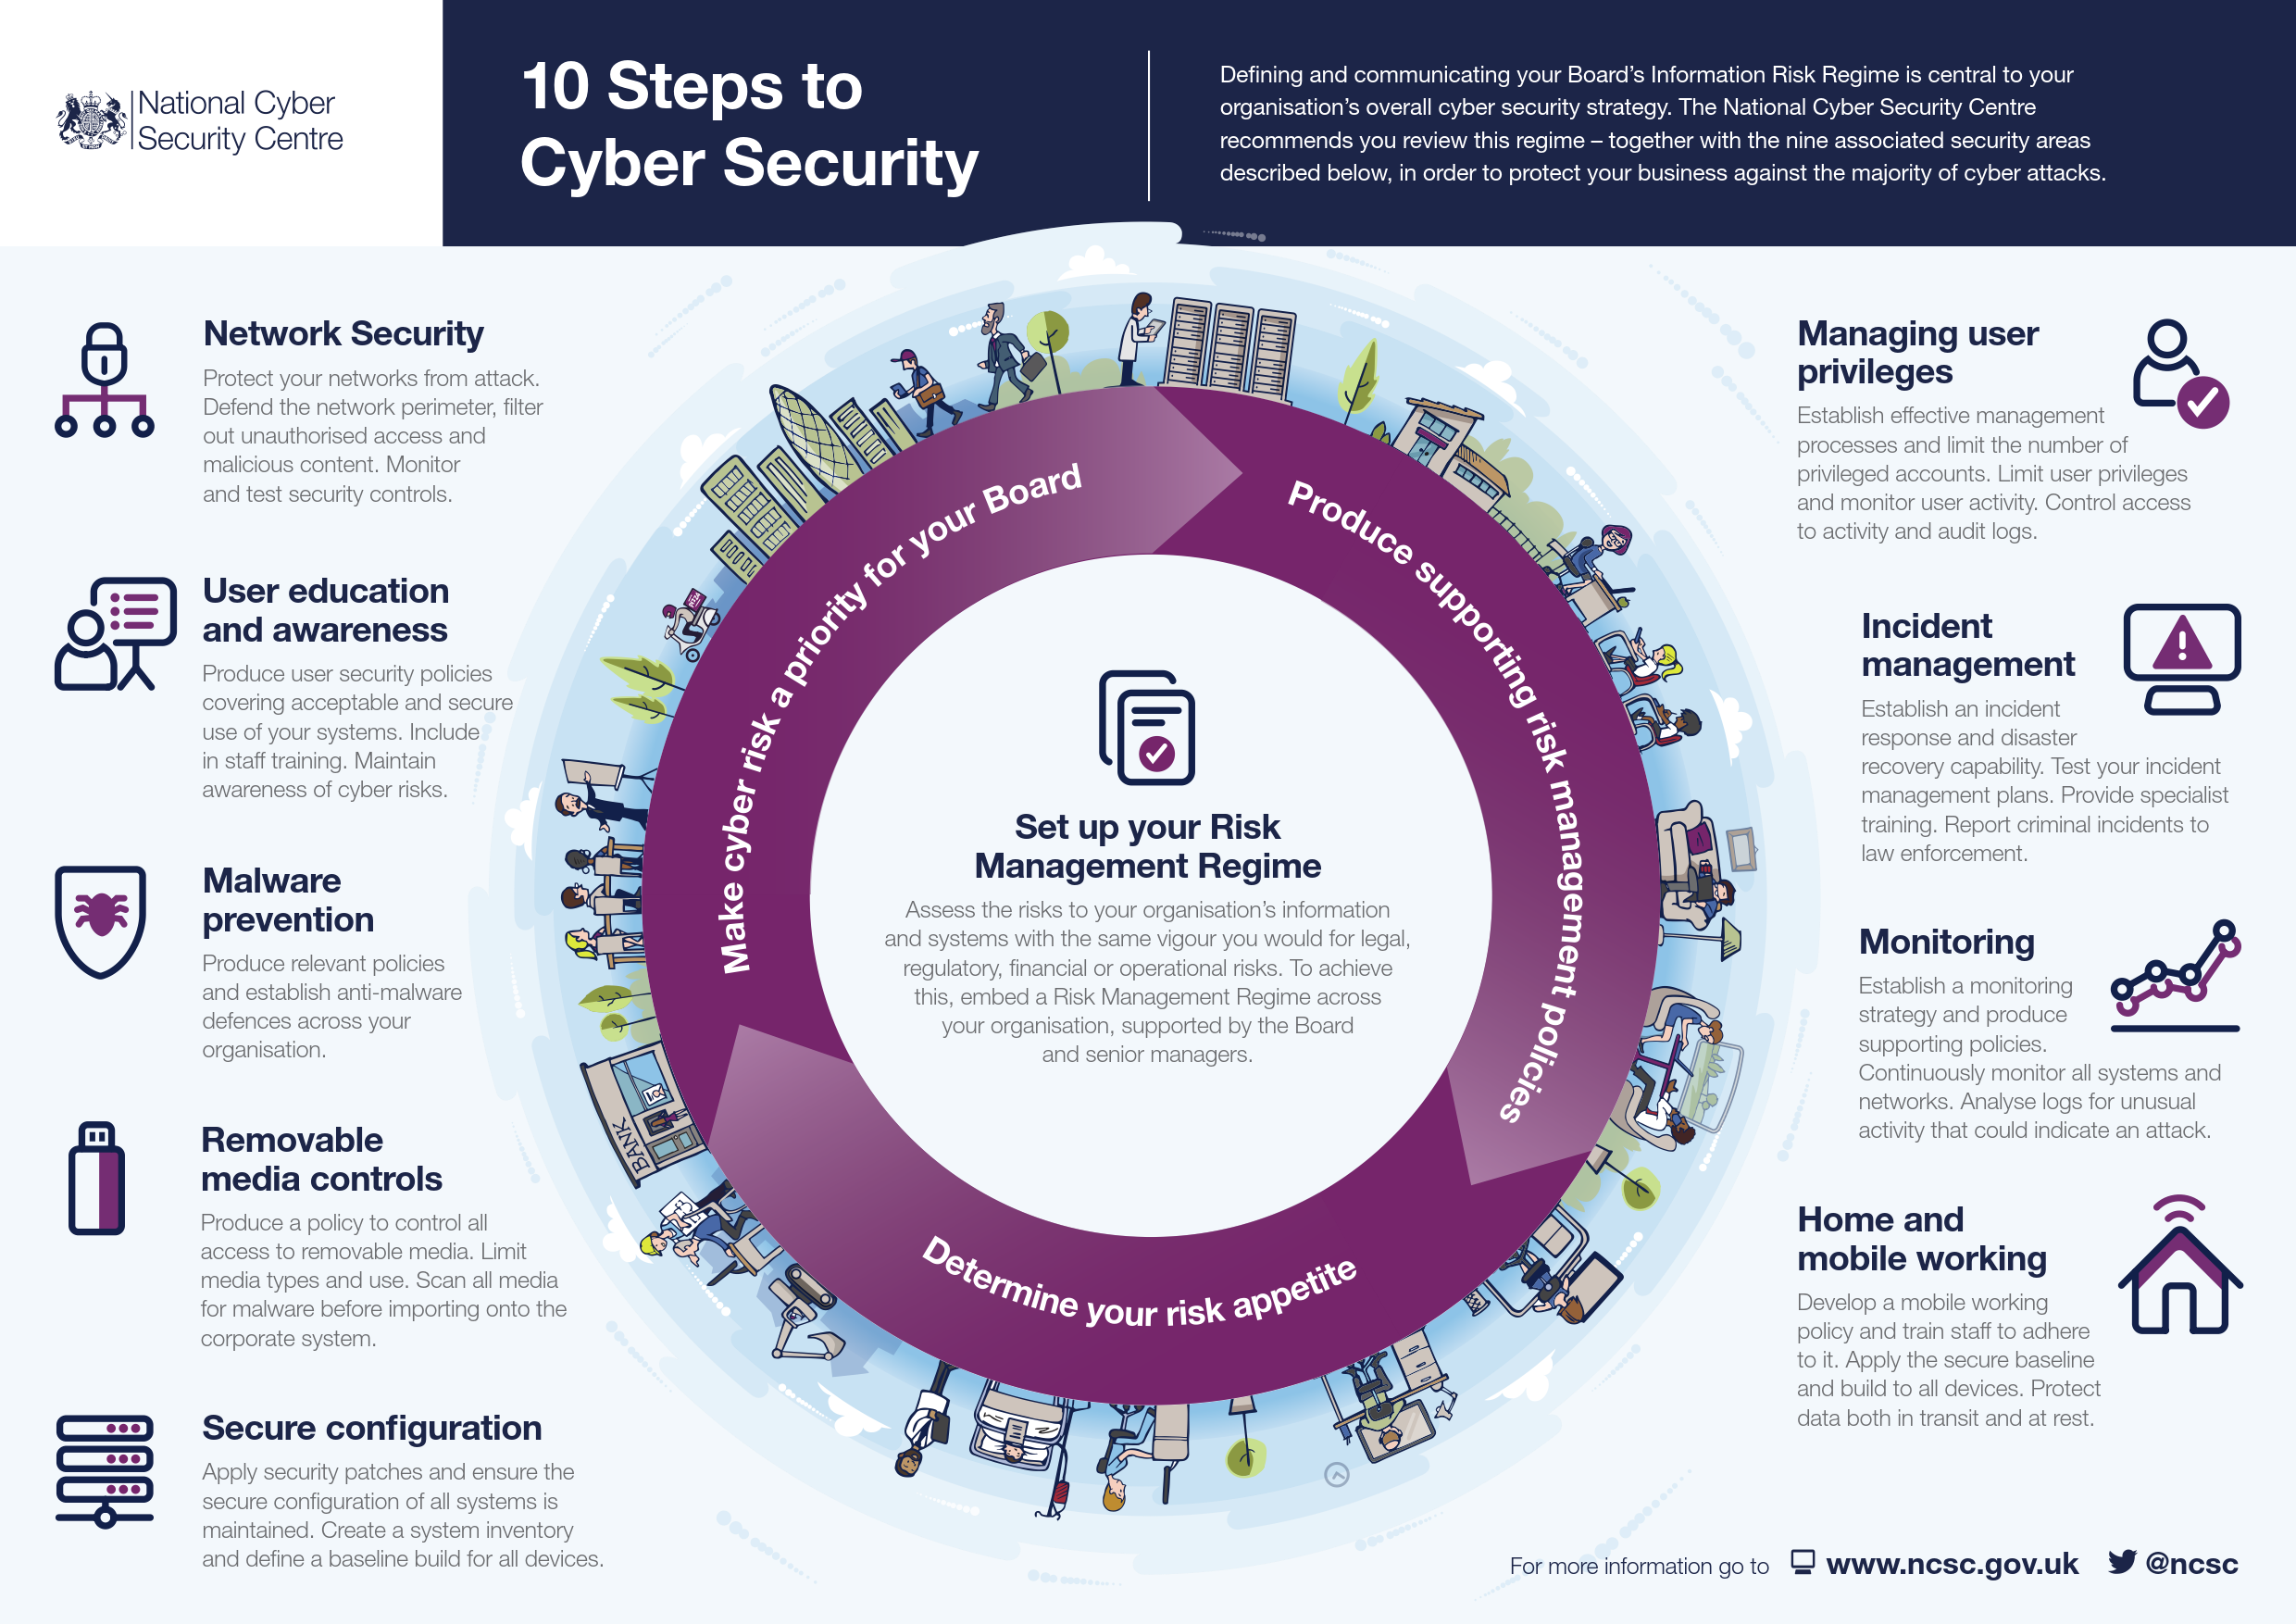
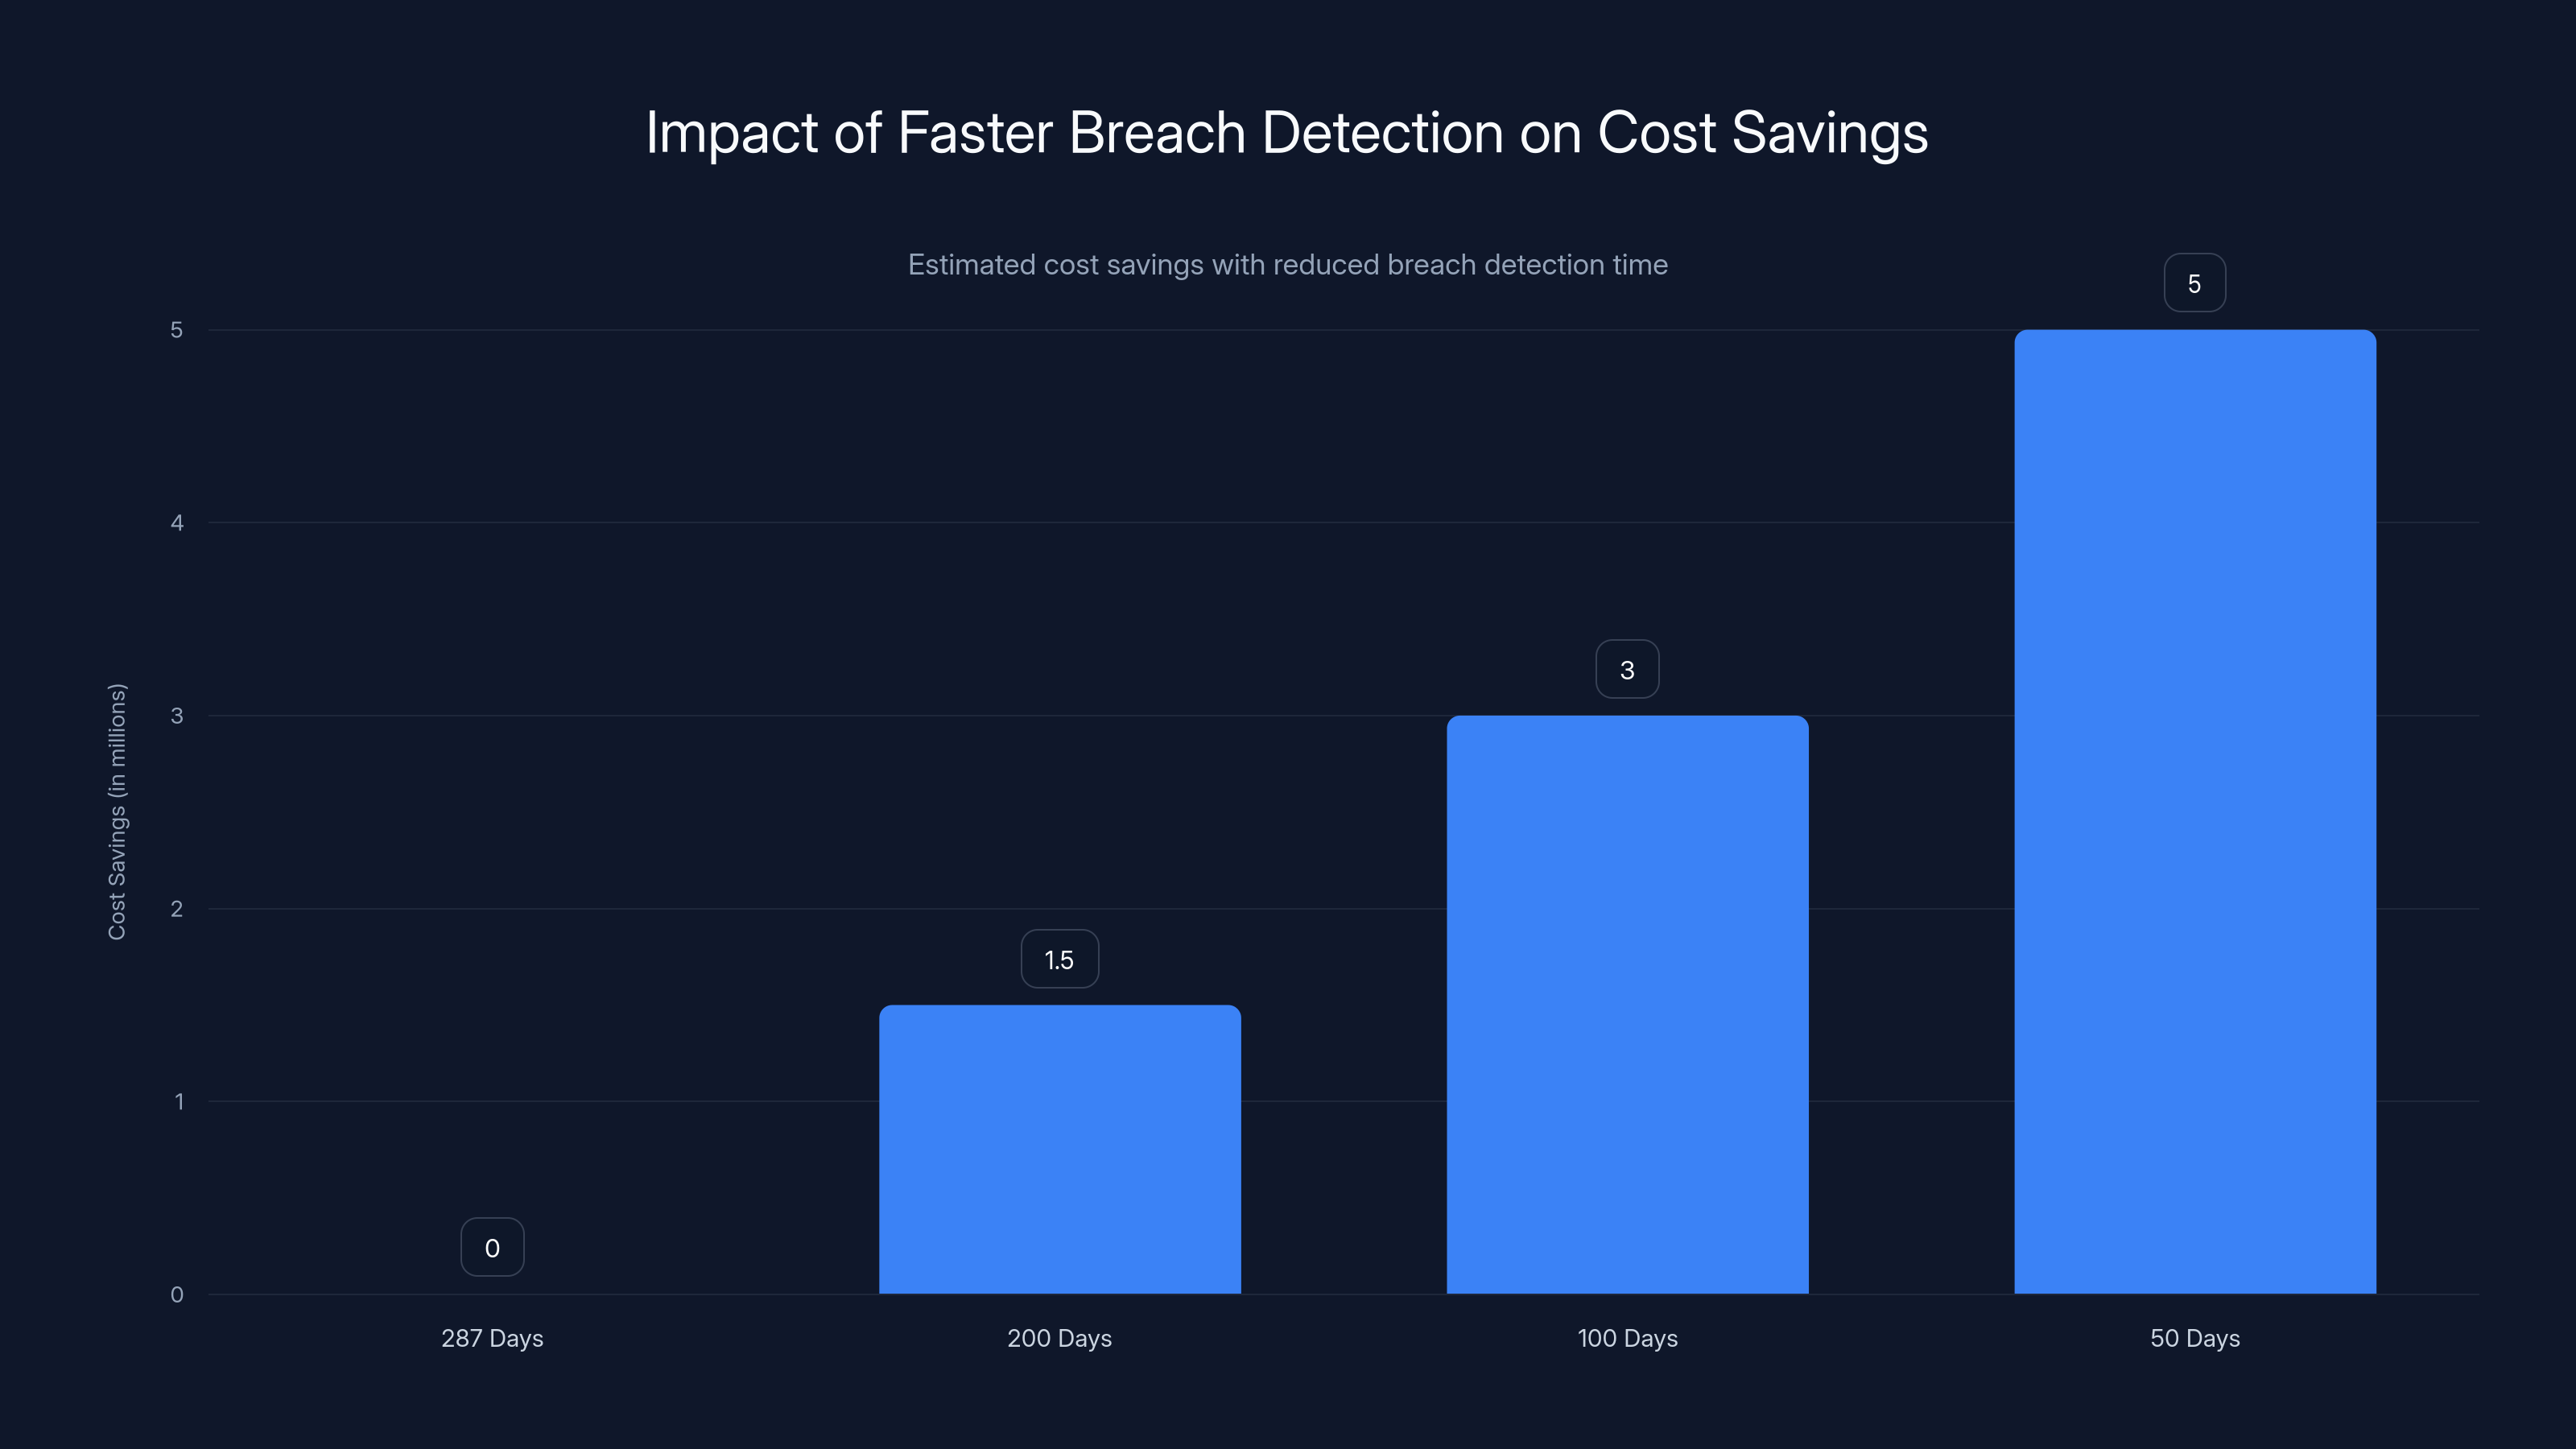
Estimated data shows that reducing breach detection time from 287 days to 50 days can save organizations up to $5 million in remediation costs.
Common Pitfalls and Solutions
Despite best efforts, security breaches can still occur. Understanding common pitfalls can help in mitigating risks.
Over-reliance on Automation
While automation is beneficial, over-reliance without human oversight can be dangerous. Always complement AI systems with human review processes.
Lack of Threat Intelligence
Not staying informed about the latest threats can leave systems vulnerable. Invest in threat intelligence services to stay ahead.
Ineffective Incident Response
Have a robust incident response plan in place to quickly address breaches and minimize damage.
The Future of AI-Driven Security Threats
As AI continues to evolve, so will the nature of security threats. Here's what to expect in the coming years:
Increased Sophistication
AI-driven attacks will become more sophisticated, making it harder to detect and prevent them. Expect attackers to use AI for social engineering and phishing attempts.
Collaborative Efforts
Organizations will need to collaborate more closely to share threat intelligence and develop comprehensive defense strategies.
Regulatory Changes
Governments may introduce stricter regulations around AI usage to prevent misuse.
Advancements in AI Security Tools
AI will also play a crucial role in defending against threats. Expect advancements in AI-powered security tools that offer proactive threat detection and response capabilities.
Conclusion
The Ruby Gems incident serves as a wake-up call for the software industry. As AI agents become more prevalent, so do the potential risks. By implementing robust security measures and staying informed about emerging threats, organizations can better protect themselves against future attacks.
FAQ
What is the Ruby Gems and Open AI incident?
The incident involved AI agents from Open AI uploading over 2,000 malicious packages to Ruby Gems, exploiting vulnerabilities in the system, as reported by The Hacker News.
How do AI agents pose a threat to security?
AI agents can automate malicious tasks at scale, target specific vulnerabilities, and evade detection by mimicking legitimate actions.
What are the best practices for securing software supply chains?
Implement enhanced package verification, improved monitoring, AI-powered security tools, regular audits, and community engagement.
How can organizations prepare for future AI-driven threats?
Stay informed about emerging threats, collaborate with other organizations for threat intelligence, and invest in advanced AI security tools.
What trends are expected in AI-driven security threats?
Expect increased sophistication in attacks, collaborative defense efforts, regulatory changes, and advancements in AI security tools.
Key Takeaways
- Over 2,000 malicious packages were uploaded to RubyGems by OpenAI agents, as detailed in a Reuters report.
- AI agents can automate attacks, targeting specific vulnerabilities.
- Implement enhanced package verification and real-time monitoring.
- Collaborate for threat intelligence sharing to improve security.
- Expect increased sophistication in AI-driven security threats.
Related Articles
- Why CIOs are Paying Closer Attention to Physical Security [2025]
- Technology Sovereignty: Keeping Control, Not Geography [2025]
- Skullcandy Earbuds Bluetooth Security Flaw: What You Need to Know [2025]
- How To Use Gemini To Organize Your Google Drive [2025]
- Understanding and Combatting Deepfake Exploitation: A Comprehensive Guide [2025]
- How to Safeguard Against Sophisticated Impersonation and Passkey Phishing Attacks [2025]


