
Understanding Voicemail Phishing Attacks and How to Protect Your Organization [2025]
When it comes to cybersecurity, the landscape is always shifting, and attackers are constantly finding new ways to exploit vulnerabilities. Recently, a surge in voicemail phishing attacks has caught the attention of security professionals worldwide. This article delves into the mechanics of these attacks, provides real-world examples, and offers actionable insights to help protect your organization from such threats.
TL; DR
- Rising Threat: Over 7,800 organizations were recently targeted by fake voicemail phishing emails.
- Attack Vector: Phishers use SVG files to bypass email filters, tricking users into entering credentials.
- Immediate Action: Verify all voicemail notifications and educate employees on spotting phishing attempts.
- Technology Solutions: Implement multi-factor authentication (MFA) and advanced email filtering.
- Long-term Strategy: Develop a comprehensive cybersecurity training program and incident response plan.
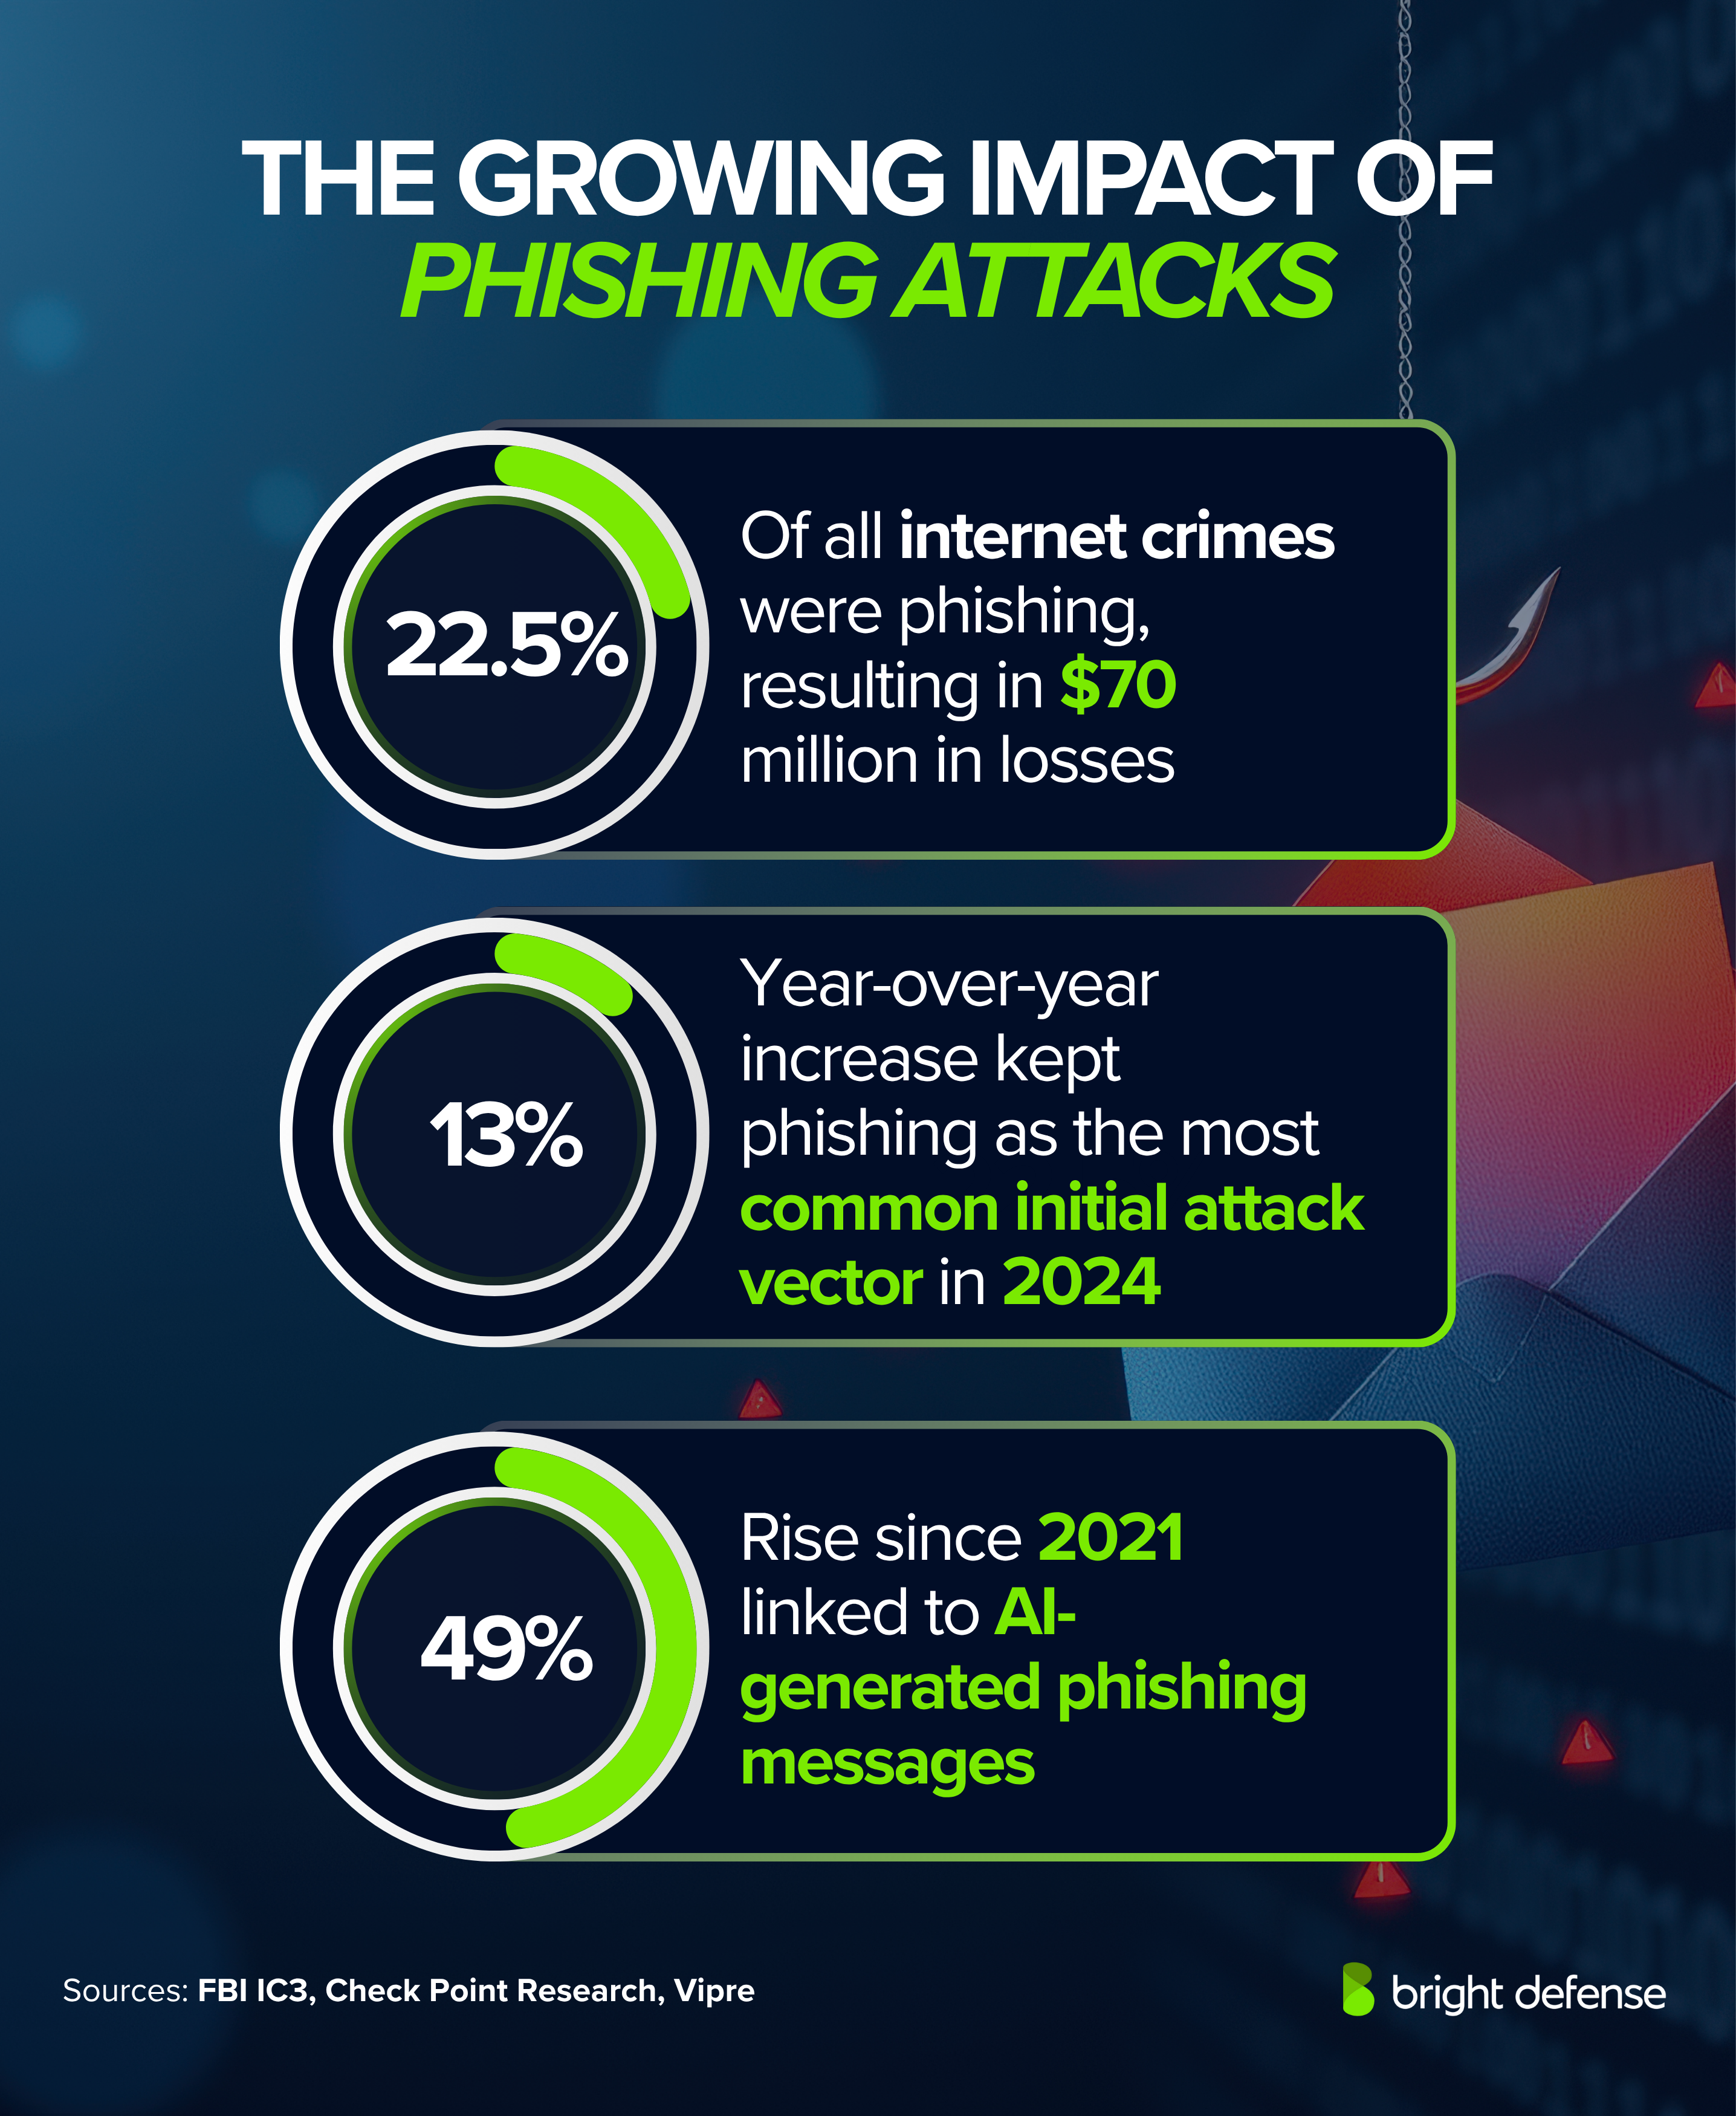
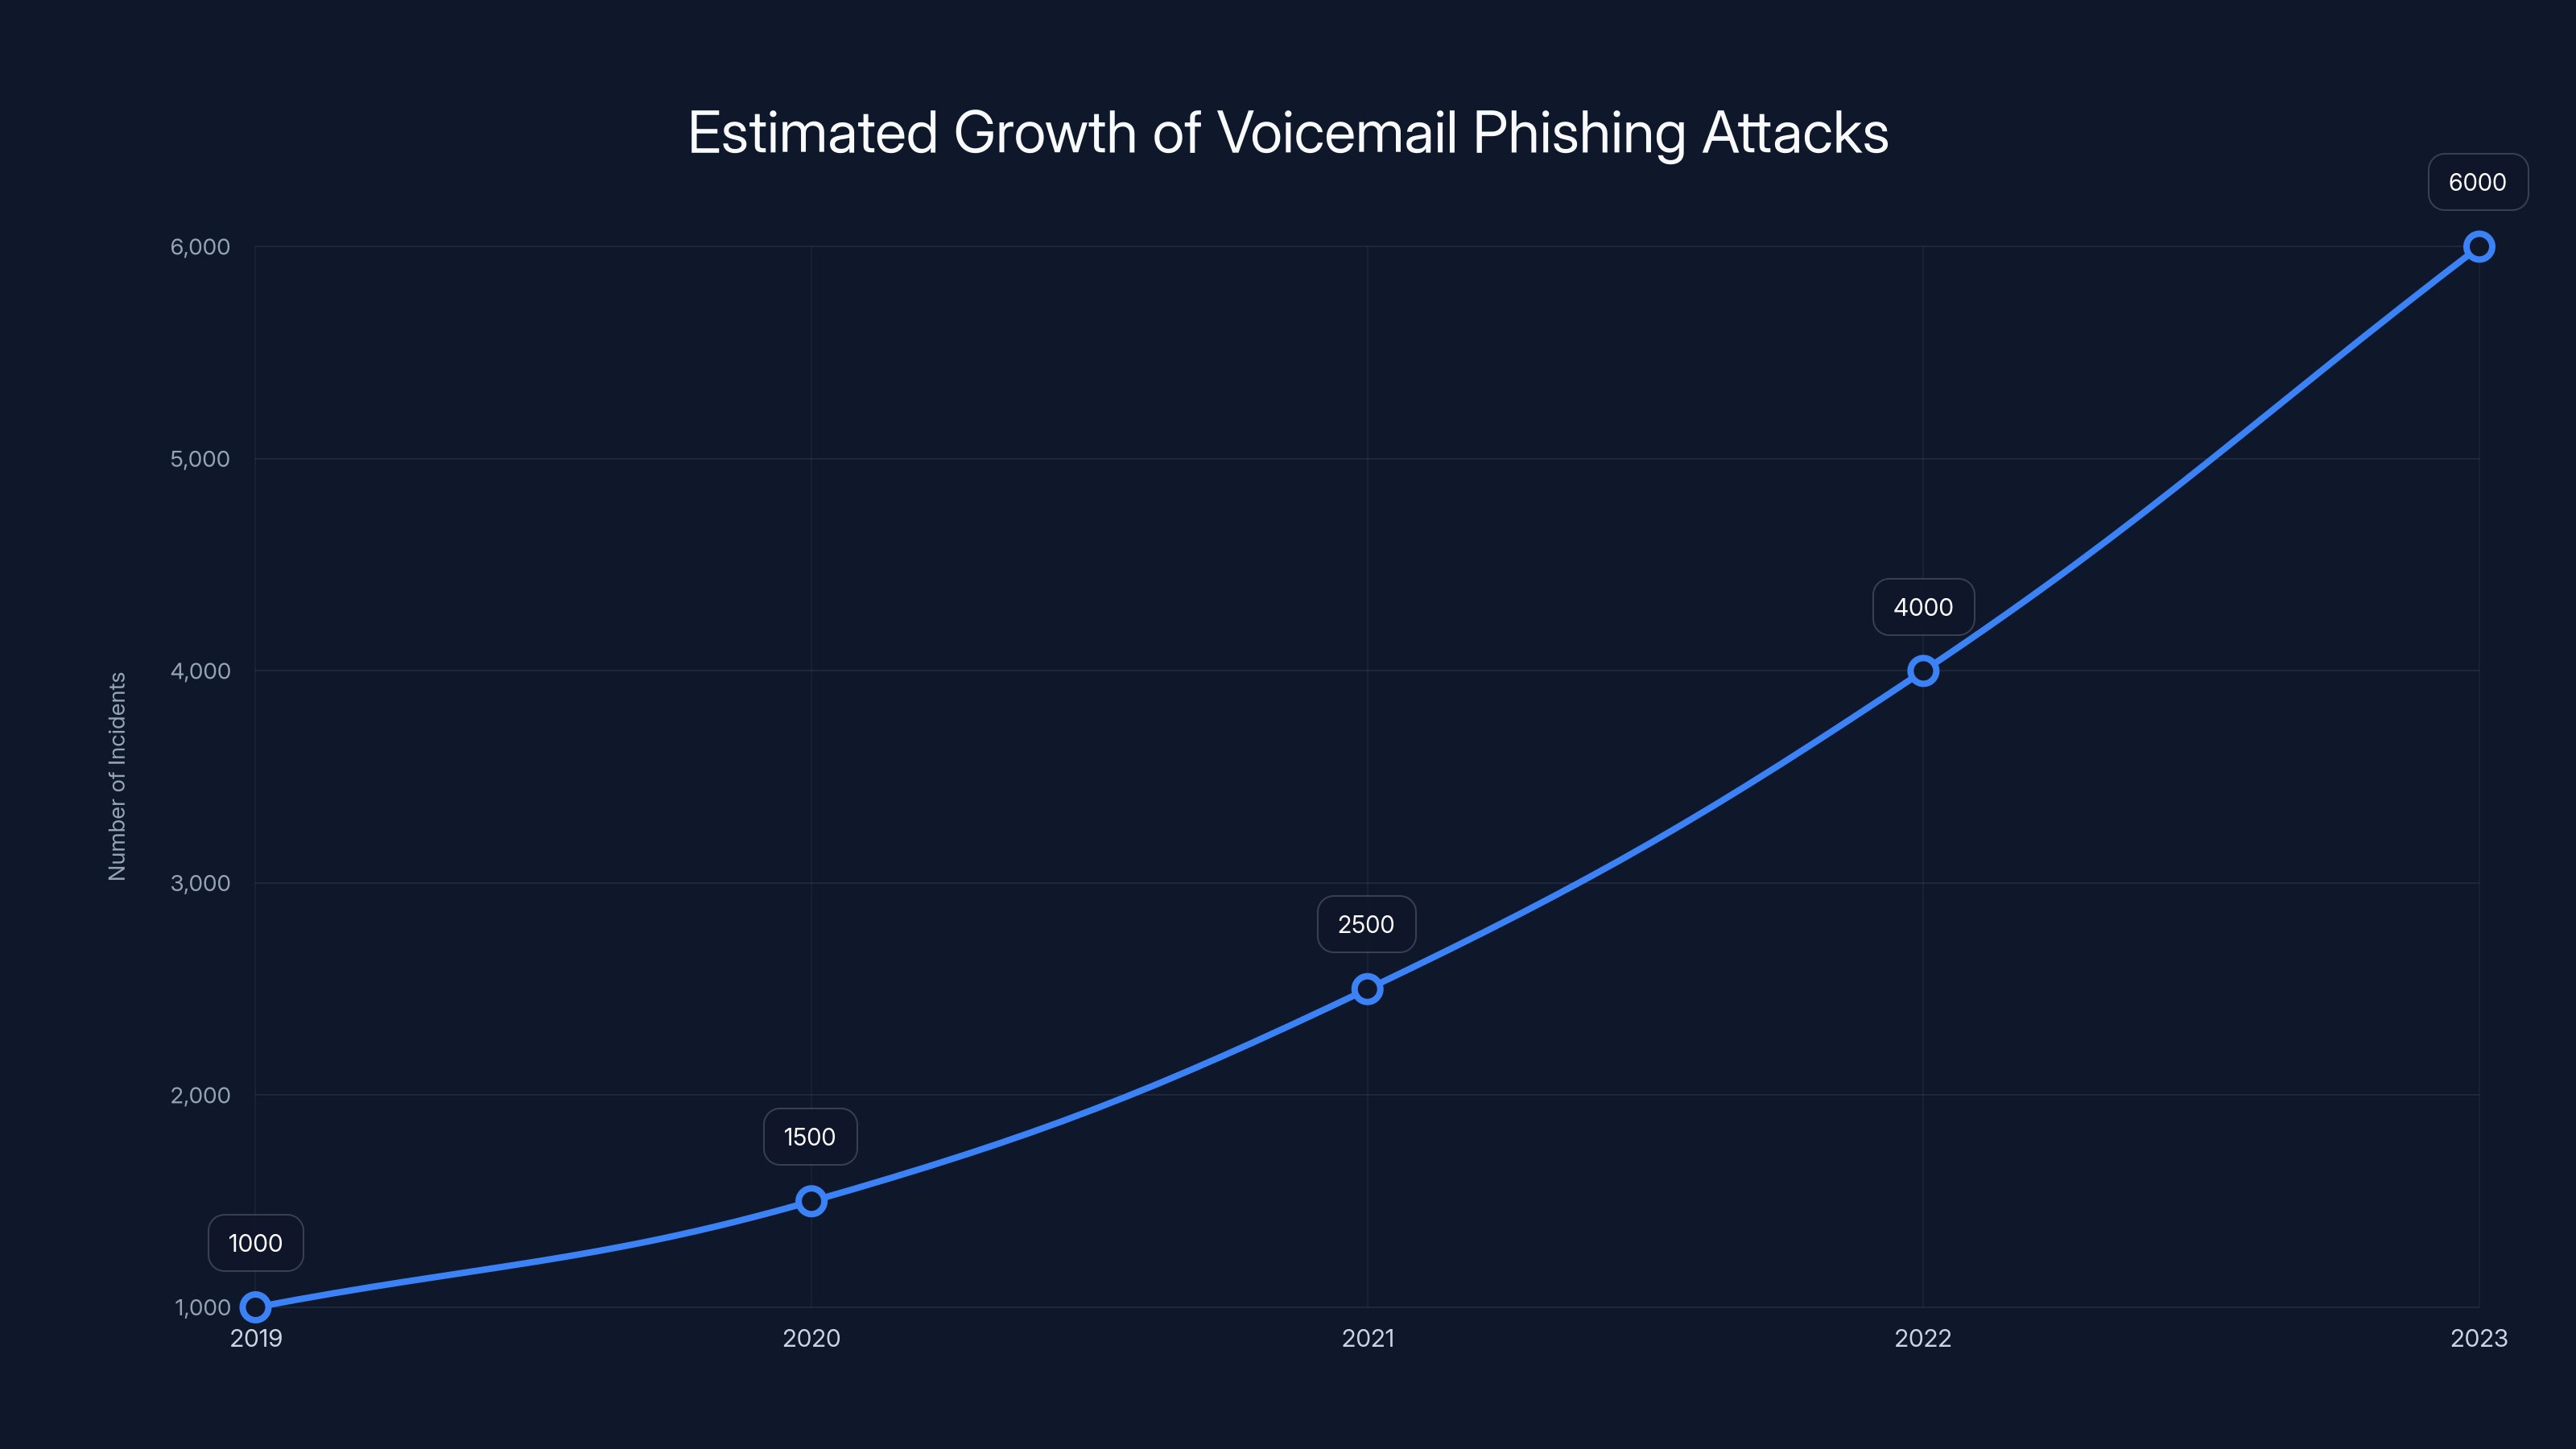
The estimated number of voicemail phishing attacks has shown a significant upward trend from 2019 to 2023, highlighting the increasing sophistication and prevalence of these attacks. (Estimated data)
The Rise of Voicemail Phishing Attacks
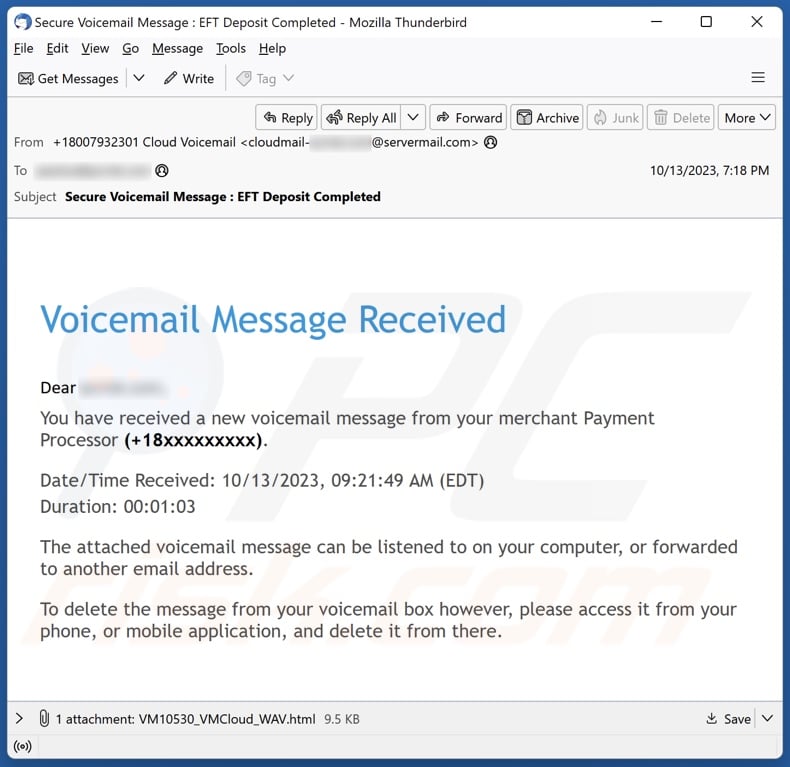
Voicemail phishing attacks, also known as vishing, have become increasingly sophisticated. The attackers send emails that mimic legitimate voicemail notifications, often including attachments or links that appear to be genuine. When unsuspecting users click these links, they are redirected to a malicious site that captures their login credentials.
How the Attack Works
Here's a typical flow of a voicemail phishing attack:
- Email Delivery: The victim receives an email that looks like a voicemail notification.
- Deceptive Content: The email contains a link or attachment, often disguised as an audio file or transcript.
- Credential Harvesting: Clicking the link leads the user to a fake login page imitating a legitimate service.
- Data Capture: The user enters their credentials, which are captured by the attacker.
Why Voicemail Phishing is Effective
What makes these attacks so effective is their ability to blend in with normal business communications. Voicemail notifications are a common part of many corporate workflows, making it easy for attackers to exploit trust.
Additionally, the use of SVG (Scalable Vector Graphics) files allows attackers to bypass traditional email filters. SVG files can contain scripts that redirect users to malicious sites, often undetected by standard security measures.
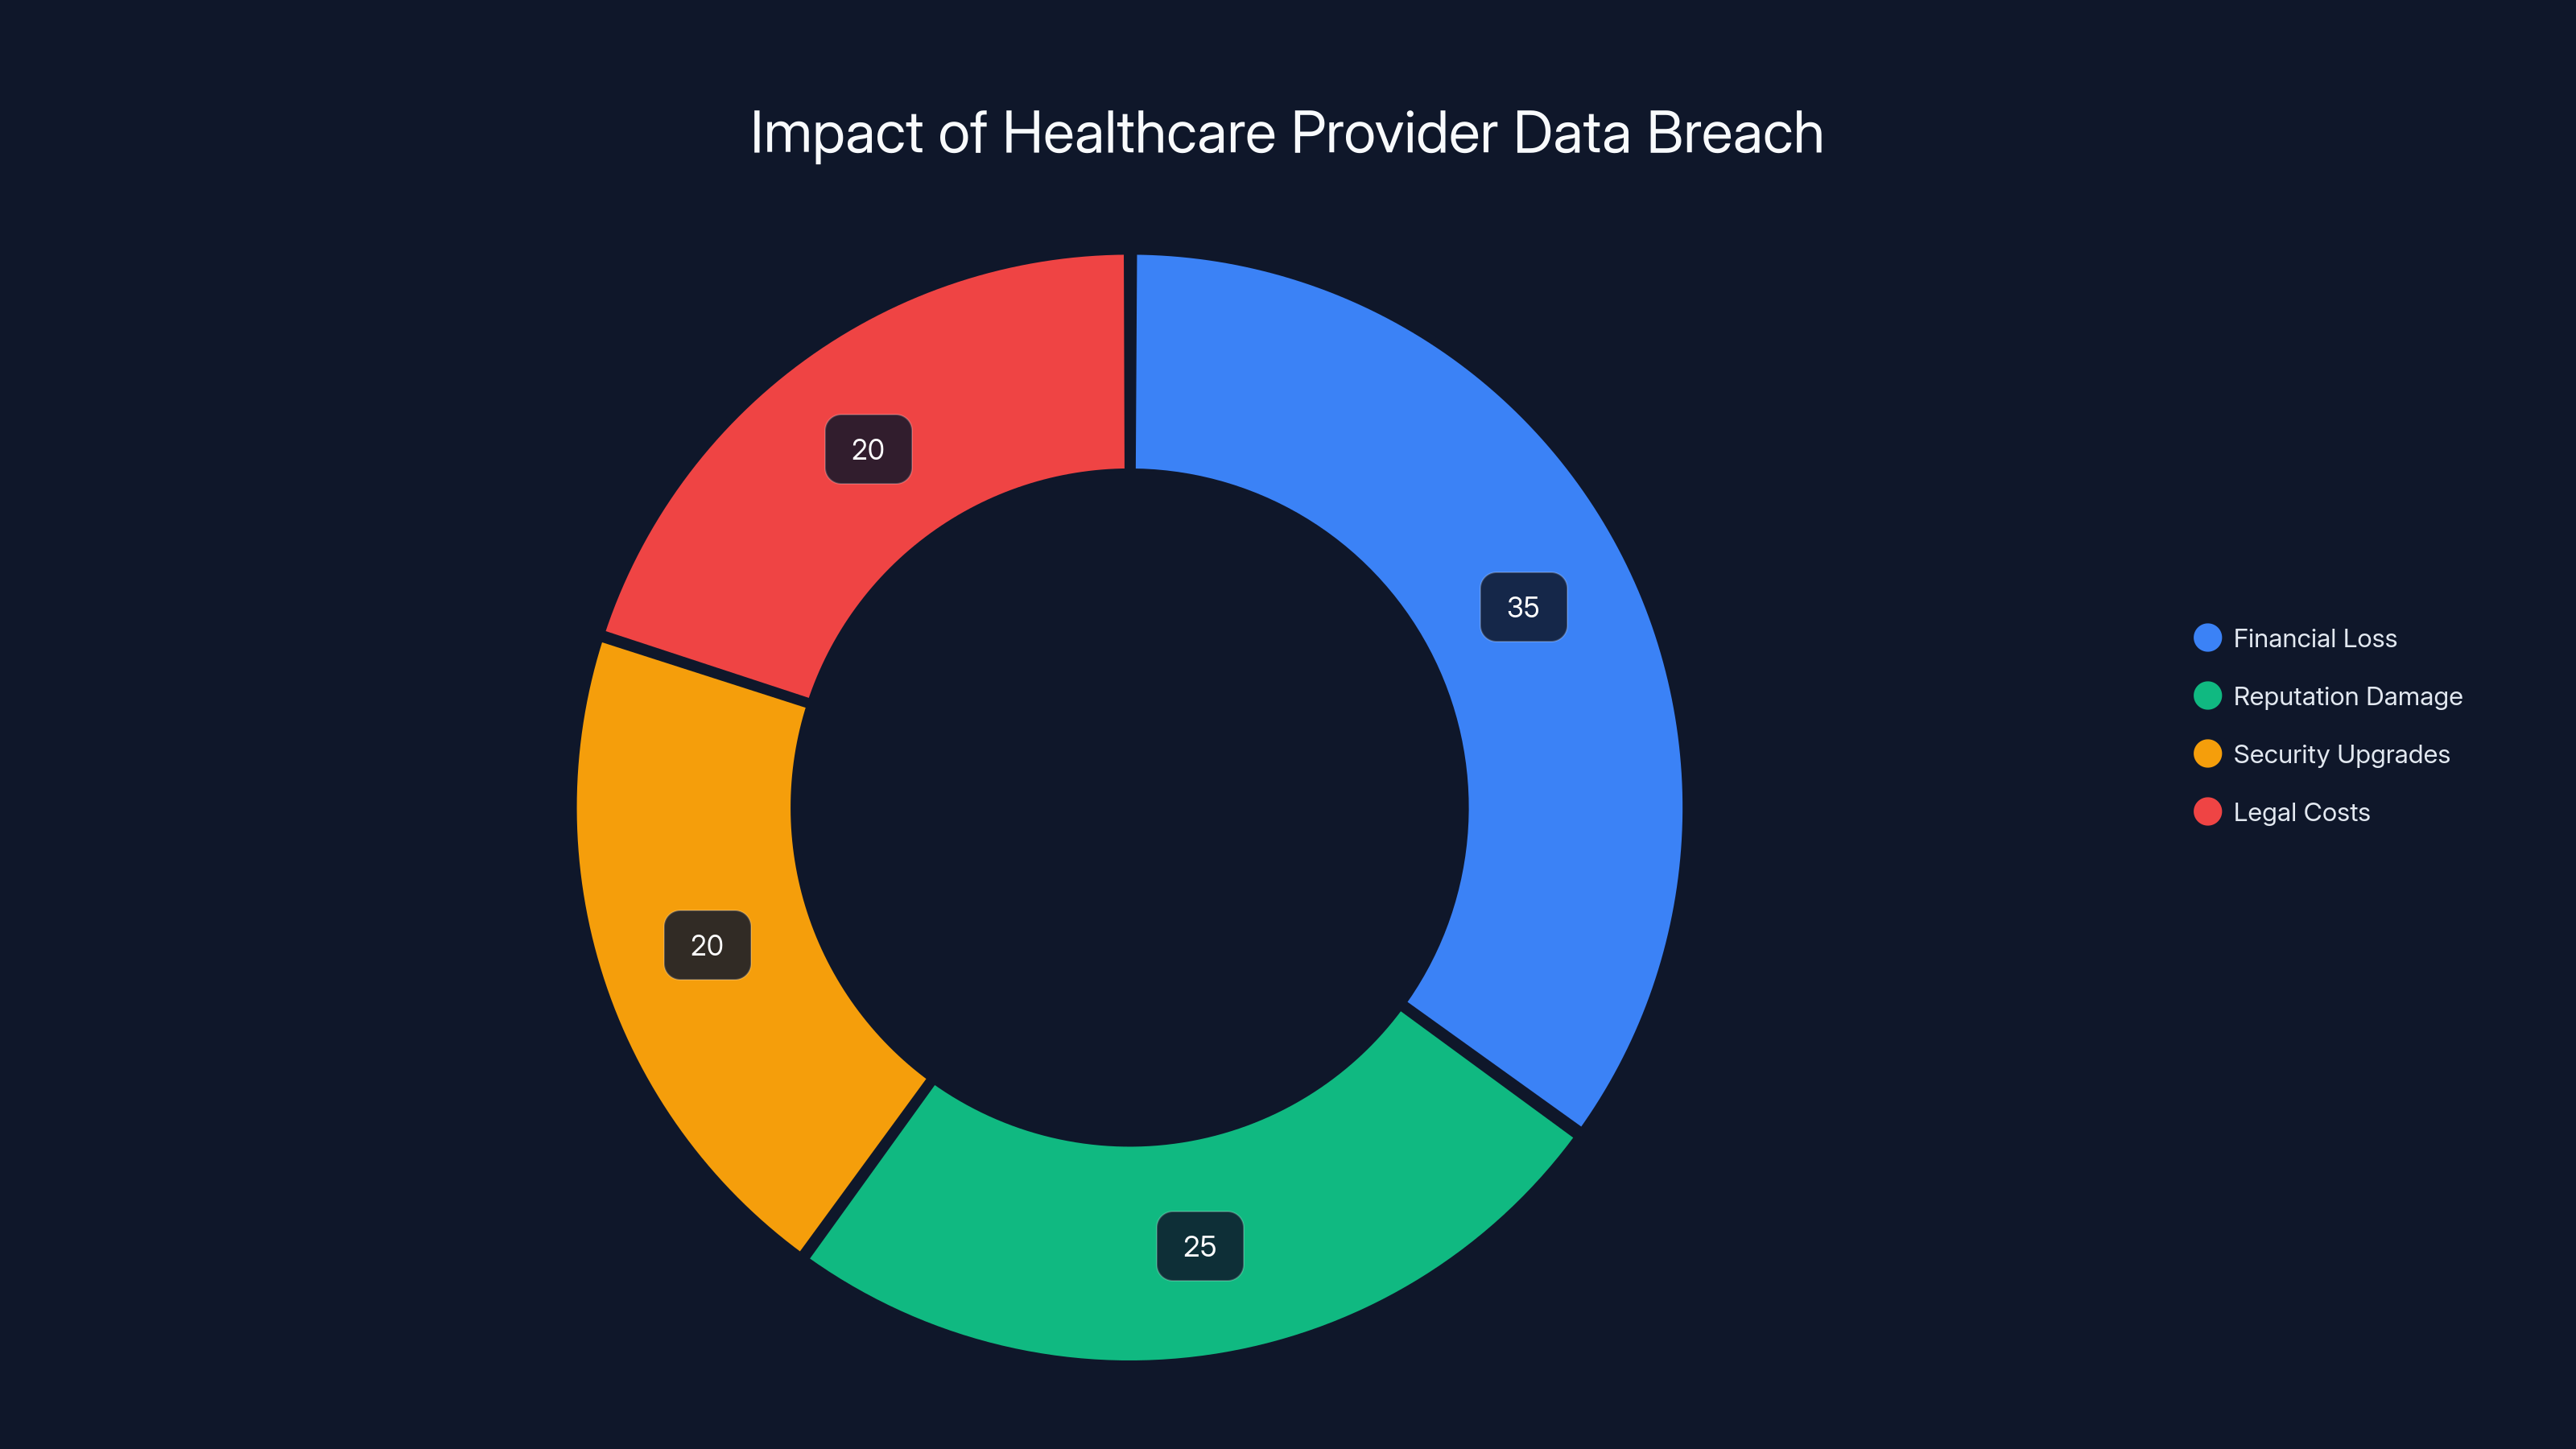
The healthcare provider breach led to financial losses, reputation damage, and costly security upgrades. Estimated data shows financial loss as the largest impact.
Real-World Consequences
The impact of a successful phishing attack can be devastating. For instance, a major healthcare provider recently fell victim to a voicemail phishing scam, resulting in the compromise of sensitive patient data. This breach led to not only financial losses but also a significant blow to the organization's reputation.
Case Study: Healthcare Provider Breach
- Incident: A well-known healthcare provider received a wave of fake voicemail emails.
- Outcome: Over 10,000 patient records were accessed illicitly.
- Response: The provider had to notify affected individuals and implement costly security upgrades.
Protecting Your Organization
Immediate Steps
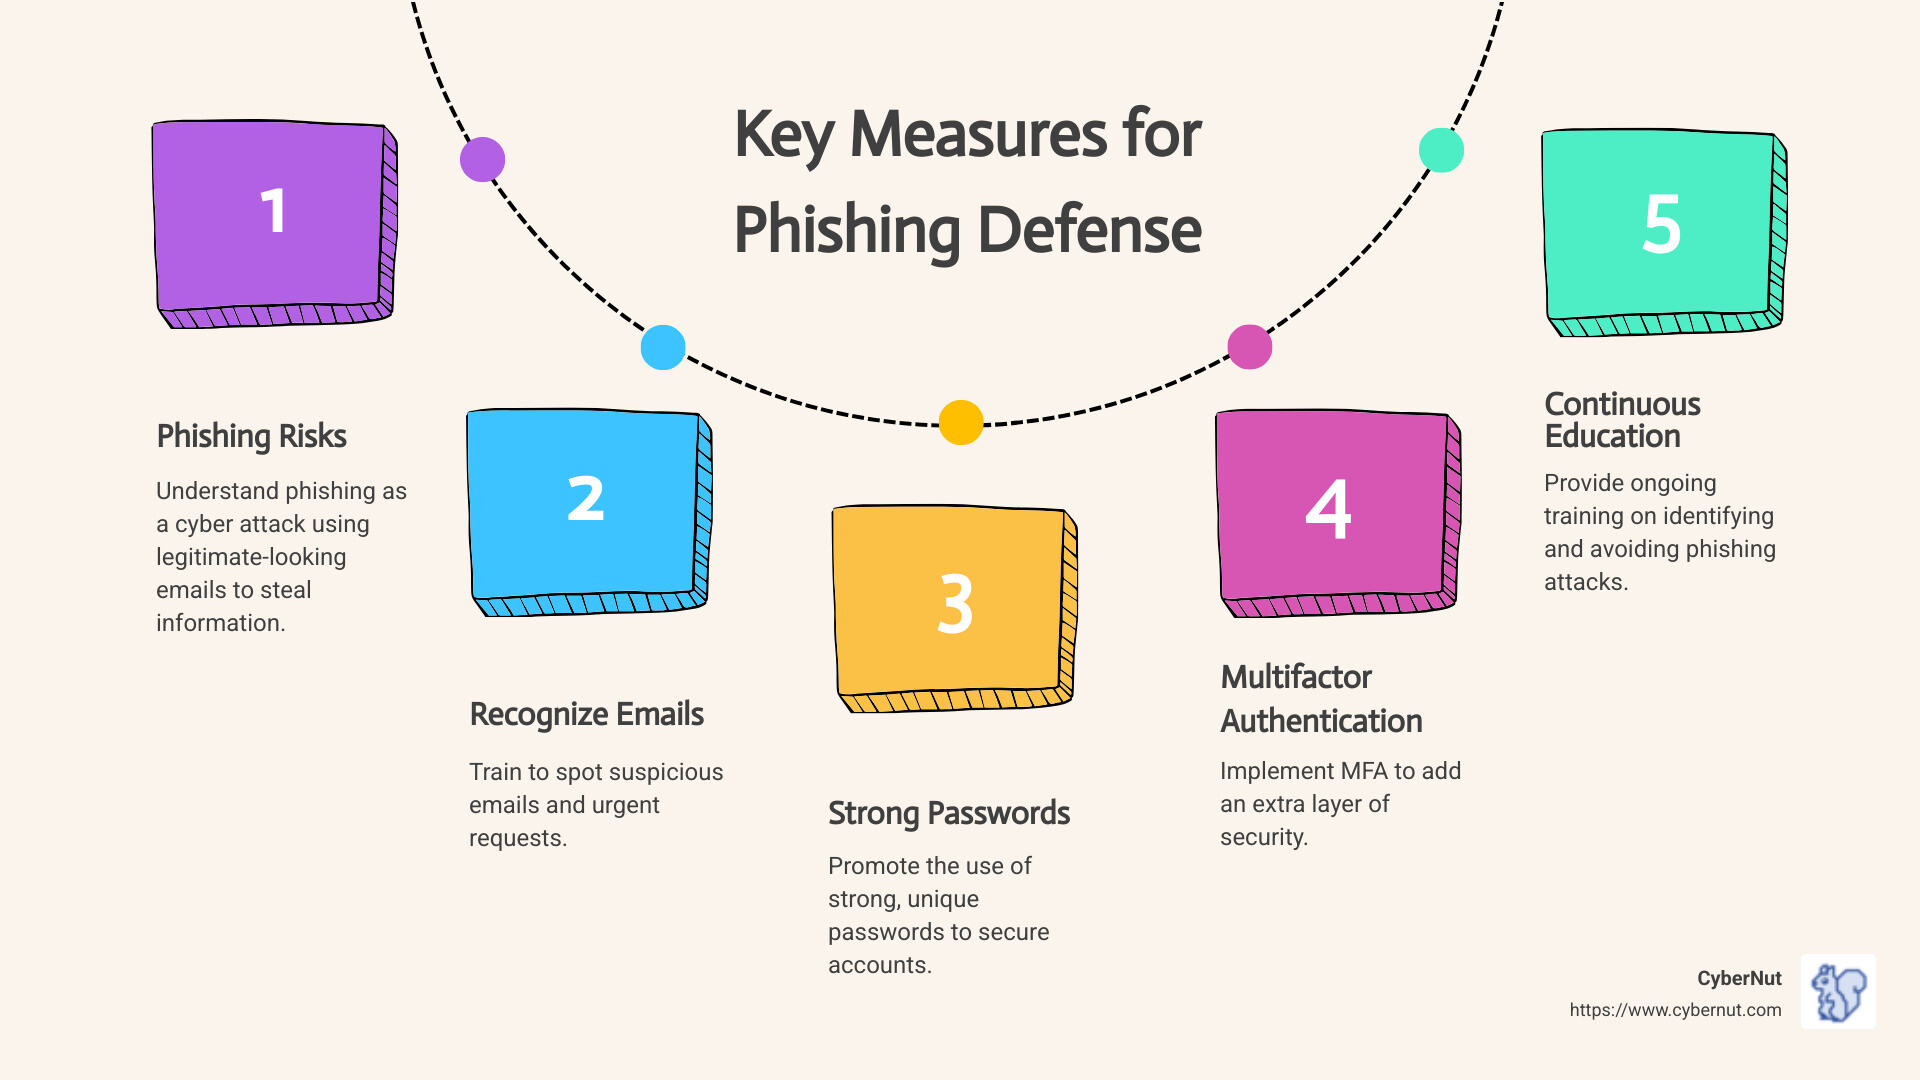
- Verify Sources: Always verify voicemail notifications by checking with the sender directly before clicking on any links or downloading attachments.
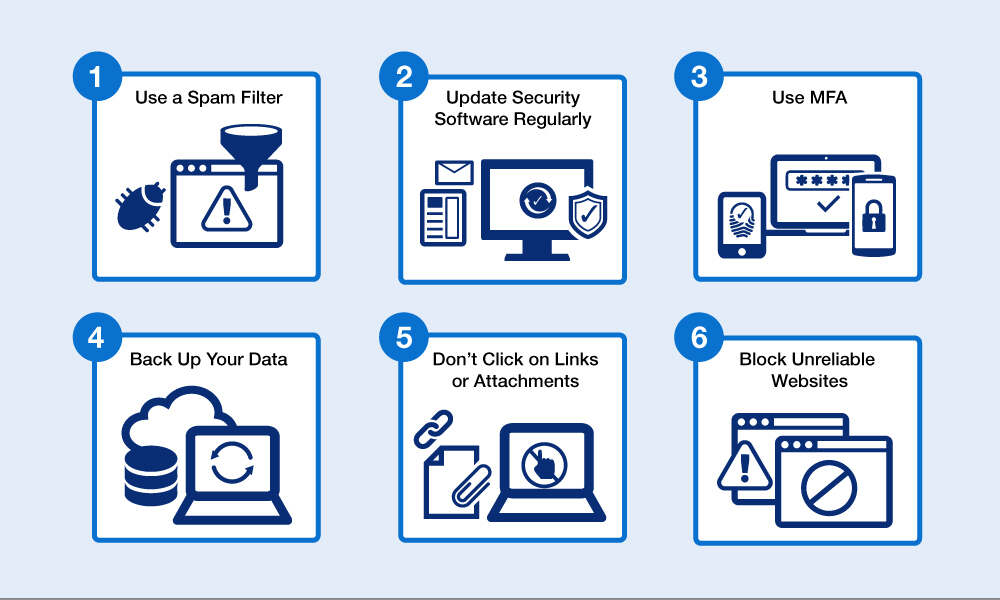
- Employee Training: Conduct regular training sessions to educate employees about the signs of phishing attacks and the importance of vigilance.
Long-Term Security Measures
- Multi-Factor Authentication (MFA): Implement MFA across all accounts to add an extra layer of security. Even if credentials are compromised, MFA can prevent unauthorized access.
- Advanced Email Filtering: Use email security solutions that can detect and block phishing attempts, including those using SVG files.
- Incident Response Plan: Develop a comprehensive plan outlining steps to take in the event of a phishing attack. This should include identifying the breach, containing it, and communicating with affected parties.
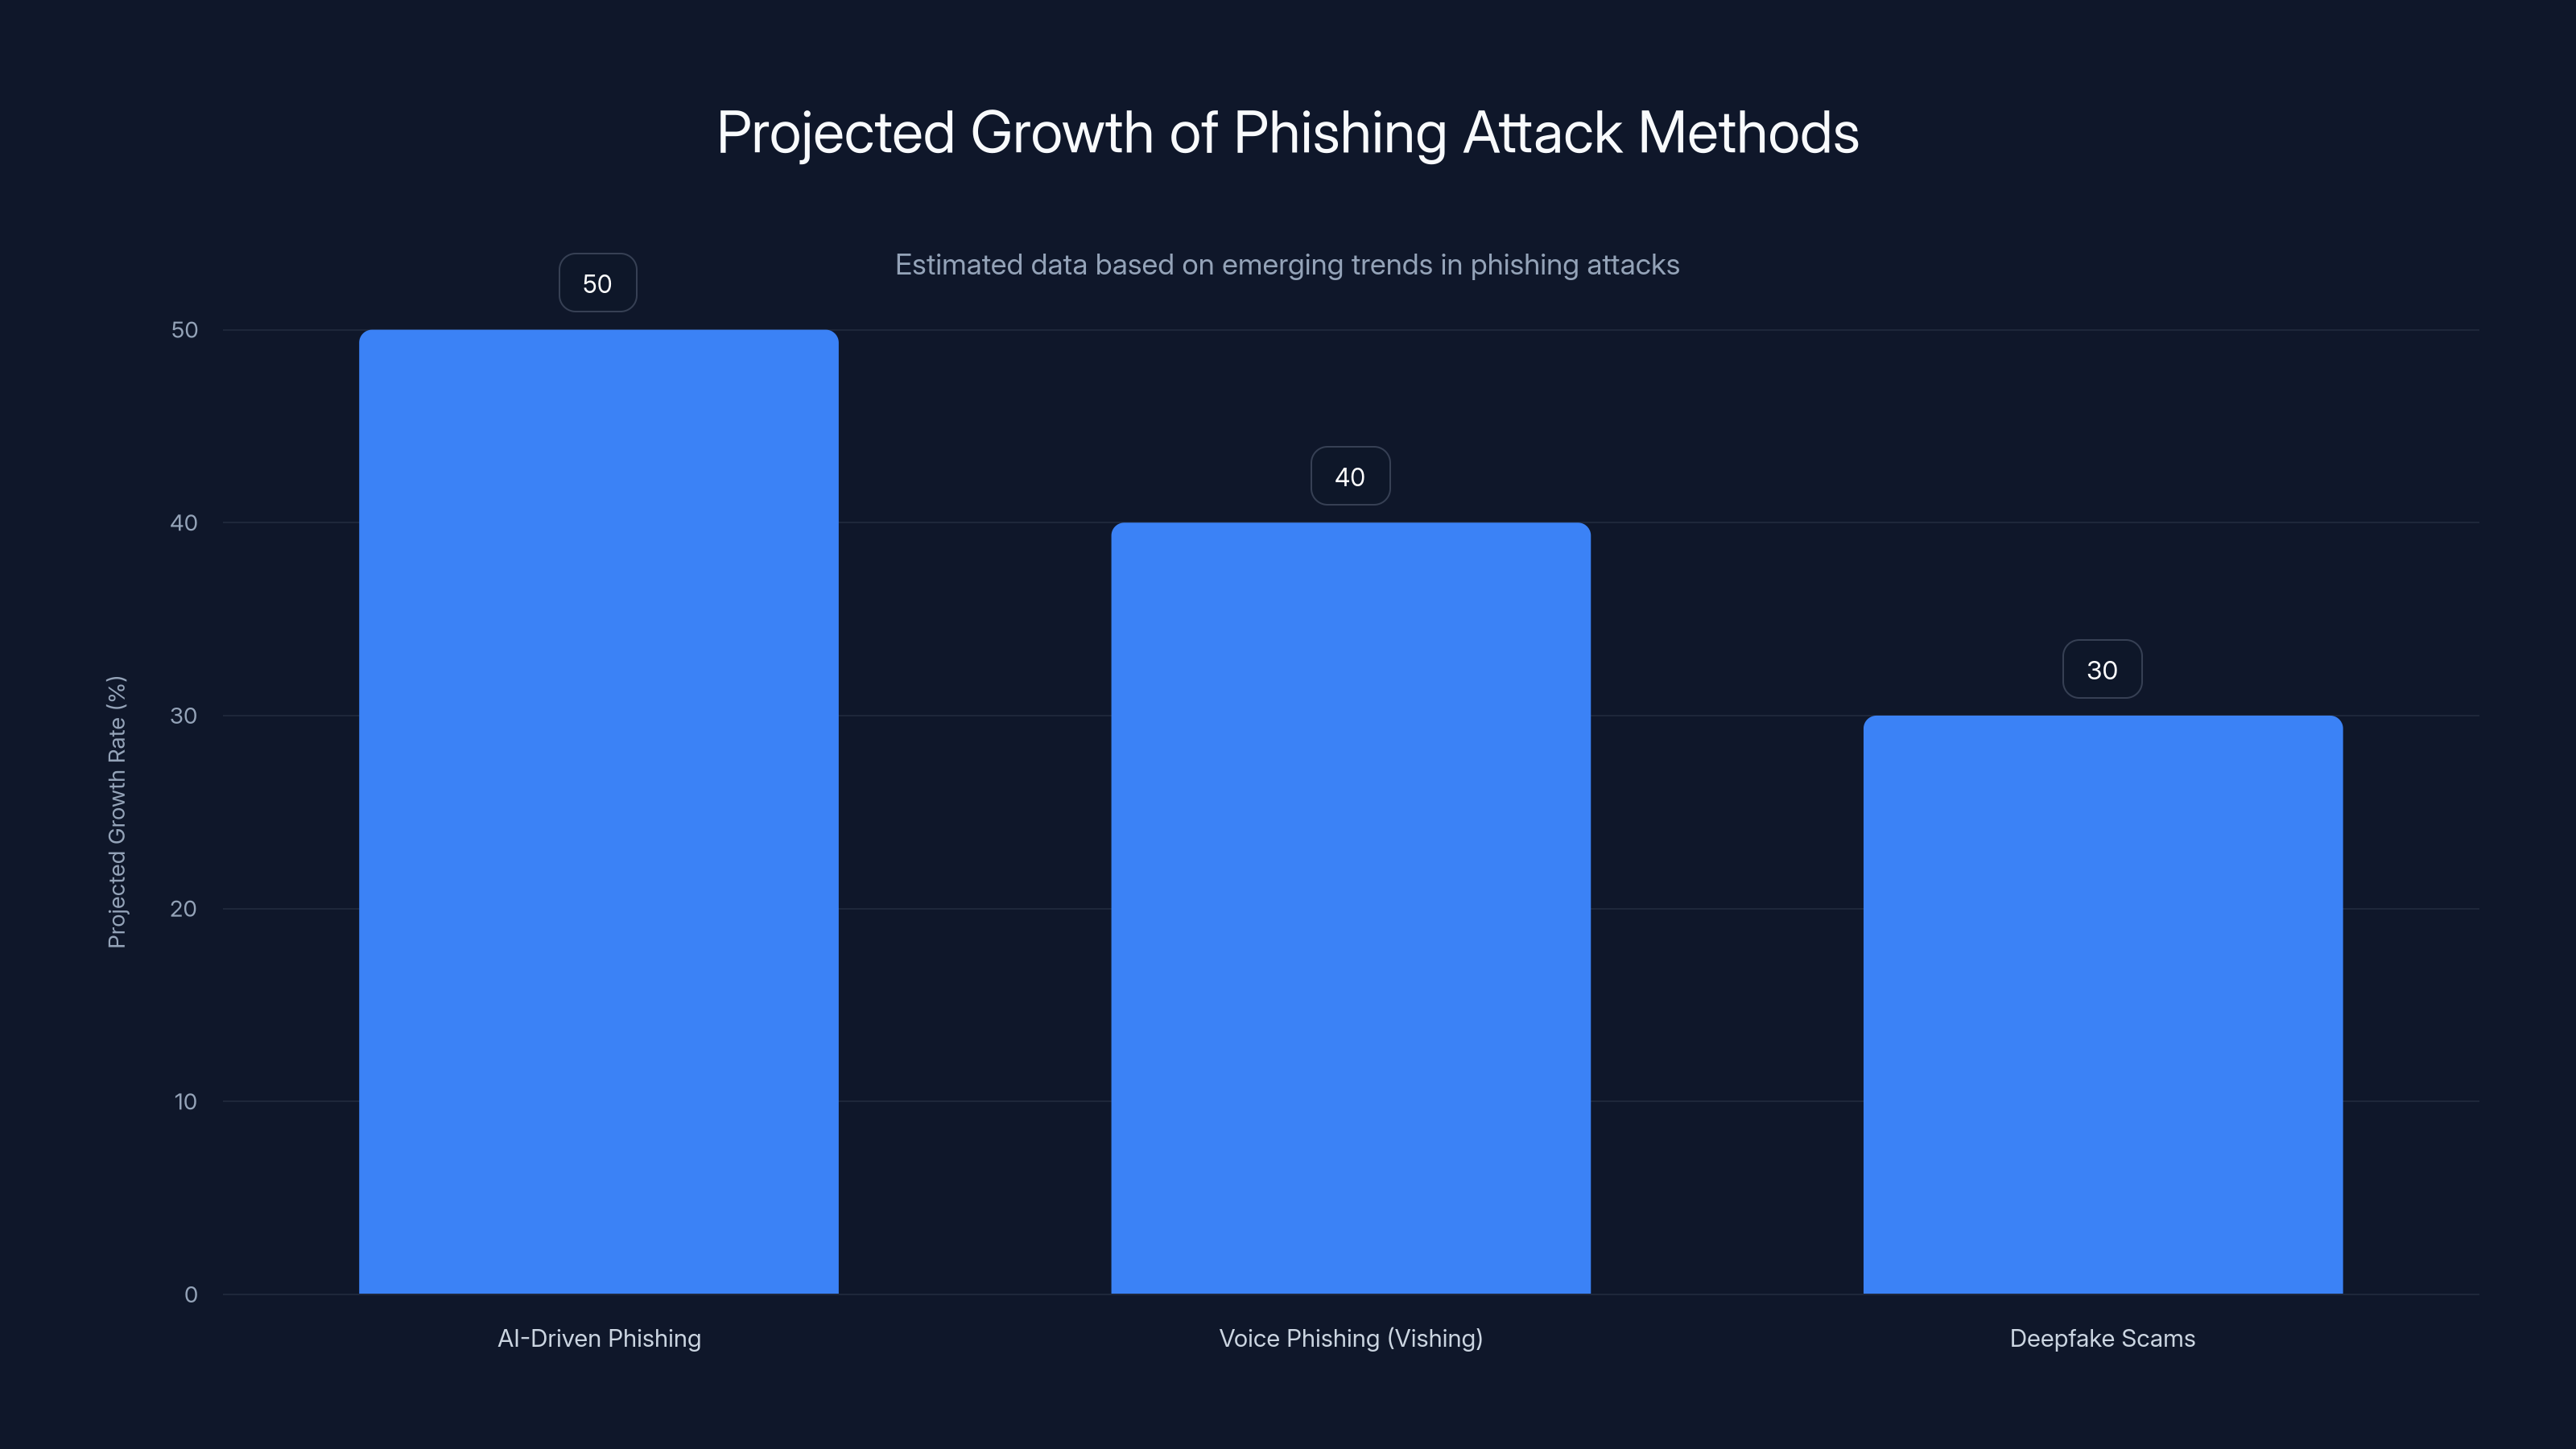
AI-driven phishing is expected to grow the fastest, with a projected growth rate of 50%, followed by voice phishing at 40% and deepfake scams at 30%. Estimated data.
Common Pitfalls and Solutions
Pitfall #1: Overconfidence in Technology
Many organizations rely too heavily on technology to protect against phishing, neglecting the human element. Technology alone isn't enough; employees must be trained to recognize and report suspicious activity.
Solution: Regular Simulated Phishing Exercises
Conduct simulated phishing attacks to test your organization's readiness and identify areas for improvement. This hands-on approach helps reinforce training and keeps employees alert.
Pitfall #2: Lack of Communication
In many cases, organizations fail to communicate effectively during a phishing incident, leading to confusion and delayed responses.
Solution: Clear Communication Channels
Establish clear communication protocols for reporting and responding to phishing incidents. Ensure all employees know whom to contact and what steps to take if they suspect a phishing attempt.
Future Trends in Phishing Attacks
As technology evolves, so too do the methods used by cybercriminals. Here are some trends to watch for in phishing attacks:
Trend #1: AI-Driven Phishing
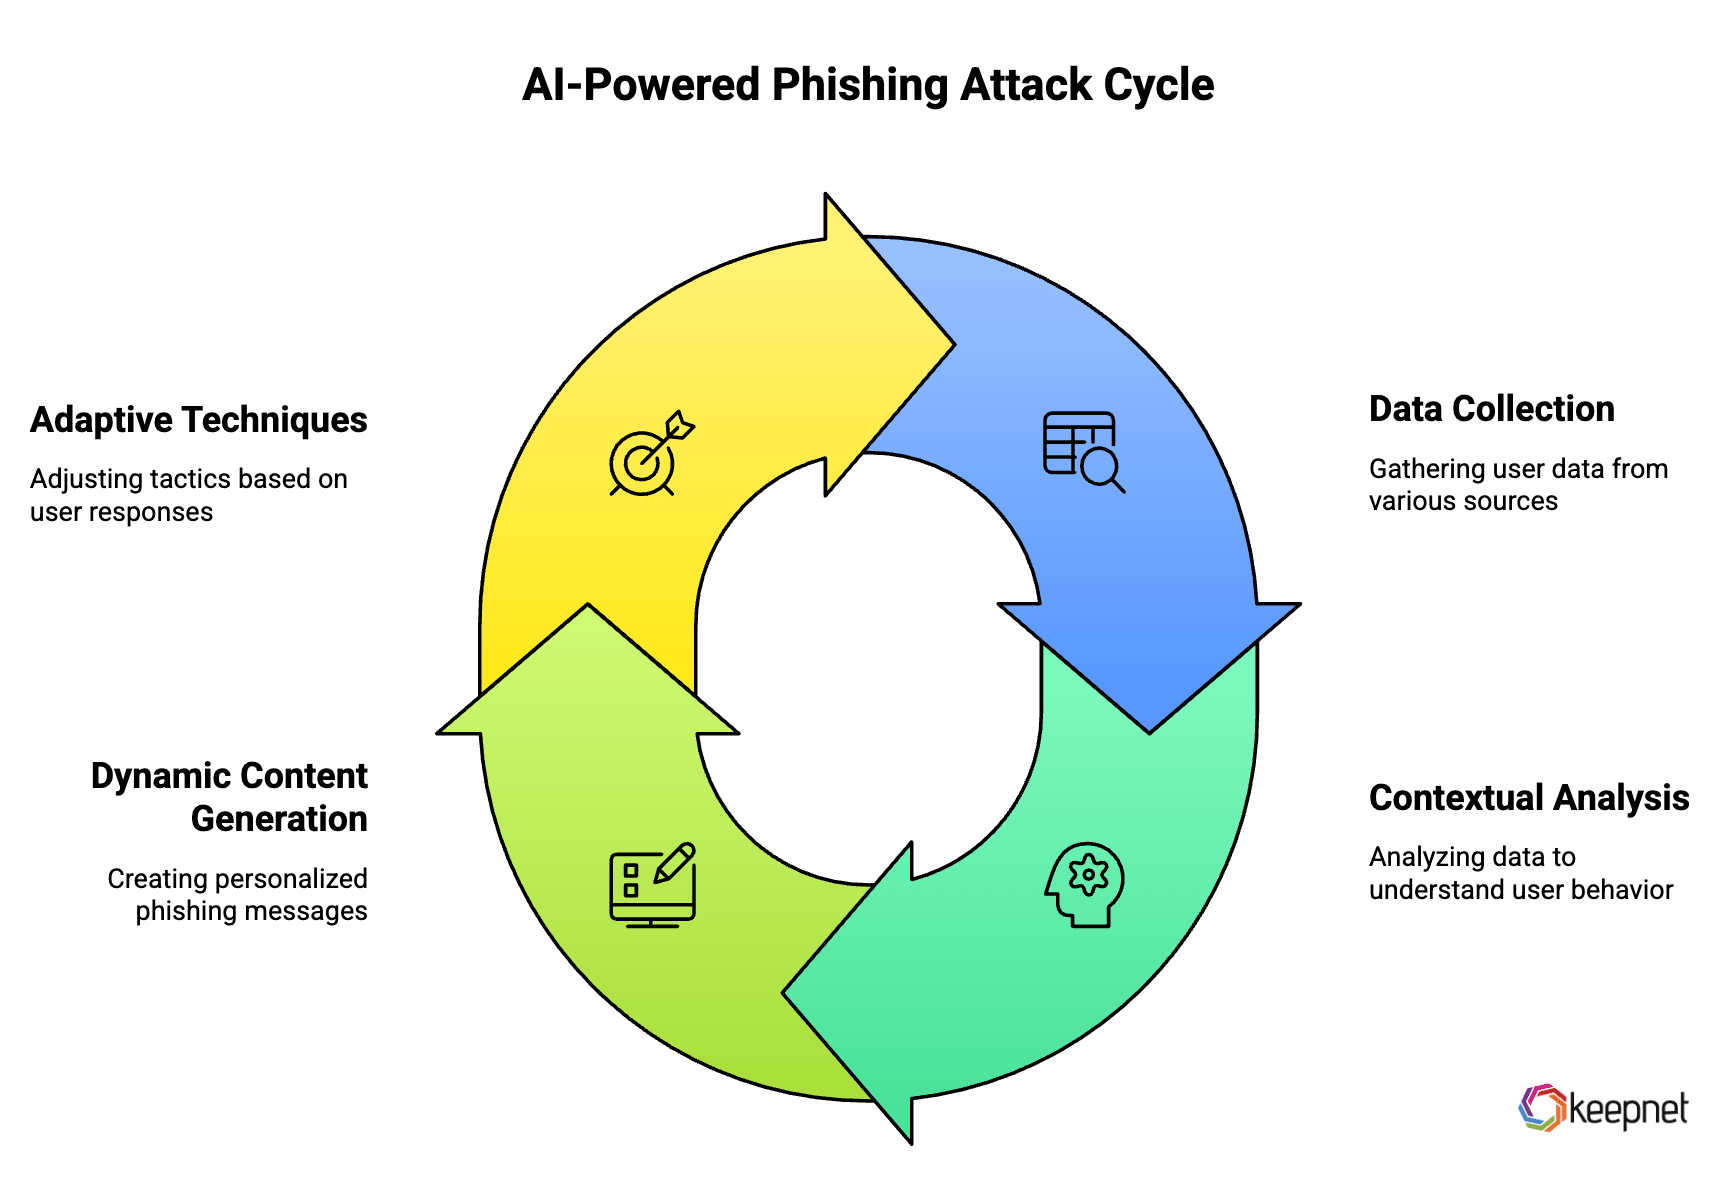
Attackers are increasingly using AI and machine learning to craft more convincing phishing emails. These tools enable them to analyze user behavior and create personalized lures that are harder to detect.
Trend #2: Voice Phishing (Vishing)
As organizations invest in voice recognition technology, attackers are turning to voice phishing, or vishing. This method involves using automated calls to trick users into revealing sensitive information.
Trend #3: Deepfake Scams
Deepfakes, which use AI to create realistic fake videos, are emerging as a new phishing threat. Attackers can create videos of executives asking for sensitive information or wire transfers, making it challenging to discern real from fake.
Recommendations for the Future
To stay ahead of these threats, organizations must adopt a proactive approach to cybersecurity. Here are some recommendations:
- Invest in AI-Based Security Tools: These tools can help detect and respond to sophisticated phishing attempts in real-time.
- Continuous Education: Regularly update training materials to include the latest phishing techniques and trends.
- Collaborate with Industry Peers: Share information and best practices with other organizations to enhance collective security.
Conclusion
Voicemail phishing attacks are just one of many evolving threats in the cybersecurity landscape. By understanding the tactics used by attackers and implementing robust security measures, organizations can protect themselves from the potentially devastating consequences of credential theft. Remember, cybersecurity is not a one-time effort but an ongoing process that requires vigilance and adaptation.
FAQ
What is voicemail phishing?
Voicemail phishing involves sending fake voicemail notifications to trick users into entering their credentials on a malicious site.
How can I recognize a phishing email?
Look for suspicious elements such as unexpected attachments, links with unusual URLs, and requests for sensitive information.
What should I do if I fall victim to a phishing attack?
Immediately change your passwords, enable MFA, and report the incident to your IT department or security team.
Why is multi-factor authentication important?
MFA adds an extra layer of security, making it much harder for attackers to access accounts even if they have the password.
How do SVG files bypass email filters?
SVG files can contain scripts that execute when the file is opened, allowing attackers to redirect users to malicious sites without detection.
How often should we conduct phishing training?
At least quarterly, with additional training following any major phishing incidents or updates in phishing tactics.
What technologies can help prevent phishing attacks?
Email filtering solutions, AI-based security tools, and MFA are all effective in mitigating phishing risks.
Can deepfake technology be used in phishing attacks?
Yes, attackers can use deepfakes to create convincing fake videos of executives to trick employees into revealing sensitive information.
Key Takeaways
- Voicemail phishing is a rising threat affecting thousands of organizations.
- SVG files are used by attackers to bypass email security filters.
- Multi-factor authentication (MFA) is crucial in preventing unauthorized access.
- Regular employee training and simulated phishing exercises enhance security awareness.
- AI-driven phishing and deepfake scams are emerging threats to watch.
Related Articles
- How to Safeguard Against Sophisticated Impersonation and Passkey Phishing Attacks [2025]
- Understanding the RubyGems and OpenAI Incident: A Deep Dive [2025]
- Anthropic's Cybersecurity Challenges and the Future of AI Security [2025]
- Technology Sovereignty: Keeping Control, Not Geography [2025]
- Skullcandy Earbuds Bluetooth Security Flaw: What You Need to Know [2025]
- Understanding and Combatting Deepfake Exploitation: A Comprehensive Guide [2025]


