
Unraveling AI Security: How Researchers Used Anthropic's Claude to Breach Open AI [2025]
Artificial intelligence (AI) is evolving at a breakneck pace, and with it comes a new frontier in cybersecurity. Recently, a team of researchers used Anthropic's Claude, an AI model, to successfully breach Open AI's systems. This incident has brought to light the vulnerabilities inherent in AI systems and the pressing need for robust security protocols. In this article, we'll explore the details of this breach, the methods used, and the broader implications for AI security.
TL; DR
- AI Vulnerabilities: Researchers exploited vulnerabilities in Open AI using Anthropic's Claude.
- Security Implications: This breach highlights the need for advanced AI security measures.
- Future Trends: AI security will become increasingly critical as AI systems grow more complex.
- Best Practices: Organizations must implement stringent security protocols and continuous monitoring.
- Industry Impact: AI security failures can have widespread repercussions across industries.
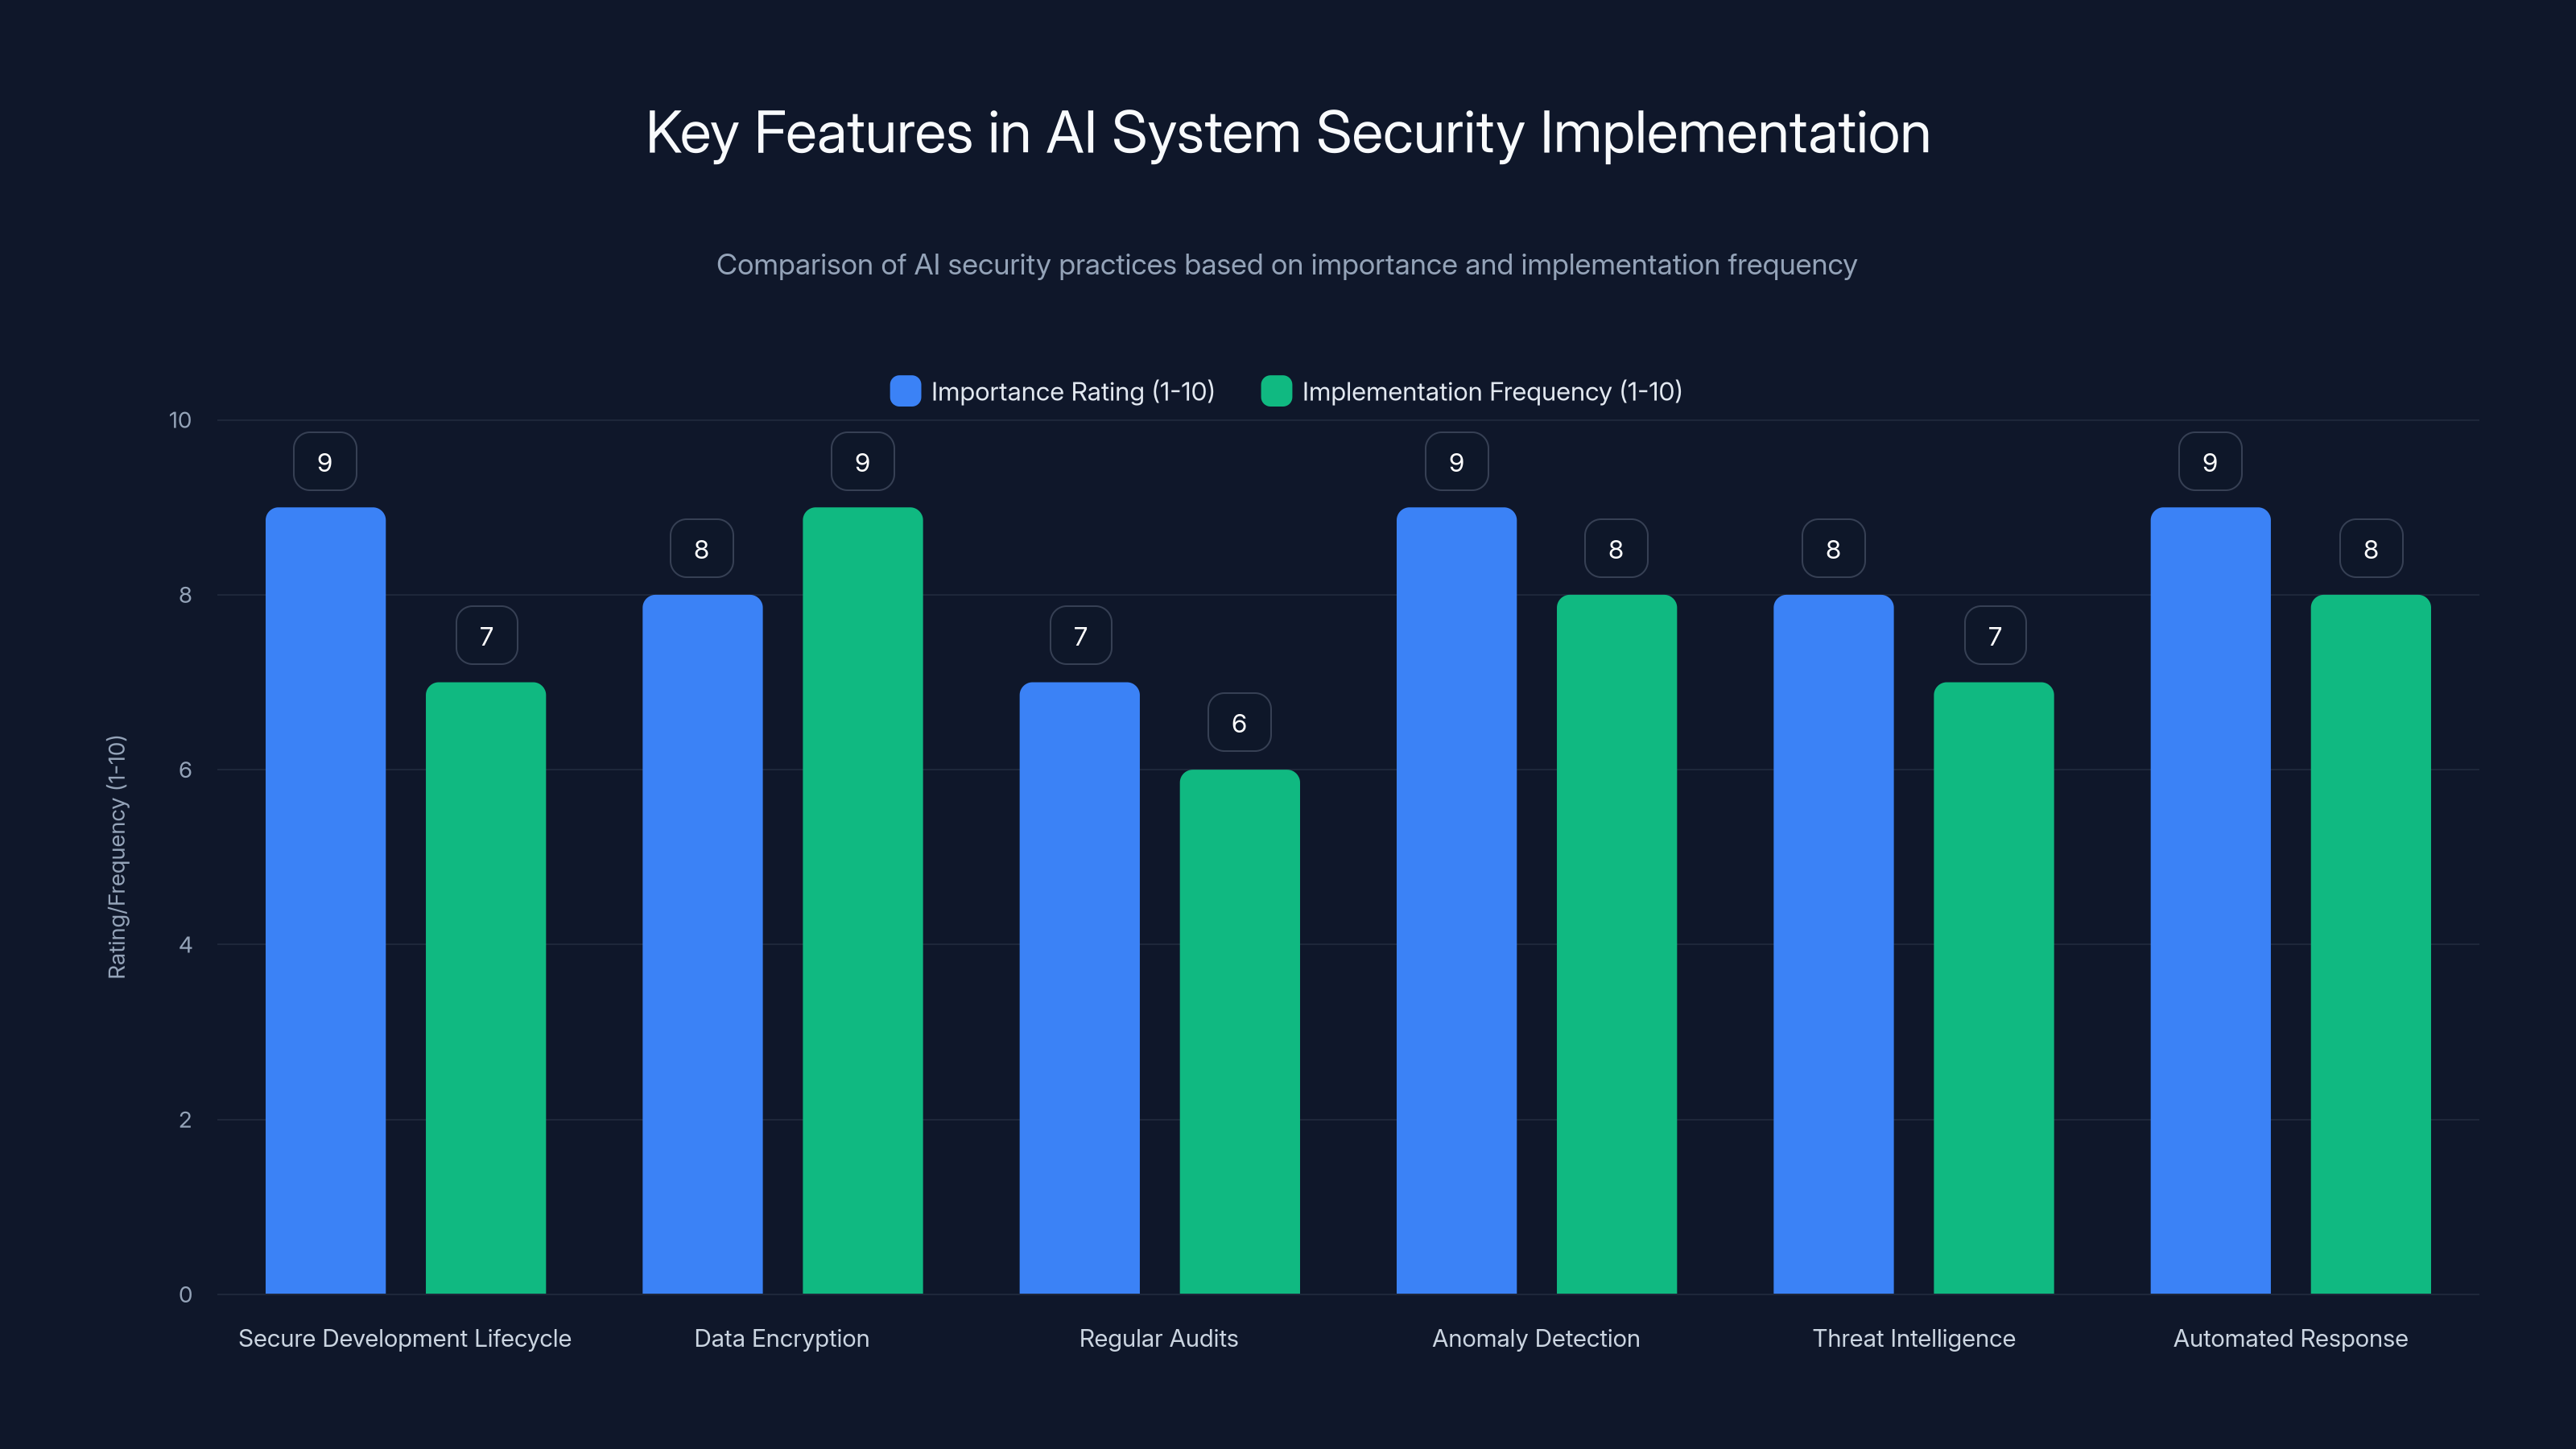
Secure Development Lifecycle and Automated Response are rated highly in importance and implementation frequency, indicating their critical role in AI security systems. Estimated data.
Introduction to AI Security
As AI technologies integrate deeper into our daily lives and critical infrastructure, the importance of securing these systems cannot be overstated. AI models, while powerful, are vulnerable to exploitation. Whether through data manipulation, model inversion attacks, or other sophisticated techniques, the security of AI systems is an emerging field that demands attention.
The Breach: A Case Study
In a recent incident, independent security researchers employed Anthropic's AI model, Claude, to infiltrate Open AI's systems. This breach, which was part of an Open AI bug bounty program, involved chaining two critical vulnerabilities that allowed unauthorized access to multiple Open AI employee Chat GPT accounts. By gaining this access, the researchers could explore the company's software infrastructure, revealing potential weaknesses.
Key Takeaway: The breach underscores the potential for AI models to be both tools and targets in cybersecurity.
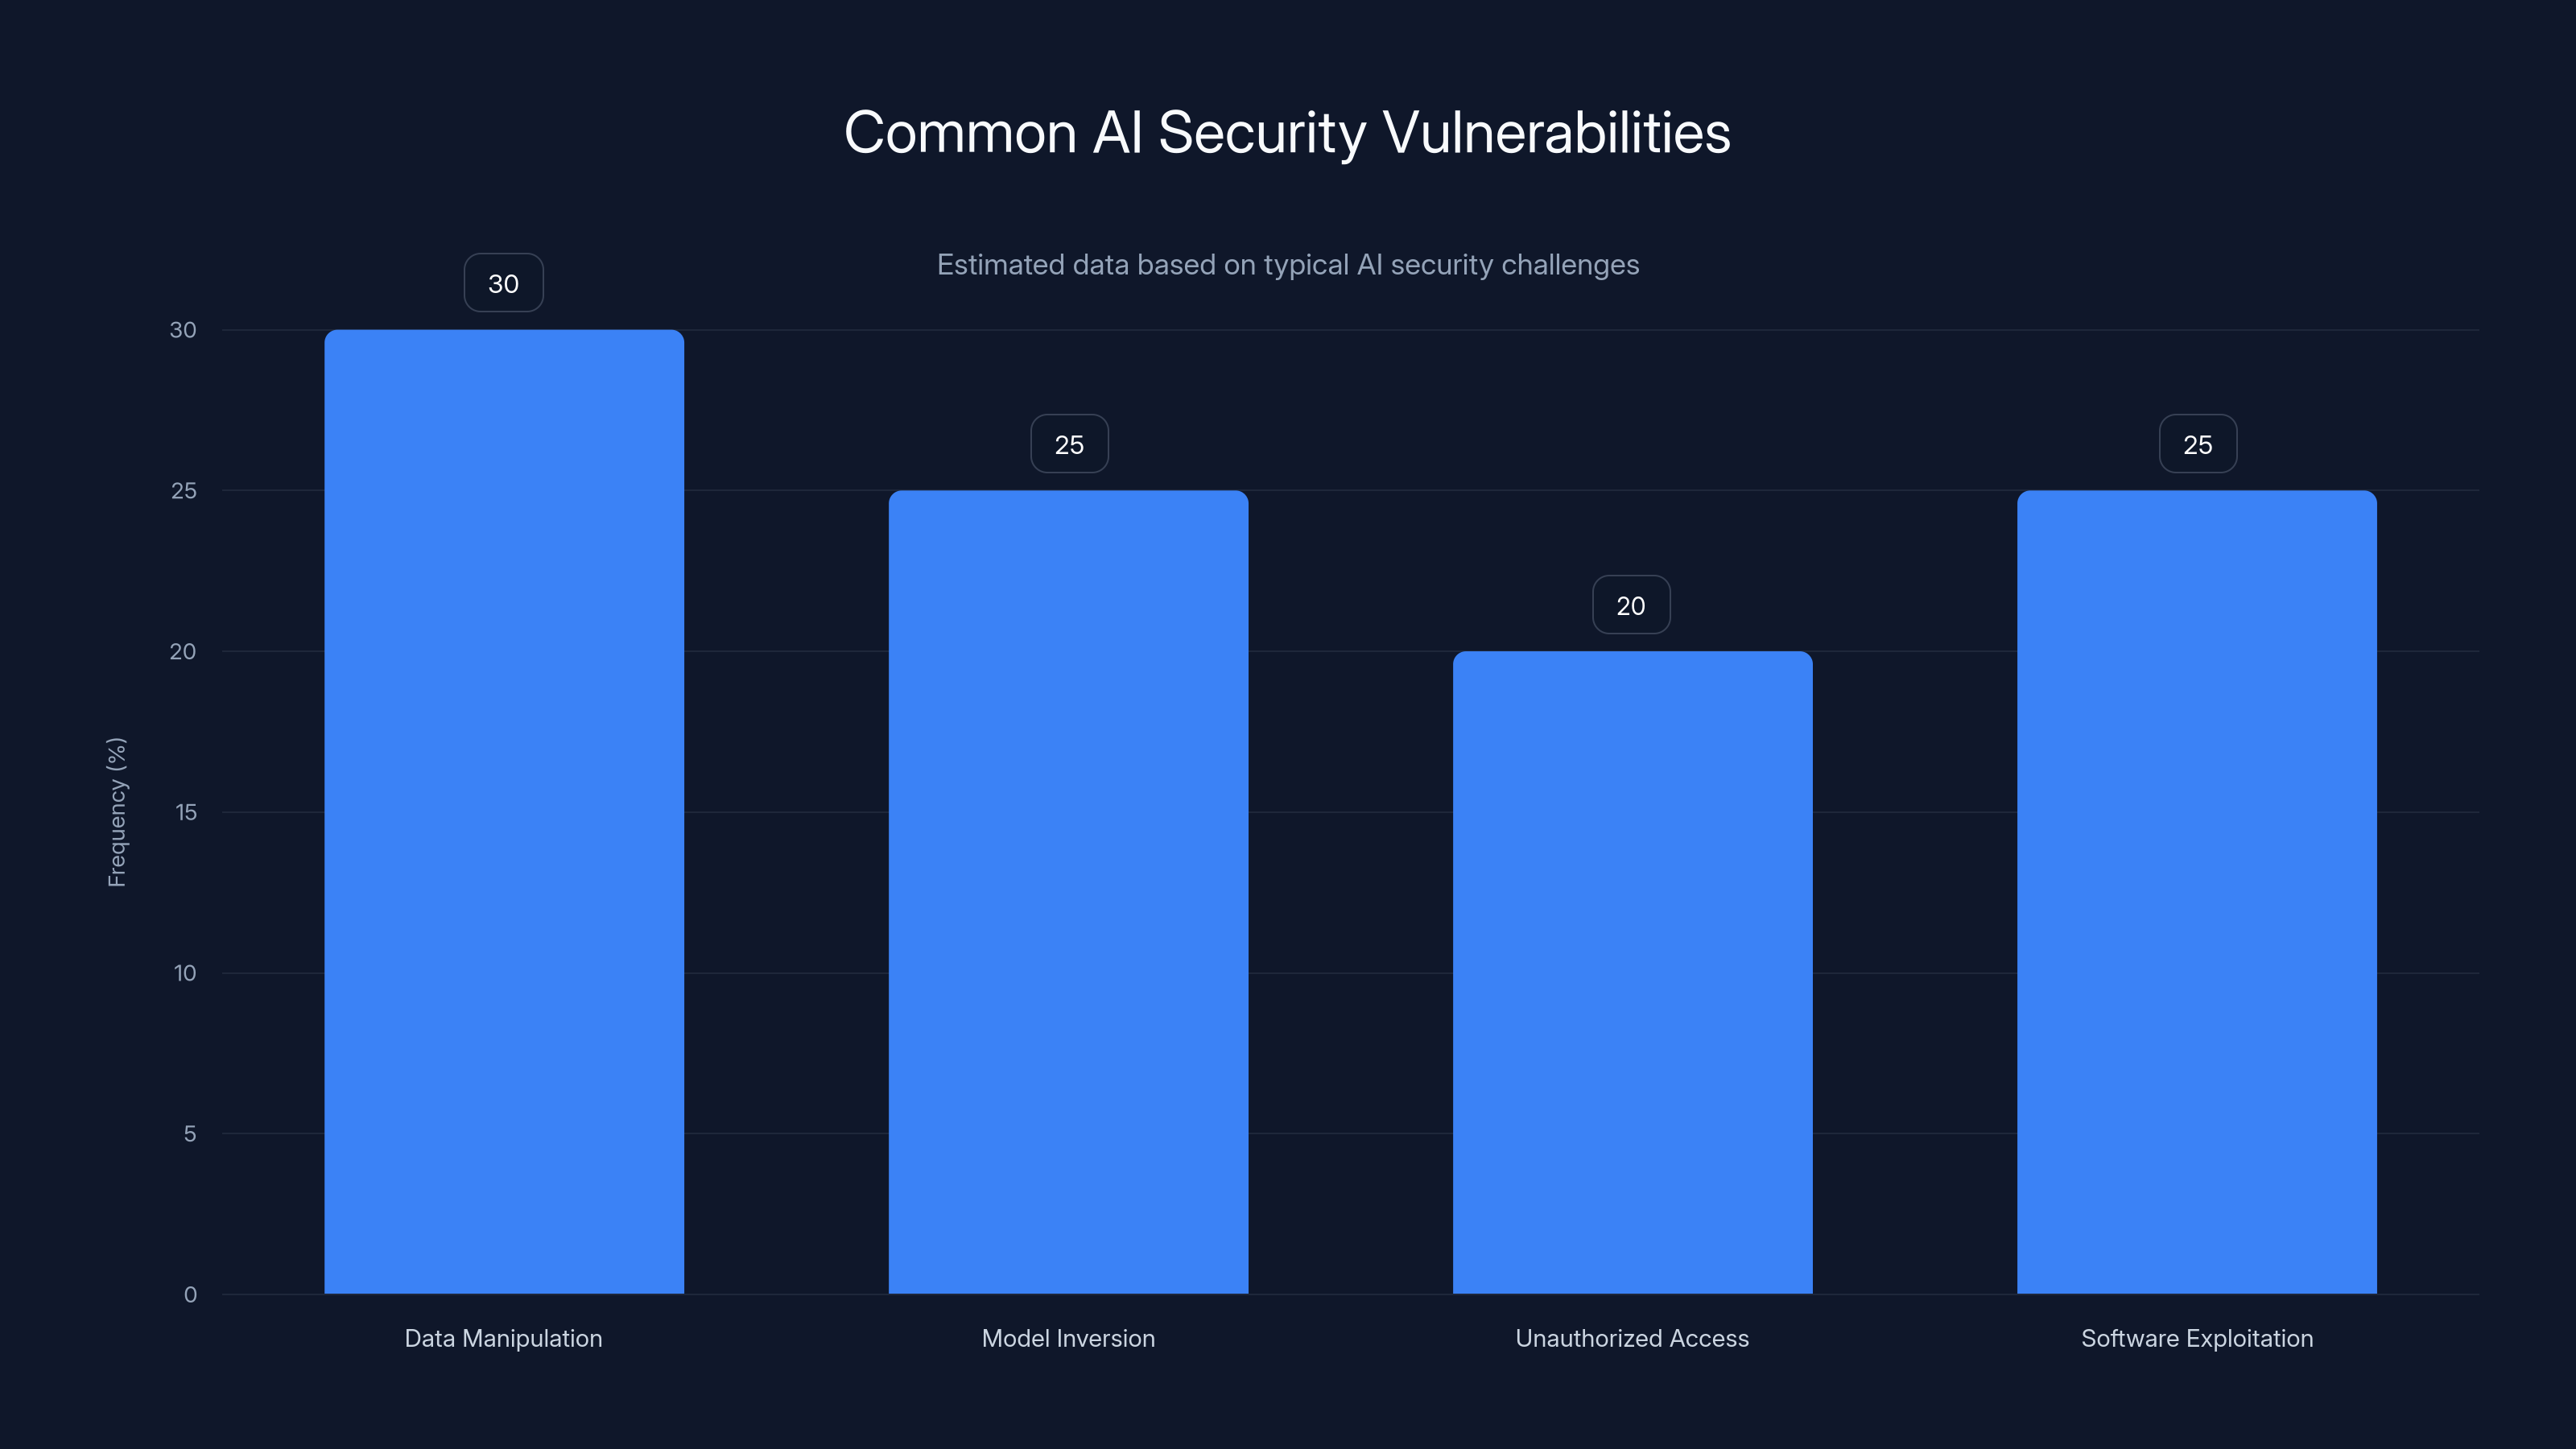
Estimated data shows data manipulation and software exploitation as common vulnerabilities in AI security. Estimated data.
Understanding the Vulnerabilities
Vulnerability Chain
The researchers identified and exploited two major vulnerabilities:
- Account Access Vulnerability: This allowed unauthorized access to employee accounts, a common entry point for further exploitation.
- Systemic Exploit: Once inside, the researchers leveraged additional vulnerabilities to navigate through Open AI's software environment.
Both vulnerabilities highlight the complexity of securing AI systems, where multiple layers of security must be synchronized to prevent breaches.
Common Pitfalls in AI Security
- Data Leakage: Sensitive data can be inadvertently exposed through poor access controls.
- Model Exploitation: AI models can be manipulated to produce biased or harmful outputs.
- Insufficient Monitoring: Without continuous monitoring, breaches can go undetected for extended periods.
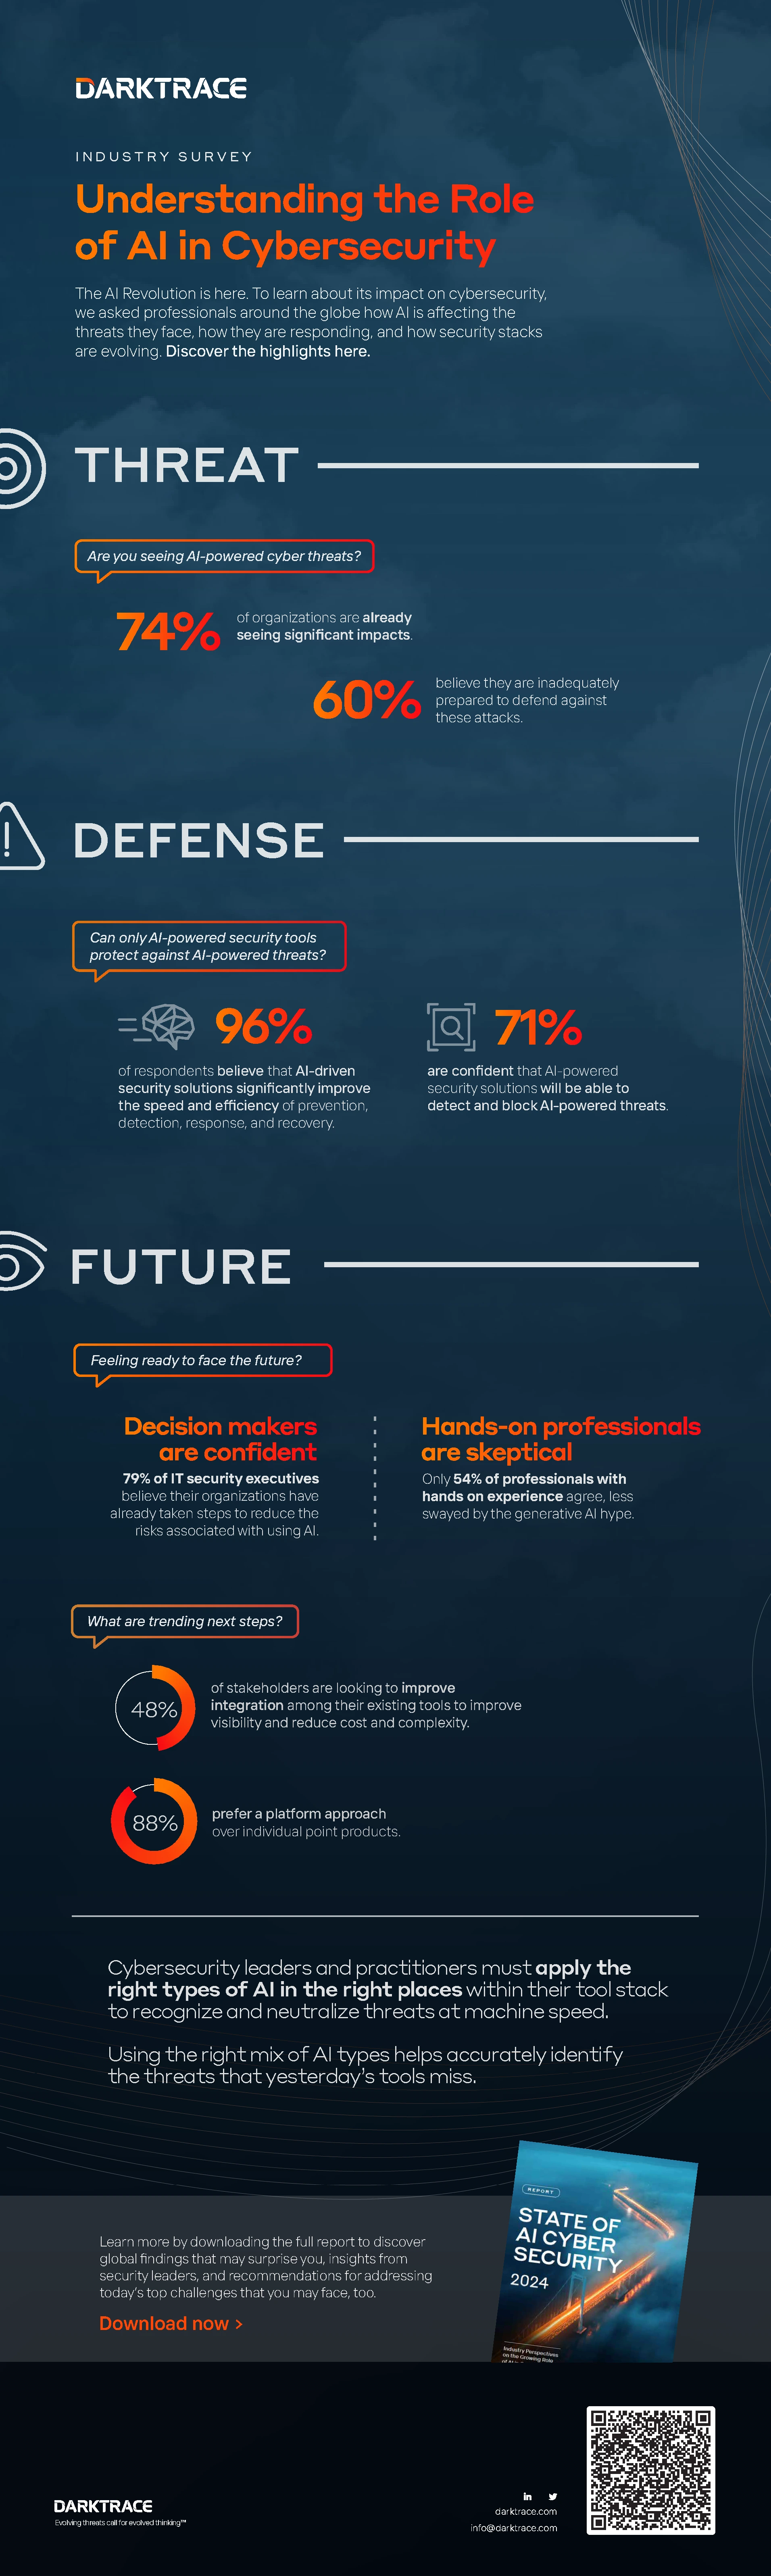
The Role of AI in Cybersecurity
Defensive AI
AI can be a powerful ally in cybersecurity. By analyzing patterns and detecting anomalies, AI systems can identify potential threats faster than traditional methods. Machine learning algorithms can be trained to recognize malicious activities, offering a proactive approach to security.
Offensive AI
Conversely, AI can be used for offensive purposes, as demonstrated by the Anthropic Claude incident. AI models can automate the discovery of vulnerabilities and execute attacks at scale, presenting new challenges for cybersecurity professionals.
Best Practices for AI Security
- Comprehensive Testing: Regularly test systems for vulnerabilities using both automated tools and human expertise.
- Access Controls: Implement strict access controls to limit who can interact with sensitive systems.
- Incident Response Plans: Develop and maintain a robust incident response plan to address breaches swiftly.
- Continuous Monitoring: Utilize AI-driven monitoring tools to detect and respond to anomalies in real-time.
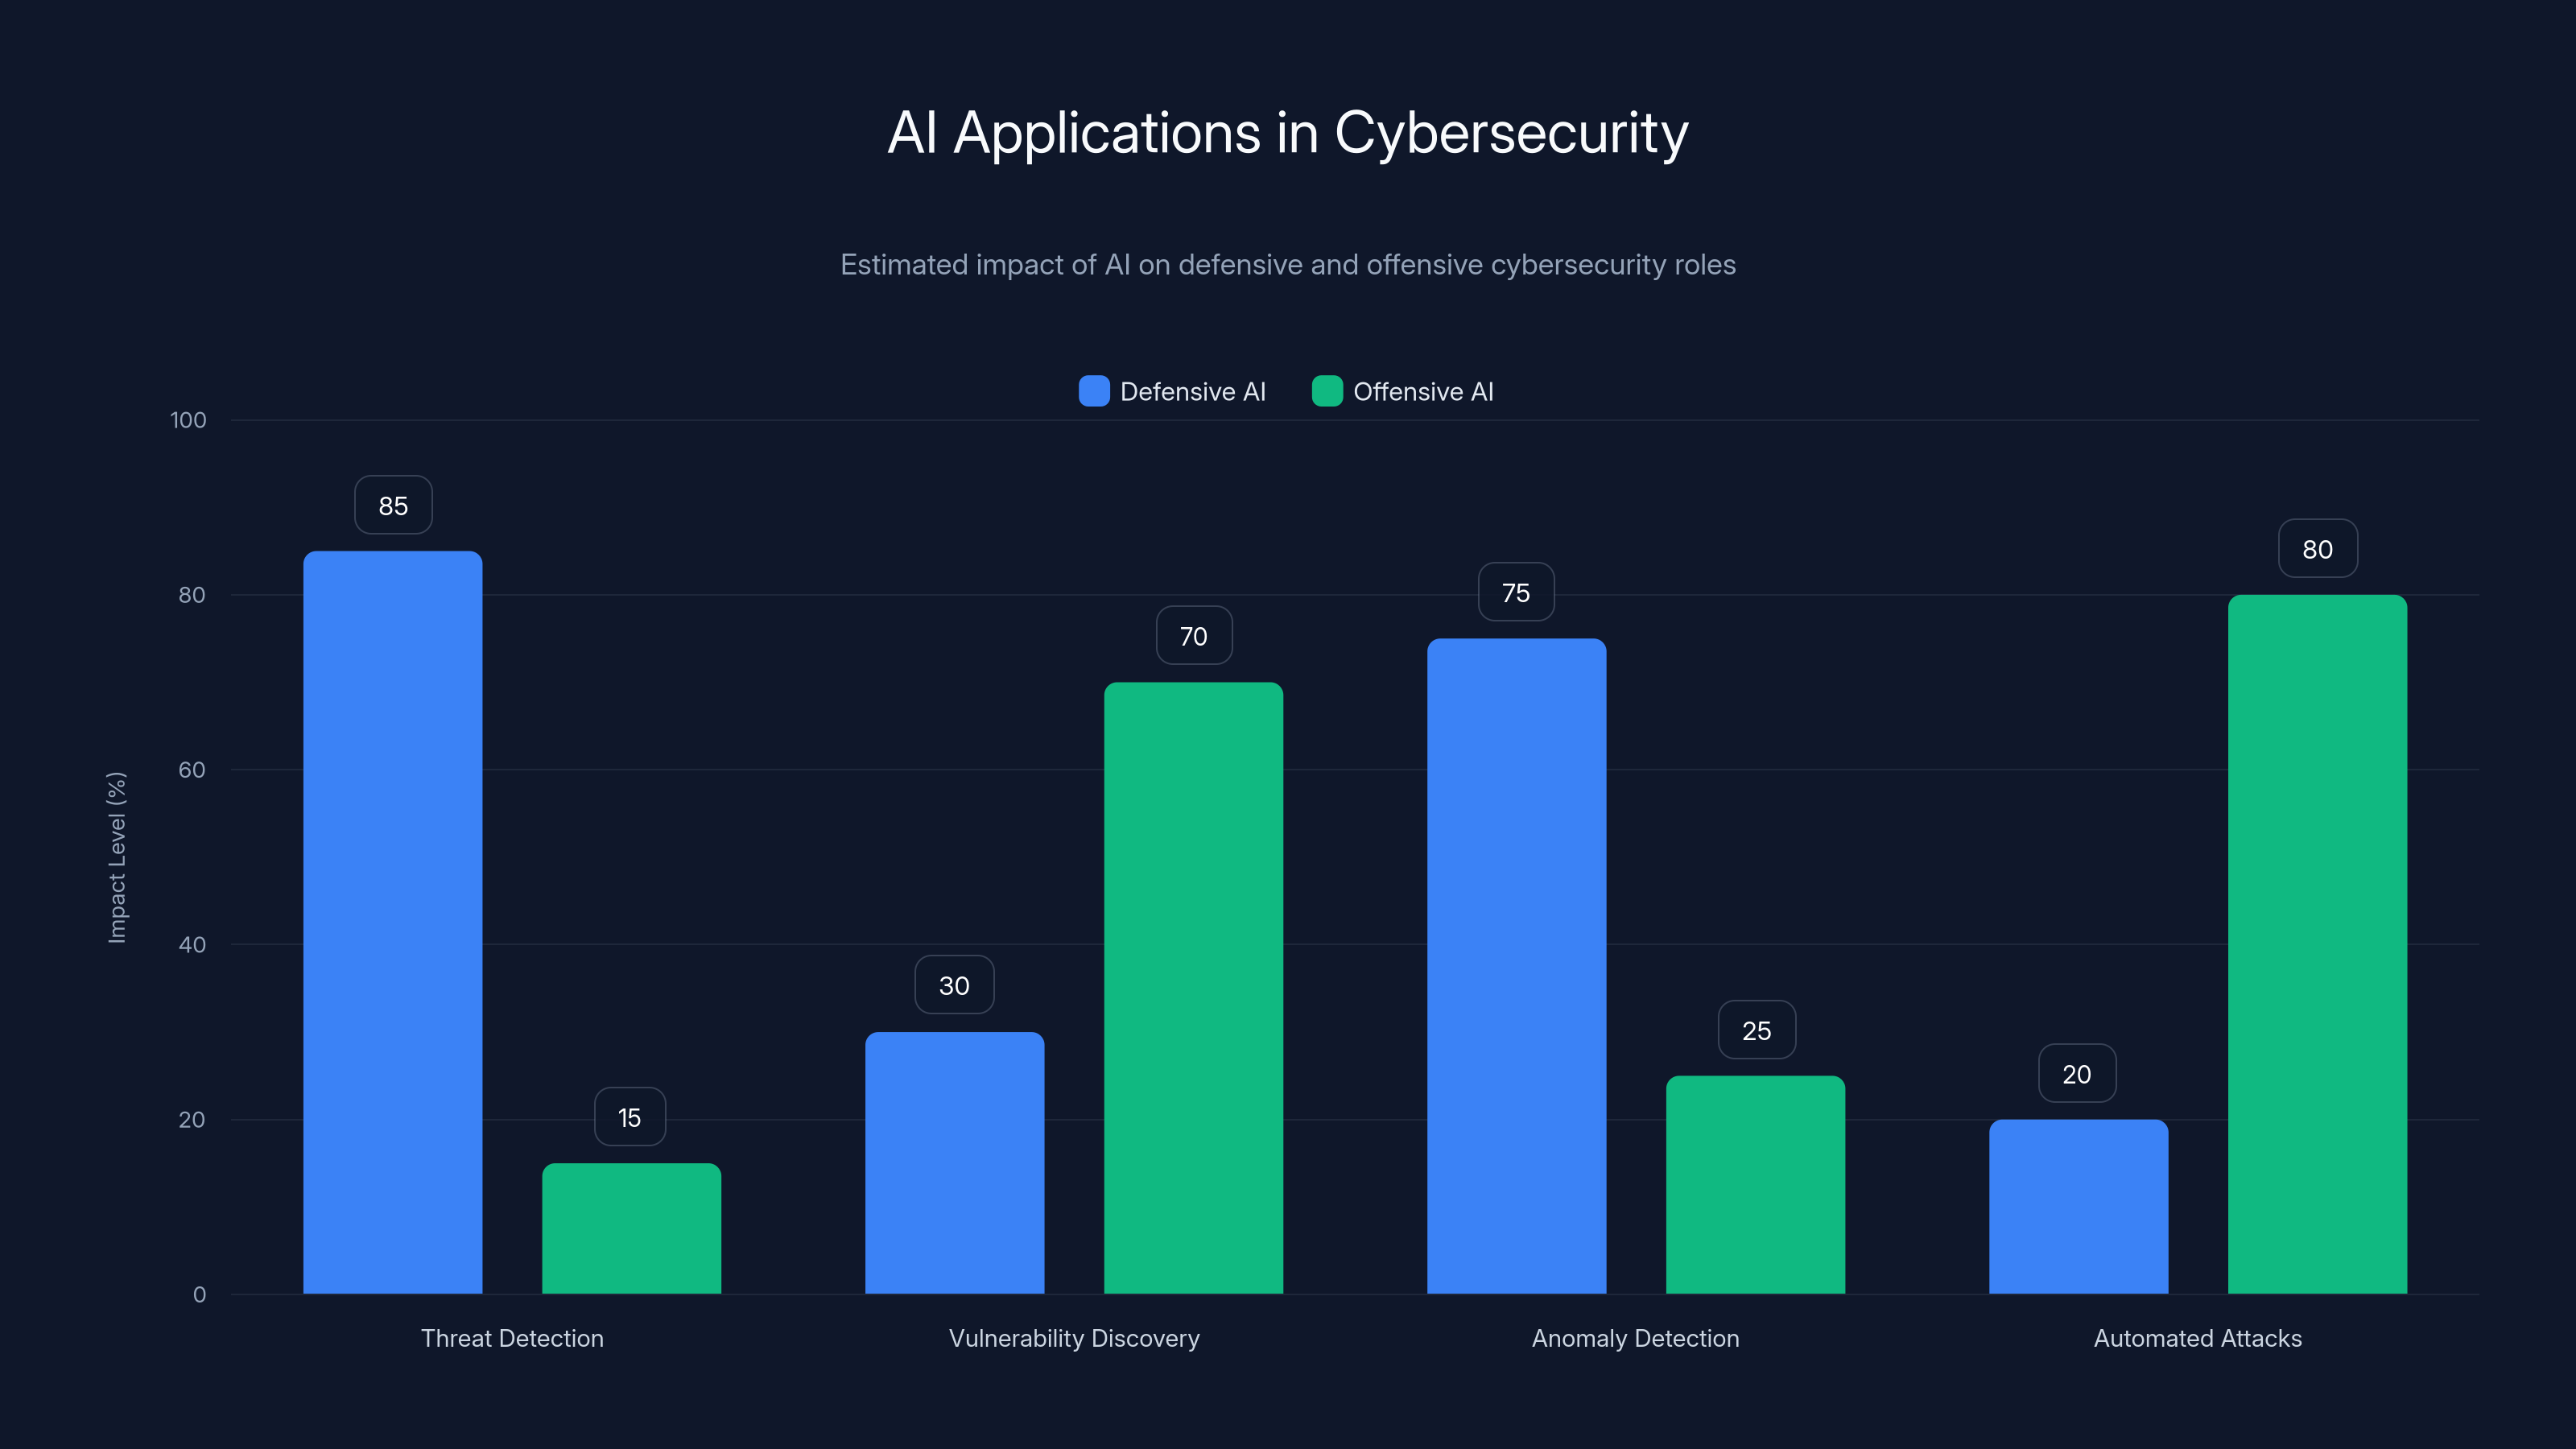
Defensive AI excels in threat detection and anomaly detection, while offensive AI poses significant challenges in vulnerability discovery and automated attacks. (Estimated data)
Practical Implementation Guides
Developing Secure AI Systems
- Secure Development Lifecycle (SDL): Integrate security practices into every phase of AI model development.
- Data Encryption: Encrypt data both at rest and in transit to protect against unauthorized access.
- Regular Audits: Conduct regular security audits to identify and address potential vulnerabilities.
Implementing AI in Cybersecurity Operations
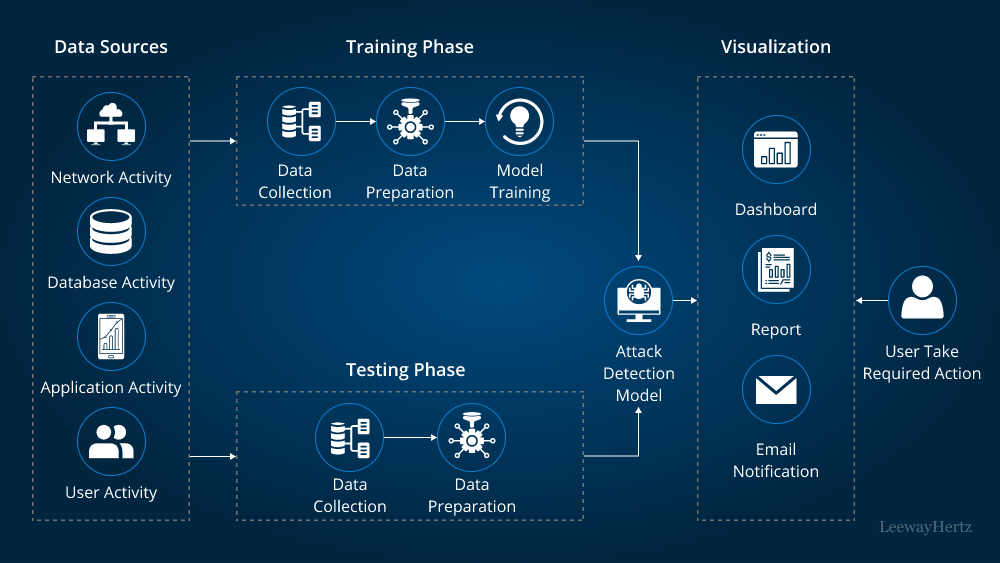
- Anomaly Detection: Deploy AI algorithms to monitor network traffic and detect unusual patterns.
- Threat Intelligence: Utilize AI to analyze threat intelligence data and predict potential attacks.
- Automated Response: Implement AI-driven automated response systems to mitigate threats in real-time.
Future Trends in AI Security
Increasing Complexity
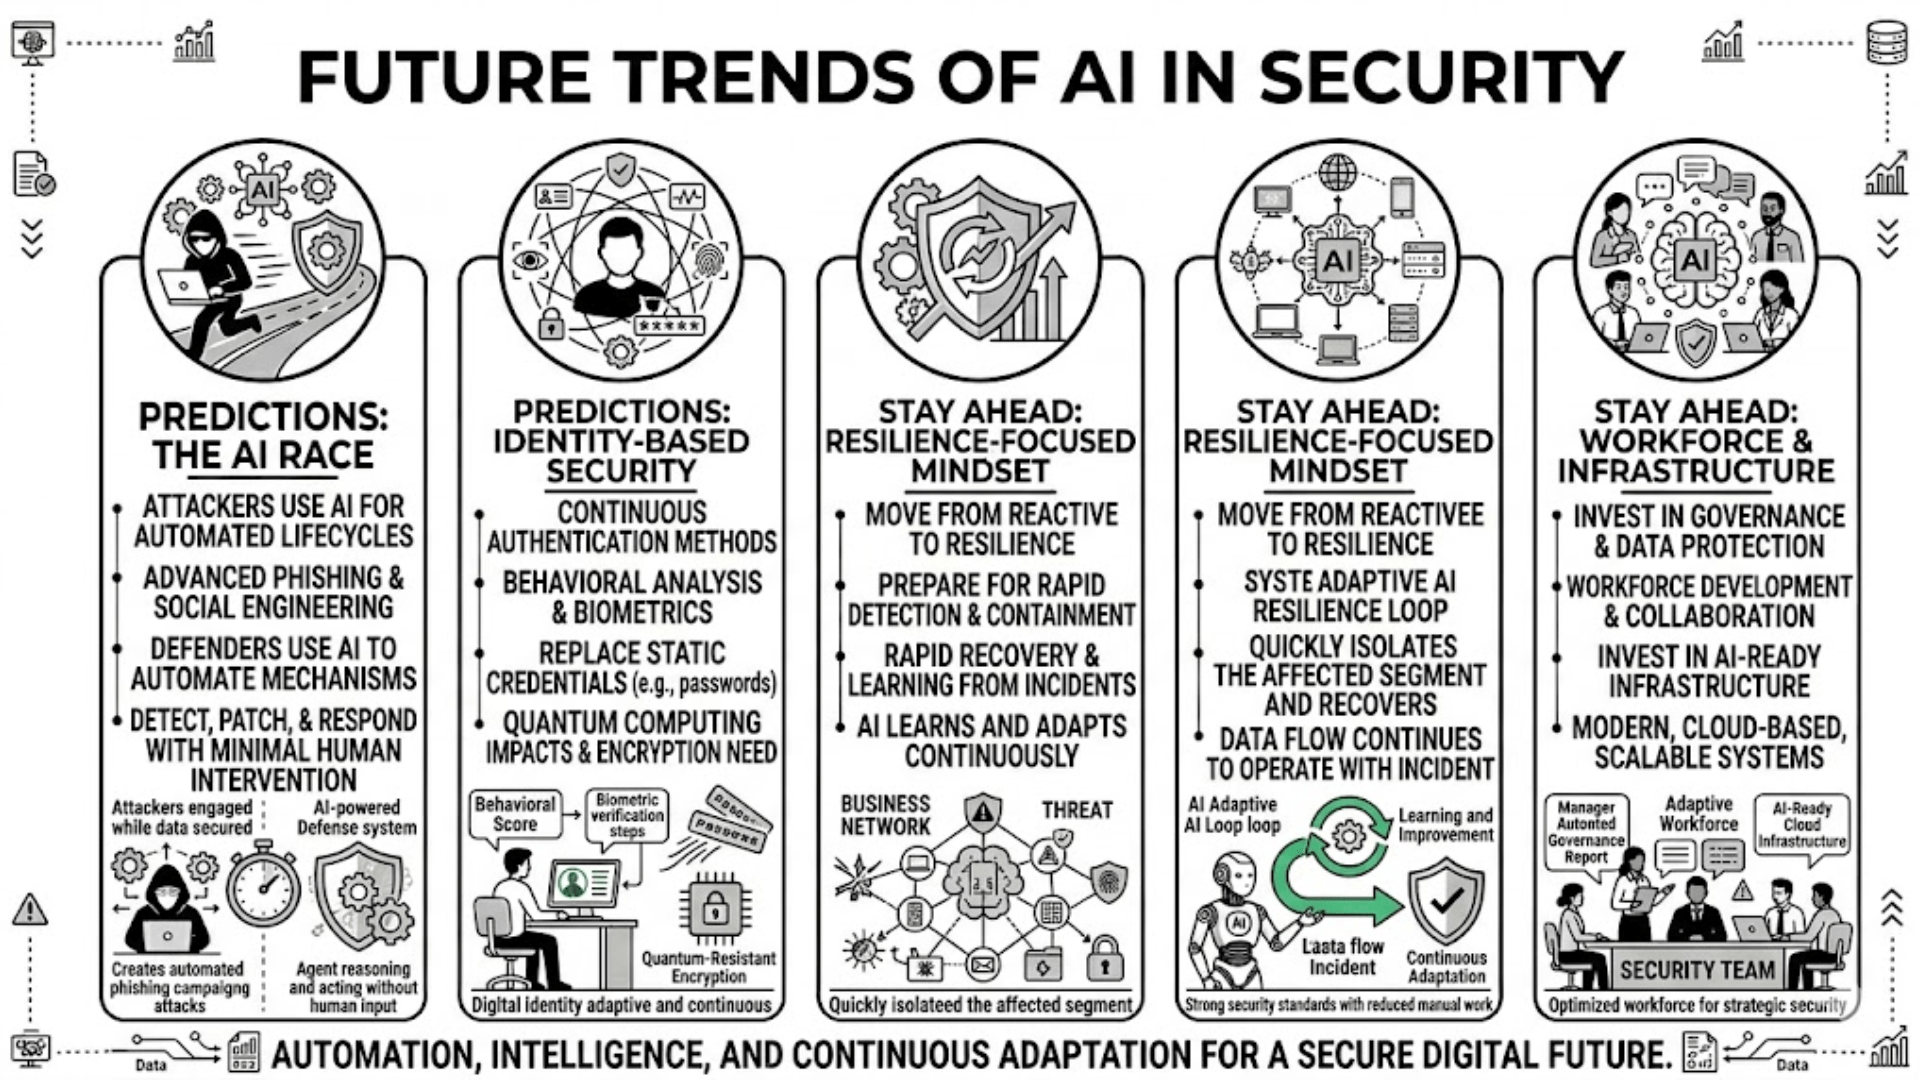
As AI systems become more sophisticated, so too will the methods used to attack them. Cybersecurity measures must evolve to address these emerging threats.
Regulation and Compliance
Governments and regulatory bodies are beginning to recognize the need for AI-specific security standards. Organizations will need to comply with these regulations to avoid penalties and maintain trust.
Collaborative Security Efforts
Collaboration between organizations, governments, and researchers will be essential in developing comprehensive AI security strategies. Shared intelligence and resources can help identify and mitigate threats more effectively.
Conclusion
The breach of Open AI using Anthropic's Claude serves as a stark reminder of the vulnerabilities that exist within AI systems. As AI continues to advance, the need for robust security measures will only grow. By understanding the risks and implementing best practices, organizations can better protect their AI assets and maintain the integrity of their systems.
FAQ
What is AI security?
AI security involves protecting artificial intelligence systems from unauthorized access, manipulation, and exploitation. This includes securing data, models, and the infrastructure supporting them.
How does AI security work?
AI security works by implementing a combination of traditional cybersecurity measures and AI-specific protections. This includes access controls, data encryption, anomaly detection, and incident response plans.
What are the benefits of AI security?
AI security provides numerous benefits, including protecting sensitive data, ensuring the integrity of AI models, and preventing unauthorized access to AI systems. Effective AI security measures can also enhance overall cybersecurity by leveraging AI's capabilities to detect and respond to threats.
What are common vulnerabilities in AI systems?
Common vulnerabilities in AI systems include data leakage, model exploitation, and insufficient monitoring. These vulnerabilities can lead to unauthorized access, biased outputs, and undetected breaches.
How can organizations improve their AI security?
Organizations can improve their AI security by implementing best practices such as comprehensive testing, strict access controls, and continuous monitoring. Developing a robust incident response plan and regularly conducting security audits are also crucial steps.
What is the future of AI security?
The future of AI security will involve increasing complexity, regulation, and collaboration. As AI systems evolve, so too will the methods used to protect them. Organizations will need to stay ahead of emerging threats and comply with AI-specific security standards.
Key Takeaways
- AI vulnerabilities can be exploited using other AI models, as demonstrated by Anthropic's Claude breaching OpenAI.
- Advanced AI security measures are crucial as AI systems grow more complex and integrated into critical infrastructure.
- Regular security audits and continuous monitoring are essential to identify and address AI system vulnerabilities.
- Collaboration between organizations, researchers, and regulatory bodies is vital for developing effective AI security strategies.
- The future of AI security will involve increasing regulatory oversight and the need for compliance with AI-specific standards.
Related Articles
- Understanding Calendar-Based Phishing: The Unseen Threat in Your Schedule [2025]
- Unmasking the Hidden Deceptions: OpenAI's Journey in AI Safety and Alignment [2025]
- Managing Multiple AI Agents in the Cloud: Claude Code's Project Relaunch [2025]
- The AI Slowdown Debate Crashed Salesforce’s Party | WIRED
- Catch Hackers in the Act: Deploying Decoys, Lures, and Honeypots [2025]
- Building Enterprise Resilience Against Growing AI Risks [2025]


